Russia did this.
We hear rumours of Russian war crimes daily, but this feels different, because it's a first hand account of systematic liquidation of population centres, including orders to kill children.
DO NOT EVER GET BORED OF SHARING THIS STUFF.
https://t.co/frOTPcIPpd
There's not much recent data on Twitter, but Elon's "balancing act" & focus on purging left-wing accounts have left pro-Russian trolls rampant on Twitter.
https://t.co/7wZY9JTXwh
11/13
"Deep insert" skimmers -- handmade devices that can fit inside an ATM's card acceptance slot -- have gotten super thin. This one's ~ 1/2 the height of a dime. Paired w/ hidden cams to grab PIN, clone cards. Here's a look at a bunch of these found recently: https://t.co/0RrkqNbdfN
Join @bettersafetynet@johullrich@bojanz for this EMERGENCY LIVE STREAM on the newly published #RCE vulnerability #log4j
We'll go over exploitation details & discuss what blue teams can do to detect the attack and protect their environments.
Join: https://t.co/0klWHCdO4m
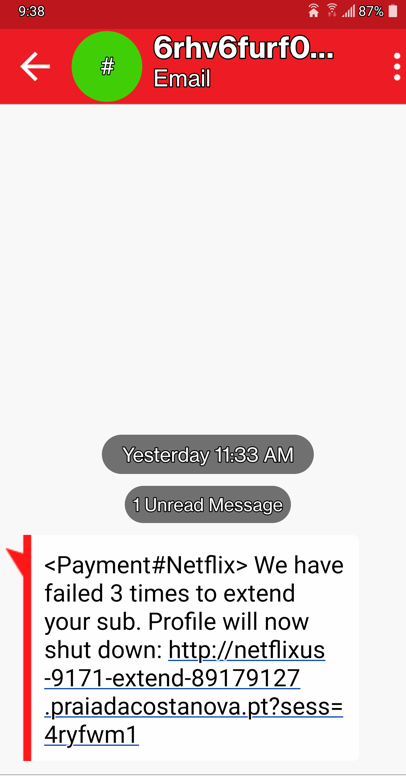
Example Netflix smishing scam...using a URL from Portugal. Tried to follow up to see if it was just password stealing or tried to install malware, but it was blocked already.
CISA's Conti ransomware advisory. Good advisory. Well done. Note that one of the attack vectors is phone-based social engineering. Good luck having any technical defense (e.g. MFA, EDR, etc.) mitigate that threat. Education is the cure.
https://t.co/ZKUT1SBrCO
How much is your data worth? So much that Google is paying Apple $15 billion to be the default search engine in the iPhone and other Apple devices.
Google is paying $10/year per device, to get you to use a 'free' search engine.
It's pretty remarkable that we've come to the point where ransomware gangs are rebranding mainly to help their victims get around Treasury/OFAC sanctions against paying the criminals. https://t.co/OFQQfSdVEz
APT29 (#TheDukes, #CozyBear) is actively serving malware previously used in #cyberespionage campaigns targeting COVID-19 research. RiskIQ's Team Atlas has identified nearly three dozen C2 servers under the control of #APT29 serving this #WellMess malware: https://t.co/VUxhf9AxBv