A new client-server communication protocol, VFS GUI, and more performance upgrades make this the fastest and most scalable version of Velociraptor yet.
Learn all about the exciting new features and upgrades here: https://t.co/K3u6paw7XT
🚀 Introducing #DFIR_IRIS v2! 🎉 Our IR collaboration platform just got better:
✅ Group management, access control and LDAP
✅ Comments, MD editors & new reports formats
✅ New customers page and stats
✅ Improved integrations
And much more! https://t.co/VEcmZUWfcY
A new update with a PsExec hotfix has now been posted!
Get the tools at https://t.co/zlch58GEpK
See what's new on the Sysinternals Blog: https://t.co/3rylQGWB9g
Our community member @DfirJos has an excellent blog piece covering two practical examples of using Velociraptor to alert you in real-time when adversaries conduct hands-on-keyboard activity on systems of the IT-infrastructure that you are monitoring.
https://t.co/5iu4p2jCpq
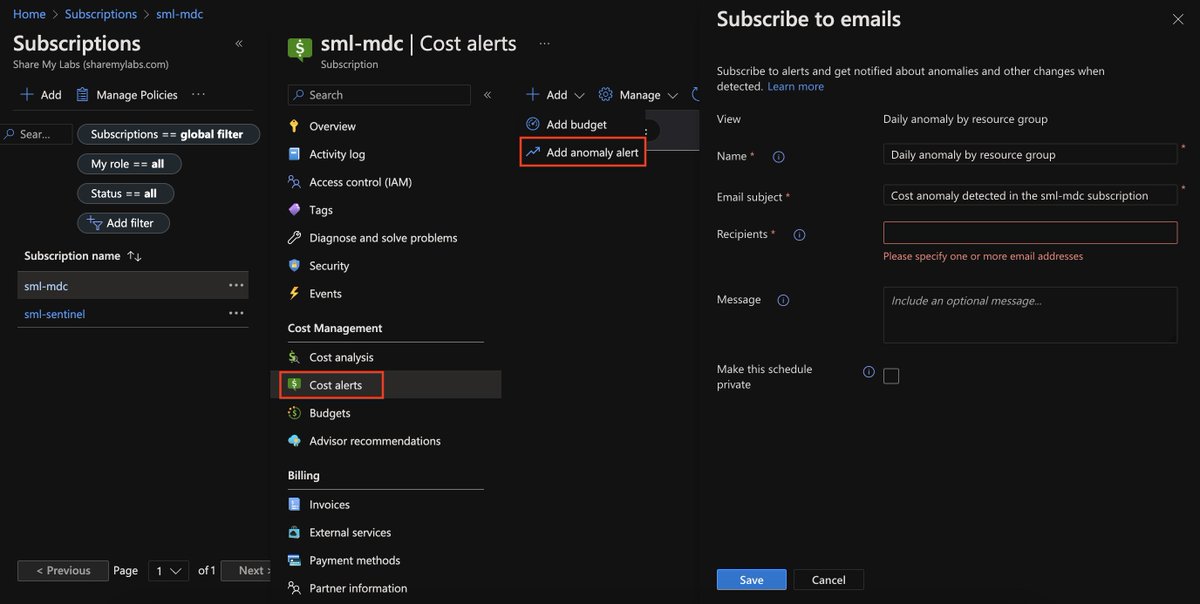
What are some of the first things you do when setting up Azure subscriptions?
Here's some of my favorites, and I'd love to hear from others too :)
First, I always start by setting up billing anomaly alerts (and budgets/budget alerts)
https://t.co/7qNPBxXiJJ
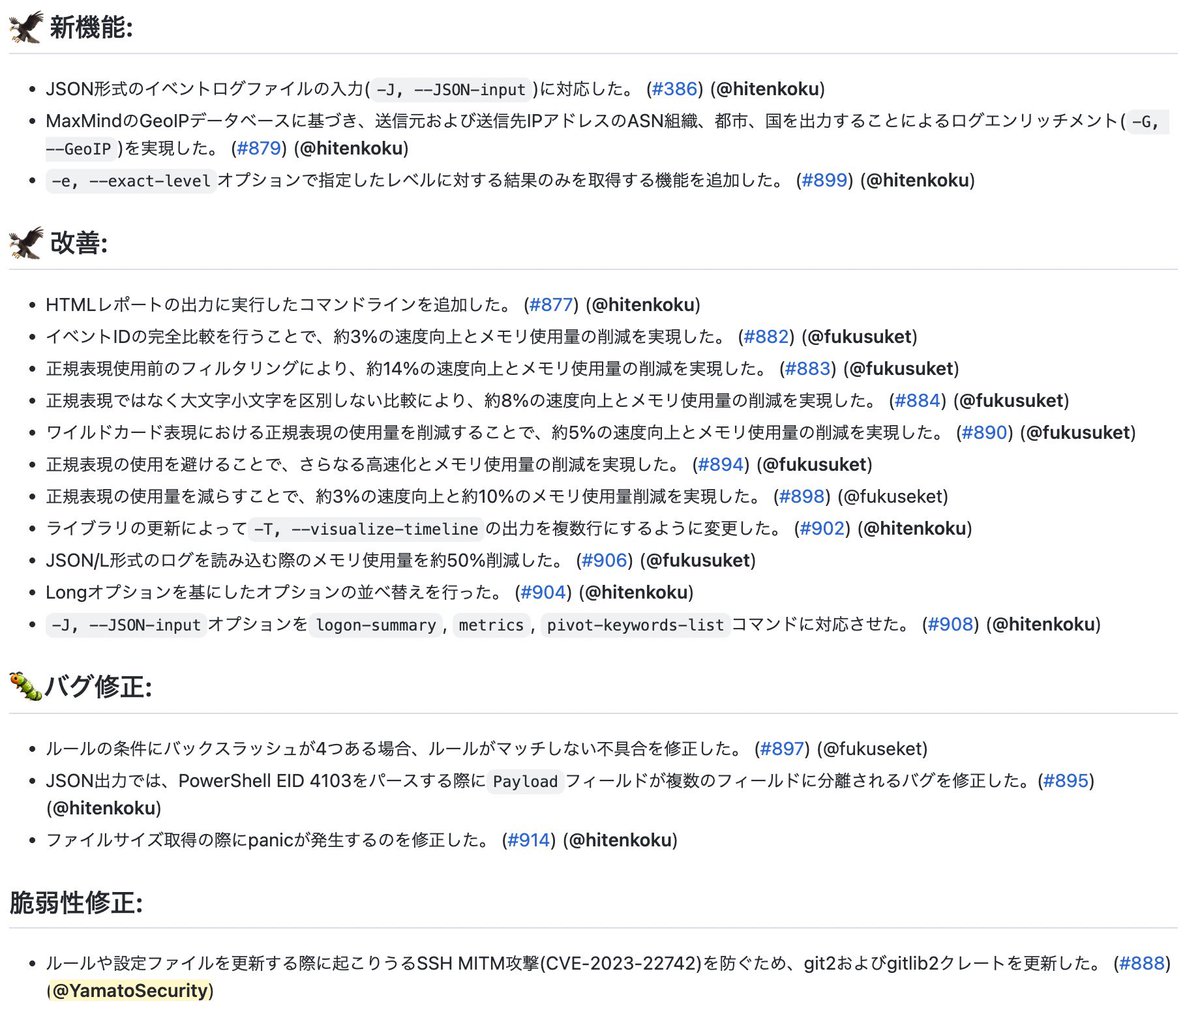
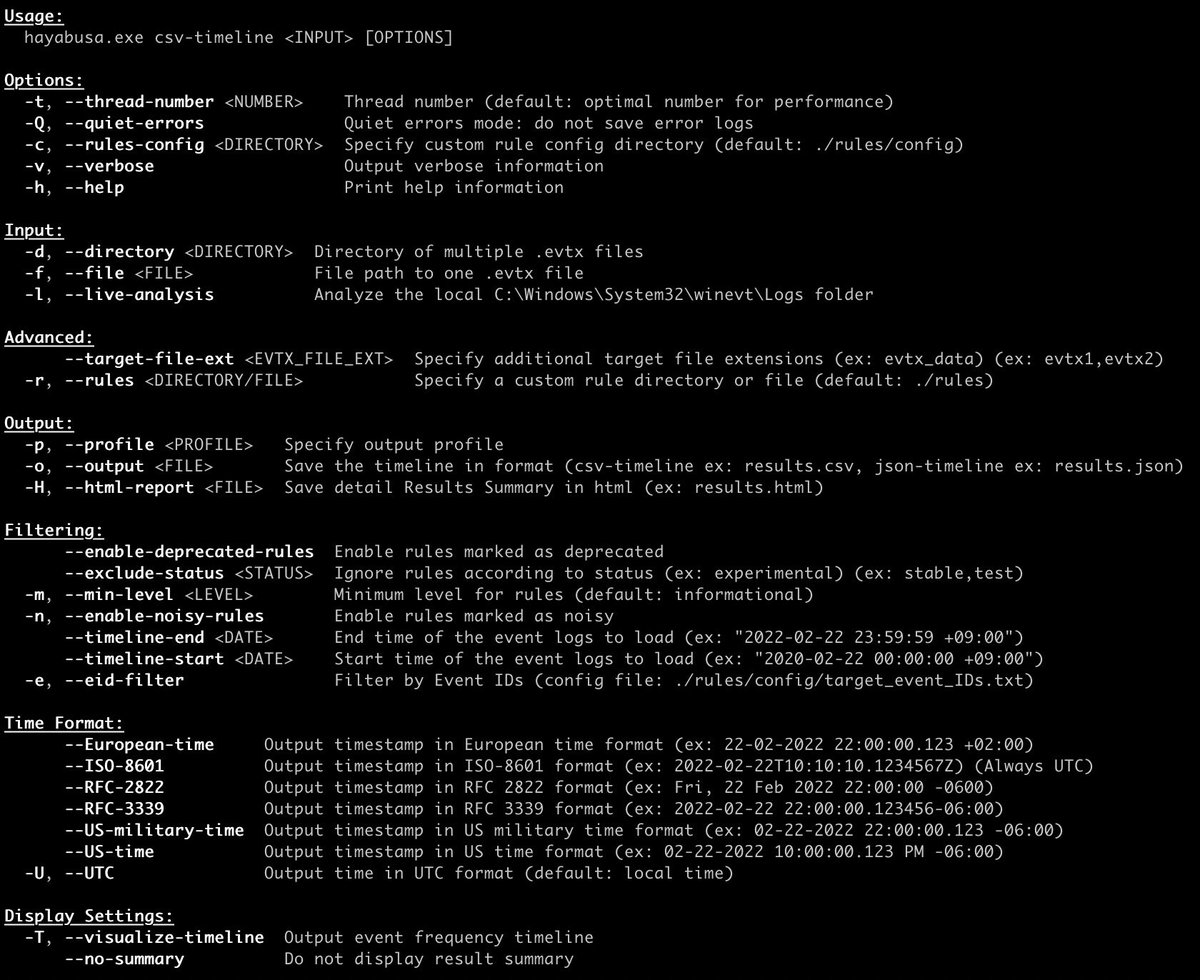
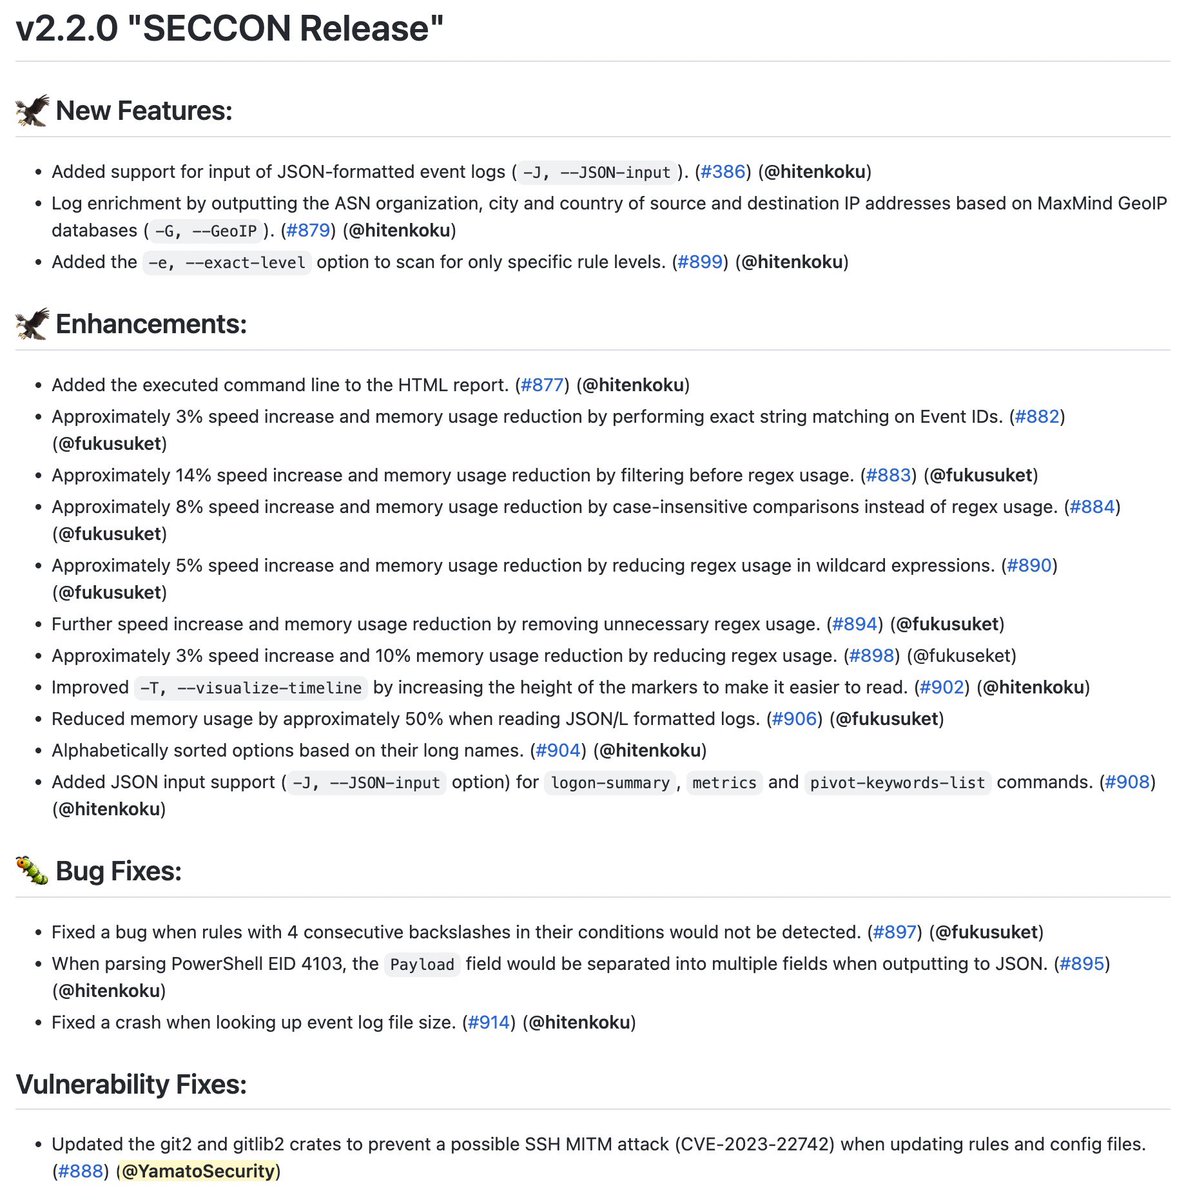
Just released Hayabusa 2.2.0 for the #SECCON CTF and conference workshop. JSON log input, GeoIP log enrichment, many performance enhancements, bug fixes and more!
https://t.co/DsZCYsu6TH
New year, new release! Ghostwriter v3.2 is now available and includes a new tagging feature and an all new activity logging interface. Find out more in this blog post: https://t.co/TrJlwzE0Sa https://t.co/2li2CnBCt6
I updated the Hayabusa artifact for Velociraptor. (Hayabusa v1.4.1 => 2.1.0) Should be faster, more customizable and more accurate than before: https://t.co/5sRkrsFbh2
Beta 3 of #DFIR_IRIS v2 is now out! It will be the last beta before the release 👷♂️
As for the last one, a demonstration instance is available at https://t.co/cBOcIwNBX2 😋 We appreciate your feedback!
✅ The source code is available here: https://t.co/W7BCMDCjF2
This is exactly what we defenders need :
1. What type of vulnerability
2. Details on affected software (versions)
3. Patch info
4. How does a successful exploitation look like = IOCs (logs, temp files, proc starts, crashes etc)
..
21. POC code
..
82. how you discovered it
Katana v0.0.3 now supports defining custom fields for data extraction/collection. Check out the changelog for new features & bug fixes!
Feature Link - https://t.co/WOuPMuCUrJ
GH Release - https://t.co/9Nkx13BXYQ
#hackwithautomation#infosec#bugbounty#webcrawling
Do you find ZAP useful?
You can show your appreciation by just starring the main repo: https://t.co/twvEBuAO2Z
Every star counts⭐
#owasp#zaproxy#AppSec
Merry Xmas everyone! We just release Hayabusa v1.9 and v2.0 with all commands refactored to subcommands for easier use! Hayabusa is now 1 years old! Still just getting started but hope you are finding it useful.
https://t.co/DsZCYsu6TH
#Hayabusa#DFIR#ThreatHunting
For those unfamiliar with DFIR-IRIS (@dfir_iris), it is a free, open source incident response platform that includes a host of useful and innovative features even many commercial platforms don't possess. Check it out here using the link below!
https://t.co/WBJCuRvXNc
Investigation Scenario 🔎
A user reported their mouse moving around on the screen by itself for a few minutes. The cursor appeared to open and close a few documents on the desktop.
What do you look for to investigate whether an incident has occurred?
#InvestigationPath#DFIR