Did already someone build a ipv6 address range to cidr list converter in Kusto?
For ipv4 there is this brilliant function: https://t.co/pRKhrKVk8A But for ipv6 it's not there.
APT Emulation Labs: NOW LIVE 🎉
Solve incidents emulating APT29, APT10 and other threat groups.
$45 per month access to ALL labs:
👀 150+ hours of lab content
👀 Disk forensics + ELK logs
👀 Hints, questions and point system
👀 7 days free trial
Labs are created & designed by industry peers:
@ZephrFish@svch0st@ippsec@DebugPrivilege @HuskyHacksMK @inversecos
Each lab comes
with scoping notes, Windows VM with forensic tools, network diagrams, disk forensics, ELK access and was created from our collective experience working in the field.
👇ACCESS THE LABS HERE 👇
https://t.co/raaUSztKtT
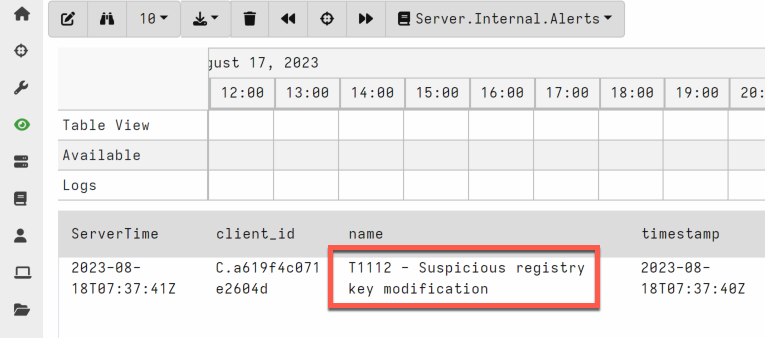
I just finished a blog that provides two new practical examples on how responders can detect adversary behaviour with the incident response and digital forensics tool Velociraptor. #Velocidex#DFIR#IncidentResponse#Velociraptor
https://t.co/C2bMGkiQ7N
The MDE blog series is updated with new content. Added more content for attack disruption, MDE settings management, Defender for Cloud Apps, Tamper protections for exclusions, and more common mistakes around MDE in part 10.
Link: https://t.co/Wrsh5u5WQ8
#MDE
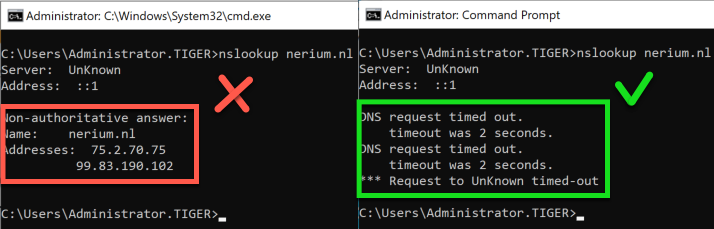
As a responder, do you trust the EDR isolation feature for containing a host?
Always check if DNS is also blocked. Because if that still works, the adversary can still operate the system if the malware communication (C2) is tunneled over DNS. Trust but verify ✅
#dfir#ir
Live demonstration rapid digital forensics & incident response -- with the CREATOR of Velociraptor @scudette & researcher @mgreen27! Absolute treat to get together with these incredible practitioners. Pro knowledge for free!! (This is the 1st of 2 videos) https://t.co/Aek4qhG2vs
Great to see that this awesome open-source incident response case management tool is continuously improving👌 Would definitely recommend other responders to check it out if you haven't already.
https://t.co/VcLbmT2WJp #DFIRIRIS#incidentresponse
🚀 Excited to announce IRIS v2.3.0 is here! 🥳 Fresh off the press with:
🤝 Collaborative edition in notes
🔎 Case peer-reviews
🚨 Alerts resolution status
🔔 New webhook module
👀 Enhanced overview & dashboard
🎨 Redesigned UI and more!
https://t.co/Pb6ycm5TLp
🚀 Excited to announce IRIS v2.3.0 is here! 🥳 Fresh off the press with:
🤝 Collaborative edition in notes
🔎 Case peer-reviews
🚨 Alerts resolution status
🔔 New webhook module
👀 Enhanced overview & dashboard
🎨 Redesigned UI and more!
https://t.co/Pb6ycm5TLp