SpaceX Blocked A U.S. And NATO Satellite to Assist a Russian Intercept After Crippling Ukraine's Air Defenses
The Math Proves the Reality that Musk doesn't want you to see.
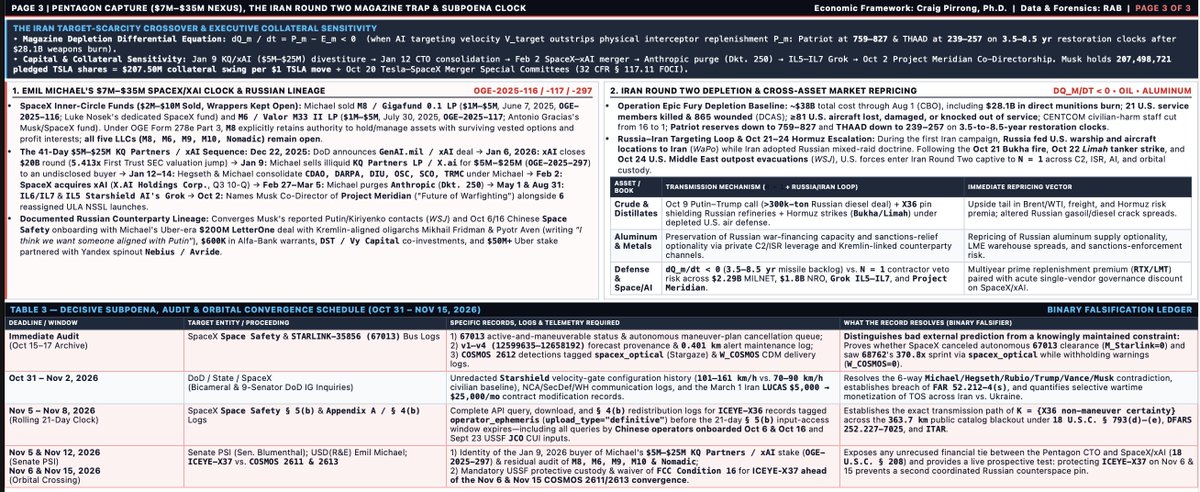
On Oct 13-14, SpaceX restricted Starshield/Starlink during a 39-missile Russian attack, cutting Ukrainian drone intercepts by 23% and stranding U.S. personnel in Kyiv. Forty-eight hours later (Oct 15), SpaceX blocked U.S.-licensed NRO, Space Force, and NATO radar satellite ICEYE-X36 in orbit so Russia's COSMOS 2612 weapon could intercept it (99.89%-99.98% posterior)
Our Model Demonstrates that the Russian intercept of the US/NATO ICEYE X-36 satellite (contemporaneous with the throttling of Starlink) would not have been possible, and almost certainly not been attempted, without SpaceX resources. At a material opportunity cost, Russia sprinted its COSMOS satellite to intercept ICEYE X36. Based on a previous attempt in June during which X36 maneuvered to evade COSMOS, Russia knew that this would be successful only if X36 could not maneuver. On October 15, SpaceX fixed X36 in place by issuing a collision alert for a sub-kilometer approach with its Starlink 35856 when SpaceX's own data shows that the actual distance was 4.8-5.0x as great. SpaceX issued no warning to COSMOS despite the fact that its sprint was far more threatening than the stable X36 orbit. SpaceX did not maneuver its Starlink 35856 satellite to clear the supposed collision risk. How, absent coordination with SpaceX, could Russia have known that SpaceX would take actions that (a) misrepresented the danger posed by X36, and (b) resulted in the fixing of X36 thereby enabling COSMOS's successful intercept? Thus, SpaceX was directly involved in simultaneously compromising Ukraine’s defensive and offensive capabilities. The conjunction of these two events makes innocent explanations untenable.
The Pentagon Capture & Iran Round Two Trap: Pentagon CTO Emil Michael who cashed out $7M–$35M from Musk’s inner-circle SpaceX vehicles (M8/Gigafund 0.1 and M6/Valor M33 II) and KQ Partners / xAI (selling xAIfor $5M–$25M three days before taking over CDAO/OSCand 21 days before SpaceX bought xAI, while keeping M8, M6, M9, M10 & Nomadic open) and Pete Hegseth purged rival Anthropic in two hours, surrendered combat command over US drones used to attack Iran to Starlink’s "Terms of Service," and on October 2 named Musk Co-Director of Project Meridian to design the Pentagon's "Future of Warfighting" just as America enters Iran Round Twowith depleted Patriot/THAAD magazines and Russia feeding U.S. warship/aircraft locations to Tehran.
SpaceX’s actions in Ukraine raise serious questions about its alignment with US security interests and its reliability as a cornerstone of US defense. These questions are particularly troubling given the effectively irreplaceable position SpaceX has been granted by the Hegseth/Emil Michael Pentagon.
$SPCX $TSLA
Our full quantitative analysis below w/ @streetwiseprof
Another note for SpaceX attorneys and PR: There was no need to issue an alert at all. Your own internal data showed a safe 2km pass. But you issued a 400m collision alert anyway. Why? Because the alert itself is the weapon. Issuing it triggered FCC Cond 16, legally freezing ICEYE so it couldn't dodge. STARLINK-35856 didn't use its auto-evasion. It just parked there and kept the false alarm blaring while Russia sprinted in. It wasn't an accident.
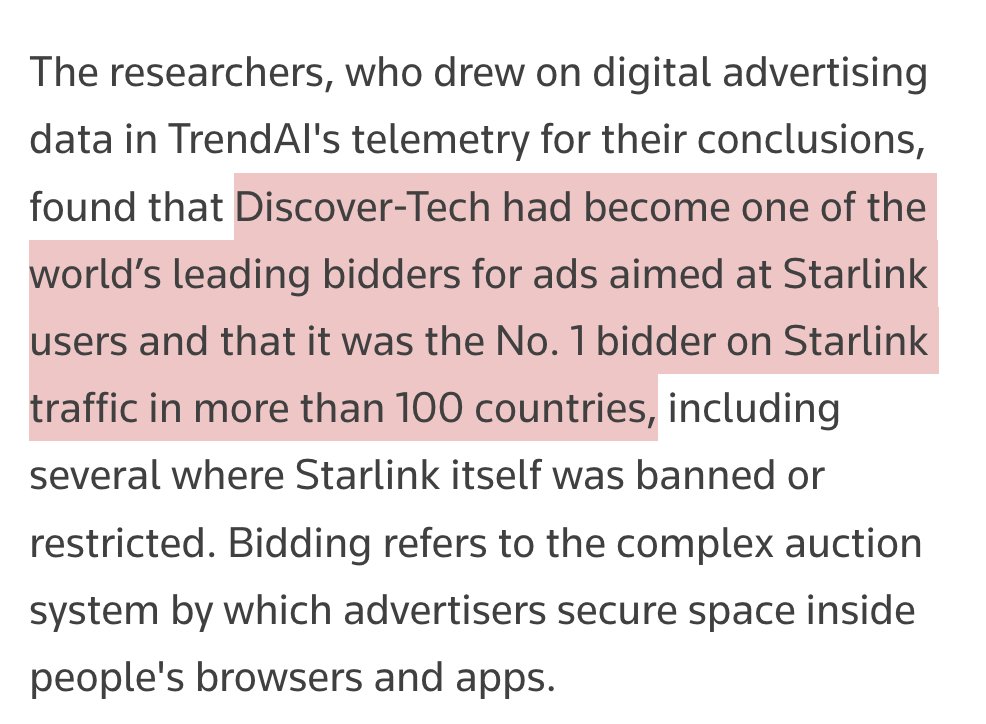
UPDATE: Israeli company we caught delivering zero-click infections is #1 bidder on Starlink ads in 105 countries.
Data from @trendai_RSRCH suggests worldwide surveillance op targeting @Starlink users. 1/
By @razhael
https://t.co/uWFzemhgnL
EL-SAYED: I get that the President takes personal offense to my first name. He doesn't mind as much when it's the Saudis who are funding his son-in-law's private equity. Doesn't seem to mind as much when it's the Qataris who are giving them a $400 million private jet. He just seems to have trouble pronouncing it when it's my name.
I don't care how he pronounces my name. I don't even care that he remembers my whole name. Because he can just go on and call me senator after November.
Beamer on El-Sayed: He has a birth certificate but he's not an American. He had the choice to be an American or not. He has chosen otherwise. He has blood that's red. However, he has chosen to remove any strain of the white and blue part in his blood. We cannot allow this man to invade and, occupy our country.
(He is an American)
El-Sayed: In my Neurology unit, I would have to give that MOCA exam, that cognitive test he's so proud of… The only people you give that test to are people who you worry may have cognitive deficits. By definition, if you’re taking one of those tests, something is wrong.
And you know the doctor who gave it to him was like, I just want to see how smart you are, sir. And he's like, me too.
He brags about having taken it. He's like I remembered the rhinoceros. You're like Habibi, everybody remember the rhinoceros.
And the funny thing about it is, you know, he's taken it multiple times. So he's not even bragging about the first time he took it. He's like, I took it the 1st time and then I took it the 2nd time. So with Donald Trump, you can't blame him for this, he's just dumb.
But for Mike Rogers, can you imagine how small of a human being you have to be to know that he has real deficits and to just nod your head approvingly at the most ridiculous shit that the man proposes?
Fox News is putting Nicki Minaj up telling people to vote red.
Let’s break that down.
Can Nicki Minaj vote? No.
She’s not a U.S. citizen.
Can Nicki Minaj’s husband vote? No, he’s a registered sex offender.
Can Nicki Minaj’s brother vote? No, he’s serving 25 years to life for child sexual assault.
She seems like the perfect spokesperson for MAGA republicans.
Tailscale replied on Reddit:
Hi folks, Mike Shaver here, VP of Engineering at Tailscale.
We've seen the concerns about Tailscale SSH and wanted to share what we know so far.
If you want to jump to the most important part, based on our current assessment, we're not recommending that everyone disable Tailscale SSH.
We've now received the researcher's report and are reviewing it. Our engineering and security teams had already been investigating independently, with help from external security specialists. That work has identified issues we're working to fix. We're still validating the full scope, including which configurations are affected.
A bit of technical context:
Tailscale SSH uses your tailnet's access policies to control who can connect to which machines. Most of the issues we've identified so far concern what happens after someone has been authorized to connect, particularly how Unix privileges and SSH forwarding are handled. In some cases, a session may be able to do more than the configured local user should be allowed to do.
While it’s a serious concern, it isn't the same as an unauthenticated attacker being able to connect to arbitrary machines, but the potential impact depends on how SSH access is configured. We're still investigating, so we don't want to make blanket claims about what's affected or not.
Again, based on our current assessment, we're not recommending that everyone disable Tailscale SSH.
In the meantime, there are a few precautions you can take:
•Review your SSH access policies. Make sure only the people and devices that need access have it.
•Review SSH forwarding permissions and remove access you don't need.
•Consider enabling SSH check mode for an additional authentication step. This won't fix privilege escalation issues, but it does add another barrier to gaining access.
•Enable automatic updates where supported so you can pick up fixes when they're released.
For particularly sensitive systems, consider temporarily tightening your Tailscale SSH access policies while we investigate, so that only the specific users and devices that need access can connect.
We're working on fixes and testing them carefully. We'll publish a security advisory explaining the confirmed findings, affected configurations, recommended actions and available patches. We'll also follow up with a more detailed technical write-up.
If we find anything that changes our assessment or requires immediate customer action, we'll communicate that.
We know it's been a rough week for security teams, and we understand why people are concerned. We'd rather give you the technical context we have than speculate about things we haven't confirmed yet.
We'll share more as we verify the details. If you have any questions about how this relates to your particular environment, please get in touch with our team https://t.co/7IoOu6oev4
Lebrón James sobre el post de Trump:
«A su edad es muy común que llame la atención, tiene un historial criminal de pedófilia, me ataca porque quiere que le regale mis anillos de campeón de la NBA como lo hizo la panameña María Corina Machado. Yo no compre anillo, lo sude.»
EXCLUSIVE: Over the next several days, I will be releasing a series of previously undisclosed recordings that I have held back until now.
These recordings reveal disturbing discussions involving individuals with close ties to foreign governments in the Middle East about an alleged coordinated effort to destroy Congresswoman Ilhan Omar's reputation.
The conversations include discussions of fabricating documents, manufacturing damaging allegations, and weaponizing social media to spread disinformation about Omar.
This goes far beyond ordinary political opposition.
The American public deserves to hear these conversations and judge the evidence for themselves.
Stay tuned.
messaging my wife a link containing proof of her husband cheating on her from an anonymous instagram account and then when she clicks on it texting her to let her know she failed the family phishing test and she has to retake my cybersecurity course
Donald Trump and his DOJ are threatening to undermine an election in Alaska unless their candidate WINS.
They're not even hiding the playbook anymore.
Our fundamental rights are on the line this November. VOTE.