https://t.co/YsE7UDC8A0 An in-depth solar-powered website experiment, courtesy @lowtechmagazine, that brings you back to the web of yesteryear where content is prioritized over all else. Watch that battery meter!
I'm torn on https://t.co/N9jBId0PZT. The good: As advertised it calls out directives in the wild such as 'https://*'. The bad: CSP isn't as simple as "it's either secure or it's not". The range of their usefulness runs the gamut but clearly 'unsafe-inline' is a problem for many.
An interesting look at the HTML <embed> element, what JS you can get browsers to execute based on varying values of its 'type' attribute, and the security implications of that.
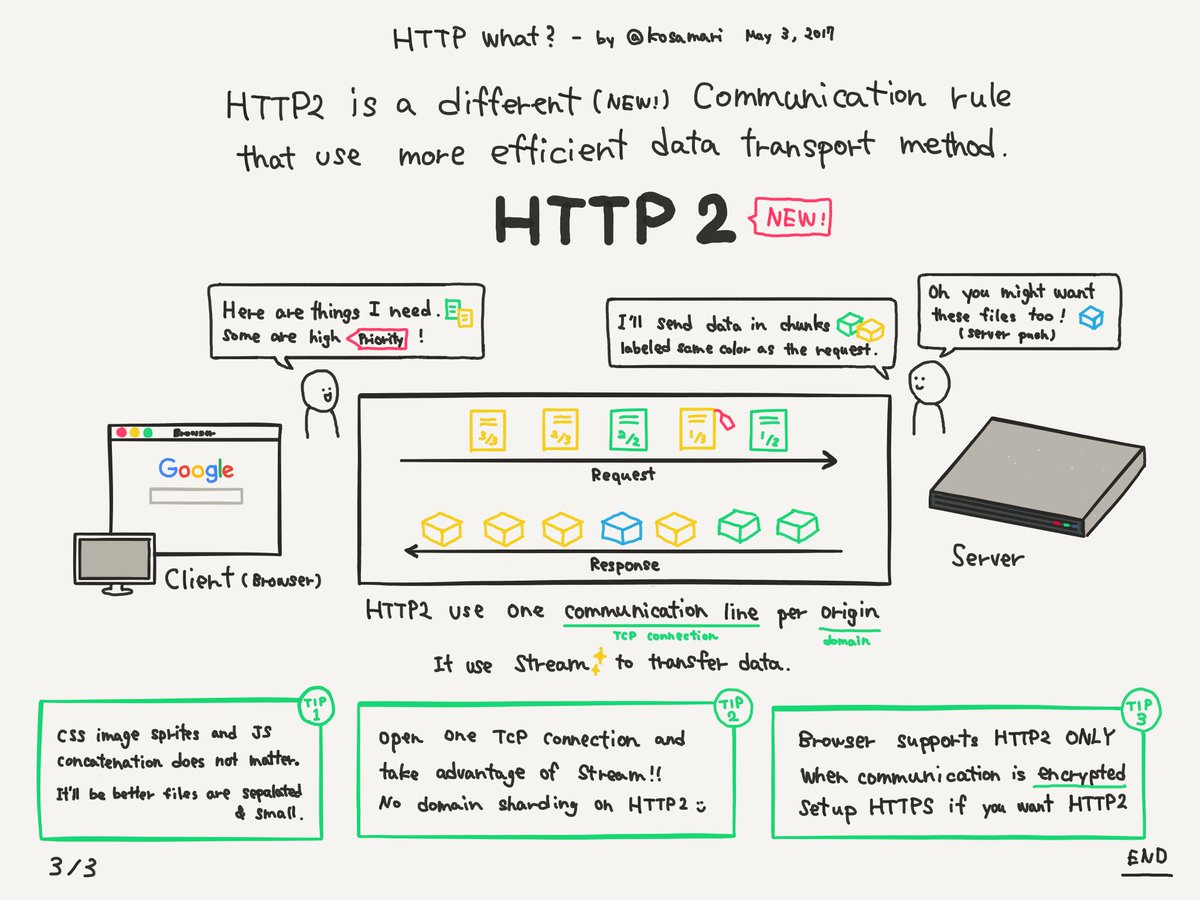
Hey kids guess what tomorrow is? Yes that's right, the day when Chrome 68 is released! Why is that important you ask? Well all HTTP sites will be marked as "Not Secure".
HTTPS = "Is the response untampered & from the expected sender?"
CORS = "Can I access the content of this resource?"
CSP = "Only allow requests that look like this…"
SRI = "Only allow content that looks like this…"
CORB = "Don't allow my data into another origin's process"
Because of #GDPR, USA Today decided to run a separate version of their website for EU users, which has all the tracking scripts and ads removed. The site seemed very fast, so I did a performance audit. How fast the internet could be without all the junk! 🙄
5.2MB → 500KB
My go-tos for confirming that TLSv1.0 has truly been disabled on sites:
Firefox: about:config -> security.tls.version.max -> 1
Curl: curl --tlsv1.0 https://t.co/oi6xVTaccp
This is a really well written look into the history of CORS that covers the details and reasoning behind preflighting requests. Not to spoil the ending, but in the final scene the response to the preflight request gets cached by yet-another Access-Control header. https://t.co/vmORR6XTah
It's hard to express just _how useful_ Mozilla's technical documentation about web technology concepts has gotten. Kudos to all my friends at Mozilla putting in the mostly thankless work to make new CSS and JavaScript concepts easily learnable with a Google search.
30 minutes ago I got curious… what do browsers do when downloading a gzip-encoded resource? Do they report the size of the data being written to disk, or bytes down the wire?
So I created a 100mb text file that gzips down to ~100k and throttled the server…
@pedrofortuna Hah, and that may only be a matter of time! This is a topic that doesn’t get the attention I think it deserves but your presentation handed out valuable insights into the power extensions are given, so thank you.
The elephant in the room of Man-in-the-Browser attacks are extensions, which receive little review and are generally granted complete control on all sites. Beyond [obviously] having full control of the DOM, extensions can override or remove HTTP headers including CSP (by design).
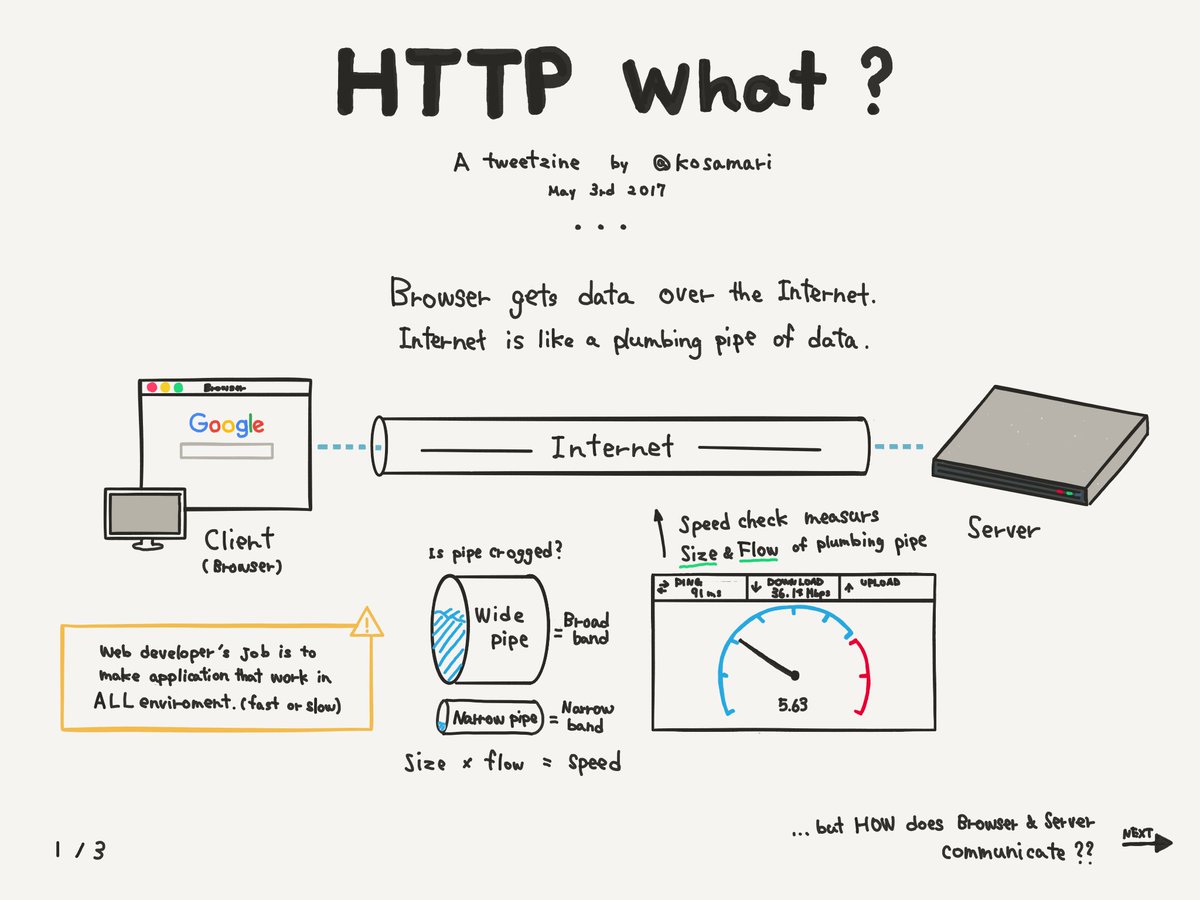
Happy to see this banner on a website. If the rest of the internet pulls this off by the end of June we will step into a generation which the majority of browsers have silent updates, and thus faster rollout of new tech such as tls1.3 many thanks @JeremyKingPCI