

Top Tweets for #200Dayschallenge

🔥 Day 98 of my #200daysChallenge with @mr_kay7
🏆 NETWORKWALKS INTERNSHIP ACHIEVEMENT!
✅ Week 1: 100/100
✅ Week 2: 100/100
✅ Week 3: 100/100
✅ Week 4: 100/100
🎯 Final Internship Exam: 99/100!
I'm grateful for the knowledge gained and the progress made throughout this


Day97 #200daysChallenge with @mr_kay7
I successfully completed a PortSwigger Web Security Academy lab on Blind SQL Injection! 🎯
I learned how the SQL SUBSTRING() function can help retrieve an administrator's password one character at a time by testing the application's


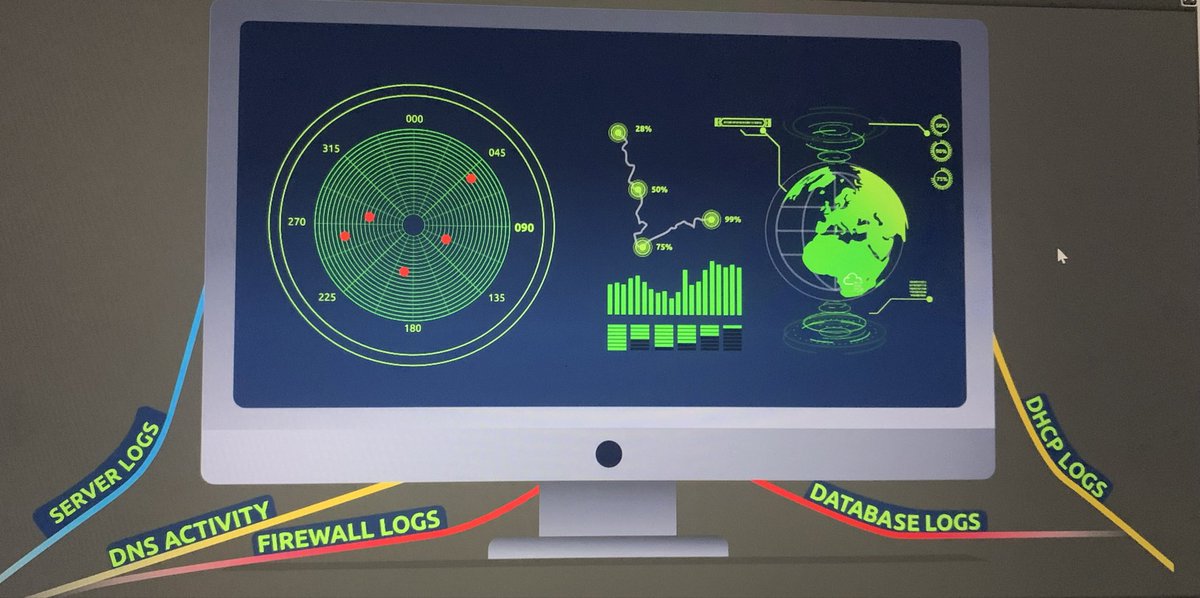
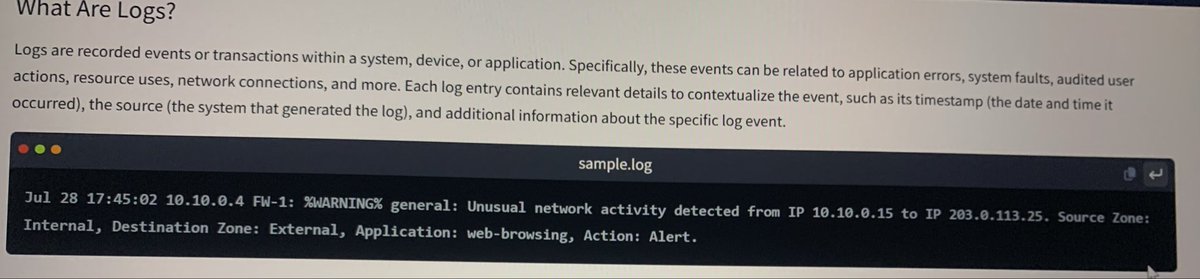
Day101 #200Dayschallenge @scriptedwebb
Intro to Log Analysis! Logs are essentially time sequenced records of events across a network. Learning how to parse them to understand what actually happened during an incident is key.
#CyberSecurity #InfoSec #LogAnalysis
Day100 #200Dayschallenge @scriptedwebb
Broken Access Control!
Once an attacker bypasses authorization controls, privilege escalation usually happens in one of two directions” Vertical or Horizontal.
#Cybersecurity #Infosec

Day97 #200daysChallenge with @mr_kay7
I successfully completed a PortSwigger Web Security Academy lab on Blind SQL Injection! 🎯
I learned how the SQL SUBSTRING() function can help retrieve an administrator's password one character at a time by testing the application's
Day 96 of #200DaysChallenge with @mr_kay7 🚀
Today, I strengthened my networking fundamentals during my TechBiz Security Ethical Hacking Internship.
🔹 IP vs MAC addresses
🔹 The 7 layers of the OSI model
🔹 10 common network ports and their services
🔹 TCP vs UDP


Day 96 of #200DaysChallenge with @mr_kay7 🚀
Today, I strengthened my networking fundamentals during my TechBiz Security Ethical Hacking Internship.
🔹 IP vs MAC addresses
🔹 The 7 layers of the OSI model
🔹 10 common network ports and their services
🔹 TCP vs UDP
Day 95 of #200daysChallenge with @mr_kay7
Today, I took my time to study the three main types of Cross-Site Scripting (XSS): Reflected XSS, Stored XSS, and DOM-based XSS.
🔹 Reflected XSS: This occurs when a website takes malicious input from a request and includes it unsafely
Day100 #200Dayschallenge @scriptedwebb
Broken Access Control!
Once an attacker bypasses authorization controls, privilege escalation usually happens in one of two directions” Vertical or Horizontal.
#Cybersecurity #Infosec
*Day99*

Day106
> Stopped all other thing like cs50, cp and dsa for now.
> Currently focusing on MERN stack.
> Building Project Management and Task Manager App.
Just showing Up Every Day. #200DaysChallenge #LearningInPublic #BuildingInPublic #Day106
https://t.co/oXWfhxTPJ5
Day105
CP: basics of C++
> Blog App
> CS50 Intro to DB
Just showing Up Every Day. #200DaysChallenge #LearningInPublic #BuildingInPublic #Day105
https://t.co/0XY2aL2MaS
Day 95 of #200daysChallenge with @mr_kay7
Today, I took my time to study the three main types of Cross-Site Scripting (XSS): Reflected XSS, Stored XSS, and DOM-based XSS.
🔹 Reflected XSS: This occurs when a website takes malicious input from a request and includes it unsafely
Day 94 #200daysChallenge with @mr_kay7 🚀
I’m excited to begin my new internship role with Techbiz Security as an Ethical Hacker! 🔐
Our first task was to study the CIA Triad, types of hackers, five phases of penetration testing, and the difference between Vulnerability
Day98 #200Dayschallenge @scriptedwebb
Broken Access Control Introduction!
Before diving into attacks, Task 1 breaks down how systems determine whether to grant or deny access to a resource. Here is my study recap
#CyberSecurity #AppSec #OWASP


Day98 #200Dayschallenge @scriptedwebb
Dive into the raw HTTP access logs and spotted the exact attack sequence from IP 203.0.113.45
Brute Force: Multiple 401 failures on the admin user, trying passwords like 'admin123', 'password' and 'letmein'.
#AppSec #OWASP #SOCAnalyst


🚀 Day 132-133 — #Upskill_with_Dishank #200DaysChallenge
This time, focused a bit more on DSA.
✅ Key concepts:
• Combinatorics & Pascal’s Triangle — nCr, counting arrangements, modulo arithmetic
• DFS / Divide & Conquer — recursive partitioning and subtree combinations
• Lambda & Custom Comparator — [&], comparator design, multi-level sorting
• HashMap + Greedy — index mapping and minimum swaps
• Math & Number Theory — digit sums, modular arithmetic & overflow handling
#LeetCode #DSA #CP #SystemDesign #LearnInPublic


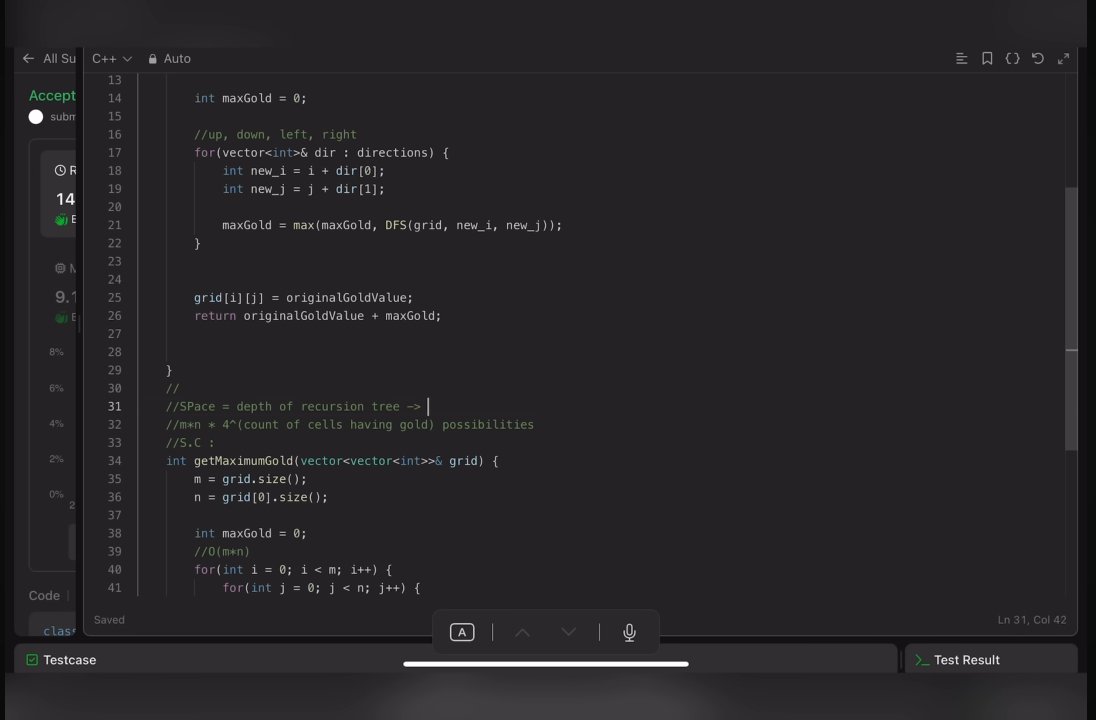
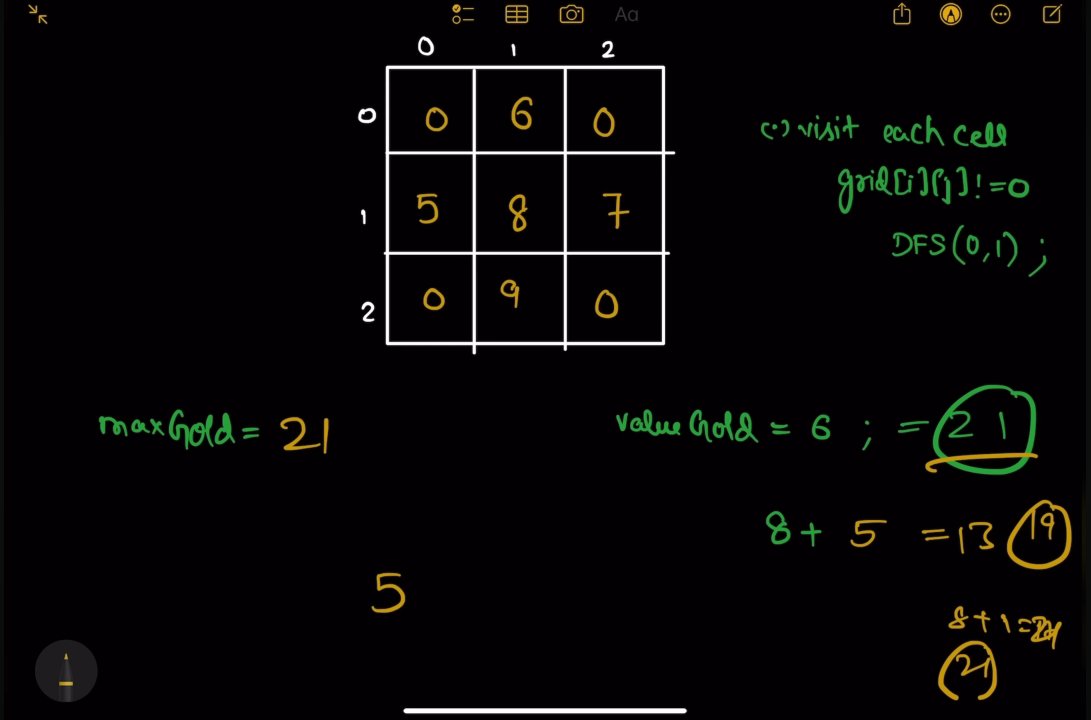
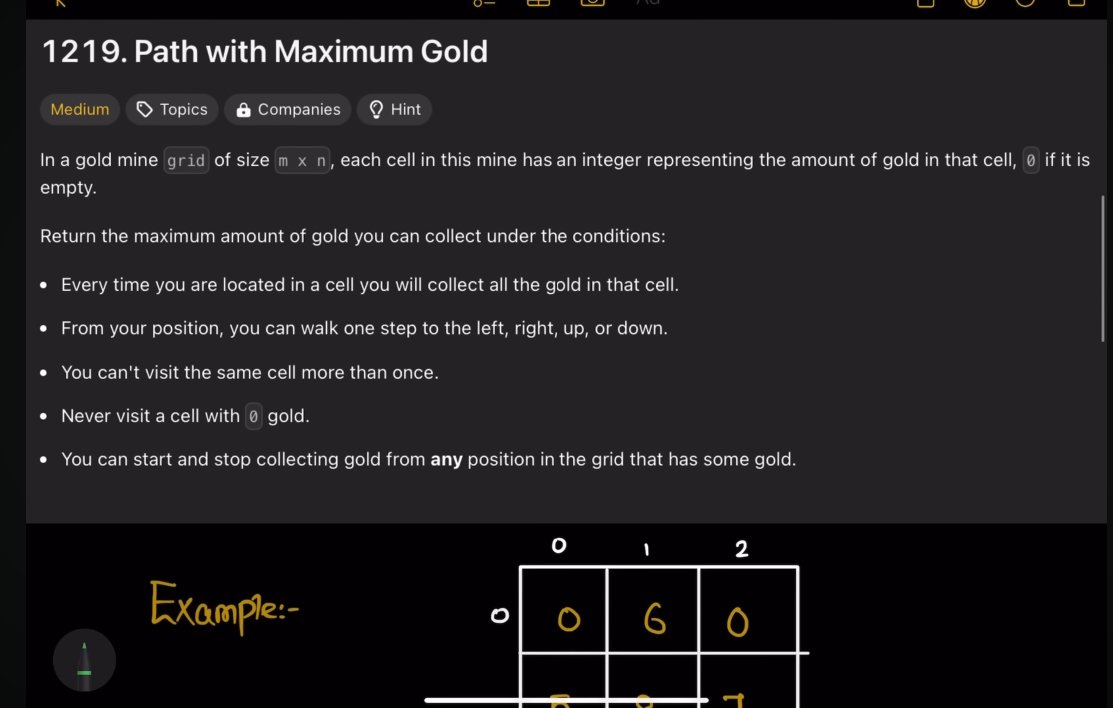
🚀 Day 158 | LeetCode 1219: Path with Maximum Gold 🏆
📌 Topic: Backtracking | Depth-First Search (DFS) | Recursion
Continuing my #200DaysChallenge with Rohit Negi Bhaiya (CoderArmy) and Aditya Tandon Guruji! 💻🔥
Day 94 #200daysChallenge with @mr_kay7 🚀
I’m excited to begin my new internship role with Techbiz Security as an Ethical Hacker! 🔐
Our first task was to study the CIA Triad, types of hackers, five phases of penetration testing, and the difference between Vulnerability
Day93 #200daysChallenge with @mr_kay7
🚩 FLAG 4 CAPTURED! 🔥
Finally completed Hacker101 CTF Micro-CMS Challenge 1! 🔐
The hint was: "Script tags are great, but what other options do you have?"
I investigated the existing button element, experimented with an


Day98 #200Dayschallenge @scriptedwebb
Dive into the raw HTTP access logs and spotted the exact attack sequence from IP 203.0.113.45
Brute Force: Multiple 401 failures on the admin user, trying passwords like 'admin123', 'password' and 'letmein'.
#AppSec #OWASP #SOCAnalyst
Day97 #200Dayschallenge @scriptedwebb
In this lab, I targeted the admin account using a Username Canonicalization flaw.
Instead of brute forcing the password, I registered a new account with the username aDmiN.
#CyberSecurity

Day97 #200Dayschallenge @scriptedwebb
In this lab, I targeted the admin account using a Username Canonicalization flaw.
Instead of brute forcing the password, I registered a new account with the username aDmiN.
#CyberSecurity
Day96 #200Dayschallenge @scriptedwebb
Windows Logging for SOC Wrapped! It’s easy to rely on polished SIEM alerts, but opening raw .evtx files in Event Viewer taught me where that data actually comes from.
#CyberSecurity #SOCAnalyst

Day93 #200daysChallenge with @mr_kay7
🚩 FLAG 4 CAPTURED! 🔥
Finally completed Hacker101 CTF Micro-CMS Challenge 1! 🔐
The hint was: "Script tags are great, but what other options do you have?"
I investigated the existing button element, experimented with an
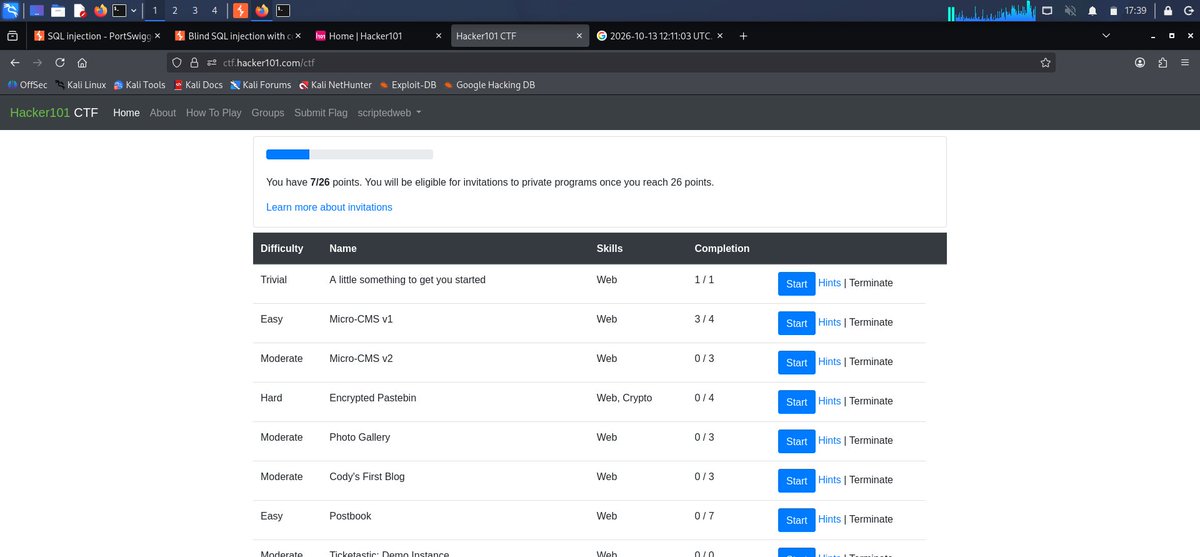
Day92 #200daysChallenge with @mr_kay7
Yesterday, I started my Hacker101 CTF journey to test my PortSwigger knowledge and prepare for Bug Bounty Hunting. 🔐
The challenges have been brain-racking, but every hint is a learning opportunity!


Day92 #200daysChallenge with @mr_kay7
Yesterday, I started my Hacker101 CTF journey to test my PortSwigger knowledge and prepare for Bug Bounty Hunting. 🔐
The challenges have been brain-racking, but every hint is a learning opportunity!
Day91 of #200daysChallenge with @mr_kay7
I completed a Portswigger lab where I was able to retrieve data from a user table with the table username and password, after which I was able to probe further to get administrator login details.
#Cybersecurity #PortSwigger #Pentesting


Day96 #200Dayschallenge @scriptedwebb
Windows Logging for SOC Wrapped! It’s easy to rely on polished SIEM alerts, but opening raw .evtx files in Event Viewer taught me where that data actually comes from.
#CyberSecurity #SOCAnalyst
Day95 #200Dayschallenge
Windows Logging for SOC, I analyzed raw authentication logs to track a live intrusion. Here's what I did, launched the raw Practice Security.evtx' file on the VM's desktop. This simulates working on forensic data outside of a full SIEM.
#SOCAnalyst

Day91 of #200daysChallenge with @mr_kay7
I completed a Portswigger lab where I was able to retrieve data from a user table with the table username and password, after which I was able to probe further to get administrator login details.
#Cybersecurity #PortSwigger #Pentesting
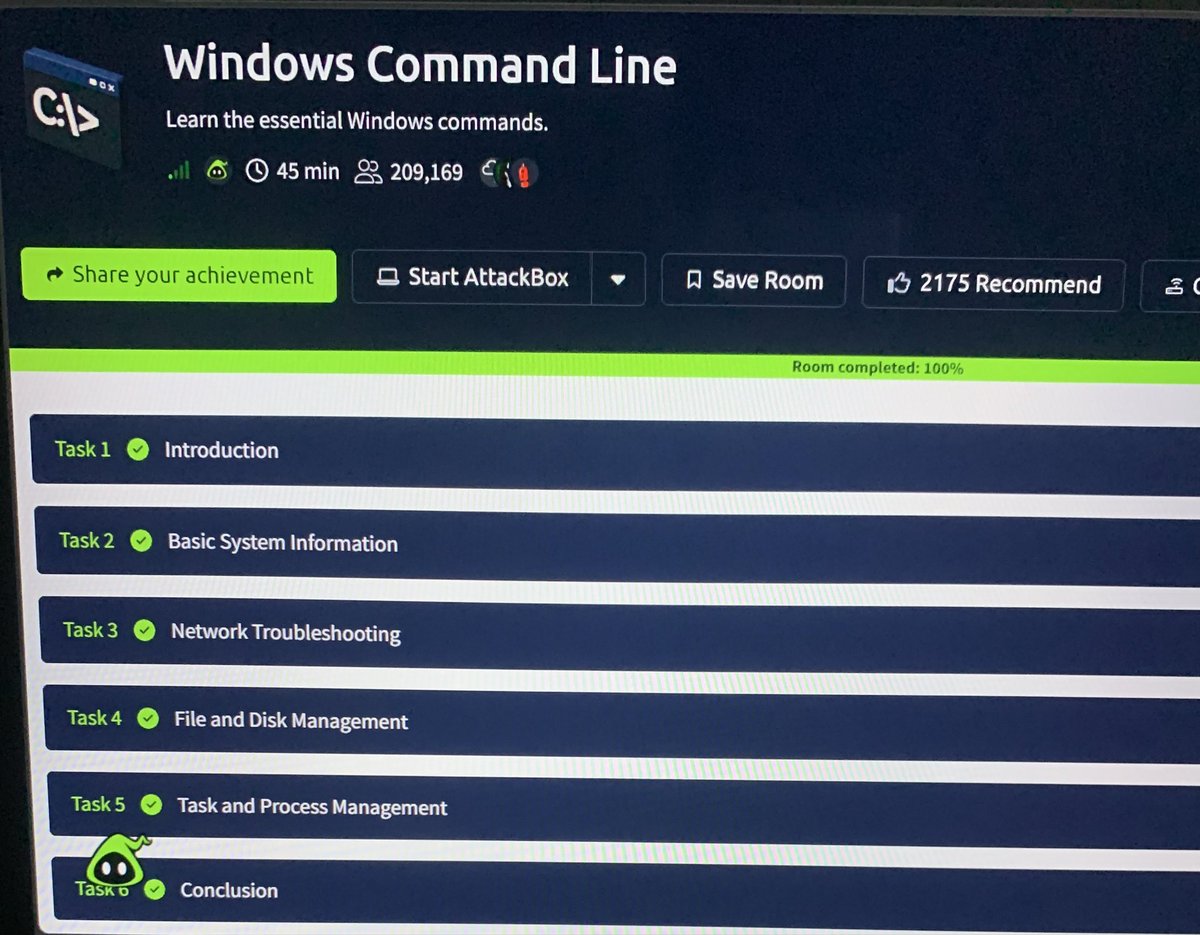
Day 90 #200daysChallenge with @mr_kay7 🚀
Another day, another opportunity to learn!
Today, we had a class on Linux Privilege Escalation. This is a topic I have already explored through hands-on simulations with Metasploitable 2 and DC-1.
However, while looking for new things

🚀 Day 128-129 — #Upskill_with_Dishank #200DaysChallenge
✅ System Design — Database Connection Pooling
• Why a single shared connection becomes a bottleneck by serializing queries
• Why creating a new DB connection per request can exhaust backend ports and database resources
• PostgreSQL uses a process-per-connection architecture, so every connection requires OS resources like CPU, memory and process/file-descriptor resources
• Connection pooling keeps a finite number of reusable connections
• Borrow → Query → Return → Reuse
• Pool size is a tuning problem: too small → waiting, too large → DB contention
• In horizontally scaled systems, total DB connections multiply across instances
✅ DSA @LeetCode Daily problems: Greedy + Bit Manipulation
✅ Key takeaway:
In system design, performance is often about controlling shared resources rather than simply adding more of them.
#LeetCode #SystemDesign #LearnInPublic #AI #DSA #CP


Day95 #200Dayschallenge
Windows Logging for SOC, I analyzed raw authentication logs to track a live intrusion. Here's what I did, launched the raw Practice Security.evtx' file on the VM's desktop. This simulates working on forensic data outside of a full SIEM.
#SOCAnalyst
Day94 #200Dayschallenge @scriptedwebb
When you're doing incident response, speed matters. Being comfortable in the CLI lets you grab system info, check running process and trace connections way faster than clicking through menus
#CyberSecurity #SOCAnalyst
Day 90 #200daysChallenge with @mr_kay7 🚀
Another day, another opportunity to learn!
Today, we had a class on Linux Privilege Escalation. This is a topic I have already explored through hands-on simulations with Metasploitable 2 and DC-1.
However, while looking for new things
Day 89 #200daysChallenge with @mr_kay7
Just completed OverTheWire Bandit Levels 11–21!
It wasn't easy as a beginner still learning Linux commands. I used AI as a learning guide, but I made sure I understood what each command does instead of blindly copying commands.

Last Seen Hashtags on Sotwe
sudanese sex
فطوم_سلطانة
Seen from Egypt
mixels
Seen from Mexico
snapchat
Seen from Italy
minichat()************************************************************************************** **filter:native_video()
Seen from Japan
k9girls() +filter:native_video
Seen from Turkey
hijabi uk
Seen from Turkey
Tails #NSFW
Seen from United States
shsgirl
Seen from South Africa
丝袜
Seen from Korea
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers