Day82 #200daysChallenge with @mr_kay7
🔐 Can I Still Hack It? - VulnBank Home Lab
Today I practiced Privilege Escalation in my authorized VulnBank lab.
🔹 Vertical Privilege Escalation
I inspected a JWT, identified the "isadmin=false" claim, modified it
Day81 #200daysChallenge with @mr_kay7
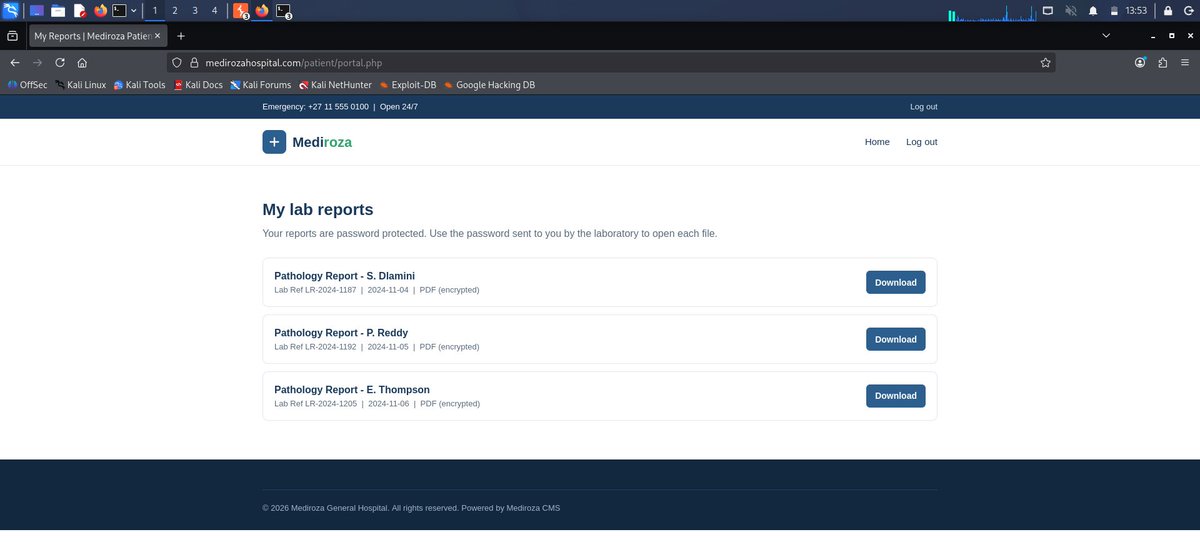
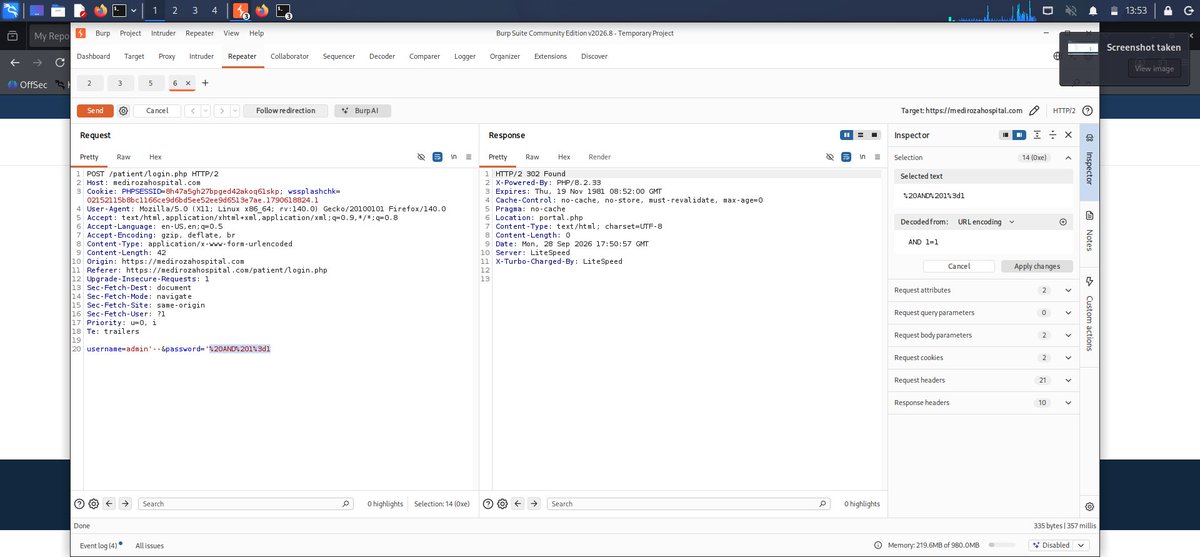
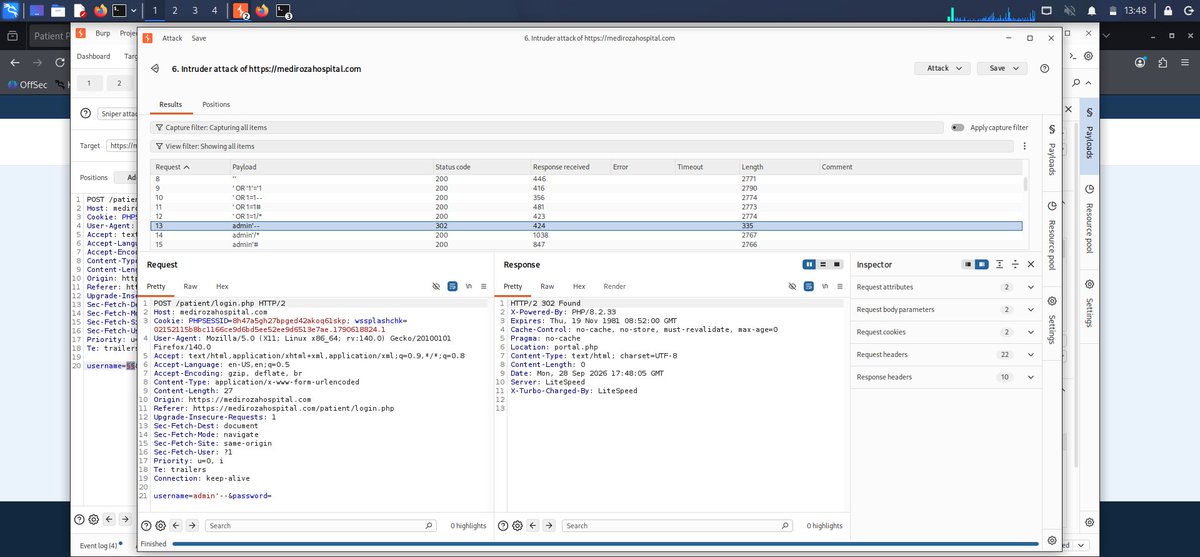
Completed an authorized Black-Box Penetration Test 🔐
The assessment covered:
• Initial Access
• File Exfiltration
• PDF password cracking to assess exposure of PHI
• Post-Exploitation: testing access to staff salary & shareholder data
🔥 Day 98 of my #200daysChallenge with @mr_kay7
🏆 NETWORKWALKS INTERNSHIP ACHIEVEMENT!
✅ Week 1: 100/100
✅ Week 2: 100/100
✅ Week 3: 100/100
✅ Week 4: 100/100
🎯 Final Internship Exam: 99/100!
I'm grateful for the knowledge gained and the progress made throughout this
🔥 Day 98 of my #200daysChallenge with @mr_kay7
🏆 NETWORKWALKS INTERNSHIP ACHIEVEMENT!
✅ Week 1: 100/100
✅ Week 2: 100/100
✅ Week 3: 100/100
✅ Week 4: 100/100
🎯 Final Internship Exam: 99/100!
I'm grateful for the knowledge gained and the progress made throughout this
Day97 #200daysChallenge with @mr_kay7
I successfully completed a PortSwigger Web Security Academy lab on Blind SQL Injection! 🎯
I learned how the SQL SUBSTRING() function can help retrieve an administrator's password one character at a time by testing the application's
@yourclouddude B. This is a stealth scan to see if the host server is online...three way handshake wasn't complete and as such, I will say the answer is B.
Day97 #200daysChallenge with @mr_kay7
I successfully completed a PortSwigger Web Security Academy lab on Blind SQL Injection! 🎯
I learned how the SQL SUBSTRING() function can help retrieve an administrator's password one character at a time by testing the application's
Day 96 of #200DaysChallenge with @mr_kay7 🚀
Today, I strengthened my networking fundamentals during my TechBiz Security Ethical Hacking Internship.
🔹 IP vs MAC addresses
🔹 The 7 layers of the OSI model
🔹 10 common network ports and their services
🔹 TCP vs UDP
@mr_kay7 responses to true/false conditions.
Example payload from the lab:
' AND (SELECT SUBSTRING(password,1,1) FROM users WHERE username='administrator')='a
This exercise helped me understand how attackers can infer sensitive information even when an application doesn't
@mr_kay7 🔹 Practical network configuration using Windows ipconfig and ipconfig /all
I completed TryHackMe's What is Networking? room and documented my practical work.
I'm building my foundation one concept at a time. 🛡️
#CyberSecurity#Networking#EthicalHacking#TryHackMe
Day 96 of #200DaysChallenge with @mr_kay7 🚀
Today, I strengthened my networking fundamentals during my TechBiz Security Ethical Hacking Internship.
🔹 IP vs MAC addresses
🔹 The 7 layers of the OSI model
🔹 10 common network ports and their services
🔹 TCP vs UDP
Day 95 of #200daysChallenge with @mr_kay7
Today, I took my time to study the three main types of Cross-Site Scripting (XSS): Reflected XSS, Stored XSS, and DOM-based XSS.
🔹 Reflected XSS: This occurs when a website takes malicious input from a request and includes it unsafely
Day 95 of #200daysChallenge with @mr_kay7
Today, I took my time to study the three main types of Cross-Site Scripting (XSS): Reflected XSS, Stored XSS, and DOM-based XSS.
🔹 Reflected XSS: This occurs when a website takes malicious input from a request and includes it unsafely
Day 94 #200daysChallenge with @mr_kay7 🚀
I’m excited to begin my new internship role with Techbiz Security as an Ethical Hacker! 🔐
Our first task was to study the CIA Triad, types of hackers, five phases of penetration testing, and the difference between Vulnerability
@mr_kay7 For example, using innerHTML with untrusted input can introduce this vulnerability.
Today, I learned that the key difference between these three types of XSS is how the malicious input is handled and how it reaches the victim's browser.