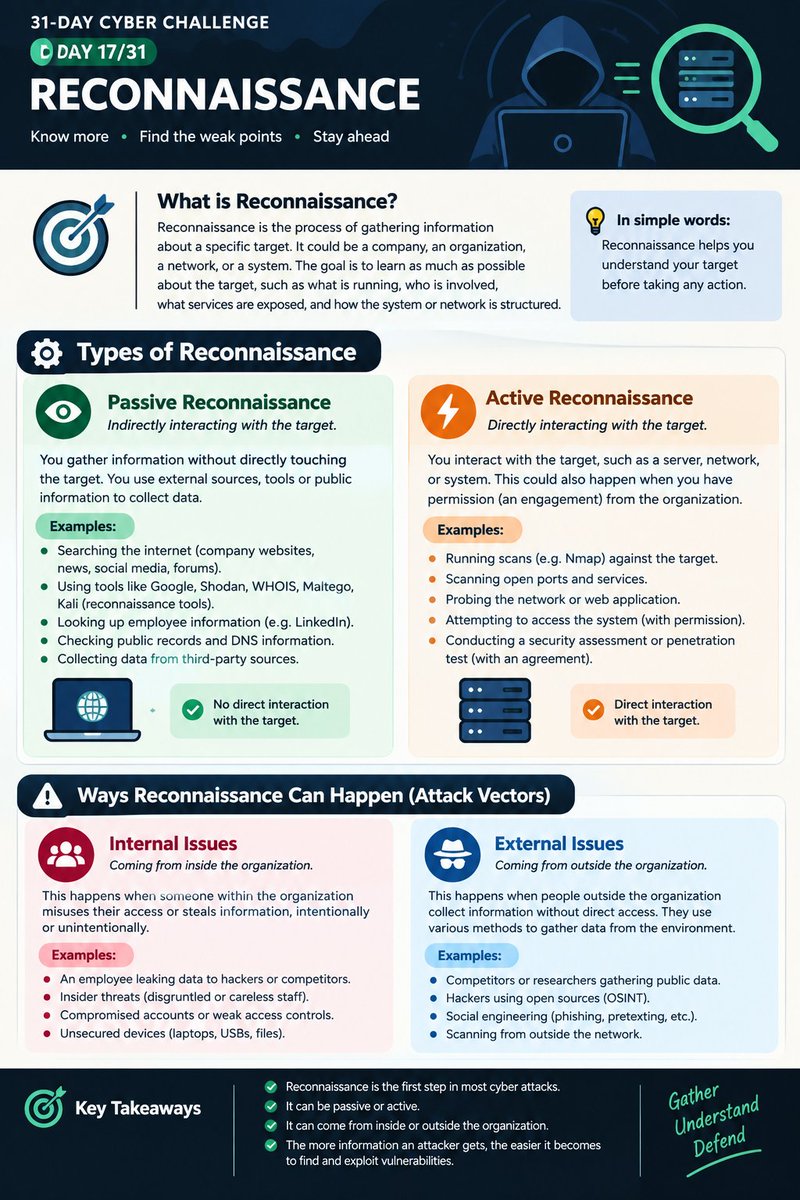
🛡️ Day 1 2/31 CyberChallenge
Completed a PortSwigger lab on User ID Controlled by Request Parameter.
I Learned how manipulating user IDs can expose sensitive information, such as API keys, when access controls are weak.
Every step counts! 💻
#CyberSecurity#WebSecurity
Day 13/31 🔐 PortSwigger Web Security Academy | Hands-On Lab
Solved the Unprotected Admin Functionality with Unpredictable URL lab! 💻
🎯 Goal: Discover the hidden admin panel and delete the user carlos.
Another step forward in my web security and penetration testing journey! 🚀
🛡️ Day 14/31 #CyberChallenge
Today, I explored Horizontal Privilege Escalation through a hands-on lab on https://t.co/ikheMGQ6z3. 💻
I learned how broken access controls can allow a user to access another user's data without permission.
Learning by doing, one lab at a time! 🚀
🛡️ Day 15/31 of my Cyber Challenge
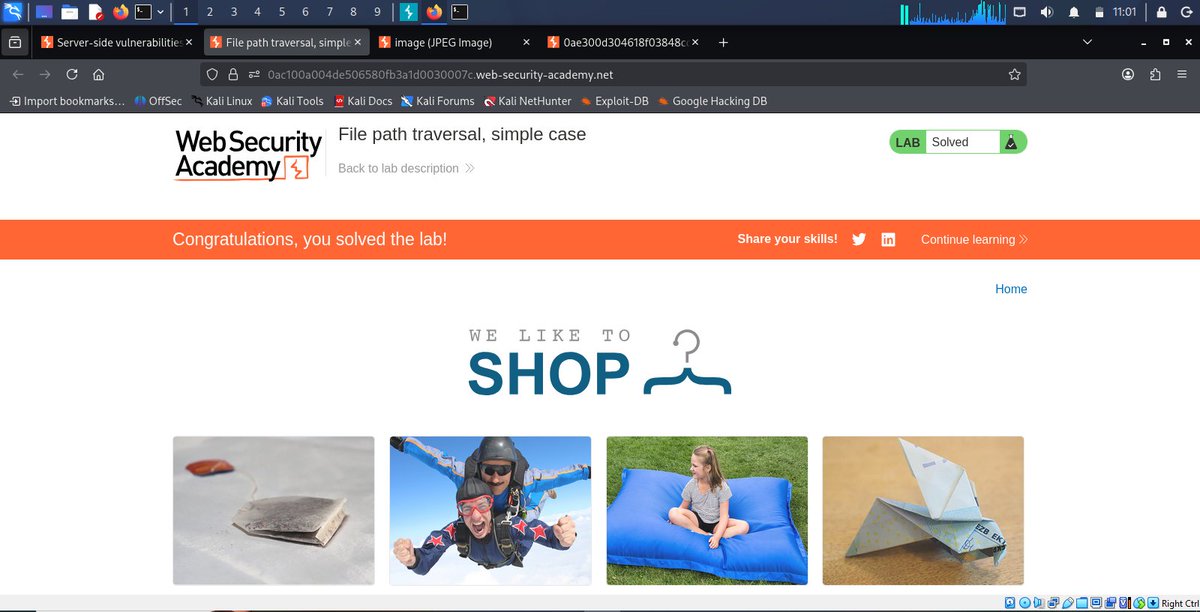
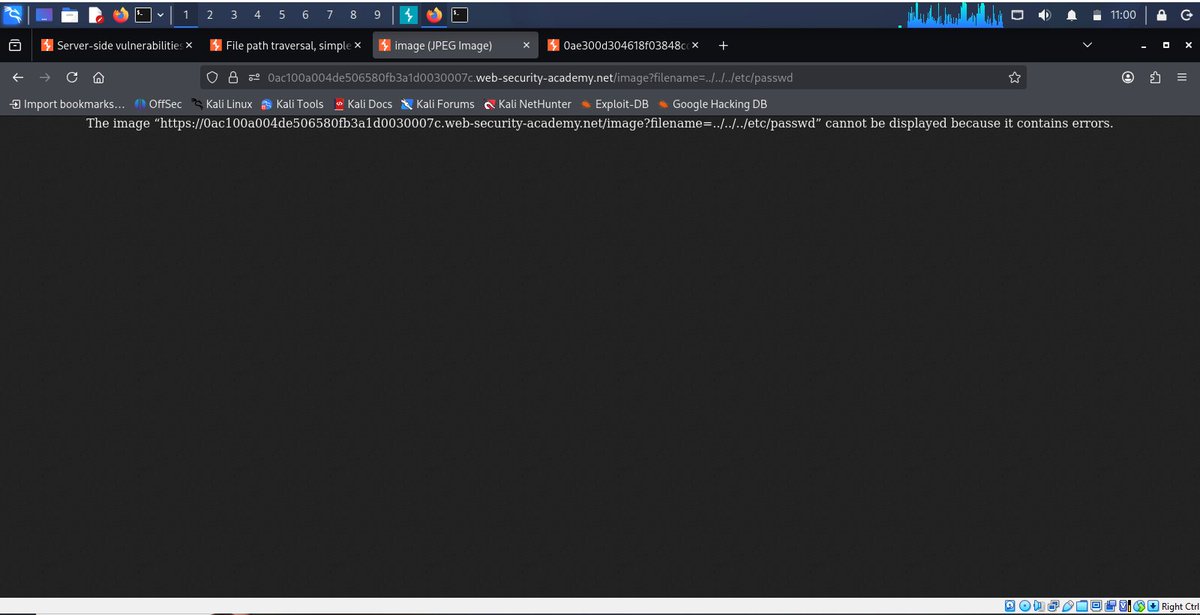
Completed a Path Traversal lab on PortSwigger Web Security Academy today. 💻
Learning how attackers exploit file path vulnerabilities and how to identify them.
One lab at a time, one step closer! 🚀
#Cybersecurity#EthicalHacking#PortSwigger
Excited to share that I’ve been selected for a Cybersecurity Internship with Networkwalks IT Solutions & Training.
I’m looking forward to learning, gaining more hands-on experience, and growing my skills in cybersecurity. @networkwalks#Cybersecurity#Internship#EthicalHacking