

Top Tweets for #Eventlogs

Method for structuring raw event logs by segmenting event streams and mapping them to known processes: “#Segmentation and #ProcessAssignment of Semi-Structured #EventLogs” by P. Przymus, K. Rykaczewski, J. Zieliński, Ł. Mikulski. ACSIS Vol. 43 p. 231–241; https://t.co/P6QKsHnIkR

Fix Active Directory account lockouts with #PowerShell https://t.co/lk89jP0qUq via @techtargetnews #ActiveDirectory #WindowsServer #ADAccountLockouts #PowerShellScripting #EventLogs #ITAutomation #sysadmin

Understanding the Windows Server Event Log ✅
https://t.co/HJHoqYLqk8
#Winserv #WindowsServer #Hyperv #WindowsServer2025 #ITPro #Eventlogs
via @orinthomas 🚀

Active Directory: Advanced Threat Hunting - MITRE ATT&CK Techniques and the Windows Eventlog ID's!
@Microsoft @github @msftsecurity @MITREattack #Microsoft #ActiveDirectory #MITREATT&CK #Eventlogs #Information #mvpbuzz #coolstuff #communityrocks
👇👇👇👇
https://t.co/4DeO71zPn1
Active Directory: Advanced Threat Hunting - Operating System Configuration Changes!
@Microsoft @github @MITREattack @msftsecurity @MVPAward #Microsoft #ActiveDirectory #MITREATT&CK #Eventlogs #Windows #mvpbuzz #coolstuff #communityrocks
👇👇👇👇
https://t.co/j7nxnyEmNR
Active Directory: Advanced Threat Hunting - Credential Theft and Ransomware Infection!
@Microsoft @github @MITREattack @msftsecurity @MVPAward #Microsoft #ActiveDirectory #MITREATT&CK #Eventlogs #Windows #mvpbuzz #coolstuff #communityrocks
👇👇👇👇
https://t.co/U8loByaCWU

Active Directory: Advanced Threat Hunting - MITRE ATT&CK Techniques and the Windows Eventlog ID's!
@Microsoft @msftsecurity @DirectoryRanger @github #Microsoft #ActiveDirectory #MITREATT&CK #Eventlogs #Information #mvpbuzz #coolstuff #communityrocks
👇👇
https://t.co/4DeO71zhxt
Active Directory: Advanced Threat Hunting - Advanced hunting for group policy settings (Default Domain Controllers Policy)!
@Microsoft @github @MITREattack @msftsecurity #Microsoft #ActiveDirectory #MITREATT&CK #Eventlogs #mvpbuzz #coolstuff
👇👇👇👇
https://t.co/Ur9Iu7IZmG
Active Directory: Advanced Threat Hunting - Credential Theft and Ransomware Infection!
@Microsoft @github @MITREattack @msftsecurity @MVPAward #Microsoft #ActiveDirectory #MITREATT&CK #Eventlogs #Windows #mvpbuzz #coolstuff #communityrocks
👇👇👇👇
https://t.co/U8loBya57m
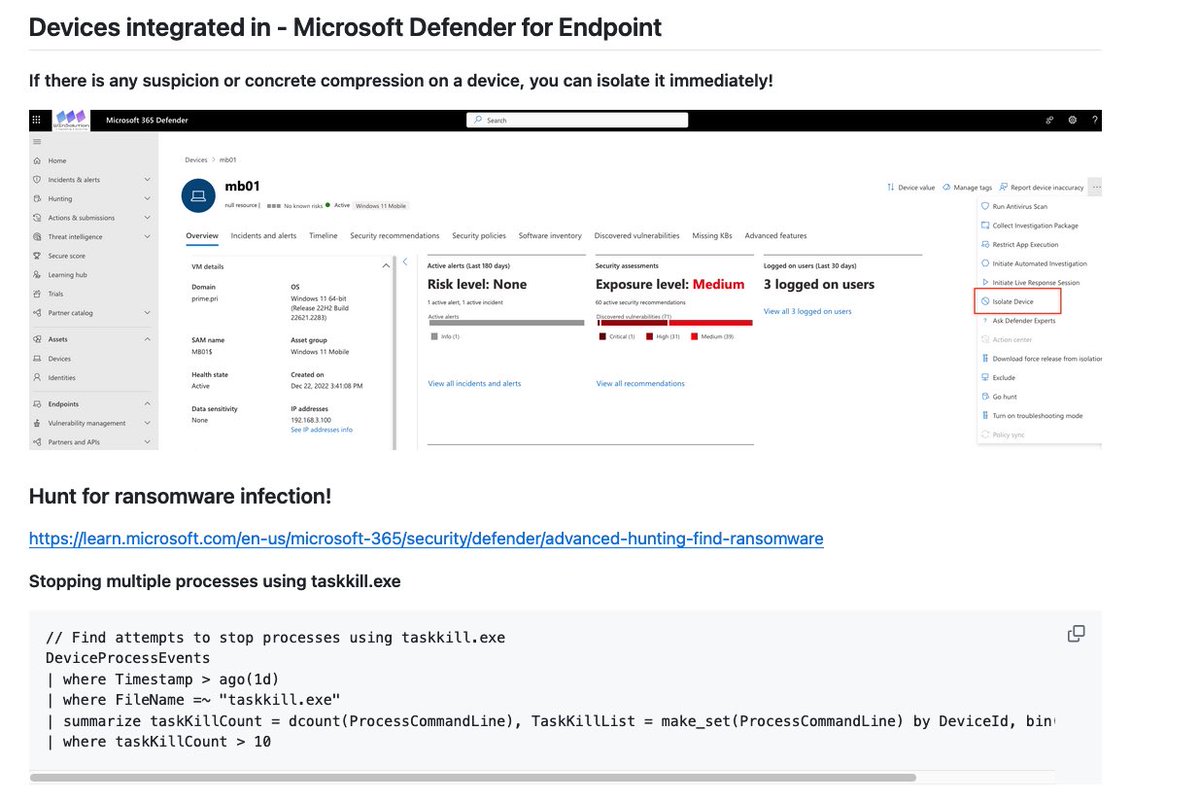
Active Directory: Advanced Threat Hunting - Operating System Configuration Changes!
@Microsoft @github @MITREattack @msftsecurity @MVPAward #Microsoft #ActiveDirectory #MITREATT&CK #Eventlogs #Windows #mvpbuzz #coolstuff #communityrocks
👇👇👇👇
https://t.co/j7nxnyEmNR
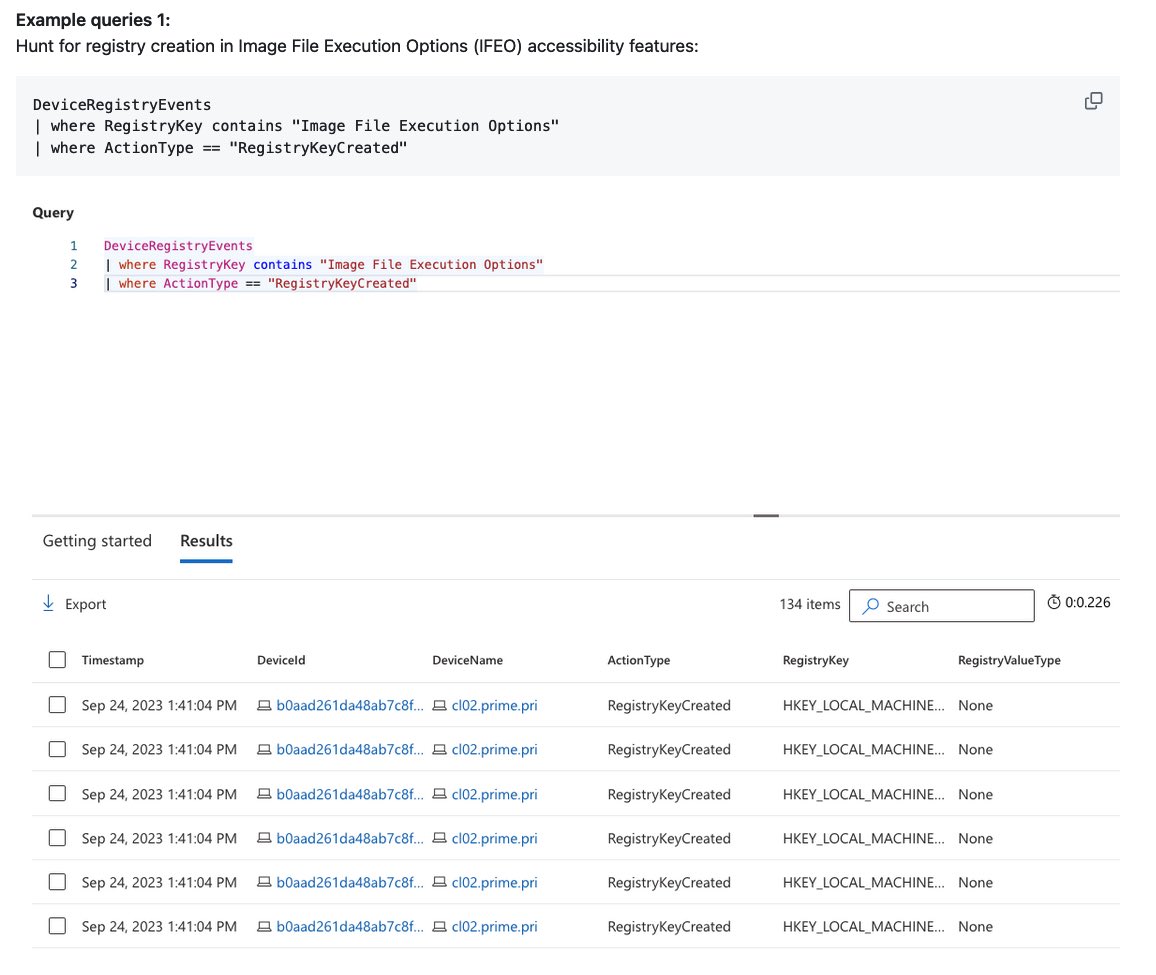

Confused by #EventLogs? 🫨Let's demystify them with a real-world example!
See a #Uniswap transfer in action on #OKXExplorer
https://t.co/OxA2OBRczt

Check out our latest! Unlocking inpatient #workload insights w/ #EHR #EventLogs w/ @TKannampallil @KenistonAngela @missamyyu @dyrbye https://t.co/rcSjokOC3l @AmerMedicalAssn @CHWENews @vineet_chopra @HOMERuN_Network @CUDivHospMed @ChristineSinsky @JHospMedicine @SamirShahMD

Detecting #browser #data theft using #Windows #EventLogs:
Since 2013, #Chromium has applied the #CRYPTPROTECT_AUDIT flag to #DPAPI calls, ensuring an #audit log is generated when #decryption occurs. This aids in detecting #datatheft, with three key steps:

Windows User Account Forensics - I have just completed this room! Check it out: https://t.co/VyZbnMSoKi #tryhackme #WindowsUserAccountForensics #WindowsForensics #WindowsSecurity #UserAccountAnalysis #RegistryForensics #EventLogs #IncidentResponse #DigitalForensics #ForensicAnalysis via @tryhackme


If you use #Hayabusa to search for suspicious behavior in eventlogs, remember that @SecurityYamato has a great tool called #Takajo to analyze the output results.
Now, it's available in #Velociraptor:
https://t.co/4eh1VWI2lM
#dfir #incidentresponse #eventlogs
Active Directory: Advanced Threat Hunting - Local host infection and malicious behavior!
@Microsoft @github @MITREattack @msftsecurity #Microsoft #ActiveDirectory #MITREATT&CK #Eventlogs #Windows #mvpbuzz #coolstuff #communityrocks
👇👇👇👇
https://t.co/GFnePLVH50


🕵️♂️ Decoding the enigma of Event ID 0 in Windows Event Logs with Python!
🐍 Unravel missing messages, explore system ..
#Cybersecurity #Python #EventLogs #TechEnigma
@"Navigating the Digital Frontier: Decoding Event Logs with Python"https://t.co/j7nvKoH2u9 on @LinkedIn
Active Directory: Advanced Threat Hunting - Credential Theft and Ransomware Infection!
@Microsoft @github @MITREattack @msftsecurity #Microsoft #ActiveDirectory #MITREATT&CK #Eventlogs #Windows #mvpbuzz #coolstuff #communityrocks
👇👇👇👇
https://t.co/U8loBya57m
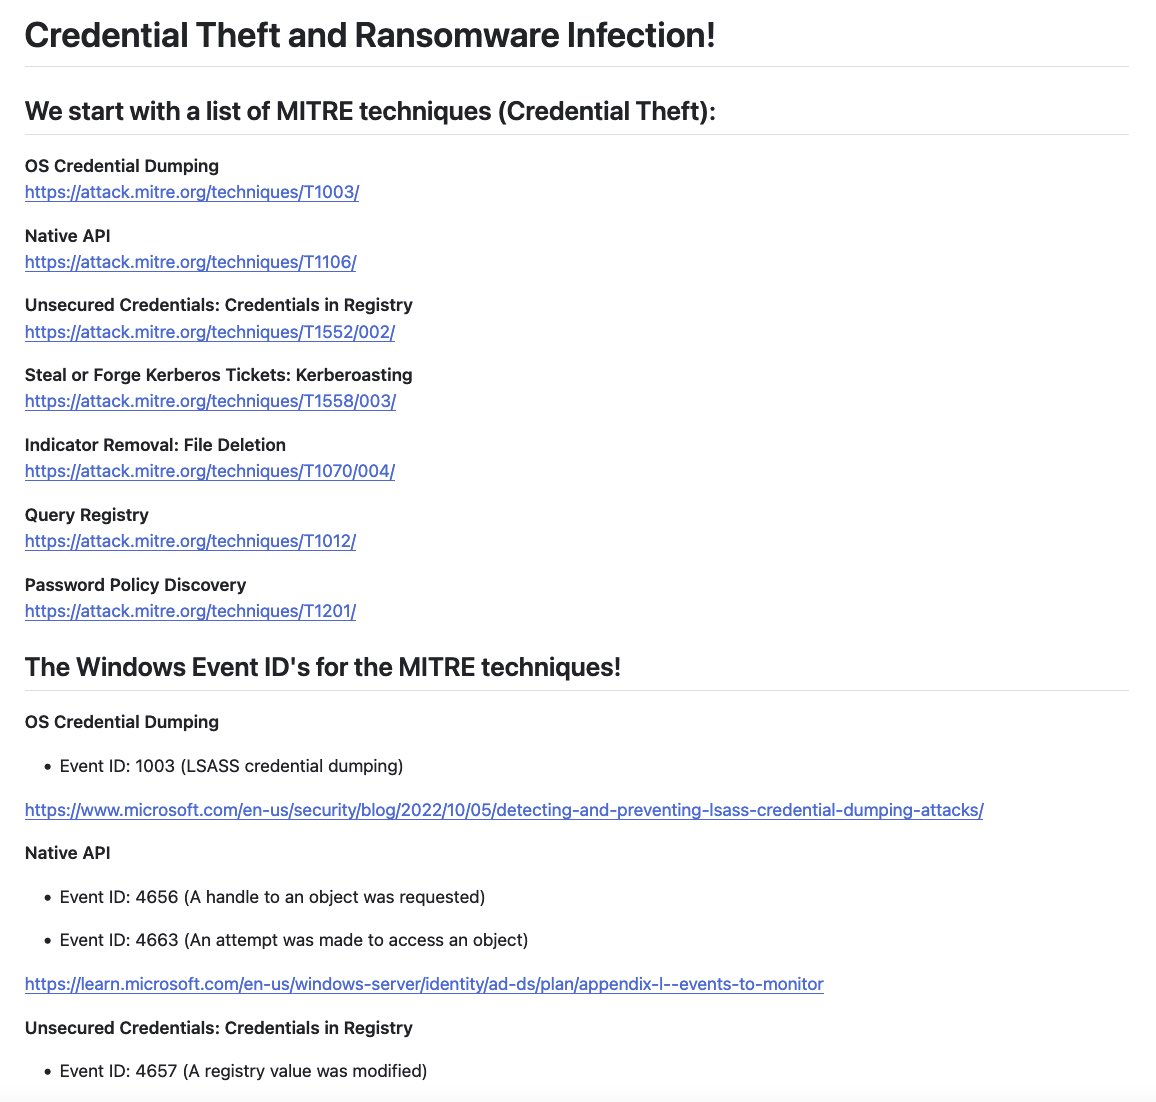

New room Log Universe from @tryhackme : Explore log files from various systems and learn how to carve data to adopt a course of action!
I learned today about new logging tool called "ULogViewer"
https://t.co/NngCshzrVK
#tryhackme #logs #eventlogs #ULogViewer

☣️Active Directory: Advanced Threat Hunting - Credential Theft and Ransomware Infection!☣️
@Microsoft @github @MITREattack @msftsecurity #Microsoft #ActiveDirectory #MITREATT&CK #Eventlogs #Windows #mvpbuzz #coolstuff #communityrocks
👇👇👇👇
https://t.co/U8loBya57m

Last Seen Hashtags on Sotwe
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers