

Top Tweets for #JSGuLdr

⚠️ #JSGuLdr is a multi-stage JavaScript-to-PowerShell loader delivering #PhantomStealer. It uses obfuscation, COM execution, and in-memory loading to minimize on-disk exposure
See the analysis of this month’s threats and detection takeaways for SOC teams: https://t.co/vDrTX7yv1s
⚠️ #XWorm in PNG files, #JSGuLdr’s three-stage loader, Linux #ransomware, Android RATs; November was packed with multi-layered attacks.
See the full analysis of the month’s major threats and key detection takeaways for SOC teams 👇
https://t.co/HW9c7GRH5f

JSGuLdr: Multi-Stage Loader Delivering PhantomStealer
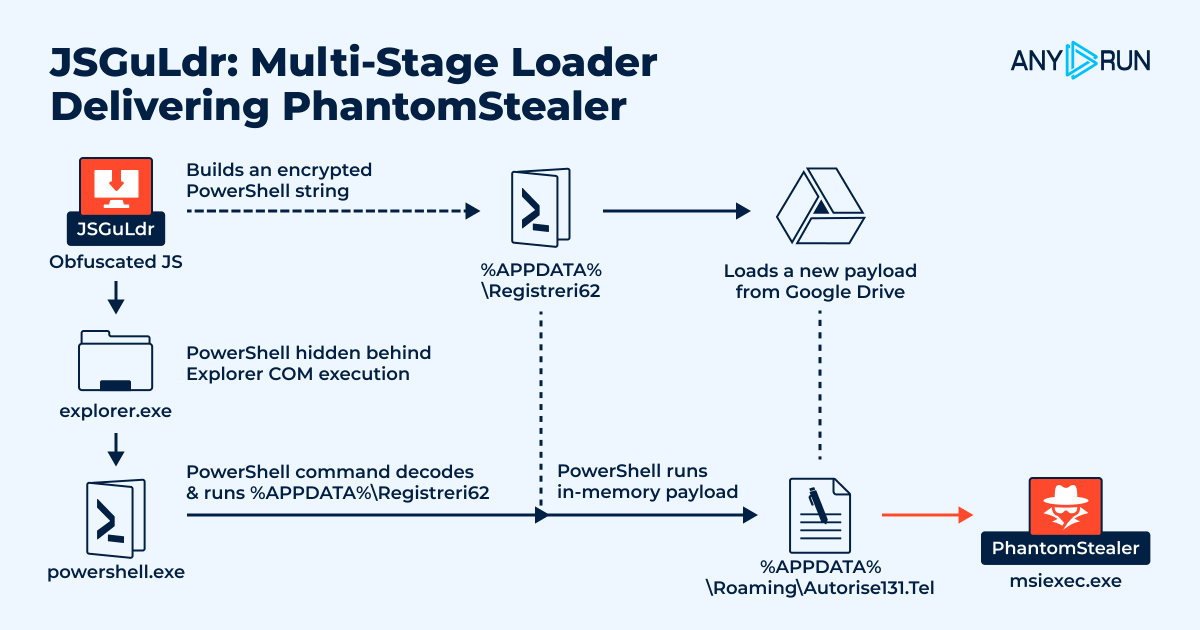
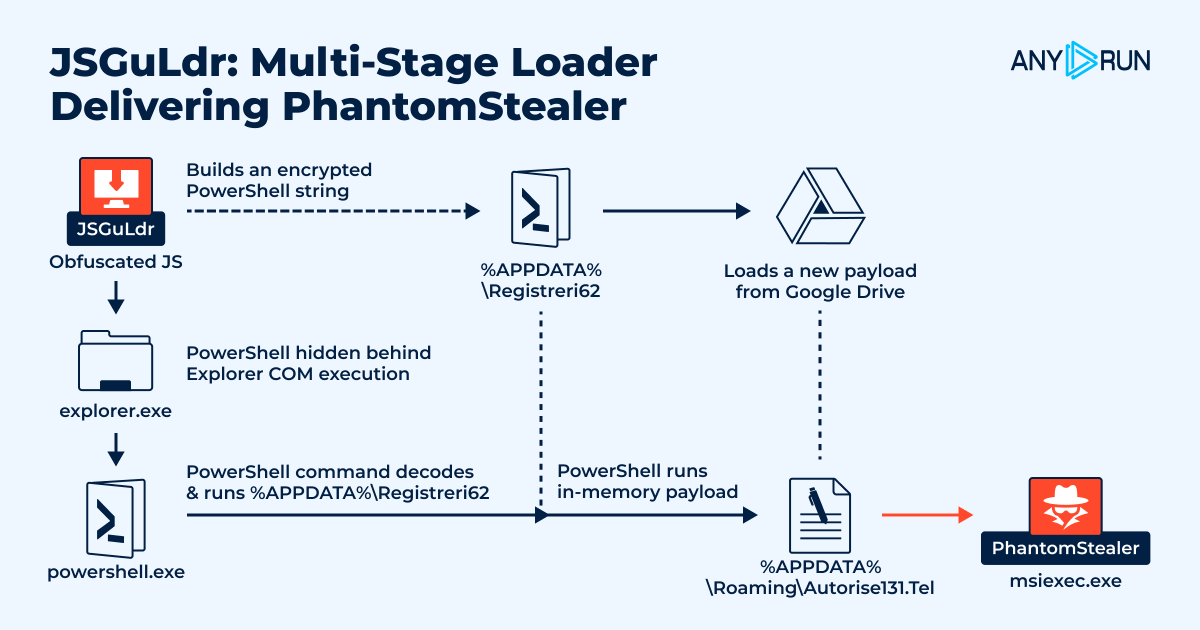
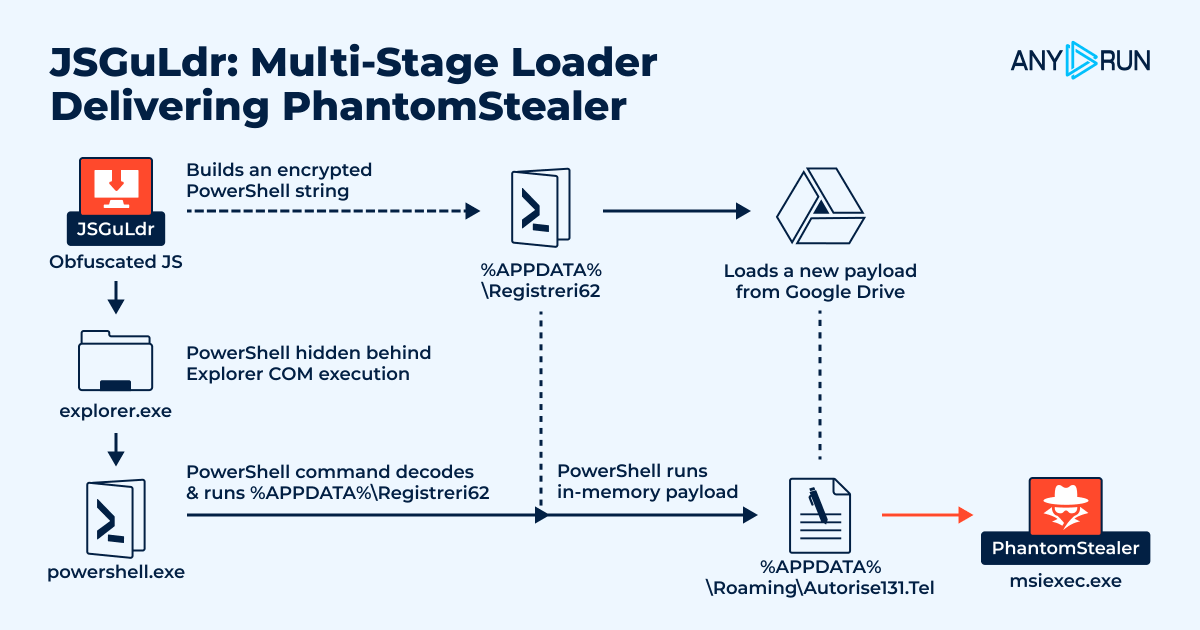
#ANYRUN researchers identified #JSGuLdr, a multi-stage JavaScript-to-PowerShell loader used to deliver #PhantomStealer. A JScript file triggers PowerShell through an Explorer COM call, pulls the second stage from %APPDATA%\Registreri62, then uses Net.WebClient to fetch an encrypted payload from Google Drive into %APPDATA%\Autorise131[.]Tel. The payload is decoded in memory and loaded, with PhantomStealerinjected into msiexec.exe.
Execution chain: wscript.exe ➡️ explorer.exe (svchost.exe) ➡️ explorer.exe (COM) ➡️ powershell.exe ➡️ msiexec.exe
👉 See analysis session: https://t.co/Ci9emGscMk…
👉 Read full analysis: https://t.co/3VAvvosOGt…


JSGuLdr: Multi-Stage Loader Delivering PhantomStealer
#ANYRUN researchers identified #JSGuLdr, a multi-stage JavaScript-to-PowerShell loader used to deliver #PhantomStealer. A JScript file triggers PowerShell through an Explorer COM call, pulls the second stage from %APPDATA%\Registreri62, then uses Net.WebClient to fetch an encrypted payload from Google Drive into %APPDATA%\Autorise131[.]Tel. The payload is decoded in memory and loaded, with PhantomStealerinjected into msiexec.exe.
Execution chain: wscript.exe ➡️ explorer.exe (svchost.exe) ➡️ explorer.exe (COM) ➡️ powershell.exe ➡️ msiexec.exe
👉 See analysis session: https://t.co/mZCoOkUSdy
👉 Read full analysis: https://t.co/wMEghiOYPp
🚨 𝗝𝗦𝗚𝘂𝗟𝗱𝗿: 𝗠𝘂𝗹𝘁𝗶-𝗦𝘁𝗮𝗴𝗲 𝗟𝗼𝗮𝗱𝗲𝗿 𝗗𝗲𝗹𝗶𝘃𝗲𝗿𝗶𝗻𝗴 𝗣𝗵𝗮𝗻𝘁𝗼𝗺𝗦𝘁𝗲𝗮𝗹𝗲𝗿
TL;DR: We identified #JSGuLdr, a multi-stage JavaScript-to-PowerShell loader used to deliver #PhantomStealer. A JScript file triggers PowerShell through an Explorer COM call, pulls the second stage from %APPDATA%\Registreri62, then uses Net.WebClient to fetch an encrypted payload from Google Drive into %APPDATA%\Autorise131[.]Tel. The payload is decoded in memory and loaded, with PhantomStealer injected into msiexec.exe.
⚠️ The chain combines obfuscation, cloud-hosted payloads, COM-based execution, and fileless in-memory loading, making it difficult to detect with automated or static detection solutions.
Execution chain: wscript.exe ➡️ explorer.exe (svchost.exe) ➡️ explorer.exe (COM) ➡️ powershell.exe ➡️ msiexec.exe
👨💻 See analysis session: https://t.co/i9EB1xWeyq
Stage 1️⃣: The sample is an obfuscated JScript script signed with a fake Authenticode certificate to bypass trust checks. It builds an encrypted PowerShell string and writes it to %APPDATA%\Registreri62, forming the second stage.
Through Shell.Application and Explorer COM interaction, the script launches powershell.exe under explorer.exe, masking the execution chain as normal user activity.
🎯 TTPs: Obfuscation (T1027), Signed binary proxy execution (T1553.006), COM interaction (T1559.001), Proxy execution via explorer.exe (T1218)
Stage 2️⃣: The PowerShell code decodes and runs %APPDATA%\Registreri62, reconstructing hidden commands (iex) and loading a new payload from Google Drive. The file is saved as an encrypted container for the third stage.
🎯 TTPs: Encrypted payload download (T1105), Cloud storage abuse (T1105), Local file staging (T1074.001)
Stage 3️⃣: Autorise131[.]Tel acts as an on-disk container for an in-memory payload.
The same PowerShell process decodes it, extracts bytes, and executes the result through Invoke-Expression, running PhantomStealer filelessly in memory.
The payload is injected into msiexec.exe, enabling PhantomStealer to steal data.
🎯 TTPs: Fileless execution (T1059.001), Reflective .NET module loading (T1620), Process injection (T1055), Proxy execution via msiexec.exe (T1218.007)
🔍 Track similar activity and pivot from IOCs using this TI Lookup search query: https://t.co/JFmvJO4gI4
#IOCs:
URL: hxxps://drive[.]google[.]com/uc?export=download&id=1gUB_fKBej5Va_l3ZSEXk_7r5Q4EeJuwd
Files: %APPDATA%\Registreri62, %APPDATA%\Autorise131[.]Tel
CMD: powershell.exe "$Citize=$env:appdata+'\Registreri62';$Guazuma=gc $Citize;$Aristape=$Guazuma[4460..4462] -join ''"
🚀 Gain fast detection and full visibility with #ANYRUN. Sign up: https://t.co/jwHNIfYXcC
#ExploreWithANYRUN
🚨 𝗝𝗦𝗚𝘂𝗟𝗱𝗿: 𝗠𝘂𝗹𝘁𝗶-𝗦𝘁𝗮𝗴𝗲 𝗟𝗼𝗮𝗱𝗲𝗿 𝗗𝗲𝗹𝗶𝘃𝗲𝗿𝗶𝗻𝗴 𝗣𝗵𝗮𝗻𝘁𝗼𝗺𝗦𝘁𝗲𝗮𝗹𝗲𝗿
TL;DR: We identified #JSGuLdr, a multi-stage JavaScript-to-PowerShell loader used to deliver #PhantomStealer. A JScript file triggers PowerShell through an Explorer COM call, pulls the second stage from %APPDATA%\Registreri62, then uses Net.WebClient to fetch an encrypted payload from Google Drive into %APPDATA%\Autorise131[.]Tel. The payload is decoded in memory and loaded, with PhantomStealer injected into msiexec.exe.
⚠️ The chain combines obfuscation, cloud-hosted payloads, COM-based execution, and fileless in-memory loading, making it difficult to detect with automated or static detection solutions.
Execution chain: wscript.exe ➡️ explorer.exe (svchost.exe) ➡️ explorer.exe (COM) ➡️ powershell.exe ➡️ msiexec.exe
👨💻 See analysis session: https://t.co/i9EB1xWeyq
Stage 1️⃣: The sample is an obfuscated JScript script signed with a fake Authenticode certificate to bypass trust checks. It builds an encrypted PowerShell string and writes it to %APPDATA%\Registreri62, forming the second stage.
Through Shell.Application and Explorer COM interaction, the script launches powershell.exe under explorer.exe, masking the execution chain as normal user activity.
🎯 TTPs: Obfuscation (T1027), Signed binary proxy execution (T1553.006), COM interaction (T1559.001), Proxy execution via explorer.exe (T1218)
Stage 2️⃣: The PowerShell code decodes and runs %APPDATA%\Registreri62, reconstructing hidden commands (iex) and loading a new payload from Google Drive. The file is saved as an encrypted container for the third stage.
🎯 TTPs: Encrypted payload download (T1105), Cloud storage abuse (T1105), Local file staging (T1074.001)
Stage 3️⃣: Autorise131[.]Tel acts as an on-disk container for an in-memory payload.
The same PowerShell process decodes it, extracts bytes, and executes the result through Invoke-Expression, running PhantomStealer filelessly in memory.
The payload is injected into msiexec.exe, enabling PhantomStealer to steal data.
🎯 TTPs: Fileless execution (T1059.001), Reflective .NET module loading (T1620), Process injection (T1055), Proxy execution via msiexec.exe (T1218.007)
🔍 Track similar activity and pivot from IOCs using this TI Lookup search query: https://t.co/JFmvJO4gI4
#IOCs:
URL: hxxps://drive[.]google[.]com/uc?export=download&id=1gUB_fKBej5Va_l3ZSEXk_7r5Q4EeJuwd
Files: %APPDATA%\Registreri62, %APPDATA%\Autorise131[.]Tel
CMD: powershell.exe "$Citize=$env:appdata+'\Registreri62';$Guazuma=gc $Citize;$Aristape=$Guazuma[4460..4462] -join ''"
🚀 Gain fast detection and full visibility with #ANYRUN. Sign up: https://t.co/jwHNIfYXcC
#ExploreWithANYRUN
Last Seen Hashtags on Sotwe
brosis since:2026-09-9 filter:videos
Seen from United States
navySSR
Seen from United States
wheredobrokenheartsgo
Seen from Spain
ballbursting
Seen from United Kingdom
mallu aunty
Seen from United States
Ring_Ring_Ring
Seen from United States
youngpussy
Seen from Greece
เย็ดแม่แท้ๆ
Seen from Thailand
عمه_عنيفة
Seen from United States
เจ้อีฟno1
Seen from Thailand
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90.1M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers