

Top Tweets for #KRYBIT

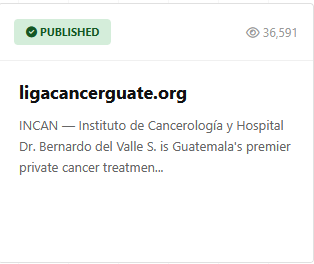
🔴🇬🇹Recordemos que el grupo KryBit fue el que listó al hospital en su sitio DLS y describió que habían robado 78.11 GB de información. Además, en la lista de archivos se pueden observar datos personales y sensibles de salud de pacientes.
#ransomware #StopRansomware #KryBit #Guatemala #ciberseguridad

Actor: #krybit
Victim: https://t.co/kHXmjOIh9T
Date: 2026-09-20 20:20:42 UTC+3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#krybit” Ransomware group has added https://t.co/kHXmjOIh9T to its victims.
Actor: #krybit
Victim: https://t.co/n3JSCQ7ZKO
Date: 2026-09-18 05:18:44 UTC+3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#krybit” Ransomware group has added https://t.co/n3JSCQ7ZKO to its victims.
Actor: #krybit
Victim: https://t.co/RaEhfKuWCI
Date: 2026-09-18 04:15:17 UTC+3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#krybit” Ransomware group has added https://t.co/RaEhfKuWCI to its victims.

#ThreatProtection #KryBit #Ransomware, read more about Symantec's protection: https://t.co/o8o121VLr3 #malware

#KRYBIT Ransomware group likes to deface webistes!
@CTI__Updates
@DarkWebInformer
Body hash:
before: 92cad6415cca43fc817a5cd9277552bc819d681c
after:
1e092453dbb38ca7bbe4b63eea98205c1fe5cb98




#KryBit is a Ransomware-as-a-Service #RaaS operation launched in March leasing encryption builders to affiliates. @PicusSecurity details how double-extortion attack exfiltrates 10GB to 250GB per victim before encryption, with ransoms of $40,000-$100,000. https://t.co/4YOsHC9zMd
Actor: #krybit
Victim: https://t.co/pMNbzhlmNh
Date: 2026-08-26 21:14:33 UTC+3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#krybit” Ransomware group has added https://t.co/pMNbzhlmNh to its victims.

🚨 nuova rivendicazione #ransomware Italia 🚨
🏴☠️ gruppo #Krybit
🧬 S.I.P.R.E.S. Società italiana progetti ricerche e sviluppo S.R.L. | Limena (PD)
🎯 settore: C - Manifatturiero
🔗 https://t.co/AzLfvWpMA9
🗓️ 17 agosto 2026
📄 sample: -
▪️ dati esfiltrati dichiarati: 248.15GB
▪️ dati esfiltrati pubblicati: -
⏲️ scadenza: 22 agosto 2026
#ransomNews #cybersecurity #cyberthreats

Actor: #krybit
Victim: https://t.co/p7aWWJit53
Date: 2026-08-12 15:27:05 UTC+3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#krybit” Ransomware group has added https://t.co/p7aWWJit53 to its victims.
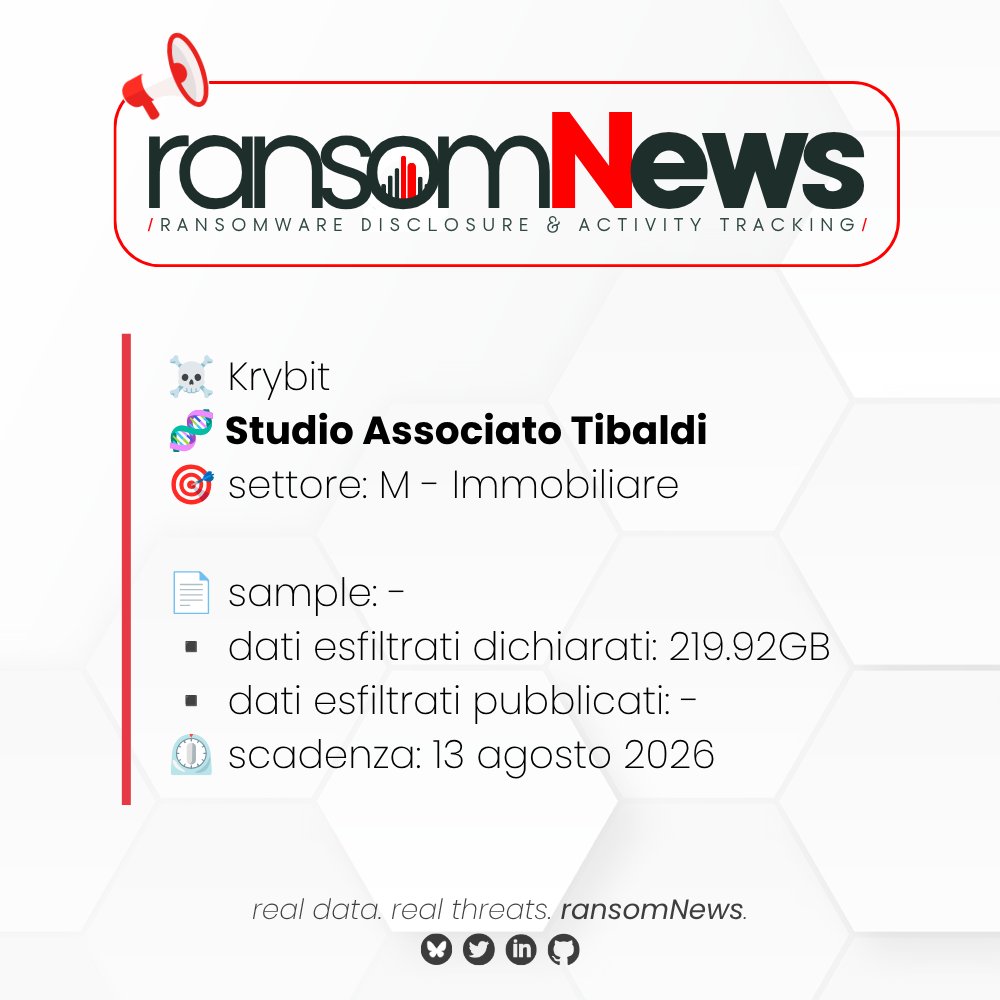
🚨 nuova rivendicazione #ransomware Italia 🚨
🏴☠️ gruppo #Krybit
🧬 Studio Associato Tibaldi| Ostia (RM)
🎯 settore: M - Immobiliare
🔗 https://t.co/zvGjVDOOaa
🗓️ 09 agosto 2026
📄 sample: -
▪️ dati esfiltrati dichiarati: 219.92GB
▪️ dati esfiltrati pubblicati: -
⏲️ scadenza: 13 agosto 2026
#ransomNews #cyberthreats #cybersecurity
Actor: #krybit
Victim: https://t.co/z7Ex0kWB5a
Date: 2026-08-02 20:13:52 UTC+3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#krybit” Ransomware group has added https://t.co/z7Ex0kWB5a to its victims.

Most ransomware groups go dark when their internal panel leaks. #Krybit just kept going. 🏴☠️
This fast-moving RaaS group has already claimed ~70 victims globally.
🔹 Double-extortion
🔹 Hitting Windows, Linux, ESXi, & NAS
🔹 Highly opportunistic
Get the intel you need to mitigate the risk and strengthen your posture.
🔍 Read the Dark Web Profile: https://t.co/Jc0qGYMxC0
#CyberSecurity #Ransomware #ThreatIntel #DarkWeb

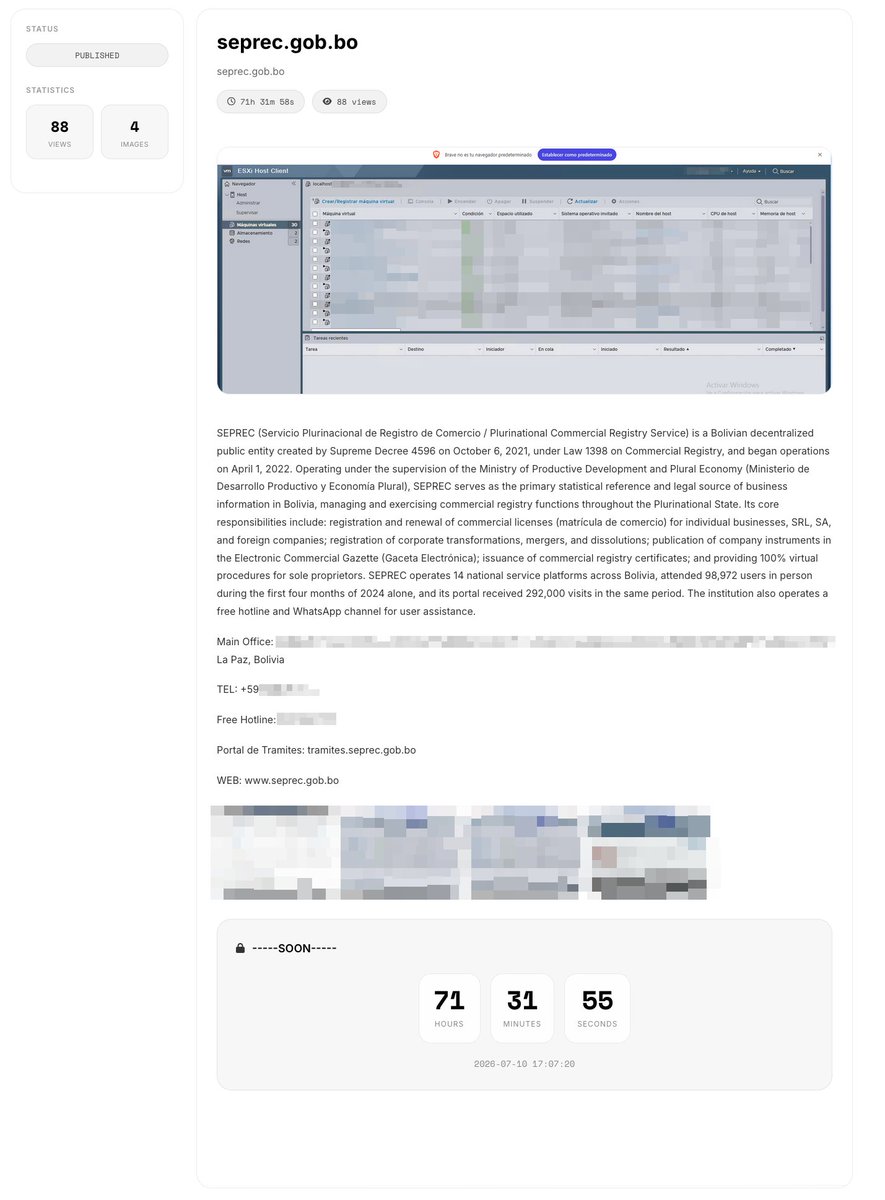
El grupo #Krybit ha publicado en su blog al Servicio Plurinacional de Registro de Comercio 🇧🇴 (@SEPRECBolivia) como posible víctima de un #ciberataque #ransomware.
#SEPRECBolivia es un organismo gubernamental que administra y supervisa el registro mercantil nacional de empresas en #Bolivia 🇧🇴.
@MDPRyABolivia
Monitorea este incidente en #VenariX ➡️ https://t.co/OW9Te2XdwS
#InfoSec #Ciberseguridad #CyberAttack #SEPREC #DarkWeb #LaPaz




🚨 Ransomware Alert 🇩🇴
🏢 https://t.co/qCJwWohh1c
💀 Listed by Krybit
📊 154 GB · Public Sector
📅 Posted 25 Jun 2026
🔗 https://t.co/lrXrKPCztL
#Ransomware #Krybit #DarkWeb #ThreatIntel

🔴🇵🇪 El grupo de ransomware KryBit publica:
A San Silvestre School en su sitio DarkWeb.
Anteriormente, habia sido publicado por el ransomware Qilin el 11 de enero 2026.
#Peru #ransomware #KryBit #ciberseguridad #ciberataque #Educacion #Lima

🚨🇵🇪El grupo de ransomware Qilin publica a la escuela privada San Silvestre School en su sitio DarkWeb.
🔗https://t.co/MQMdWj7rZN
#Peru #ransomware #Qilin #ciberseguridad #ciberataque #Educacion #Lima


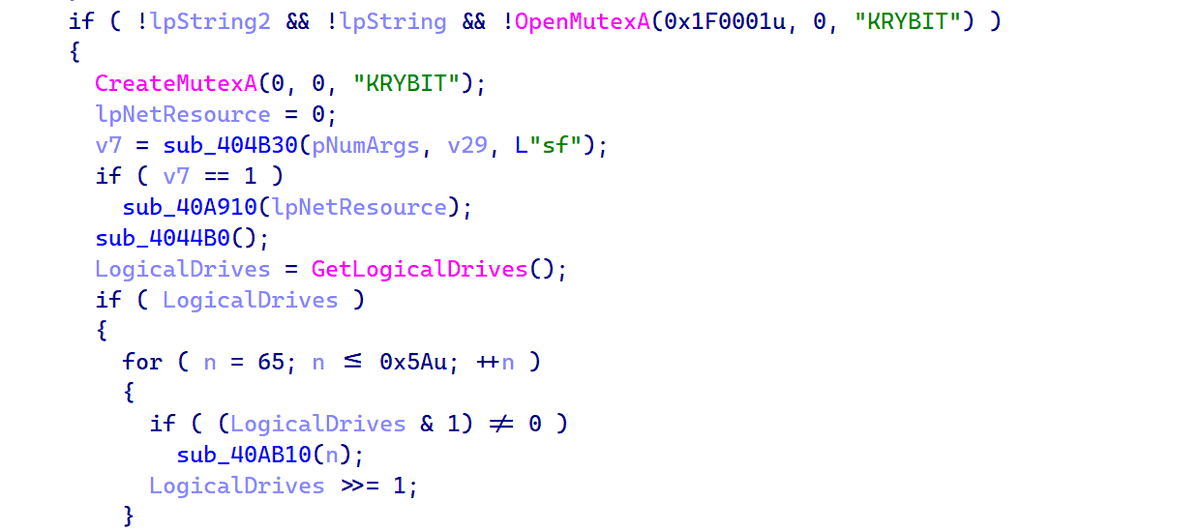
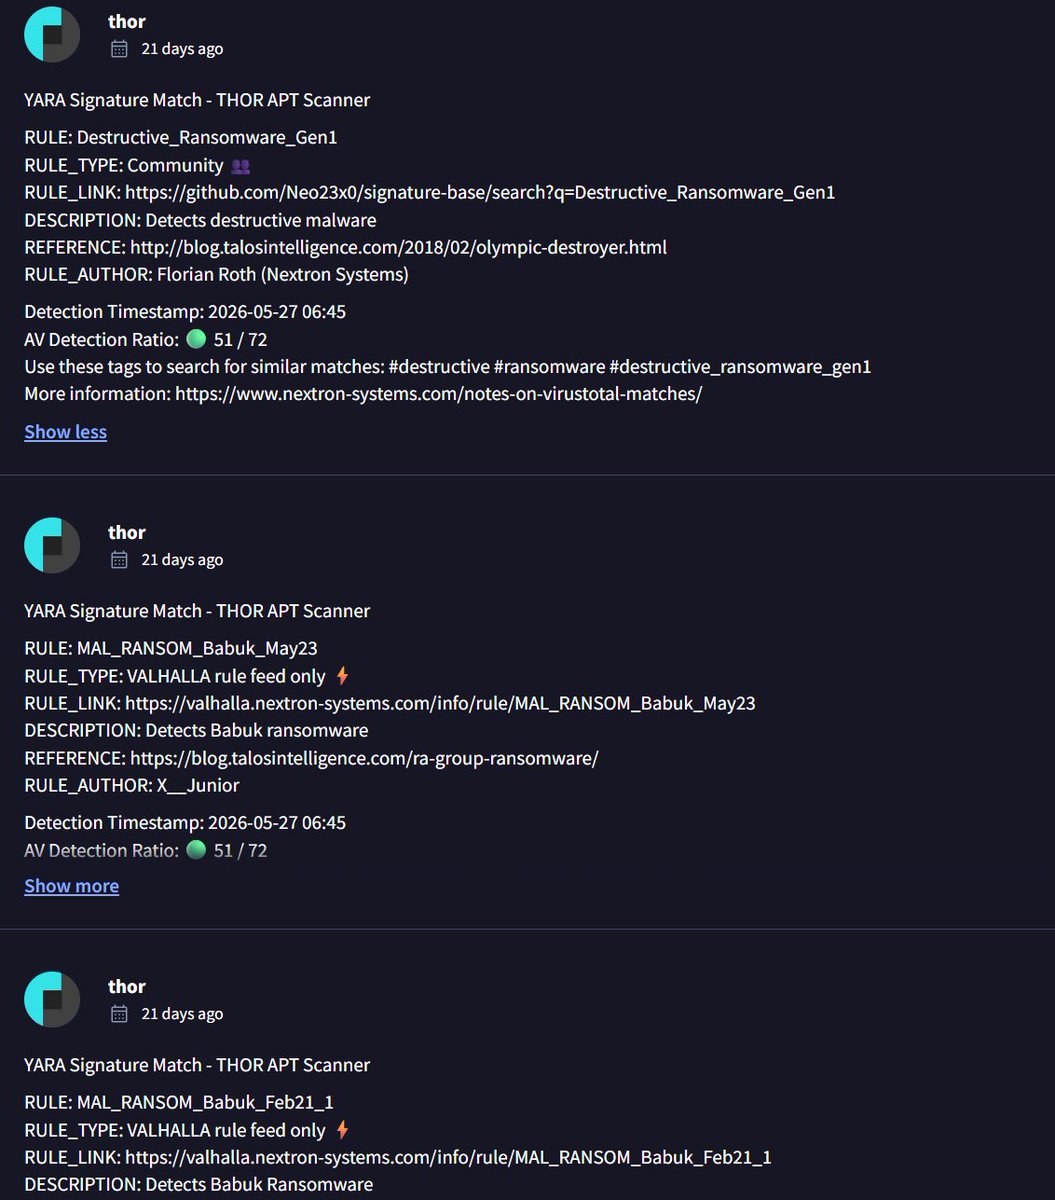
We found a new ransomware called #KRYBIT, a double-extortion strain whose YARA profile overlaps heavily with the leaked #Babuk codebase
Two of our @thor_scanner hits land on dedicated #Babuk rules, so this looks like yet another build standing on Babuk's leaked foundation 🧵
Once on a host, #KRYBIT encrypts local and reachable storage and can optionally extend across mapped network shares, maximizing impact across a victim environment before the operator moves to extortion
Double extortion. The embedded ransom note claims both encryption and exfiltration:
"We have downloaded compromising and sensitive data from your system/network … If you refuse to communicate with us … your data will be published."
Victims are pointed to a Tor leak/negotiation blog
THOR / Valhalla YARA hits on the sample:
https://t.co/lfon6dkSHR
https://t.co/msQrtdaVap
https://t.co/dQqIZ2Ihsm
https://t.co/ZWsjzcyUA7
IOCs
https://t.co/RQTOpyDwKi



🚨 New ransomware player on the radar: KRYBIT
From zero footprint to one of the most active groups in just weeks — 49 victims since early April 2026, and still hitting hard in June.
🌍 20+ countries · every continent
🏭 No sector is safe: tech, finance, manufacturing, legal, education, construction
👁️Groups like this don't ramp up slowly — they arrive at full speed. Watch this one closely.
More: https://t.co/1TFlJ1IuL7
#Ransomware #CyberSecurity #ThreatIntel #CTI #DarkFeed #InfoSec

El grupo #Krybit ha publicado en su blog a la Agencia de Infraestructura en Salud y Equipamiento Médico de #Bolivia 🇧🇴 (@AISEM_BOLIVIA) como posible víctima de un #ciberataque #ransomware.
#AISEM es un organismo gubernamental boliviano que planifica, financia, construye, equipa y remodela hospitales y otros centros de salud en todo el país.
@SaludDeportesBo
Monitorea este incidente en #VenariX ➡️ https://t.co/OW9Te2XdwS
#LaPaz #SaludPública #InfoSec #Ciberseguridad


🔴🇧🇴El grupo de ransomware KryBit publica:
A la Empresa Constructora de Ciudades Inteligentes(ECCI SRL) en su sitio DarkWeb, se enfoca en el desarrollo y construcción de infraestructura urbana bajo el concepto de comunidades tecnológicas.
#DarkWeb #Krybit #ciberataque #ciberseguridad #ransomware #Bolivia #SantaCruz
Last Seen Hashtags on Sotwe
UTSWFrisco
Seen from United States
minichat()******************* filter:videos
Seen from Italy
kimseyle_seks
Seen from Germany
ünlükadınlar
Seen from Turkey
tango arabic
Seen from France
lifewithroy
Seen from United States
dih
Seen from Jordan
cocaina
Seen from Italy
nolimit()**************************
Seen from Netherlands
nolimit exny.
Seen from Israel
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.3M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
89.9M followers

Taylor Swift
@taylorswift13
83.9M followers

Lady Gaga
@ladygaga
75.4M followers

Virat Kohli
@imvkohli
73.3M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.3M followers

Bill Gates
@billgates
65.1M followers

Selena Gomez
@selenagomez
63M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers