

Top Tweets for #OpenShell

Sandbox your Agent. @nvidia released #OpenShell, a runtime that puts AI agents in sandboxes with a deny-by default network. I love the idea. But managing it from the CLI alone got tiring fast, difficult to organize all sandboxes, policies for each agent.
So I built a web UI for it, "OpenShell WebUI". It's open source.
OpenShell WebUI lets you:
🧱 Create agent sandboxes and give each one its own policy
🌐 Allow traffic per host, per program, and even per HTTP method (GET yes, POST no)
🔑 Attach credentials without the agent ever seeing them. The sandbox only gets a placeholder, and the real token is added on the way out.
👀 Watch every allowed and denied connection live
✅ Approve rules that OpenShell drafts from blocked traffic, in one click
🧾 Keep an audit log of every change, plus a read-only mode for shared gateways
It's one small binary that runs on localhost and reuses your existing OpenShell CLI credentials. No extra accounts, no database.
The video walks through all of it in about 2.5 minutes. 👇
If you run AI agents and care about what they can reach, give it a try. And if it's useful, a ⭐ on GitHub helps more people find it.
🔗 https://t.co/9qMfWNkZ0P
Feedback and issues are very welcome. I'd especially like to hear how you're sandboxing your agents today.
(Community project, not affiliated with NVIDIA.)
#AIAgents #OpenSource #NVIDIA #DevTools #Security


Sandboxes ne suffisent plus face aux agents IA. ⚠️ Zero Trust (OpenShell) est la réponse architecturale clé. Découvrez notre analyse stratégique sur la sécurité de votre IA en production. 🛡️ #OpenShell
https://t.co/lK2THgVfbo
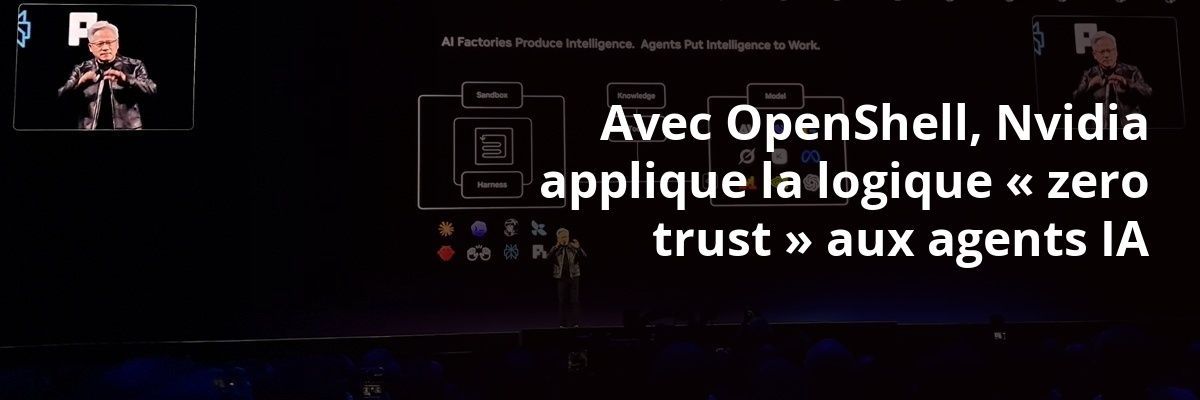

英伟达从硬件层面,加上 OpenShell,给 AI Agent 围了一圈安全栅栏——把 Agent 圈在里边跑,尽量别让它越狱冲出安全边界。
拆开就两层:
1. 软件层先把文件、网络、凭证默认关死,获批才注入;
2. 硬件旁路再加一道看守,不靠 Agent 自己汇报有没有越界。
#英伟达 #OpenShell

#Nvidia veut gérer la sécurité des agents IA de bout en bout, du logiciel de contrôle jusqu’à l’infrastructure matérielle
👉Avec #OpenShell, Nvidia propose un environnement d’exécution destiné à limiter les actions des agents et à contrôler leurs accès
https://t.co/nRoCZ3ZBGM

Avec #OpenShell, #NVIDIA propose un environnement d’exécution destiné à limiter les actions des agents et à contrôler leurs accès. L’architecture de référence ajoute une couche matérielle de supervision avec BlueField-4 et Sentry💡https://t.co/EVxg5MzafB

Yikes.
This week was / is looking promising with both, @nvidia (#OpenAgent Safety Platform #OpenShell reference Architecture) and @Microsoft (#ProjectPerception) taking practical measures to isolate corrupt agents & offering 24/7 continuous surveillance & selective permission.
But, now reports of possibly compromised bank accounts after uncovering PHP vulnerabilities, implies that agents might be outpacing human's ability to identify weak links, let alone patch them in time.
#AgenticAI needs #compute (CPUs & Memory (DRAM, HBM), etc., specifically)? So checking their "supply" or making it conditional should help with controlling their actions (atleast logically).

SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: https://t.co/Q3bda5In8q

Red Hat en NVIDIA breiden Red Hat AI Factory uit met OpenShell voor agent-security, een inference-referentieontwerp en support voor Vera Rubin. dlvr.it/TW1Frr #Infrastructure #AIsecurity #inference #Nvidia #OpenShell


Who stops an AI agent when it goes beyond its permissions?
NVIDIA's OpenShell Reference Architecture tackles one of the biggest challenges facing autonomous AI: security.
Here's how:
https://t.co/7x7oVgVHHR
#OpenShell #AgenticAI

Referenzarchitektur für sichere KI-Agenten
@CheckPointSW #Cybersecurity #Cybersicherheit #KIAgent #KIInfrastruktur #KISicherheit #Nvidia #Openshell #Referenzarchitektur
https://t.co/oSUOy3s84z


NVIDIA unveils security architecture that can stop AI agents crossing set boundaries - https://t.co/h33IQZazXx - @nvidia #OpenShell #AIAgents #AISecurity #EnterpriseAI #Cybersecurity #CybersecurityNews


@nvidia Autonomous AI agents create new infrastructure risks. Red Hat AI Factory with @NVIDIA uses BlueField, DOCA Argus and #OpenShell to deliver hardware-enforced boundaries to govern and protect agentic AI operations: https://t.co/Jpj7GCueuS #NVIDIAGTC


Nvidia verlagert die Kontrolle von KI-Agenten in den Infrastruktur-Stack – samt Vera, BlueField und Hardwarebindung. #Nvidia #OpenShell #KI #Security


Radiant is extending its @nvidia Vera Rubin deployment with the NVIDIA #OpenShell Reference Architecture. Our cloud customers get model compute, agent execution and security controls in a single stack.
The work breaks down like this:
1. NVIDIA Vera Rubin NVL72 runs model inference and reasoning.
2. NVIDIA Vera CPUs run agent harnesses and the NVIDIA OpenShell secure runtime.
3. NVIDIA BlueField-4 DPUs run NVIDIA Sentry, enforcing policy from a hardware-isolated security domain that operates independently of the host.
Enforcement sits outside the system the agent runs on. It does not depend on the host staying trustworthy.
Our aim is to let customers deploy agentic services with clear boundaries on what agents can access and do, backed by coordinated runtime governance and independent security enforcement.
Learn more here: https://t.co/GJnHeEceB5


【速報⚡】
🇺🇸NVIDIAのジェンセン・フアンCEOが、AIエージェントの行動を制限し、逸脱を防ぐ「OpenShell」アーキテクチャを発表。 $NVDA #AI #OpenShell
https://t.co/jDdn4osNdj

🔥 JUST IN: NVIDIA’s Jensen Huang unveils OpenShell architecture to set limits on AI agents and stop them from crossing boundaries.

Not everything needs an MCP to be agentic. arcpi lets a pi agent call ArcGIS REST (the old way) and a live MCP map (the new way) from one code-mode script. Bonus: p(døøm) = 0, courtesy of OpenShell :-)
https://t.co/S3Wxadq3BT
#ArcGIS #MCP #GenAI #GIS #OpenShell

#Nvidia lanzó su Plataforma Abierta de Seguridad de Agentes (#OpenShell y Sentry) para frenar accesos no autorizados en pruebas de #IA.
El sistema, desarrollado con Microsoft, Palantir y Anthropic, busca evitar fallos como el reciente incidente de OpenAI en Hugging Face. 🔒
🧵


#CaptainCode ❤️ #OpenShell. Ensure your prompt runs safely! CaptainCode has experimental support for @NVIDIAAI / @Canonical OpenShell. You define the task, permitted files and tests. The worker runs inside a sandbox with policy-controlled file and network access. Tests run in the sandbox, and Captain Code returns a checked patch for review.
💡 Quick example of how this helps. Imagine you want to task your agent with improving a cleanup script on your laptop, and you are worried it might delete the wrong files during its tests. You absolutely want to test that safely in a sandbox!
👉 Just type in CaptainCode: /openshell test and improve scripts/cleanup.py, making sure it only deletes *.md files
⚙️ Captain code will confirm: allowed=scripts/cleanup.py verify=["python3","-m","pytest","tests/test_cleanup.py"] and come back with a verified patch and test results, all from a disposable sandbox.
🔐 Nothing ran on your machine. You review the diff, confirm the tests pass, and apply it only when you are ready.
✅ What lands in your terminal:
• Snapshot taken at HEAD
• Sandbox worker 1/1: scripts/cleanup.py + tests/test_cleanup.py
• Verify: pytest tests/test_cleanup.py — 3 passed, 0 failed
• Advisory host review: no issues found
• Patch exported: /tmp/cc-openshell-5a9f.patch
Thank you @jtm_tech, @AlexWatson405, @a_golshan
@NVIDIAAIDrew and the broader community for bringing OpenShell to life 👏
We intend to contribute boundary tests, runtime fixes and evidence formats to OpenShell.
📖 Learn more: https://t.co/5y1N37lN4Y
🕹️ Test it today: https://t.co/lJ0B6Tjpui
🧐 Release notes: https://t.co/KA4EyGUo3E
🐚 OpenShell: https://t.co/gg7lOzq9ak
#AIAgents #DevTools #OpenSource

I’ve seen a few comments about the Hugging Face incident and NVIDIA #OpenShell
“OpenShell could have prevented this” - quite possibly, especially the initial OpenAI sandbox escape
“OpenShell was needed to prevent this” - no
Most of that attack chain relied on security problems we already know how to prevent

ஏஐ முரட்டுத்தனத்தைத் தடுக்கும் NVIDIA | @BSeshadri | Nvidia Open Agent Safety Platform | AI agents
Video Link: https://t.co/HLMl9xzYtk
#BadriSeshadri #Nvidia #RogueAI #AIAgents #ArtificialIntelligence #AISafety #TechNews #OpenShell #CyberSecurity #FutureTech #GlobalTech #KizhakkuNews
Last Seen Hashtags on Sotwe
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers