

Top Tweets for #REF9334

#ThreatProtection #KREMLIN toolkit leveraged in malicious operation #REF9334, read more about Symantec's protection: https://t.co/PEu5l9Tnip #malware

🚨 SLOWMIST ALERTA SOBRE KREMLIN: MALWARE BANCARIO QUE UTILIZA ETHEREUM
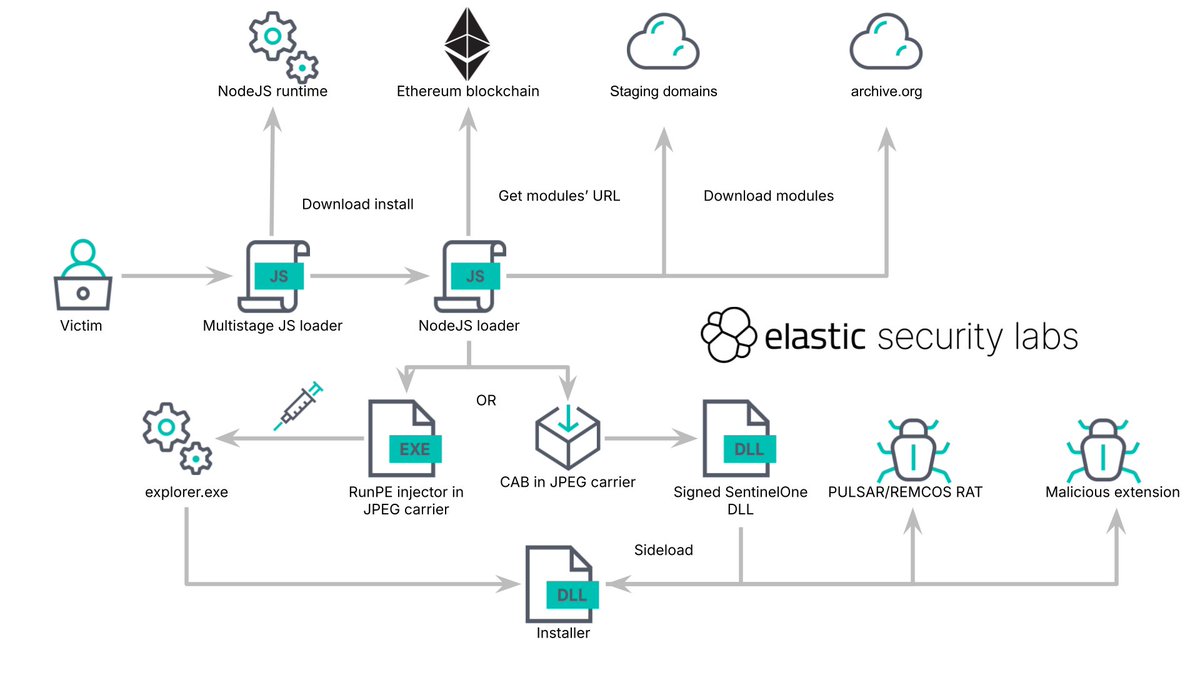
Según la alerta compartida, la campaña #REF9334 está activa desde al menos mayo de 2025 y utiliza cargadores de múltiples etapas y extensiones maliciosas para robar credenciales, tokens de sesión y datos sensibles.
🔴 Las extensiones pueden instalarse en Chrome y Edge sin aprobación del usuario, eludiendo controles de integridad de Chromium.
⛓️ La operación utiliza contratos inteligentes de Ethereum para actualizar las direcciones de sus servidores de control y de descarga de malware, dificultando la interrupción de su infraestructura.
🇧🇷 Tras registrar un dominio utilizado como interruptor de la campaña, los analistas observaron conexiones de 1.515 equipos infectados: el 98,75% estaba en Brasil.
🛡️ La alerta recomienda vigilar las extensiones de navegador y la infraestructura asociada.
🔎 Indicadores reportados:
Administrador:
0x5C32A09873be70a92fd8bB5A9fED7967dE06BdE6
Contratos:
• 0x902EDbFECFF38f285Bf26283fB9cEB3700061873
• 0x64Def0A6099c4DE9C413B108EAae85A3C7457615
• 0xCD7360A83E5cdbBbbbcEB0e78748babA6740d07b señalado como activo en la alerta.
#Ciberseguridad #Ethereum #SlowMist #Malware
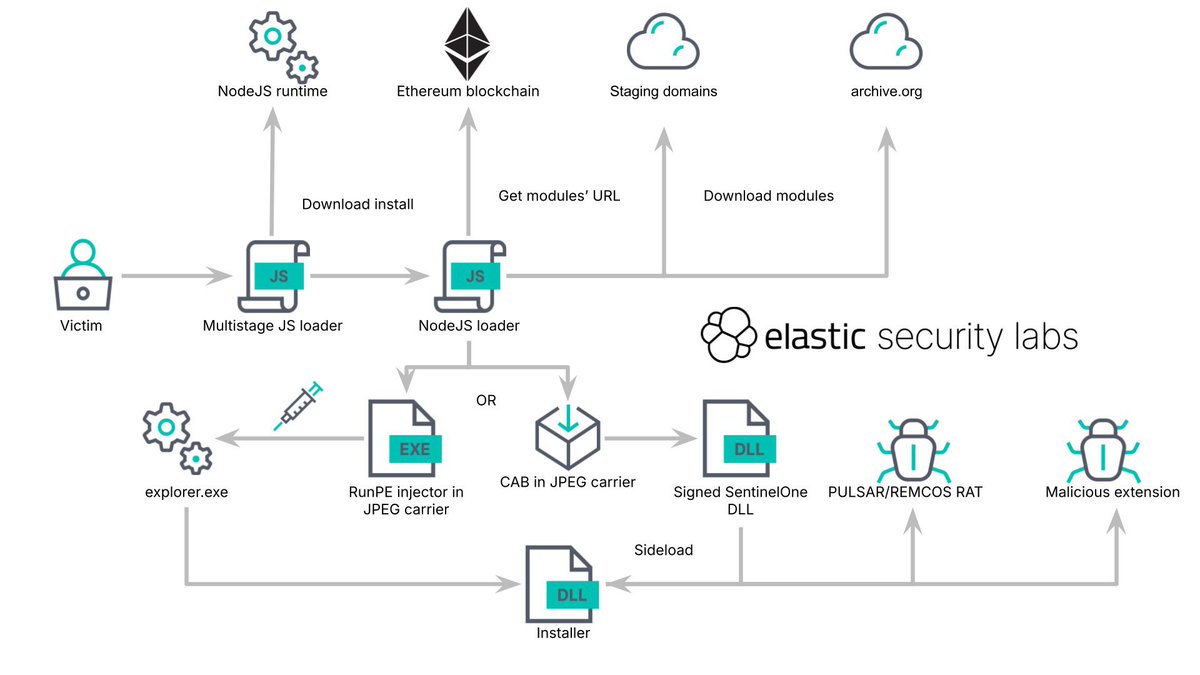

🚨 SlowMist TI Alert: KREMLIN Malware 🚨
Recently, a Brazilian banking malware operation, #REF9334, active since at least May 2025, was disclosed.
🔴 The #KREMLIN malware ecosystem uses multi-stage loaders and malicious browser extensions to steal credentials, session tokens, and sensitive data.
⚠️ Its malicious extensions can be installed in #Chrome and #Edge without user approval by bypassing Chromium integrity mechanisms, including Secure Preferences, HMACs, and App-Bound encrypted hashes.
⛓️ The operation also uses #Ethereum smart contracts as dead-drop resolvers to dynamically update C2 endpoints and payload hosting locations, making the infrastructure harder to disrupt.
⚙️ After registering a network canary (kill switch) domain, analysts observed 1,515 infected hosts checking in, with 98.75% located in Brazil.
🛡️ Security teams should monitor for related malware, browser-extension activity, and infrastructure associated with the campaign.
🔑 Admin:
- 0x5C32A09873be70a92fd8bB5A9fED7967dE06BdE6
📜 Smart Contracts:
- 0x902EDbFECFF38f285Bf26283fB9cEB3700061873
- 0x64Def0A6099c4DE9C413B108EAae85A3C7457615
- 0xCD7360A83E5cdbBbbbcEB0e78748babA6740d07b (currently active)
🔎 IOCs: https://t.co/mnkXUEY3py
📌 Source: https://t.co/7lTzuUNJCi
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.4M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
83.9M followers

Lady Gaga
@ladygaga
75.4M followers

Virat Kohli
@imvkohli
73.3M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.3M followers

Bill Gates
@billgates
65.1M followers

Selena Gomez
@selenagomez
63M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers