⚠️CVE-2026-85706 (CVSS 10.0)⚠️
Your GitLab will hand a stranger its files. 😱
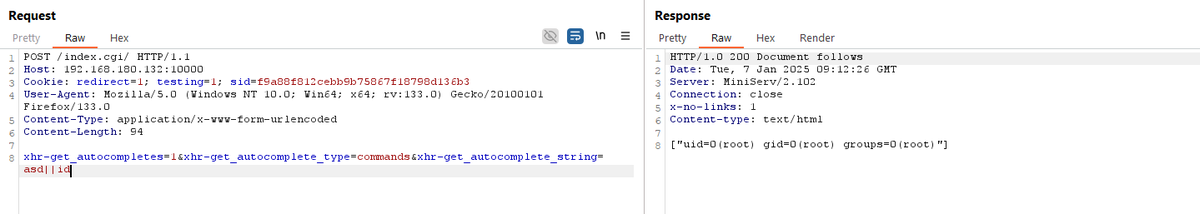
No login. No account. An attacker just URL-encodes one letter of commits → %63ommits, and GitLab-Workhorse waves the request through — so a single unauthenticated POST to the repository commits API reads files straight off the server filesystem. Config, internal logs, source paths, versions… all without ever signing in.
Already in CISA KEV — exploited in the wild. 🚨
If you self-host GitLab, patch to 19.1.8 / 19.2.6 / 19.3.2 now.
🔥PoC + setup: https://t.co/qgJaKGxJ04
#GitLab #ArbitraryFileRead #CVE #PoC #Exploit #CyberSecurity #CVE_2026_85706
F5, BIG-IP, a 20-year-old primitive, a security appliance, an "authentication" mechanism - and a CISA promise ring.
Yes, it's CVE-2026-94127.
Give us strength. Speak soon xo
https://t.co/1l3e0Y3wNN
All WordPress users need to update their WordPress installations immediately 💯
There is a 9.2 CVE that discloses a remote code execution vulnerability that affects versions all the way back to 2016 😬
Here's the official notice https://t.co/tbJlzC780L
We recently looked deeper at the authentication bypass vulnerability in Next.js (CVE-2025-29927) and discovered some intelligent and comprehensive ways to check for the vulnerability. Read more in our blog post: https://t.co/f7f6VKzEcS
In one of #Telerik's recent updates, I noticed a fix for CVE-2024-10095, an insecure deserialization vulnerability in their UI for WPF.
So I thought, what a perfect time for a patch analysis :)
Check it out here:
https://t.co/01n0v1JiTm
🔥 The "impossible" XXE in PHP? Not so impossible anymore.
Our researcher Aleksandr Zhurnakov discovered an interesting combination of PHP wrappers and a feature of XML parsing in libxml2 to exploit it.
Read: https://t.co/GuW2Vf5qLN
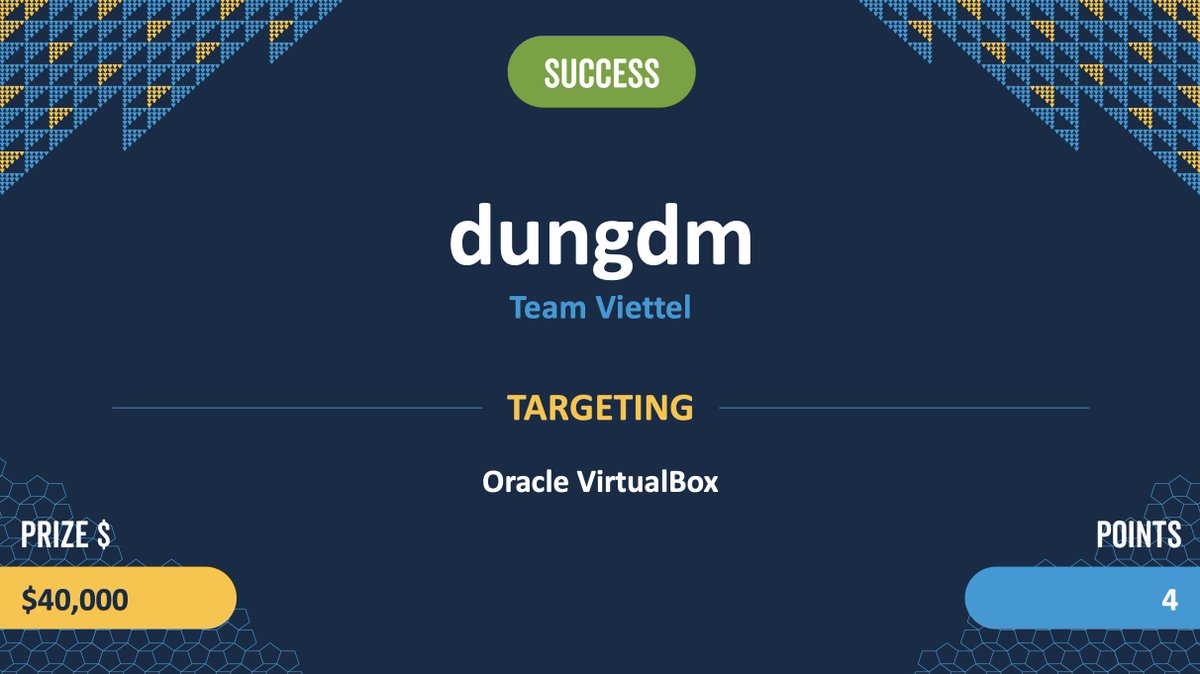
Success! dungdm (@_piers2) of Team Viettel (@vcslab) used an uninitialized variable and a UAF bug to exploit Oracle VirtualBox. They earn $40,000 and 4 Master of Pwn points. #Pwn2Own#P2OVancouver
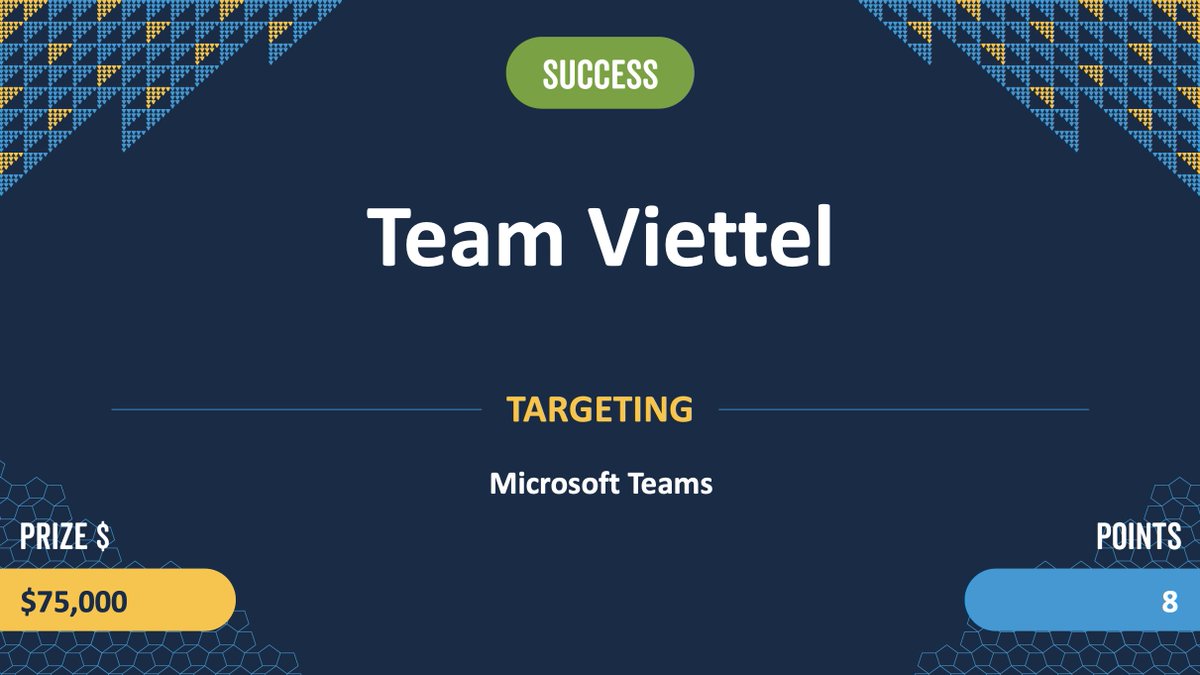
Success! @hoangnx99, @rskvp93, and @_q5ca from Team Viettel (@vcslab) used a 2-bug chain in their attempt against Microsoft Teams. They earn $75,000 and 8 Master of Pwn points.
12 #recon tools you NEED to know about! 🧵
Recon, the gathering of information about your target, is becoming more and more important! 🧠
Here are the tools to help you spot subdomains, vhosts, S3 buckets, parameters and more faster and more effective than the others 👇