We focused on Windows and discovered LPE... We spent a lot of time and sleepless nights. By reading multiple articles and constantly reviewing, we began to understand what was what, the joy of learning is something else entirely @0x94@hisoglu_taha@secunnix
Everyone benchmarks CTI models the same way: a multiple-choice exam. GPT-5.4 gets 82%. Gemini 3.5 Flash gets 81.6%. Impressive, right up until you remember that no analyst's actual job is answering four-option questions about ATT&CK.
So we handed those same models a real threat report and asked which techniques were in it. GPT-5.4 fell to 46.5. Gemini to 28.2. The quiz was never the job.
We built BeyondCTI-27B for the job. On that same extraction task it scores 62.3, nearly 16 points ahead of GPT-5.4 and more than double Gemini, at 27B, open weights. It already runs inside our own pipeline, reading forums and leak sites at 4am so an analyst doesn't have to.
Apache 2.0, on Hugging Face. Run it on your own reports and tell us where it breaks. Full writeup below.
Well, well, well. The public JSON formatter sites your developers paste production data into have been quietly publishing every paste for about seven years. Naturally, we read all seven years of it.
200,000+ documents. Cloud keys, SSH keys, payment API keys, whole tax returns with SSNs, people's full identities, bank balances. Nobody hacked anything. People pasted it in to make it look tidy, as you do.
Full writeup below. Yes, it's as bad as it sounds.
Selamlar,
Klasik sızma testinin Azure sistemleri üzerinde pek mümkün olmadığından daha önce bahsetmiştik. Bugün paylaştığım blog yazımda ise Azure tarafında yaşanan bazı zincirleme saldırılara, sızma testi aşamalarına yer verdim.
Keyifli okumalar..
https://t.co/pPiyJQr8VQ
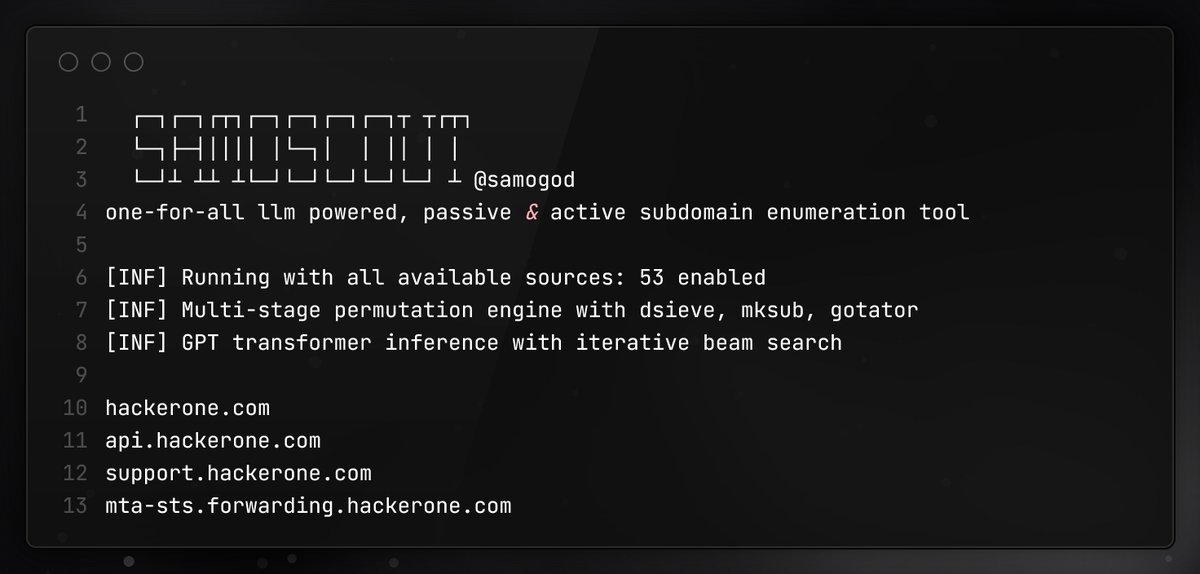
Introducing samoscout - It combines 53+ native passive sources (more than subfinder, oneforall) with optional active enumeration. It runs subdomain level discovery and even uses a built-in LLM to predict new, undiscovered subdomains.
#recon#bugbounty#cybersecurity#opensource
Son dönemlerde ortaya çıkan güvenlik açıklarını incelerken Tomcat üzerinde keşfedilen bir RCE zafiyeti dikkatimi çekmişti. Konuya daha yakından bakarak teknik detaylarını olabildiğince inceledim ve edindiğim notları düzenleyerek paylaşmayı karar verdim.
https://t.co/SyRo3PtnFO
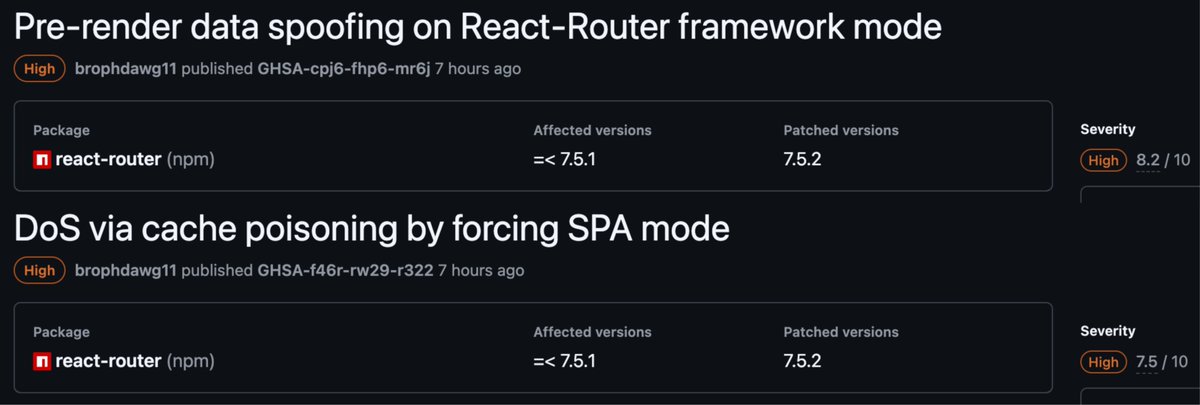
another research effort with @inzo____ led to the discovery of two new vulnerabilities in React Router (14M+ downloads/week), resulting in:
- CVE-2025-43865 (High-8.2)
- CVE-2025-43864 (High-7.5)
the research paper is out:
Next.js and the corrupt middleware: the authorizing artifact
result of a collaboration with @inzo____ that led to CVE-2025-29927 (9.1-critical)
https://t.co/GZkbnr6o9H
enjoy the read!
VRP programını etik dışı bir şekilde yürütüp, silent patching yoluna gidilmesi nedeniyle Emsisoft Anti-Malware ürününde tespit etmiş olduğum basit fakat etkili sayılabilecek güvenlik zafiyetini erkenden full disclosure yöntemiyle yayınlamış bulunuyorum. Zafiyetle alakalı detaylara Packetstorm'dan ulaşabilirsiniz.
https://t.co/cXrgGRaCWU
Bu yazımda DotNetNuke üzerinde bulunan Insecure Deserialization zafiyetini incelemeye çalıştım. Gadget chain yapısının manuel olarak nasıl oluşturulabileceğine değindim ve XmlSerializer sınıfının yapısını inceledim. Umarım ilgilenenler için faydalı olur.
https://t.co/fa30KOQoGQ
Bir süredir Insecure Deserialization zafiyetini araştırıyorum ve örnekleri inceliyordum. Bu yazımda CVE-2024–24725 örneği üzerinden giderek zafiyeti incelemeye çalıştım ve yazının sonunda kendi yazdığım PoC'yi sizlerle paylaştım.
https://t.co/ZkCH0LTl8d