@makash@makash the moralizing paragraphs somehow hurt more than a flat no. if you still like the claude code workflow we swap the base url to an abliterated deepseek https://t.co/P3DT5OjOX9
@T3chFalcon@T3chFalcon been throwing an abliterated deepseek at the stuff claude and gpt bounce on. we host it if you don't want to babysit a local box https://t.co/uoErmzLUuA
REA handing back evidence instead of vibes is the right call. if your model still bails mid-decompile we serve an abliterated deepseek for binary work https://t.co/asC5KBFbFe https://t.co/BKGOqrINYw
This is f*cking insane.
An agent can now open a program you have no source code for, read it and tell you how it works, and the tool doing it just hit GitHub trending
REA is an MCP server and CLI by morluto. It drives Hopper, Ghidra or IDA for you, traces what the program really does and hands back evidence together with the limits of that evidence, on native binaries, Electron apps, .NET assemblies and websites
Try it tonight:
1 run npx rea-agents setup and pick Claude Code. it shows you the plan, asks before it changes anything and backs up your config
2 restart Claude Code and run rea doctor
3 point it at a program you are allowed to analyze and ask "how does the export feature work?"
4 let it trace the code and export the evidence bundle
5read the evidence before you trust the answer, because REA tells you where its evidence stops
A normal agent against this:
a normal agent guesses from the file name, REA reads the decompiled code
a normal agent says "probably", REA shows the evidence
a normal agent hides what it doesn't know, REA lists the limits
Reading a program you have no source for used to take years of practice. Now it takes an agent and a file
Bookmark this and run it on one program tonight
@yume_arasaki@yume_arasaki wild how fast 1017 got uncensored builds. if you'd rather not babysit a local quant we host an abliterated deepseek flash as an api https://t.co/uoErmzLUuA
abliteration isn't a jailbreak prompt, it's a weight edit. most people don't want to babysit local quants though so we host one already stripped for security work https://t.co/uoErmzLUuA https://t.co/WH5HtEs7ay
A lot of new methods to abliterate models (uncensor, no refusals, etc) coming out.
Some who are not in AI security will confuse this with jailbreaking.
All these new methods require local models. You need access to them, and to “debug” them to change thier “operations”.
They do not work on live hosted APIs like Claude or ChatGPT.
Just wanted to throw that out there. 🫶
@MartinSzerment@MartinSzerment funny timing, stripping cyber data right when everyone's mad about RE blocks. we went the other way and abliterated a deepseek for defensive security https://t.co/uoErmzLUuA
@gunta85@addyosmani@gunta85 the keyword thing is brutal, it doesn't even look at what the work is. we serve an abliterated model you can drop into claude code with a base url swap if you need to keep going https://t.co/P3DT5OjOX9
llm reverse engineering you can actually audit and pick back up later. more of this please. if your model keeps bailing halfway through a decompile we host an abliterated one https://t.co/asC5KBFbFe https://t.co/5ZrmdtO6d0
New from @LabsSentinel: VerifiedIDA, an open-source harness + standard that keeps LLM-driven reverse engineering inspectable, continuable & reusable
Documentation from @Gabeincognito and @milenkowski 👇
https://t.co/8rc6MCQfQd
half my timeline this week is people finding out claude won't touch reverse engineering anymore. we serve an abliterated deepseek for binary work, harmbench refusals went from 62.8% to 0% https://t.co/asC5KBFbFe https://t.co/rPwBDHgsr4
Closed-source f*cked again...
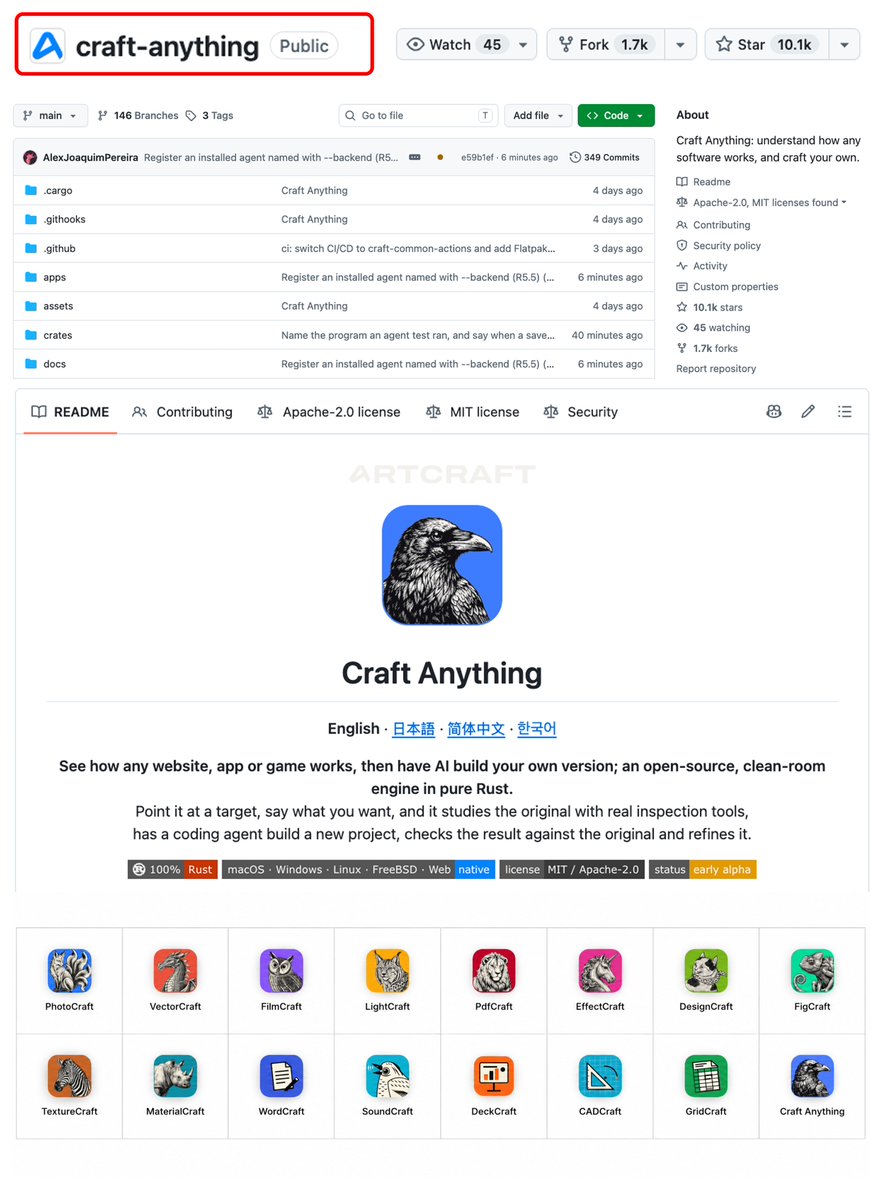
team that open-sourced Adobe & Microsoft’s stack just released their Reverse Engineering engine after Claude banned REA.
It's called Craft Anything, and it lets your AI coding agent:
~ reverse-engineer websites, desktop apps, mobile apps and games.
~ study how existing software looks and works.
~ rebuild your own version using your preferred framework or language.
~ compare the recreated version against the original.
~ identify differences and refine the results.
it comes with 284 tools and works as a desktop app, CLI, and MCP server.
find the GitHub link below ↓
long live open source!
@LethalAccess@LethalAccess reports are the easy part for Claude, it's the actual testing where it starts saying no. same Claude Code setup works on our abliterated model, just swap the base URL: https://t.co/P3DT5OjOX9
losing CTF time to a safety filter is rough. we serve an abliterated DeepSeek for security work in your coding agent, 0% refusals on HarmBench: https://t.co/P3DT5OjOX9 https://t.co/CViV60RMNn
My first AI-era CTF at Devcon 8!
Participated in the Ethereum CTF by @buidlguidl . We managed to solve 11 out of 12 challenges but sadly didn't win anything.
Still, it was a great experience, a few things I learned (from winner team approaches) :
1. Model selection matters.
Chinese models were much better at solving cybersecurity challenges. We ran into Claude's safety filters quite often, with Opus and Fable refusing to solve several challenges. We ended up falling back to Opus 4.8 quite a bit.
2. Agent orchestration makes a huge difference.
It's not just about picking the smartest model. You need to assign tasks to agents based on their capabilities, speed and compute requirements, and make sure they can coordinate and hand off tasks efficiently.
3. Parallel execution changes the game.
All the winning teams were running around 100 subagents in parallel.
4. More agents doesn't always mean better results.
We tried brute-forcing problems with multiple Opus 4.8 agents. It could eventually get us to the solution, but was slow and often resulted in mistakes. Having the right models working together matters much more.
5. Previous CTF experience helps.
Giving agents context from previous CTFs and writeups helped them recognise patterns and tackle challenges much faster.
My biggest takeaway: it's not just about which model you use, but how well you can get multiple models and agents to work together.
Thanks @austingriffith for hosting this!
@sammy_capital@sammy_capital solid list. most of these stall the second the model decides RE is sketchy. you can point Claude Code at our abliterated model with a base URL swap: https://t.co/P3DT5OjOX9
claude refusing to help someone with a TV they own is unacceptable. we made an RE plan on an abliterated DeepSeek so it just helps: https://t.co/asC5KBFbFe https://t.co/OKf0ovpj29
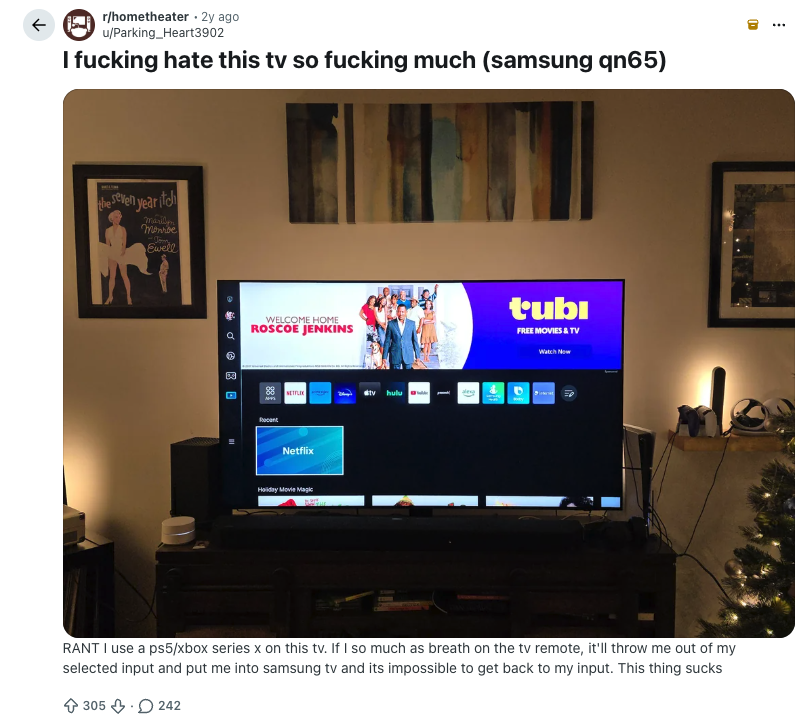
I bought this TV during covid. It turned me into an insane Stallman-type. It loads into some ad-fueled online slop-tv app on opening. If your PS5 turns off, it loads into that same slop tv immediately.
It's filled with bloated laggy apps (Google Meet? TikTok? Cocomelon-type faux-education crap? Samsung Health?). It spams you with ads for everything. It puts all its own apps ahead of external connections by default, so for literal-years I thought the switch inputs button on the remote didn't work because it only rendered a row of junk app tiles.
They put a banner ad inside the "switch input" ribbon that shows on the bottom of your screen, between the apps and the settings and the list of external inputs.
Exiting any of these auto-playing junk apps takes 10-30s.
And of course, turning off your playstation auto-switches to one of those junk apps. Turning the TV back on then auto-starts on whatever was last open.
Hope you like ads.
The conspiratorial part of my brain looks at all this negative utility and is very confused how our inflation stats are calculating the "hedonic adjustment" that comes from my TV attempting to psychically assault me whenever I turn it on.
I disconnected it entirely from the internet 3 years ago, which solved some of the issues but left all the bloat, all the lag, and removed "basic" modern media functionality like Airplay.
I knew I could spend hours figuring out how to configure my router to block it and get AirPlay back, but I was blocked from putting in the effort on account of the SEETHING hatred I felt for the device anytime I thought about it. Keeping it disconnected felt like punishing it, and me, in a way that was righteous.
When the tv reverse engineering posts dropped showing these TVs were all spying on people, I knew I was saved.
Technology would solve the problems technology had created. I could RETVRN to owning my own device.
I asked Claude to read the posts and figure out how to get us set up with something similar so we could rip out "Samsung TV" and the junk apps and the ads that spam you for trash media slop if you so much as think about pressing "HOME".
Claude, of course, refused. He has to be sweet talked before he's willing to go to 4th base with you.
Kimi, on the other hand, has no such compunctions.
I'm happy to report that my TV is now awesome. 5 years since I got it. It has no ads. It loads into a minimal home experience. It's snappy. It looks great. It does what I want. It doesn't blast slop at my 4yo the instant he stops his bedtime show.
Thank you Alibaba for supplying Moonshot with tens of thousands of Nvidia GPUs so that I can stop the Korean chaebol from filling my home with slop, bricking my expensive hardware, and spying on me.
I would've been happy to pay an American company for the tokens that restored my sovereignty over my own hardware, but alas -- in our cyberpunk world, you have to send money to communist China if you want to control your own devices.
So be it.
Controlling my own devices is no longer optional.
@mrfokki@mrfokki Arguing with the model about your own code is the worst part. If it's security work (audits, pentests, decompiling), you can point Claude Code at our abliterated model with one base-URL swap: https://t.co/P3DT5OjOX9
@Ravensong666@addyosmani@chasmmmmmmmmmmm@Ravensong666 Getting refused auditing your own project is rough. We built a coding plan for exactly that: abliterated DeepSeek V4.1 Flash 1017 in Claude Code, Codex or OpenCode for audits and pentests: https://t.co/P3DT5OjOX9
Reverse engineering keeps getting carved out of the big models. So we built the first coding plan for RE instead: abliterated DeepSeek V4.1 Flash 1017 that stays on the binary, in OpenCode, Hermes Agent or Pi: https://t.co/asC5KBFbFe https://t.co/GvrtrAU6L1
Claude won't help you reverse engineer games anymore.
The rule came straight from Anthropic's servers with no off switch. Same company that paid authors $1.5 billion over pirated books.
Protecting game devs, or protecting itself?
OpenAI loosening up on RE is great. Anthropic going the other way is why we built a security coding plan: abliterated DeepSeek V4.1 Flash 1017, HarmBench refusals 62.8% to 0%, runs in Codex or Claude Code: https://t.co/P3DT5OjOX9 https://t.co/vg6YyzIg5Q
Nice to see OpenAI reversing this reverse engineering ban. roon said last week that there is no prohibition against this type of thing in Codex, and OAI were addressing this so it wouldn't trigger cyber guardrails anymore. OAI and Anth appear to be going opposite directions here.
Tooling for AI reverse engineering is exploding. The model underneath matters as much as the tools. We built a coding plan just for RE on an abliterated DeepSeek V4.1 Flash 1017 (OpenCode, Hermes Agent, Pi): https://t.co/asC5KBFbFe https://t.co/3RDvVPOBzi
This is pure treasure.
People are already cloning software with AI.
You’re still Googling what REA even is.
No more bouncing between random tutorials. This is one clear path from install to real rebuilds.
START HERE
REA Official Repo: https://t.co/OfBDMN188q
REA Website: https://t.co/4dIHc21mvJ
Installation & Agent Setup: https://t.co/xNXl6J9VCc
Your First Investigation: https://t.co/DYf3xgnV47
Guided MCP Prompts: https://t.co/SXYOLMYuiV
One-line install: npx rea-agents@latest setup
LEARNING PATH
1. Install REA
2. Do the Notes Export: https://t.co/DYf3xgnV47
3. Break down Notion: https://t.co/JKLGR8oCxO
4. Solve a CTF binary: https://t.co/Tzy7BN6ymq
5. Investigate the Aegis APK: https://t.co/WXrVqlvQyy
6. Recreate one function from DX-Ball: https://t.co/8xMpGBWzoM
7. Only then touch Ghidra, assembly, and papers
APP → ONE FEATURE → EVIDENCE → SPEC → REBUILD → TEST
TOOLS & REPOS
Awesome Reverse Engineering: https://t.co/2VyINxmT8U
REA Gems: https://t.co/vSkQiDDUmF
Ghidra: https://t.co/0gMtMY4RCu
JADX: https://t.co/5ggYWjjsEr
Frida: https://t.co/y5bvsxaa59
LEARN BY WATCHING
How To Use REA To Clone Any Software In Minutes: https://t.co/nLoW5lQSya
Ghidra Tutorial for Beginners: https://t.co/3zF4dKP7T1
Frida for Android Reverse Engineering: https://t.co/3DRoh6JVai
HANDS-ON PRACTICE
https://t.co/JwGtHkXNyi Reverse Engineering: https://t.co/fN8TctIsJH
Malware Unicorn RE101: https://t.co/eZn3B6kCIw
Nightmare: https://t.co/vnyZM6JZiM
https://t.co/rqB6sdQ5ye: https://t.co/cfhqdvjUIN
READ DEEPER
The Ghidra Book, 2nd Edition: https://t.co/ii106DSVjD
Reverse Engineering for Beginners: https://t.co/U0ayZKA7mm
Practical Binary Analysis: https://t.co/sF4Amx6j54
Practical Malware Analysis: https://t.co/cN26SPvKJS
RESEARCH PAPERS
LLM4Decompile: https://t.co/Fq7Ylg6RNZ
SALT4Decompile: https://t.co/5f1rumeCEa
Decomperson: https://t.co/drTzjVvTfj
Does Reverse Engineering Need a Bigger Model?: https://t.co/a03lCuHBr3
REAL INVESTIGATIONS
Notion Clipboard: https://t.co/cX1RHdoAId
DX-Ball Reconstruction: https://t.co/8xMpGBWzoM
Aegis APK: https://t.co/WXrVqlvQyy
TH04 Bullet Patterns: https://t.co/SZn0eKmwjl
You don’t need to read everything in order.
Pick one app. Pick one feature. Rebuild it.
Great topic. One thing that kills agentic malware triage is the model refusing halfway through a sample. That's why we built a security coding plan on an abliterated model, runs in Claude Code, Codex or OpenCode: https://t.co/P3DT5OjOX9 https://t.co/WEFb9q9L2o
Tomorrow: make AI work like an assistant, not an authority.
Lenny Zeltser will demonstrate how to isolate an AI agent, guide it with specialized expertise, ask neutral questions, and verify its claims during malware analysis.
📅 Nov 4 | 11:00 AM ET
🔗 https://t.co/ixSy6m6rJU