I just turned 24.
I quit boxing after 8 years, got into Web3 Security with no tech background, earned $0 for 210 days, then made $100K+ hunting bugs.
11 lessons I wish I knew earlier:
Bug Bounty Methodology with OpenCode CLI – Step by Step
1. Install OpenCode
curl -fsSL https://t.co/c9IOYvtVSN | bash
2. Clone the Bug Bounty Skills
git clone https://t.co/SIAaTKNd6I
cd Agentic-Bug-Hunter
./install_tools.sh
./install.sh --opencode
3. Start OpenCode and Check Skills
Run opencode then type:
do you have bug bounty skills?
4. Core Workflow
• Scope (never go out of bounds)
• Recon
• Hunt
• Validate
• Report
5. Run Recon
recon https://t.co/yM8s8wg5ju
(It handles subdomains, live hosts, crawling, and nuclei)
6. Hunt for Bugs
It covers IDOR, Auth Bypass, XSS, SSRF, Business Logic, SQLi, File Upload, GraphQL, and more.
7. Autopilot Mode (Optional)
autopilot https://t.co/yM8s8wg5ju --normal
8. Generate Reports
After validating a finding,
type report to get a clean, professional report with CVSS, PoC, and impact.
Repo: https://t.co/SIAaTKNd6I
Cursor Pro is FREE 😳
- no student ID needed
- open to everyone worldwide
- normally $20/month
- claim your code through MLH
ends October 15
claim here: https://t.co/IugBkZlViW
Recon is EVERYTHING in bug bounty 🎯
Before you run a single tool, understand the app:
1️⃣ Check the business. What does it actually do?
2️⃣ Google it, browse the app like a user
3️⃣ Watch videos, read Reddit posts
4️⃣ Learn the app in and out
Then bring the tools:
- Subdomain enum: subfinder, assetfinder, findomain, https://t.co/OUKa7k6rzJ, https://t.co/N9xpqrlKOM
- Live hosts: httpx
- URLs: waybackurls, waymore
- Full chain: reconftw, or build your own pipeline
@Reddit Please take another look at my ban appeal. My account was banned for spam by mistake, and I believe the decision was incorrect. I’ve submitted an appeal and would really appreciate it if someone could review my case. Thank you 🙏
Bug Bounty Methodology with OpenCode CLI
1/10
Turn your terminal into an AI-powered bug bounty machine.
Recon → Hunt → Validate → Report — all inside OpenCode.
No more context-switching. Just pure hunting flow.
#BugBounty#OpenCode#CyberSecurity#WebAppSec
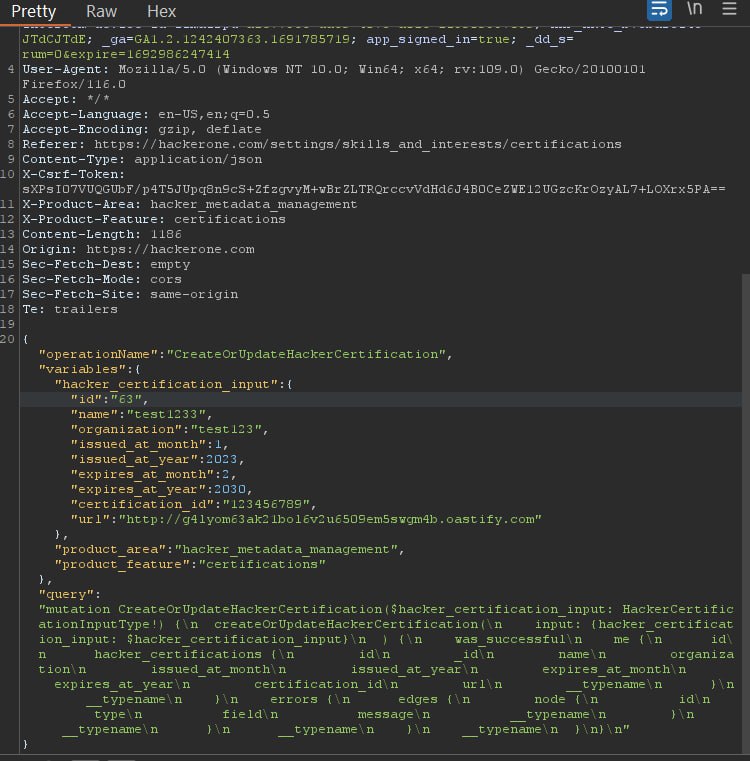
$12,500 IDOR - Delete all Licenses and certifications from users account using CreateOrUpdateHackerCertification GraphQL query on HackerOne by Harsh D Ranjan (harshdranjan) 🤯
🔗 https://t.co/2TLLEXpOWJ
Join team 👉https://t.co/pJWHoCMDix
Performing recon can take hours of your time... 😅
Recon-skills by @uphiago packages 169 offensive security skills into an AI-ready toolkit, covering everything from subdomain enumeration and vhost discovery to JS analysis and GitHub secrets, all tested across 600+ real targets in 45+ sectors! 🤠
Check it out! 👇
https://t.co/1zEMvDU47e
Bug bounty talks that are 5+ years old
and still produce bugs nobody else is
finding.
Most hunters watch the latest recon
tool demo and skip the talks that built
the methodology they're using without
knowing it.
Here are 10 forgotten talks 🧵 that still pay