The operating system controls file access in Linux by utilizing file permissions, attributes, and ownership. In Linux, file permissions, attributes, and ownership determine the level of access that system programs and users have to files.
Learn more about Linux file permissions
You can now probe for password-reset hijacking via DNS poisoning directly in Burp Suite, using the DNS Analyzer extension from @sec_consult! Can't wait to try this out.
https://t.co/U2da1uGpV3
Find well-hidden subdomains using the power of ✨permutations✨ with chaos, alterx and dnsx! 💪
Generate subdomain permutations using alterx on an existing list of passive subdomains from chaos and resolve using dnsx!
This yielded us 7 new subdomains! 👇
1/ Last month, I dived into a bug bounty, taking on the challenge of bypassing a Web Application Firewall (WAF) for XML External Entity (XXE) injection. Buckle up, here's the story! #Tip#BugBounty#AppSec 🧵
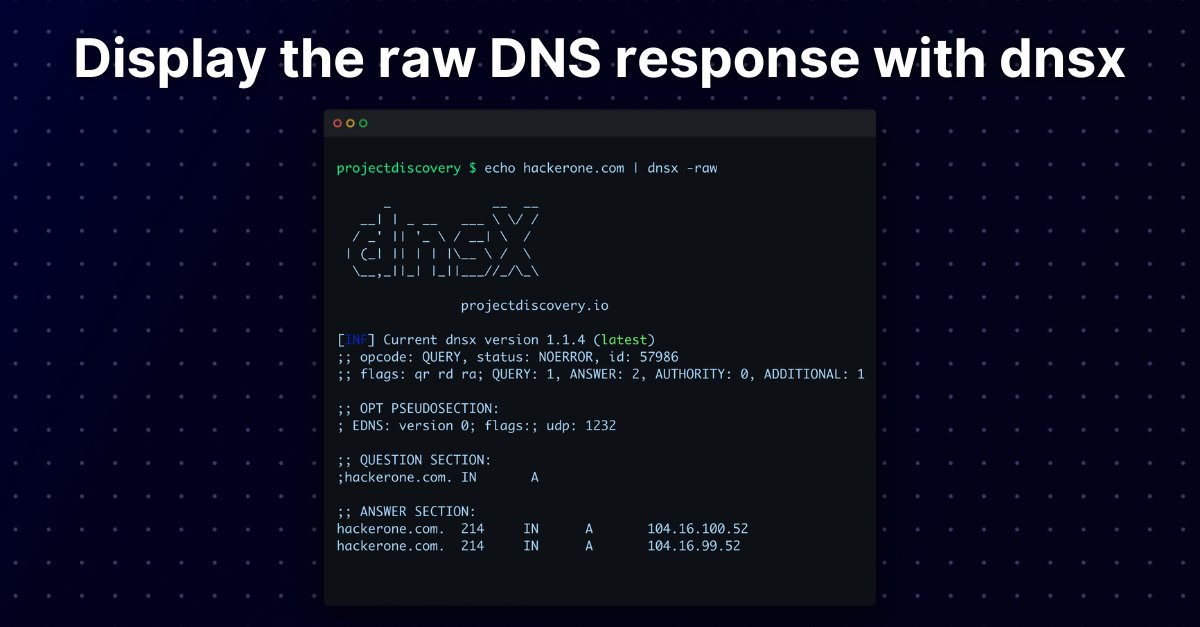
If you prefer viewing the raw DNS response from your DNS enumeration tools you can use the dnsx -raw option! 👇
Install now 👉 https://t.co/1319t7GKtL
#hackwithAutomation#DNSenumeration#recon
The @assetnote security research team was successful in reproducing the MOVEit Transfer SQLi->RCE attack vector. We will be releasing the payload in 30 days, but we help bootstrap researchers through our most recent blog post: https://t.co/0UD1ozjHYc
🚨 ✨NEW✨ blog alert! 🚨
Nuclei isn't just for Christmas 🎄... I mean "HTTP"! 🤩
⚛️ Learn how to use Nuclei for TCP, DNS, Files, and Headless protocols in our latest blog post! 👇
#Nuclei101#Security#HackwithAutomation
https://t.co/LzAcmytobd
Celebrating Trickest 2.0 and the lightening-fast ⚡️ new workflow engine with a #giveaway! 🥳
We're giving away 5 monthly PRO licenses!
Here's how to enter:
1️⃣Like & retweet this post
2️⃣Follow @trick3st
3️⃣Tag 2 fellow #bugbounty hunters in comments
⏰ 7 days to enter!
Introducing the Nuclei Foundation 🎓
⚛️ Learn all things Nuclei from installation to using filters to writing your own templates!
⚛️ 6 Nuclei Tutorials to get you started and more to come 📹!
If you're new to Nuclei, start here! 👇
#Nuclei101
https://t.co/xjrGFerPwl
Nuclei supports markdown export of valid findings with -markdown-export flag! 📇
⚛️ Include requests/responses in the markdown report when -irr flag is used along with -me!
Heres a basic example 👇 #Nuclei101
A guide to finding subdomain takeovers with ProjectDiscovery Tools! 🚀
This blog covers:
🌀 Recon
🌀 Building to PoC
🌀 Remediation
🤩 Maybe you can get your first subdomain takeover too! 👇
#HackWithAutomation#security#hacking
https://t.co/G64avj7AFM
Bug bounty hunters: want a #bugbountytip on finding the right public programs to participate in?
1️⃣ Look at some of the more successful bounty hunter's profiles (if they are public)
2️⃣ Scroll down to their most awarded or participated in.
3️⃣ Hack those. There's vulns there.
Discover the origin host to bypass WAFs with hakoriginfinder! 🔥
How?
1️⃣ Supply it with a list of IPs and a hostname
2️⃣ It sends HTTP + HTTPS requests to all IPs
3️⃣ Compares responses with the real website's response
Find out how 👇 #hacking
https://t.co/8eXRcWo1em