Malware Evasion Techniques
Part 1: Process Injection and Manipulation
Part 2: Anti-VM Blog
Part 3: Anti-Sandboxing
Part 4: Living Off The Land
https://t.co/iTaEkKHBnc
THIS IS DANGEROUS.
Someone just open-sourced an AI hacking army that runs autonomous pentests.
It's called Sapper.
Sapper-v2 has 986 GitHub stars, and its Docker image ships Nmap, Nuclei and a full Kali toolchain 👀
The play: clone the repo > install the CLI > point it at a lab you own > let the commander dispatch agents
> First steps
- Go to: https://t.co/pkNprVnAsj
- git clone https://t.co/pkNprVnAsj
- cd sapper-v2
- bash https://t.co/weZlahexiA
- sapper setup --goal "assess http://your-lab-target" --agents
- sapper status
- For the full swarm, build the commander Docker image or load the v18-champion release
- Wire Claude Code or Codex as the agent CLI, and add your model API keys
> What you get
- One AI commander that plans, plus a swarm of worker agents
- Real tools (Nmap, Masscan, Nuclei) inside a Kali environment
- A shared fact graph and an offline knowledge base of 50+ playbooks
- MIT license
> The catch
- The Tencent "634 teams / 8 hours unattended" win comes from the author's own battle report, not an independent results page
- The repo is FREE; the models are not. You still pay for API tokens
- It was built for CTF-style arenas. Real networks need a written scope and a human on the kill switch
> What not to do
- Don't point it at any system you don't own or have written authorization to test
- Don't treat "authorized labs only" as optional. Unauthorized scanning is illegal
- Don't leave API keys or live sessions on a shared machine
Run it on a lab or CTF range first, with a clear target list and a way to stop it in one command.
Which lab or CTF would you try it on? Reply below.
Bookmark this for your next authorized red-team drill.
HOLY F*CK, can't believe my eyes, someone leaked an entire reverse engineering degree on GitHub.
This free stack completely automates dissecting closed binaries, applications, and firmware using AI agents:
1. radare2 → Full binary analysis straight in the terminal.
Replaces heavy GUI tools and lets you tear through code via scripts and CLI.
Instant execution file analysis on remote headless servers.
↳ https://t.co/HLFQkpSs8X
2. Ghidra → Free decompiler matching high-end enterprise suites.
NSA's open-source tool that completely covers commercial decompiler needs.
Visual call graphs, structured control flow, and automated logic recovery.
↳ https://t.co/LCrxavTuqy
3. LLM4Decompile → Neural machine code translation into clean C.
Specialized model that reconstructs variables and function structures after compiler passes.
Turns stripped assembly into readable source code in seconds.
↳ https://t.co/amFQlx3ujI
4. r2ai → Local AI copilot embedded in your terminal debugger.
Integrates language models directly into your active session without external chat switching.
Explains dense logic and flags cryptographic routines or bugs during live execution.
↳ https://t.co/NnyTnGfggC
5. reverse-engineering-assistant → Bridge Ghidra to AI agents via MCP.
Model Context Protocol server opening symbols, functions, and memory to external LLMs.
Lets Claude Code or Cursor explore target codebases and deobfuscate variables autonomously.
↳ https://t.co/tolqcDEXTS
6. ida-pro-mcp → Full IDA Pro orchestration without manual clicking.
Drives the industry-standard decompiler over Model Context Protocol.
Delegates xref tracing, batch symbol mapping, and binary patching directly to agents.
↳ https://t.co/aIsECl3MnF
7. REA → Autonomous software reverse engineering on autopilot.
Engine handling 35 target types: native binaries, Android APKs, Electron apps, and firmware.
Ingests a closed-source target, pinpoints target features, and generates verifiable evidence for replication.
↳ https://t.co/nE4S4GMBgp
Analysis → Disassembly → Neural Decompilation → MCP Bridge → Autonomous Report.
Bookmark this. The era of manual bytecode grinding is over ↓
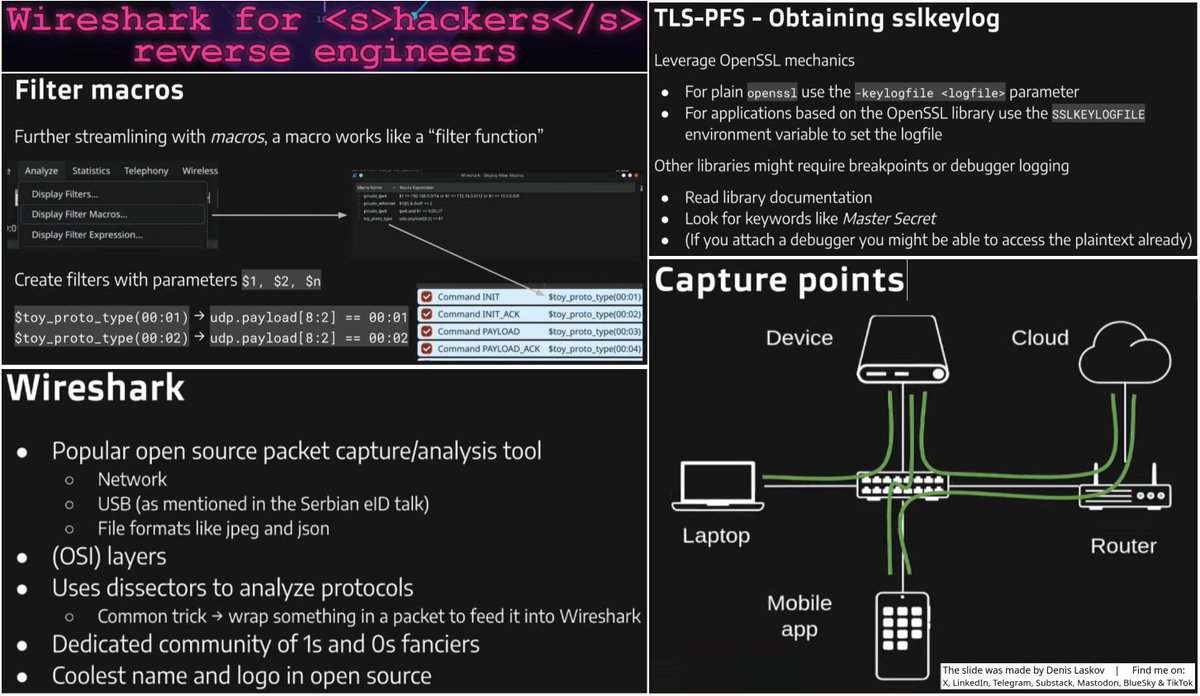
Crash course on Wireshark for reverse engineering: The missing training for hackers and security researchers. ➿🦈🛠️🏴☠👨🏻💻
More details on:
LinkedIn: https://t.co/LPRQaZt5Cm
Substack: https://t.co/yNpJte28PD
Telegram: https://t.co/H5e8YoYwzJ