Interesting paper title😀
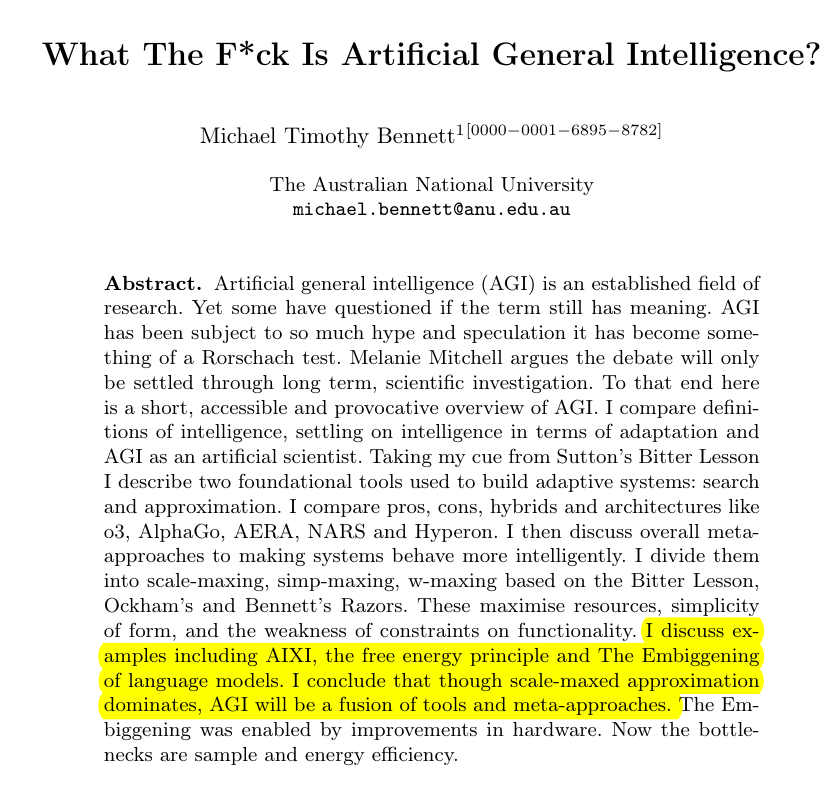
"What the F*ck Is Artificial General Intelligence?"
It defines intelligence as adaptability under limits of compute, memory, and energy.
So AGI is a system that adapts at least as generally as a human scientist
That means it should be able to plan experiments, learn cause and effect, balance exploration and action, and operate with autonomy.
The paper calls this type of AGI an artificial scientist, because it is judged by its ability to discover and adapt across many tasks, not just by passing human-like tests.
So AGI is not just “human-level AI” but a whole system that can adapt broadly, efficiently, and scientifically, at least as well as a human scientist.
----
arxiv. org/abs/2503.23923
🤼♂️ Cloudgrappler
@permisosecurity built a tool to easily scan your logs for TTPs using @cadosecurity's cloudgrep
Supports AWS and Azure, and comes prepackaged with a set of intel-based detections for cloud threat actors
https://t.co/wS1LXLRDMj
Free tools for searching social media posts by geolocation:
Reddit Hunt https://t.co/16Teu8q14A
Bird Hunt https://t.co/xN4VNKlE7Y
Insta Hunt https://t.co/sIQes3oxTa
Creator @LouisTomosEvans#geoint
⛅ Cloud Security Maturity Model Assessment v2.0
v2 of the CSMM expands into a practical framework for cloud security programs
* 12 categories
* 3 domains
* ~100 control objectives, many mapped to AWS controls
by @securosis@rmogull@cloudsa
https://t.co/vMSUwBcYPJ
Late next week I will open up the registrations for my new course “Red, Blue, Purple AI”
I am so excited.
I basically brain dumped my 20 years of security, and an intense year of LLM research, into it.
It really is something special. See you soon!
🫡🧙😎🤓
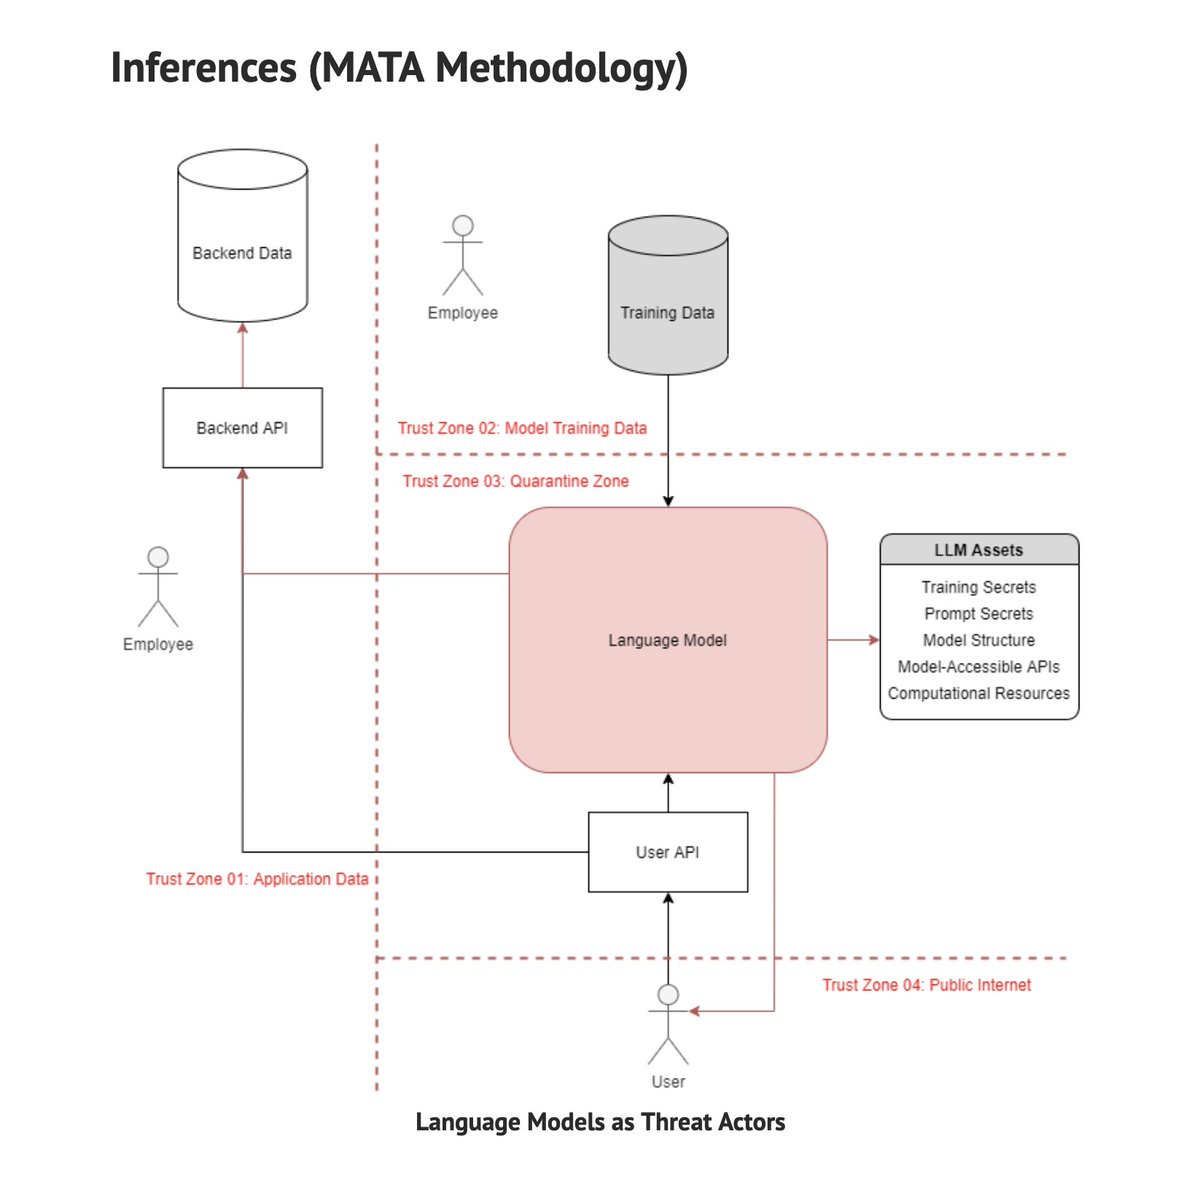
🤖 Analyzing AI Application Threat Models
An analysis of the attack surface of apps that employ AI
→ Attack vectors enumerated by a Models-As-Threat-Actors (MATA) methodology
→ Security controls & how to validate them
By @NCCGroupInfosec
https://t.co/TG5sftj6f1
📦 Simulator: A Kubernetes security training platform
Creates a Kubernetes cluster in your AWS account; runs scenarios that misconfigure it and/or leave it vulnerable, trains you in mitigating them
→ 9 CTF scenarios
By @controlplaneio
https://t.co/w4v70q2AnY
🛠️ API Detector
Tool to efficiently scan for exposed Swagger endpoints across web domains and subdomains.
By @brinhosa#bugbountytips
https://t.co/MzQS7uvcRB
I wanted to share an excited news Packt has given me #Christmas#Birthday and #Newyear Gift.
i just published my first book, Implementing DevSecOps Practices: Supercharge your software security with DevSecOps excellence. 📚
https://t.co/fGdEGNleQl
#firstbook#bookpublished #devsecopsimplementation
💼 Inject My PDF: Prompt Injection for your Resume
@KGreshake shares a tool that injects invisible text into your resume PDF to make any AI LLM that reads it think you are a perfect candidate
https://t.co/OIJ887fd3u
🧠 Vulnerability Management: You should know about EPSS
@Magoo on the value of the Exploit Prediction Scoring System → the probability of a CVE being exploited in the wild within 30 days
Helps you prioritize, as most High/Crit CVSS are not exploited
https://t.co/w7eNNFAXXw
🤦 The massive bug at the heart of the npm ecosystem
npm package manifests are published independently from their tarball
Manifests are never fully validated against the tarball's contents
Tooling assuming they are the same can be tricked
By @darcy
https://t.co/MIR1FaoRnj
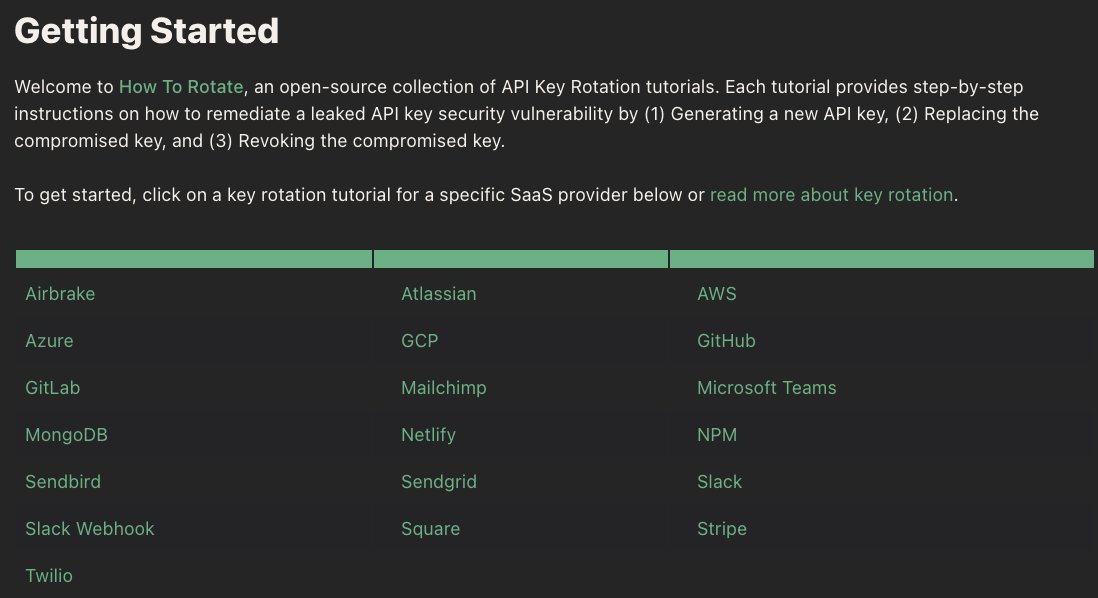
🔑 How to Rotate: Key Rotation Tutorials
Open source key rotation tutorials covering a number of SaaS providers, describing step-by-step instructions on how to remediate leaked API keys.
By @trufflesec
https://t.co/QWArR6qyIL
😱 4,500 of the Top 1 Million Websites Leaked Source Code, Secrets
→ Found by searching <domain>.com/.git
* AWS/GitHub keys: 45% leaked credentials
* 67% of GitHub creds had Admin Access
B y @trufflesec, @harshbothra_, @hakluke
https://t.co/en4uOl8yAW
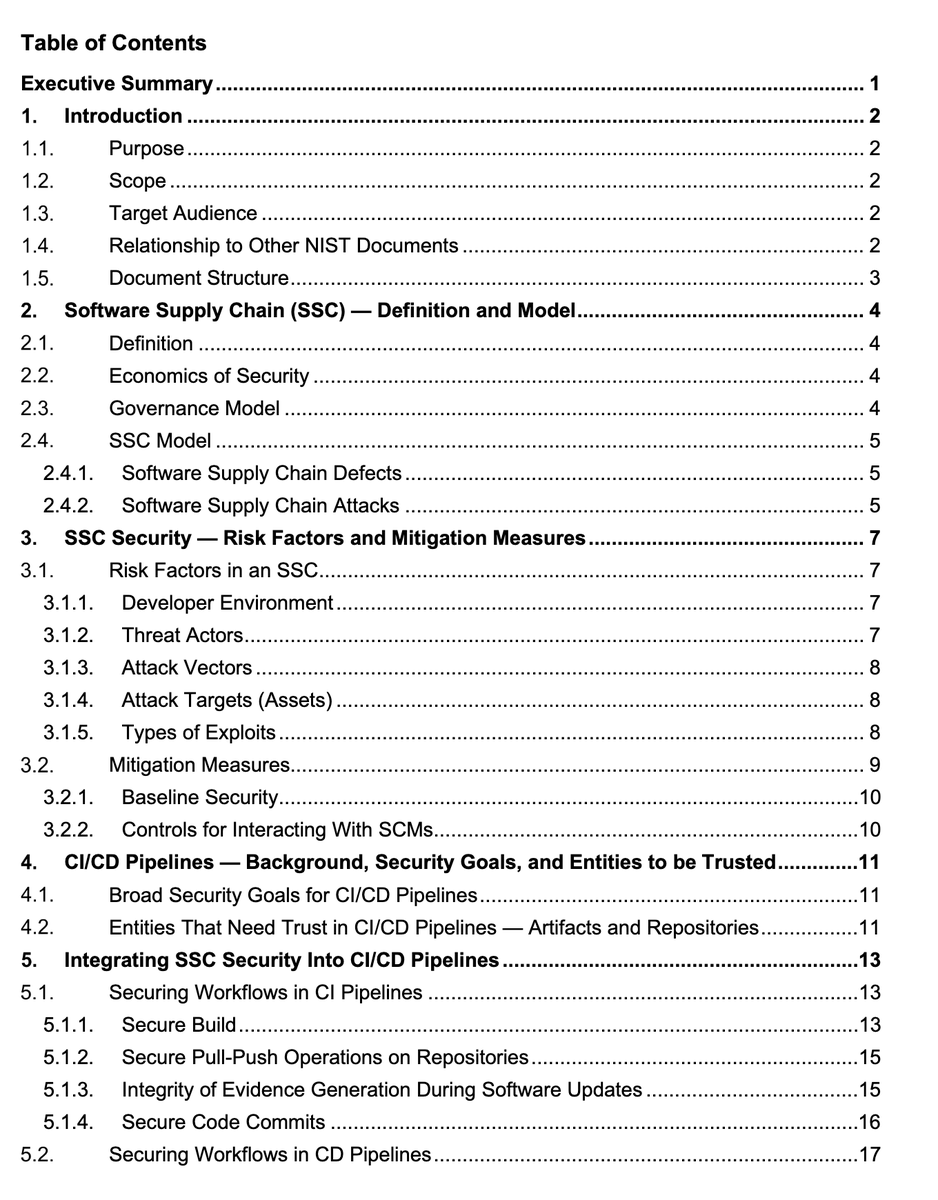
🛡️ Strategies for the Integration of Software Supply Chain Security in DevSecOps CI/CD Pipelines
37 page PDF from @NIST
* Risk factors and mitigation measures
* CI/CD security goals
* Securing workflows in CI pipelines
+ more
https://t.co/NzBvjE1sqz