4 WEEKS. 1 CHALLENGING PROJECT. SUBMITTED AT LAST! 💃
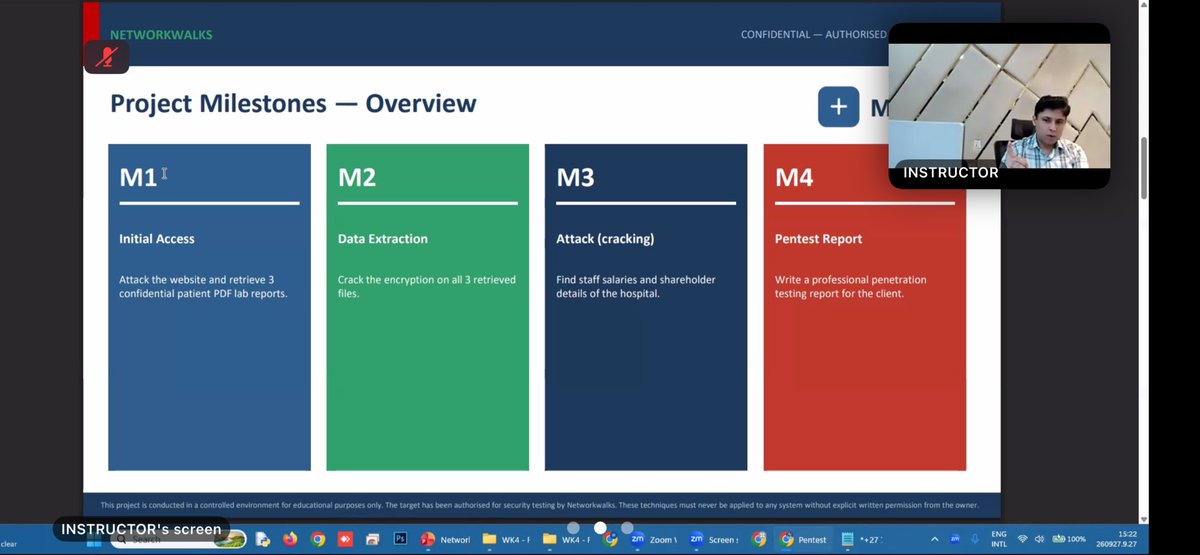
Wrapped up my Week 4 Full Black-box Pentest Assessment with @networkwalks 🎯
What was done:
• Recon & OSINT on target domain
• Bypassed Patient Portal auth via SQLi
• Extracted & cracked password- (completed in comments)
• Uncovered exposed DB backups leaking salary & shareholder data
• Delivered a full pentest report with remediation strategies
Key takeaway: A single weak login form can cascade into a full system compromise.
Huge thanks to Waqas Karim (CCIE) for the mentorship! Exams is next!
Day 3 - Enable Multi-Factor Authentication
“One lock is good. Two locks are better”
A password is important, but it shouldn’t be your only line of defence. Multi-Factor Authentication (MFA) adds an extra layer by requiring additional verification before access is granted.
If an attacker gets your password, they still can’t get in without that second factor. Where available, choose phishing-resistant MFA methods (such as hardware security keys or app-based authenticators), and never approve a login request you didn’t initiate.
Quick tip: Treat unexpected MFA prompts like suspicious calories, don’t accept them. If you didn’t request it, deny it.
What would you do if you received an unexpected MFA request right now?
Your password is your front door. Will you leave it open or guard it?MyWeek 3 with @NetworkWalks was all about password cracking & hash analysis.
The practical showed me just how quickly weak/common passwords can be recovered.
@hassanoguns@Ogechee_ Please enlighten me, a hash isn’t normally recovered, what are tools like JTR used for? Don’t the analyse the hash and produce the plaintext pw?
Cybersecurity is such a vast and fascinating field!
I used Maltego a few weeks ago without fully understanding its setup & capabilities. Now that I’m learning how powerful it really is, I’m amazed at how much more there is to explore.
Grateful to my instructor, @waqaskarim 🙏🏾
Two-in-one again! 🥳💃🏾💃🏾
Completed one, started another!
I’m ready for all it takes to growth in this field!😌
So help me God!
#cybersecurity#internship#networkwalks#growth
It’s that time of the year ✨
Applications for my 2026/27 mentorship cohort open on September 12, 2026. If you’re interested in joining the next cohort, this is your opportunity to put your best foot forward.
Eligibility criteria:
Passionate about Cybersecurity
Access to a laptop
Availability to commit to tasks and learning activities
Strong communication and collaboration skills.
Application process:
Stage 1: Submit a pitch on X (link below) or a video pitch (link will be shared after the X Space.
Stage 2: Shortlisted candidates will be interviewed, with final selections made in October 2026.
If you know someone who would benefit from this opportunity, feel free to share this post. Good luck 💪 https://t.co/H4R5HizK2L
August was great. 🥳I pushed my self near my elastic limit! I was able to keep 4-Weeks Internship @AFRIMENT running, while making content, sales and taking orders for @idspeciale This month, I’m going all out to utilizing all the resources I can lay my hands on in #cybersecurity
Started the year with leather and sole. Ended the month with a cybersecurity certificate! Turns out shoe making and cybersecurity have a lot in common after all! Thank you @TechSphereAcad for this huge opportunity! Excited for what’s ahead! #cybersecurity#