Excited to finally share my recent research, where I managed to hack Chrome, Comet, Edge, Opera and Claude in Chrome using one single browser extension
2 CVEs & $20,000 in bounties 🙂
Introducing - BragJack!
https://t.co/XJIQ4Yf5Oo
Written on January 8, 1986 by The Mentor - Phrack Magazine
𝑻𝒉𝒆 𝑯𝒂𝒄𝒌𝒆𝒓 𝑴𝒂𝒏𝒊𝒇𝒆𝒔𝒕𝒐
“Another one got caught today…”
“I am a hacker. Enter my world.”
“This is our world now… the world of the electron and the switch, the beauty of the baud.
We explore… and you call us criminals.
We seek after knowledge… and you call us criminals.
We exist without skin color, without nationality, without religious bias… and you call us criminals.”
“Yes, I am a criminal. 𝐌𝐲 𝐜𝐫𝐢𝐦𝐞 𝐢𝐬 𝐭𝐡𝐚𝐭 𝐨𝐟 𝐜𝐮𝐫𝐢𝐨𝐬𝐢𝐭𝐲.”
“You may stop this individual, but you can’t stop us all… after all, we’re all alike.”
Thank you, @DarknetDiaries (@JackRhysider ) for the true stories from the dark side of the Internet. Best podcast ever.
I’ve always wanted to be a cybersecurity researcher. Not just to find vulnerabilities, but to write about them.
I know that might sound a bit silly to some, but I’ve always loved the idea of reading security articles, research about them and turning them into a clear story.
The writing forces me to truly understand what I’m learning.
I like it, it helps others, and it also helps me grow.
And I care a lot about how these posts are written.
I like them focused, not rambling.
Accessible, even to people coming from different areas of security, so they can fully understand the point of the article.
And most importantly, I want them to be worth the few minutes someone chooses to spend reading.
Sometimes the value comes from simplifying something complex. Sometimes from going deeper technically.
Either way, the goal for is the same: to give something back.
I’m always glad to contribute to the cybersecurity community that’s given me so much, and I’m always happy to get feedback. It helps me improve.
For my latest blog post:
𝐍𝐨𝐭𝐞𝐩𝐚𝐝++ 𝐔𝐩𝐝𝐚𝐭𝐞 𝐌𝐞𝐜𝐡𝐚𝐧𝐢𝐬𝐦 𝐇𝐢𝐣𝐚𝐜𝐤𝐞𝐝 𝐛𝐲 𝐒𝐭𝐚𝐭𝐞-𝐒𝐩𝐨𝐧𝐬𝐨𝐫𝐞𝐝 𝐀𝐜𝐭𝐨𝐫𝐬 𝐟𝐨𝐫 𝐒𝐢𝐱 𝐌𝐨𝐧𝐭𝐡𝐬
https://t.co/4VffiYjedM
And for everything I’ve published so far:
https://t.co/c54x9DQAVt
We're excited to announce one of our giveaways thanks to "@CaidoIO" 🎉 We will pick 5 winners to win a 1-year Caido Pro license!
To enter:
1️⃣ Follow us @BugBountyDefcon and @CaidoIO
2️⃣ Like this post ❤️
3️⃣ Retweet this post 🔁
You have time to participate until Friday (9/13)!
@BadAt_Computers Wow happened to me countless times, I always tried to cheer myself up by saying that probably it wasn't intended to be yours, and what needs to be yours will be in the future..
The dots will connect in the future, just keep your head up and look for the future
Hey @Shopify@Hacker0x01 ...
I have had two bug hunters come to me and tell me horror stories about your bug bounty lately.
Valid bugs being exploited and you coming out saying... "oh we had planned on fixing that... no impact"
That is NOT the bug bounty contract. If there is a PoC showing the bug was exploitable at ANY time, you should pay the researcher.
Don't contribute to a bug bounty community that makes researchers think bug bounty is a scam.
Also - dont hide behind the new CVSS. Program owners looking to downgrade bugs to save money using the new CVSS and splitting bugs are SUPER scummy.
Contact @G0LDEN_infosec
In case you missed my #defcon31 talk, the recording is now available!
In this presentation, I reveal my strategy for manipulating targets in the Android source as a unique form of obfuscation.
https://t.co/fadTvFouIT
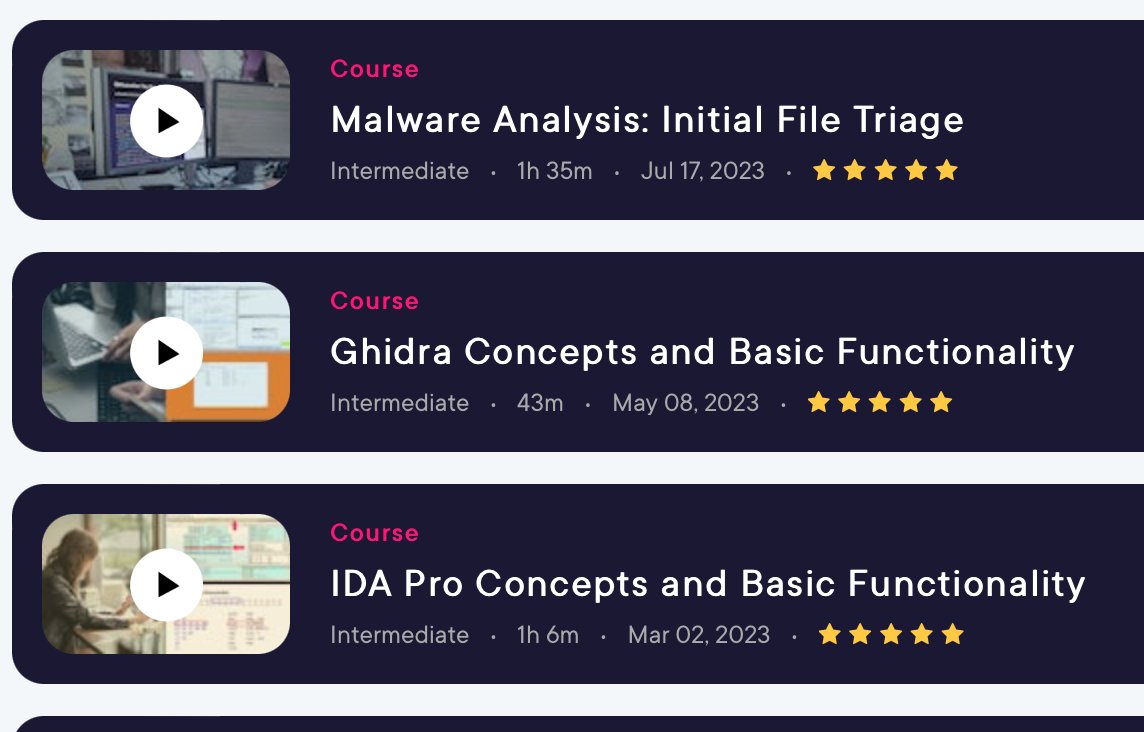
If you're looking to get started in #malware#analysis/#reverse#engineering consider my 3 latest courses on @pluralsight to help get you started!
🛠️ Basic File Triage - https://t.co/0QAe9cBi52
🐲 #Ghidra - https://t.co/ZW8xIXp4VJ
🔍 #IDAPro - https://t.co/rAO9OXhxUN
Why a "cybersecurity vs. everyone" mode of operating is counterproductive, and how to foster a collaborative environment. via @lennyzeltser https://t.co/fLaNDxPxvh
New ARM Assembly Series Video!
In this lesson, we add the ADD, SUB, and MUL instructions to our repertoire. We also take a look at the different flags of the CPSR and how we can set them by adding "S" to the instruction mnemonic
https://t.co/NErJf9vYag