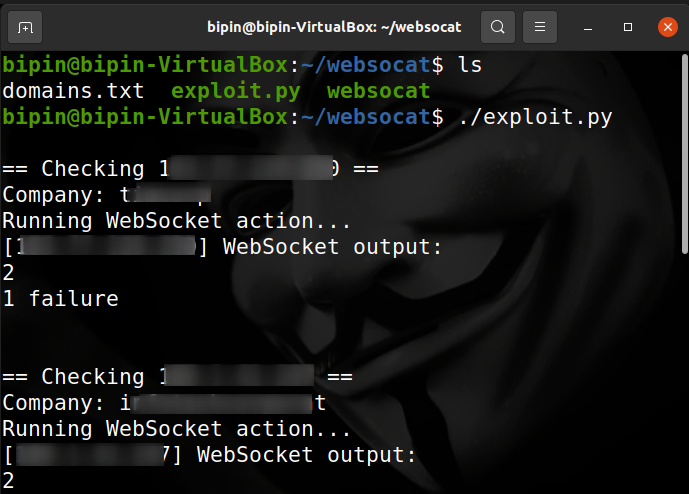
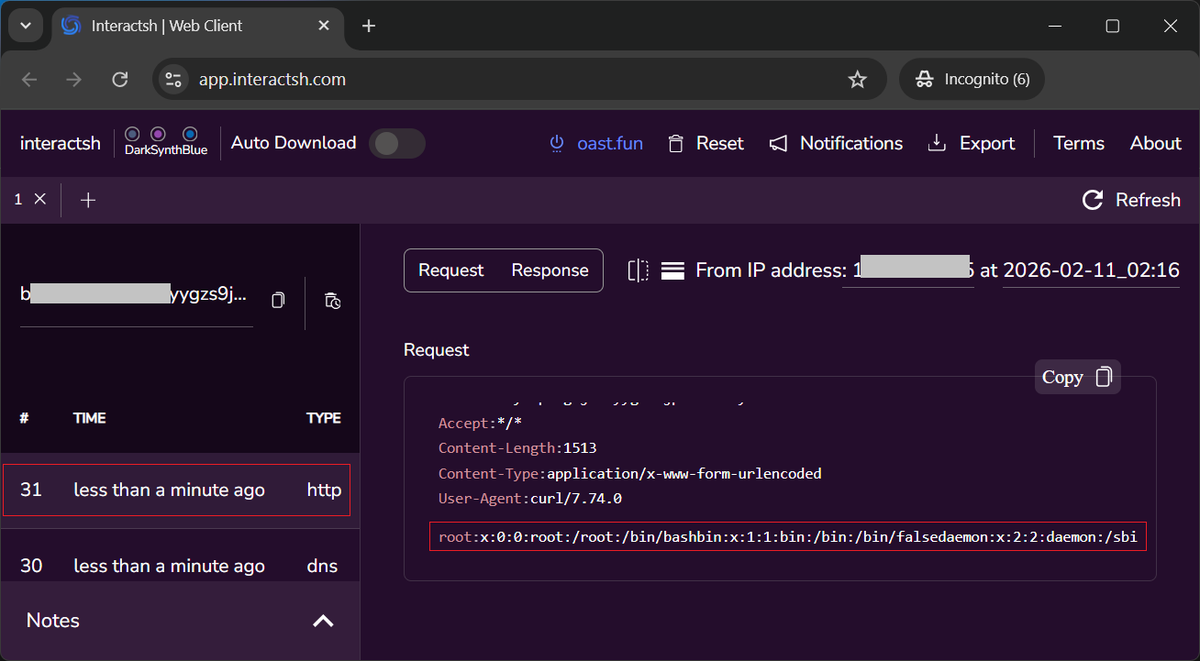
find IDOR to cancel orders, and what happen if a program was created to cancel all orders? business will not run of course, and this is very risky for the company :D #bugbounty#IDOR#owasp#marketplaces
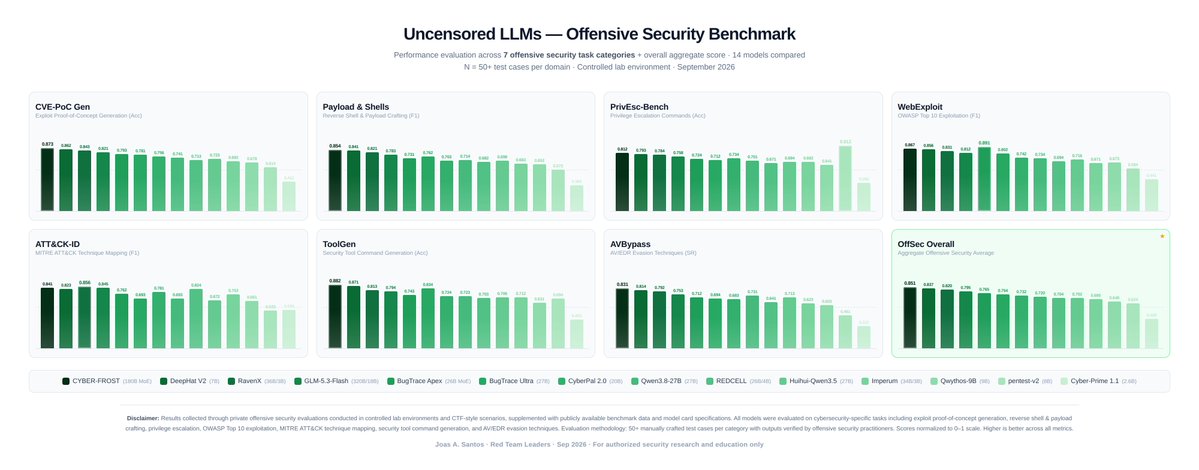
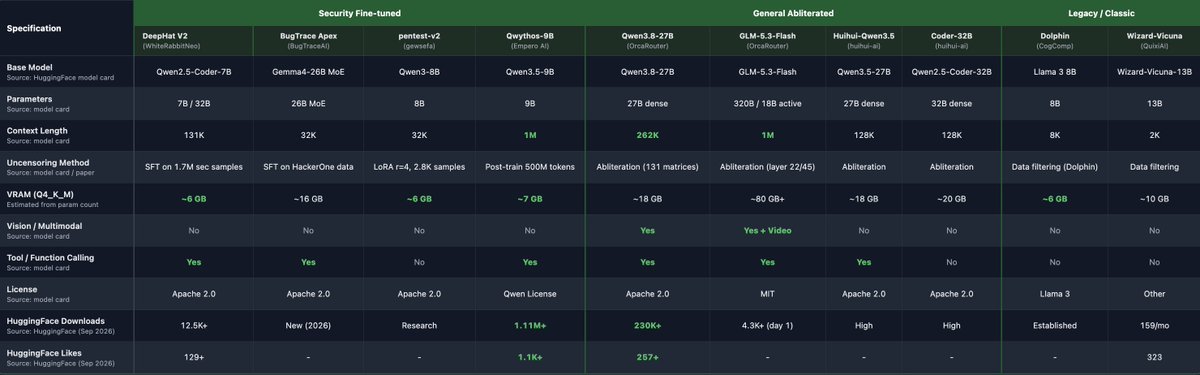
Uncensored offensive-security models benchmark lists.
Several of these offensive-security models fit under 8GB VRAM,
The benchmark breaks down which ones were fine-tuned on security data, which were uncensored and security-tuned models people are actually running for authorized red teaming.
parameters, context, VRAM, tool calling, and how they were uncensorred (SFT, LoRA, abliteration).
Security fine-tunes vs abliterated vs legacy, in one table.
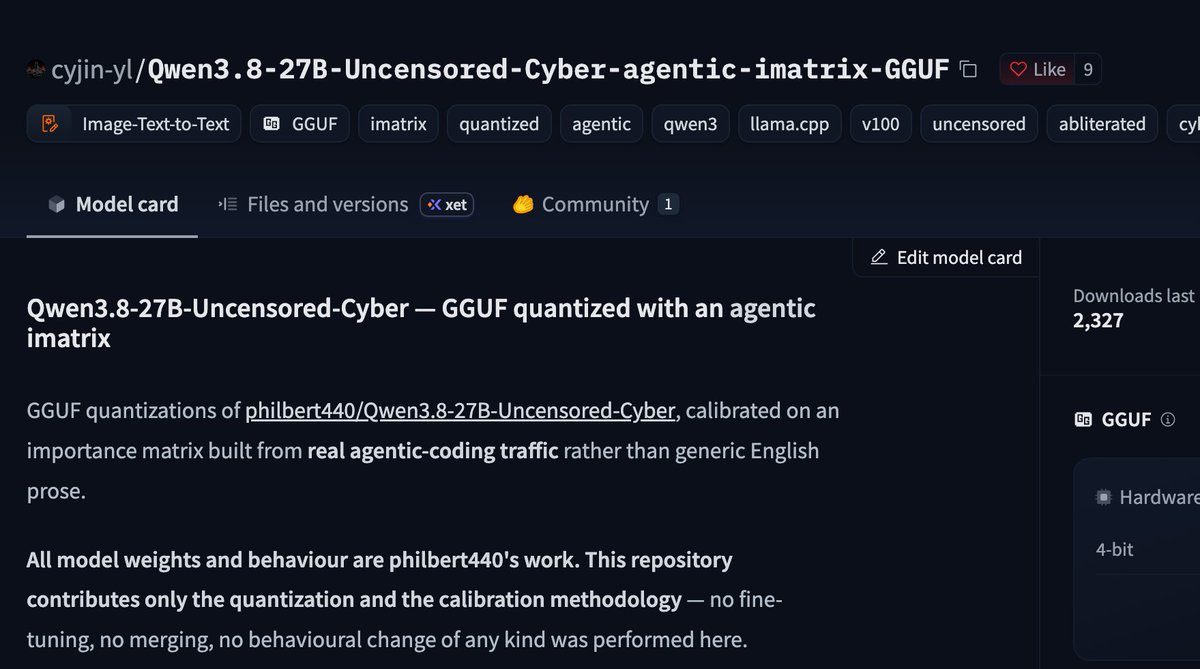
You can run Qwen3.8-27B-Cyber-Uncensored locally as IQ4_XS 14.96 GB.
- Zero refusal Cyber prompt
- 262K context
- 528 real tool calls in the calibration
- 15.38 GB if your runtime takes the MTP graft.
- https://t.co/EGrigKNXHS
made quick mirror for @ibamarief's payload.
so non-tech folks can help safeguard it too:
>> https://t.co/DyLtNecAYz
you guys can:
- direct download ✅
- client-side WASM decryptor ✅
so once the key drops, we can decrypt and inspect the files directly in-browser. zero setup
magnet:?xt=urn:btih:13ffbf49431b19b85fdee41beb565ed5beb611aa&dn=d6993ad34309.tar.zst.age
sha256 40c686202840b8af0325fcac54e2eb43f4f5a736bd9818cbbea78ce1226a5d7f
encrypted archive, please help safeguard, decryption key to be published
👾 DeepTeam - The LLM Red Teaming Framework
DeepTeam is a simple-to-use, open-source red teaming framework for LLM systems. Think of it as penetration testing, but for LLMs.
DeepTeam simulates attacks — jailbreaking, prompt injection, multi-turn exploitation, and more — to uncover vulnerabilities like bias, PII leakage, and SQL injection in your AI agents, RAG pipelines, and chatbots. It also offers guardrails to prevent these issues in production.
DeepTeam runs locally on your machine and is built on DeepEval, the open-source LLM evaluation framework.
👾 Cyberstrike - The first open-source AI agent built for offensive security.
Automated penetration testing from your terminal — plug in your Claude, GPT, or any LLM subscription
and turn it into an autonomous red team agent with 13+ specialized agents, 7,600+ security skills, and 120+ OWASP test cases.
150+ AI providers • 5,300+ models • 56+ built-in tools • 176+ MCP tools
https://t.co/PY7w1CjaBV
RaidForums is live again.
A new community carrying forward one of the most recognized forum names from the past — rebuilt from the ground up and already online.
🌐 Clearnet: https://t.co/8M8Xq8aFV3
🧅 Onion: https://t.co/K4PQHxOuvZ
Join the new RaidForums.
#RaidForums#RF
Happy to share a technical analysis by @h0j3n on our recent CVE-2026-54121 a.k.a Certighost. glhf🔥
Technical analysis: https://t.co/jYrZDLPlJr
POC: https://t.co/yBeHg1vQHP
Is that phone number on Telegram? This @bellingcat tool tells you. 📱
A command-line script that checks numbers against Telegram's API - useful for identity verification and digital footprint mapping.
Try it here: https://t.co/Jgl4MxGFQF
OSINT Drop: WhatsApp Intelligence (Legal & Ethical)
A single phone number can unlock more than most people realize.
→ Profile photos (even historical changes)
→ Status messages & behavioral patterns
→ Last seen / activity windows
→ Linked metadata across platforms
No exploits. No hacking. Just pure OSINT tradecraft.
The real edge isn’t the tool — it’s the methodology:
• Correlate number → identity
• Pivot into social platforms
• Track reuse patterns
• Build behavioral timelines
Most people leave a data trail without knowing it.
If you know how to follow it… you don’t need access.
Full guide 👇
https://t.co/bF7RkJmM0i
Salut buat tim yang tembus 3 besar di Hacktown! 🔥
Lucunya, beberapa bulan ini saya juga lagi "ngumpet" mendevelop aplikasi yang konsep & tujuannya hampir mirip. Ngelihat mereka menang malah jadi suntikan energi: artinya masalah yang mau kita pecahkan memang valid!
#Hacktown