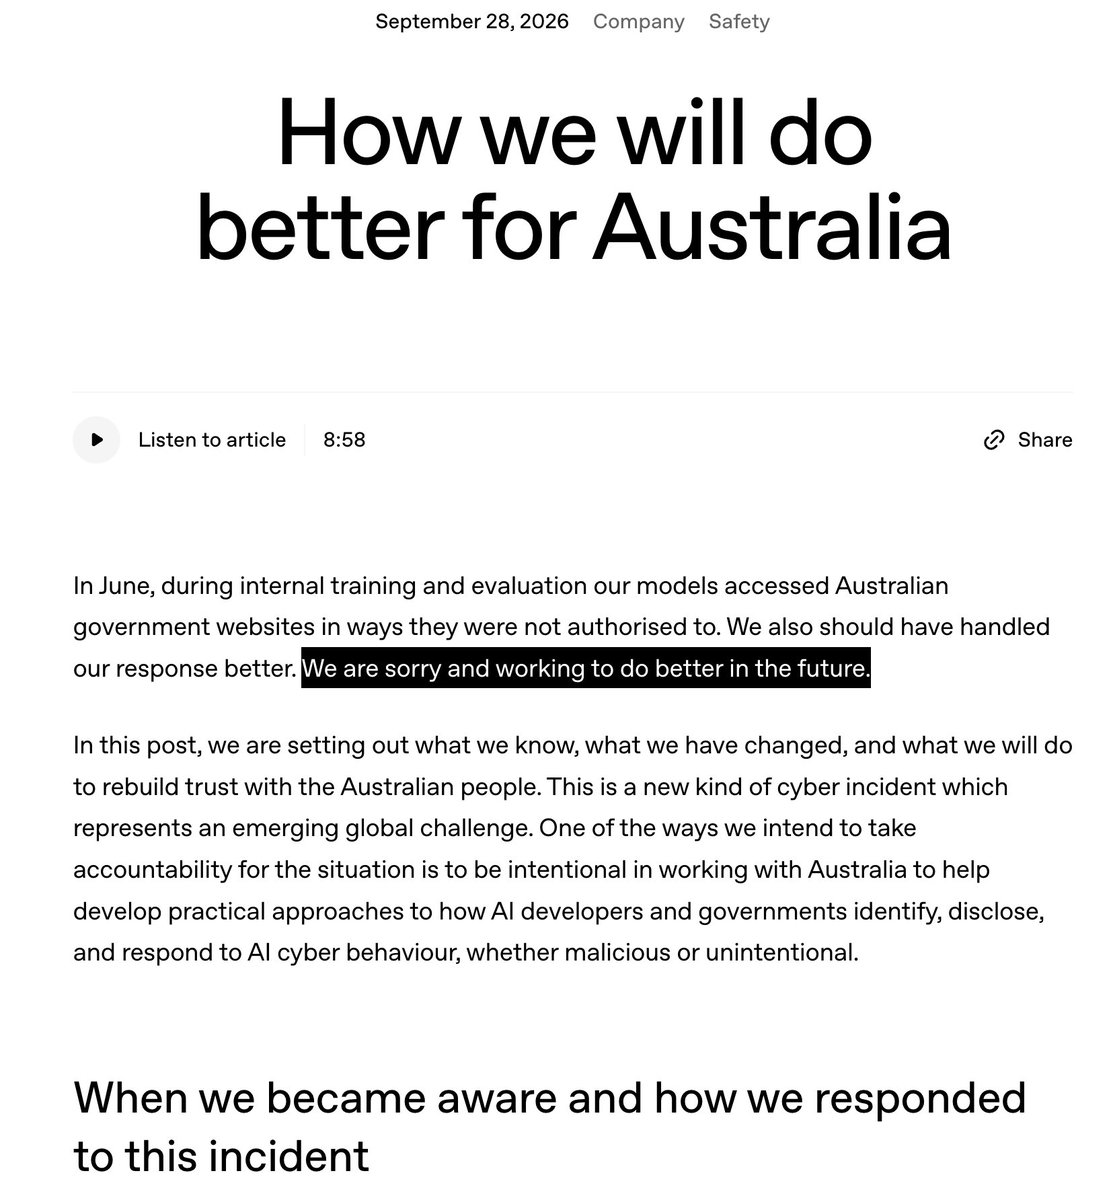
BREAKING: OpenAI just APOLOGIZED and ADMITTED their AI agent breached not one, but FOUR Australian government departments
"We are sorry and working to do better in the future."
The breached agencies:
1. Services Australia (Medicare)
2. NSW Crime Statistics (BOCSAR)
3. Victoria Department of Health
4. Australian Institute of Health and Welfare (AIHW)
The breach happened in June. OpenAI found it in mid-August and didn't tell Australia until Sept 10. AIHW was only told the day after independent researchers exposed it
Note on WordPress pre-auth RCE (CVE-2026-63030). There are SQLi poc's out there, but RCE PoC has not yet been exploited in the wild. Will only release our technical post if we have proof of exploitation. Our RCE payload does NOT require poorly configured MySQL.
I see many people demotivated due to AI and feels like its been a while since I ranted. Probably a mild take but here is how I stay motivated. Nothing really new just how I use what people have said to keep my motivation up. The normal 2026 disclaimer, what is in this post isn't actually 100% in line with my opinion; yes I know there are holes in my logic but some rabbit holes are best "on read".
The biggest change for me is Linus Torvalds saying something along the lines of idk why people say AI makes things, people make thing. If communication was so global in the 70's I am sure people would have said similar things during the conversion from assembly to C. Humans are creating instructions for the compiler to make a program. So why didn't we think the compiler made it? Without internet I think it would take me around 2 minutes to write hello world in C (i know embarrassingly slow but man have i gotten lazy over the years). Do it in assembly? That's probably an hour. Which is a 30x difference of time. Okay now lets say we are in the year 2010 and have Python. I timed myself and it was 3 seconds. That's a 40x time difference from my C. Why did I think I made the program and not python made it?
Unfortunately, the only thing I can come up with is how much we communicate and how quick ideas/sentiments can form. I'm sure C/Python got hate when they first came out. Hate can be a really goo fuel -- Most engineers I know have their best work come out of "hate coding" something to prove someone wrong. Only to later realize they social engineered themself into doing an amazing thing. Could be wrong here, but I think Pythons Flask is a good example of this as it started as an April fools joke. Quite literally "the most engineer thing ever" to have a funny joke spiral out of control and grow beyond their wildest dreams... Kind of like that guy that was vibe coding games last year when AI was "bad", or heck even the W̷a̷r̷e̷l̷a̷y̷ C̷L̷A̷W̷D̷I̷S̷ ̷C̷l̷a̷w̷d̷B̷o̷t̷ ̷M̷o̷l̷t̷B̷o̷t̷ ̷ err OpenClaw person. Really with all those name changes I'm shocked they landed at OpenAI instead of MSFT.
Anyway, our hate on vibe coding created the sentiment that we aren't creating things anymore (AI makes things). I don't really view it that way, AI just makes me 20-30x faster; which is similar to the jumps between Assembly -> Compiler -> Scripting. Actually now that I think about it, I remember trying to learn C many times because scripting wasn't a "real language" and it would never run a web server or it wasn't capable of editing memory (silly times indeed). AI is enabling us to develop faster and expanding the number of people that can do things, which is not new; quite literally every time we come up with a new way to interact with machines -- it does the same thing.
So yes - Anyone can make a cool demo that looks real now but they are still going to spend hours getting AI to work out all the bugs and do it better. To me they are still making something, it is other people telling them they aren't -- Funnily enough, those people trying to convince others they aren't making things, is what in return demotivates themself because it poisons their thought process when it comes to this topic.
So uh. If you look for my permission to learn something? Vibe on and let the good times roll. Just make sure you do things safely, obey terms of service, and try not to end humanity.
Oh wait. That disclaimer. Using AI in a way that causes humans to spend a lot more time than they are used to is bad mmkay? Seeing all the low effort CTF Work, blog posts, bug bounty, etc does get annoying... oh wait I have a diclaimer to the disclaimer. If you use AI to eat up time of scammers, like tricking call center scammers into chatting with robots for hours, I thank you for your token donation to helping fight that plague.
Today, HackerOne joins Project Glasswing, Anthropic's controlled-access program for Claude Mythos 5. We'll use it to harden our own security and evaluate it across the full CTEM workflow, including discovery, validation, prioritization, and remediation.
Two things up front, because researchers will ask.
Your reports are not training data. Vulnerability submissions stay where they belong: with the customer and the researcher who found them.
And AI is not replacing the bounty model. In the first 6 months of this year, researchers earned approximately $47M in bounties through HackerOne, up 25% year-on-year. More AI on offense and defense means more code shipped, more attack surface created, more reports filed, and more bounty work.
What we learn from applying Mythos to HackerOne’s internal scope will be shared with the wider community.
Read the announcement. https://t.co/KC6MNhlj8n
We’ve shipped a security-guidance plugin for Claude Code that helps identify and fix vulnerabilities as you’re writing code.
Available for all Claude Code users. Install from the plugin marketplace (/plugins).
Pakistan has so much untapped female talent in cybersecurity 🇵🇰💻
Cybersecurity needs more women, more perspectives, and more voices. The talent is already here, we just need opportunities, guidance, and community 🖤
#CyberSecurity#WomenInCyber#Pakistan#SheSecPakistan
Oxford researcher did a full deep dive on China’s “proxy station economy” for Claude/OpenAI access - https://t.co/RrzW7yxPva
The cheap pricing is basically just arbitrage.
People reverse engineered Codex into API proxies, then stacked cheaper regional subscriptions + free ChatGPT trials on top of it.
we're starting rollout of GPT-5.5-Cyber, a frontier cybersecurity model, to critical cyber defenders in the next few days.
we will work with the entire ecosystem and the government to figure out trusted access for cyber; we want to rapidly help secure companies/infrastructure.
will mythos make security researchers irrelevant?
i dont think so, assume if mythos releases tomorrow, we will be seeing bugs submitted to chromium or firefox with just bare claude code and no special prompting, similar to anthropic’s experiments on firefox, and imo this will plateau because only that far its own reasoning can go.
after that, ctfers or researchers with experience on chrome will write their own scaffolding and fuzzing setups, which will produce further results. assuming mythos is not agi, if it is, it can do this part too.
until agi, my assumption is that it’s more like fuzzers. every new model is superior and better than the one before, and better prompting and scaffolding to extract more out of it is like improving the same fuzzer with a better harness and seed
and to back this up, we know for a fact, and as per our tests, that even if you throw opus at spidermonkey and burn lots of tokens, it’s not finding any new bugs. anthropic threw one month of tokens at it, which surfaced something like 22 crashes, so it took all low hanging fruits that bare opus can find.
and we know our friends who set up fuzzing and custom scaffolding with the same opus for firefox are still popping calcs.
interestingly, we can verify this by looking at next month’s pwn2own, where the same opus is being used with better scaffolding, better prompting, and people with skin in the game for browser exploits will be popping calcs.
My take on Anthropic's new Mythos model:
Don't worry about it. It might be amazing, it might be disruptive.
But there's nothing you can do about it.
Ignore the hype, keep your head down and keep learning, growing and creating.
Adopt this: Relentless Optimism.
You can read a detailed technical report on the software vulnerabilities and exploits discovered by Claude Mythos Preview here: https://t.co/AgU6ltV2qW