DON'T scan your face for Roblox.
DON'T scan your face for Discord.
DON'T scan your face for Twitter.
DON'T scan your face for YouTube.
DON'T scan your face for Instagram.
DON'T scan your face for Reddit.
DON'T scan your face for Spotify.
DON'T scan your face for Twitch.
Good series on Pwning AI Agents
Part 1: Exploiting AI Coding Agents https://t.co/XKy0WjqHFl
Part 2: RCE and Data Exfiltration https://t.co/ineERmxlFg
Part 3: Read Only Bypass https://t.co/jLfshrnrBh
Part 4: Exploiting MCP Hosts with a Malicious MCP Server https://t.co/RD4rRjiHB0
RACE CONDITION TESTING CHECKLIST
Some bugs appear only when multiple requests hit the same operation at nearly the same time.
What to Look For:
1. Coupon redemption
2. Password-reset flows
3. OTP verification
4. Account balance operations
5. Reward/points redemption
6. Inventory purchases
7. File operations
8. Invite/referral systems
9. Vote/like counters
10. One-time actions
Safe Burp Suite Workflow:
Find State-Changing Request
↓
Create Your Own Test Account
↓
Capture Baseline Request
↓
Identify the Security-Sensitive Action
↓
Send Controlled Parallel Requests
↓
Compare Responses & Final State
↓
Check Whether a One-Time Action
Occurred More Than Once
↓
Stop After Safe Validation
↓
Document & Report
Impact Validation
Ask:
Was the action supposed to happen once?
↓
Did concurrent requests bypass that limit?
↓
Did the final application state become inconsistent?
↓
Can the behavior be reproduced safely?
↓
Is there measurable security or business impact?
Example
A test account receives one authorized coupon.
Normal:
Redeem → Success
Redeem again → Rejected
Concurrent:
Request A → Success
Request B → Success
If the application grants the same one-time benefit twice, you've demonstrated a potential race-condition/business-logic flaw.
Reporting Template
Title:
"Race condition allows <action> to occur multiple times"
Include:
- Endpoint + method
- Preconditions
- Number of controlled requests
- Timing/concurrency behavior
- Request/response evidence
- Expected vs actual result
- Final application state
- Reproduction steps
- Security/business impact
- Recommended remediation
Pro tip:
Don't confuse duplicate requests with a race condition.
The important evidence is a concurrency-dependent security boundary failure.
Only test authorized systems and use accounts/data you control.
#BugBounty #RaceCondition #WebSecurity #CyberSecurity #BurpSuite #AppSec #EthicalHacking #Pentesting #SecurityResearch #InfoSec
Confirmed: The DNS records that tell systems how to find https://t.co/qHzVq2Mr4E or https://t.co/JoIPxXI9GI got withdrawn this morning from the global routing tables. Can you imagine working at FB right now, when your email no longer works & all your internal FB-based tools fail?
ReconSpider
Advanced Open Source Intelligence (#OSINT) Framework for scanning IP Address, Emails, Websites, Organizations
13 tools in one (view pic)
https://t.co/6lAUd1IdFB
Creator @bhavsec
All researchers have heard of Google Dorks, but much less well known are the dorks for #Github, #Shodan, #DuckDuckGo, #Bing, #VirusTotal...
Here is my small collection with links to a list of dorks for various search tools.
https://t.co/wiyaQ6VXEy
#osint
🚨 It's finally here! 🚨I'm happy to announce the launch of my new academy and new course!
This course teaches you how to hack web applications, automate your exploits in Python and defend web applications against real world attacks!
https://t.co/fK7MzELUAs
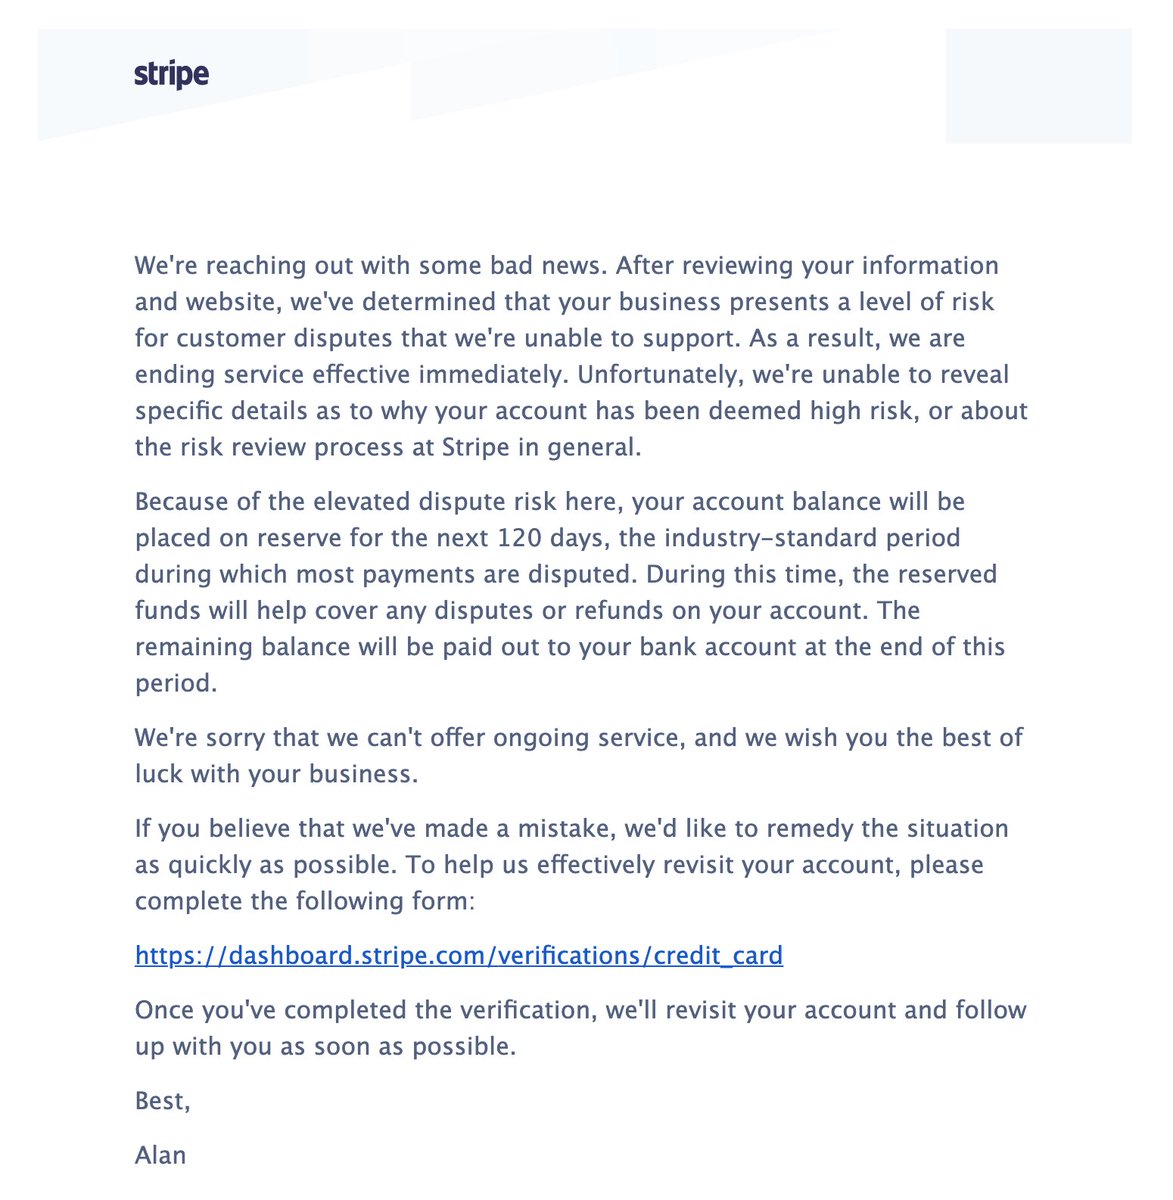
OMG! @Stripe keeps looking for reasons to block us. This time they blocked the payments because we sell TELEPHONE!! equipment, which is obviously absurd. Also they refuse to release already collected funds without providing a FULL list of our backers by email. Is this even legal?
Today @stripe blocked our account and hold all the money that we charged via @backerkit for shipping of #FlipperZero. Explaining this by the fact that we have a “risky business”. Pretty weird considering that Stripe already processed all our Kickstarter payments before.
Adversary simulation doesn’t find all high impact pain points
It usually finds exactly one—the one per stage that is needed to progress
The positive effects of red teaming
- uncovers flaws in blue team processes
- reveals some detection blind spots
- generates attention in mgmt
Dealing with the current COVID-19 crisis, most infosec men have taken it upon themselves obsess over a new pet --sourdough -- and learn all about its growth, rise, consistency, humidity, and color. I've chosen to obsess over compression algorithms -- LZMA in particular. 1/4
This is amazing, Windows Defender used the open source unrar code, but changed all the signed ints to unsigned for some reason, breaking the code. @halvarflake noticed and got it fixed. Remote SYSTEM memory corruption 😨 https://t.co/gsx9ZMk1Hz
У нас несколько поменялось отображение реестров и статистики. Также мы добавили интересные цифры по количеству внесенных в реестры запрещенных сайтов IP-адресов, принадлежащих тем или иным компаниям ->
✅ Статистика: https://t.co/L4IBu4KBSH
✅ Реестры: https://t.co/B5kqw5bTpb