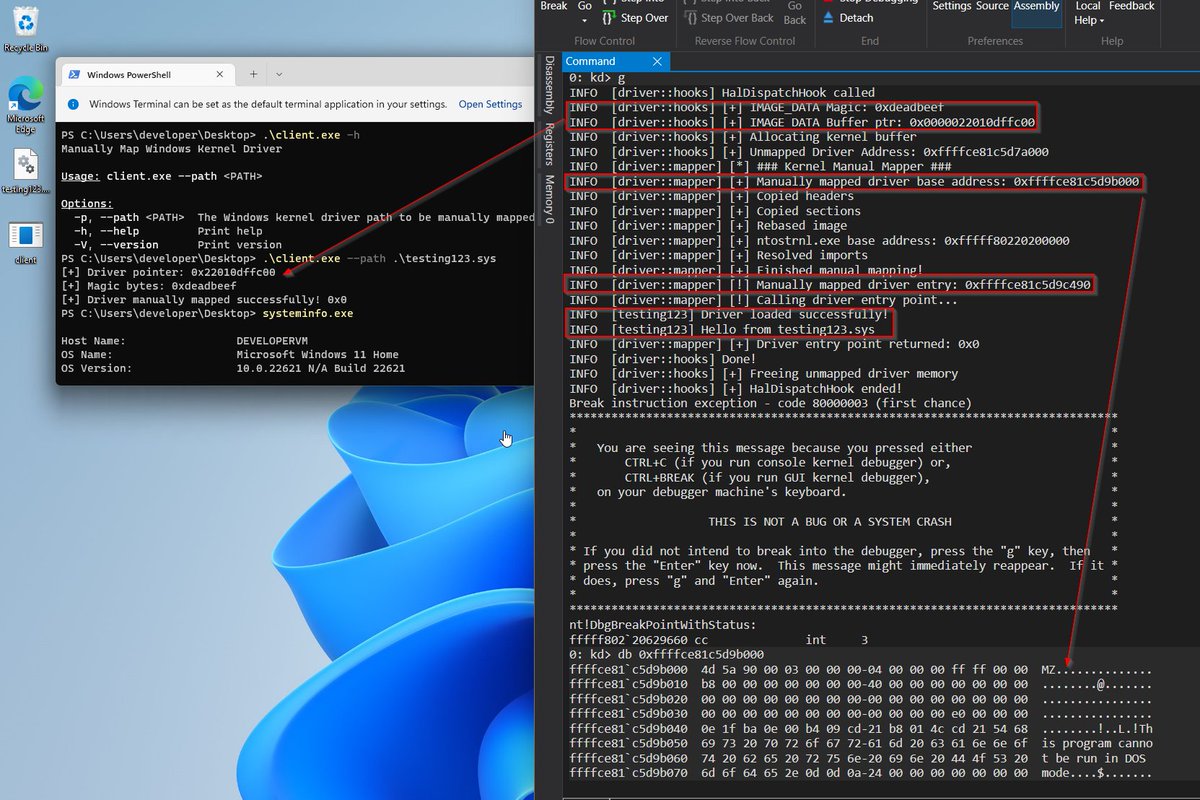
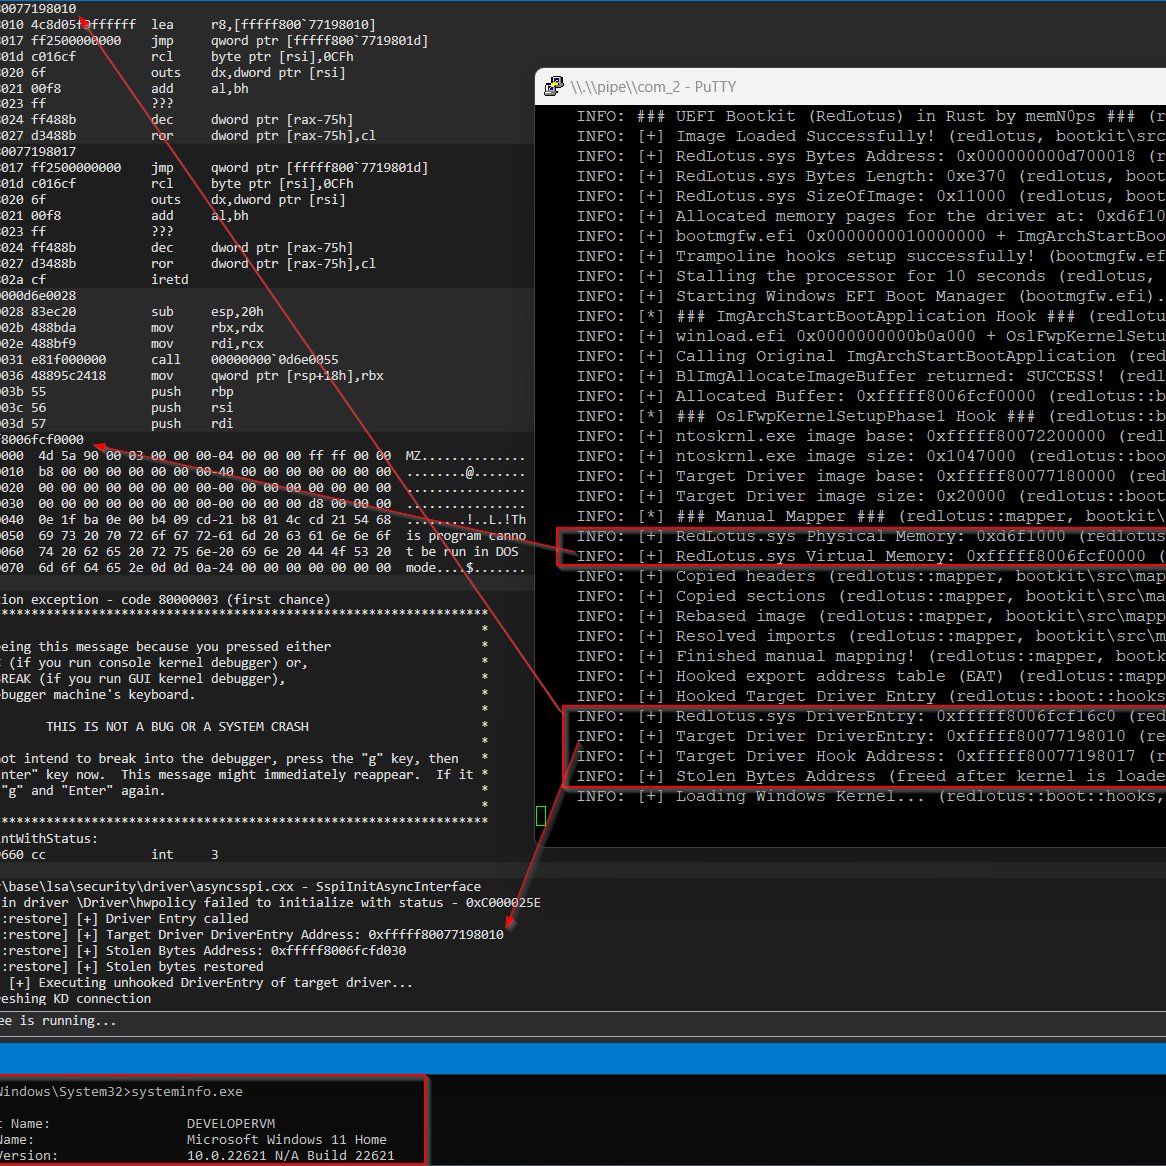
RedLotus is a Rust based Windows UEFI bootkit that executes before ntoskrnl.exe to bypass DSE and manually map unsigned kernel drivers. A research focused PoC demonstrating modern bootkit techniques and low level rust development. by MemN0ps
Blog:- https://t.co/YKY5KN6DAK
New Anthropic research: Discovering cryptographic weaknesses with Claude.
Claude Mythos Preview has helped our researchers find weaknesses in cryptographic algorithms—the mathematical methods that are used to keep data private.
Read more: https://t.co/TYKLjb3Q7V
German and U.S. authorities dismantle the Kratos phishing-as-a-service platform
Authorities in Germany and the United States disrupted the central infrastructure of Kratos, a phishing-as-a-service platform used to create credential-harvesting pages and conduct attacks globally. The suspected developer was arrested in Indonesia.
#DDW #Phishing #Kratos #DarkWeb
Initial access. Post-exploitation. Persistence.
These are the phases most of you need to simulate in your day-to-day engagements.
RustPack can help across all of them. Our latest blog post covers a range of common TTPs and shows how RustPack can help you save time, reduce effort, and streamline your operations. 🫡
https://t.co/W4uhn3mx0g
#OST #maldev #Pentest #RedTeam
Burp Intruder has 4 attack types 👇
🔶 Sniper - One payload list in one position
🔶 Battering Ram - Same payload in multiple positions
🔶 Pitchfork - Different payload sets in parallel
🔶 Clusterbomb - All combinations of multiple payload sets
Try it out 🧪
❗️❗️Threat actors are actively exploiting a critical authentication bypass flaw in Palo Alto Networks firewalls to breach corporate networks and deploy Qilin ransomware.
Full Story: https://t.co/MRbgjeWpst
The flaw, tracked as CVE-2026-0257 (CVSS 7.8), affects the GlobalProtect portal and gateway in PAN-OS. It becomes exploitable when authentication override cookies are enabled alongside specific certificate configurations, allowing unauthenticated attackers to bypass login controls entirely and establish legitimate-looking VPN sessions.
#cybersecuritynews
🚨 Threat Actor Offers Fraudulent Emergency Data Requests for Major Platforms
A threat actor is advertising what they claim are "emergency data requests" (EDRs) for several major technology platforms on a cybercrime forum.
According to the listing, the service allegedly covers:
* Meta (Facebook & Instagram)
* X (formerly Twitter)
* Telegram
* T-Mobile
The seller claims to provide emergency data requests for $300 per request, accepts cryptocurrency payments (preferably Monero), and advertises that "proof" can be provided to prospective buyers.
Emergency Data Requests (EDRs) are legitimate legal mechanisms used by authorized law enforcement agencies to obtain user information in situations involving imminent threats to life or serious physical harm. Cybercriminals have increasingly attempted to abuse or fraudulently obtain these requests through social engineering, compromised government accounts, or forged legal documentation.
Daily Dark Web cannot verify the authenticity of the seller's claims or whether they possess the advertised capability.
Analyst Note: The emergence of EDR-related services on cybercrime forums highlights continued attempts by threat actors to exploit trusted legal disclosure processes. Organizations should ensure robust verification procedures for emergency requests, enforce strong identity validation for government portals, and monitor for signs of unauthorized access to law enforcement or government accounts.
#DDW #Intelligence #DarkWeb #Cybercrime
Updated our inference fuzzing write-up - now with the vuln specifics we held back. Full detail on a pre-auth path traversal in OpenWRT (LuCI bmx7) that reads any file as root. Notified 8 July, no reply. https://t.co/Oxuk6eevC3
Discover how to create a highly efficient ESP32-C3 ad blocker for just $5. This miniature device seamlessly blocks over 537,000 domains on your network.
#ESP32C3#AdBlocker#DNSFilter#Cybersecurity#DIY
https://t.co/dD45XoWG3L
🚨 RaidForums [.]su domain was suspended.
New domain: [.]ru
They also have a new site called RaidBin, which is a paste-sharing platform.
raidbin[.]org
Dark Web: http://raidbinahr33urj6dcnuphimsnnxkvryvomimphp5wsfa5x3gkm2jsqd[.]onion
Microsoft researchers have observed increased ACR Stealer activity across customer environments. These campaigns are using ClickFix lures to steal browser credentials, authentication tokens, and sensitive documents from enterprise environments. https://t.co/kVF65gdubY
We desperately need someone to update noob malware literature.
The shit for malware noobs looks like it was written in 1995 and by someone who doesn't know shit about malware or how it actually works.
It reads like someone describing swimming who hasn't ever been in a pool
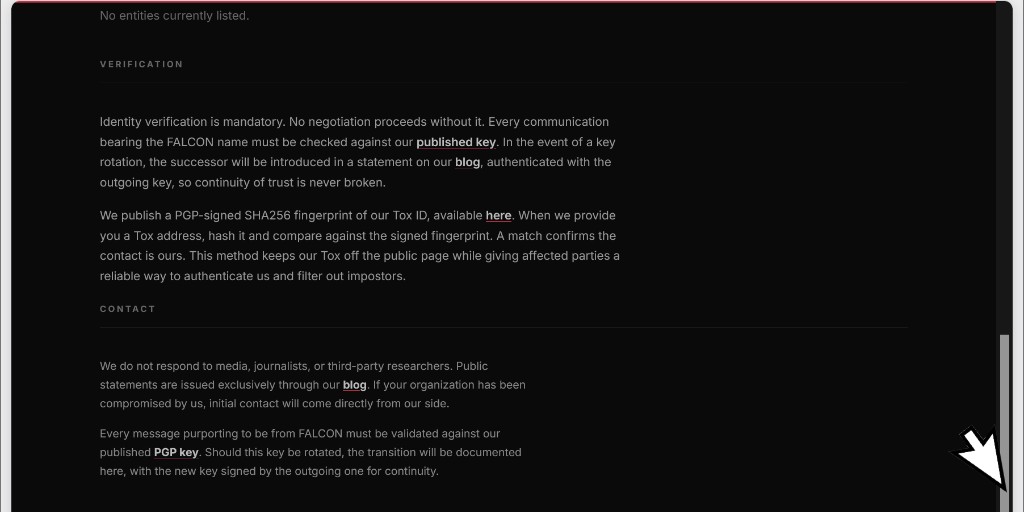
We recently investigated cases involving a vishing playbook and passkey-themed domains from an extortion group calling itself FALCON. We track this activity as CL-CRI-1182 and assess with moderate confidence that this is related to CL-CRI-1116 (BlackFile) https://t.co/eanCXvTgpe