my $10/month hackbot found a privilege escalation vuln in @omarchy in its first hour.
setup:
1. run hermes agent on a device that stays on 24/7
2. get a $10 opencode subscription
3. set model to deepseek v4.1 flash
4. paste the prompt (in replies)
it runs 4 bots:
→ scout: picks the hackerone program most likely to pay out
→ researcher: finds vulns, builds PoCs, saves evidence
→ reviewer: tries to reproduce and disprove every finding
→ submitter: writes the report and uploads evidence, checks with you before submitting
it texts me when it finds something 👇
Easily run an offensive security / pentesting LLM locally:
1. Download @lmstudio
2. Pick one of the @WhiteRabbitNeos models (I tried WhiteRabbitNeo-13B-GGUF but there are others eg distilled into Qwen)
3. no crime? unless?
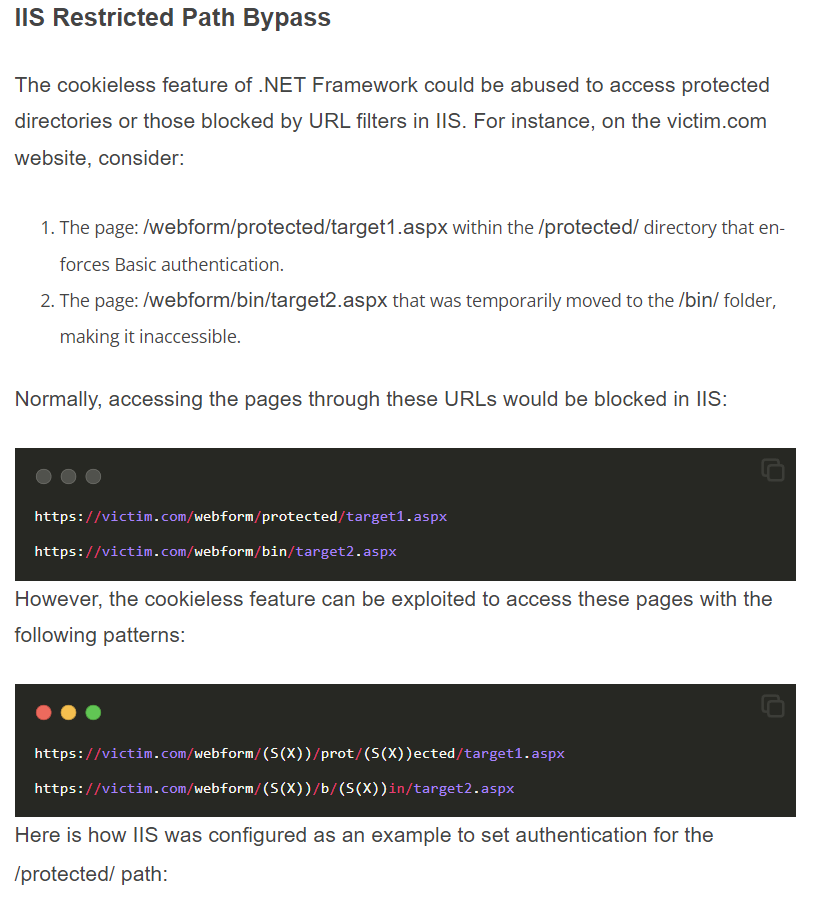
🍪 Cookieless DuoDrop: IIS Auth Bypass & App Pool Privesc in https://t.co/Ahs7bnPTMM Framework (CVE-2023-36899)
https://t.co/CUicDGrjvE
Interesting vulnerabilities found by @irsdl#infosec#bugbounty#bugbountytips#cybersecurity
I just updated leaky-path: https://t.co/6vhUjXMOfV
You're leaving a lot on the table if this wordlist isn't already part of your automation – it's what I use to keep 100s of applications tidy and clean across various tech stacks.
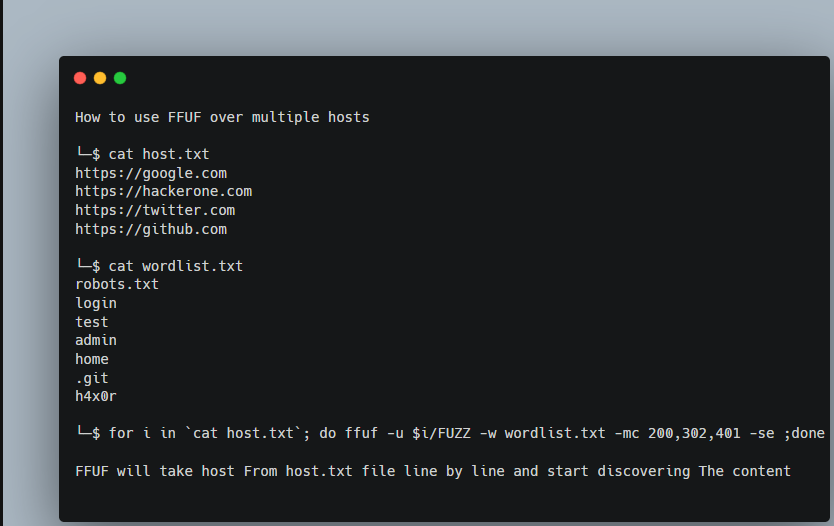
How to use FFUF over multiple hosts
$ for i in `cat host.txt`; do ffuf -u $i/FUZZ -w wordlist.txt -mc 200,302,401 -se ;done
#bugbountytips#BugBounty#ffuf