Ethereum can meet bank requirements with two things in place: control over what they send, and confidentiality over what others see.
On Nov 18 in Singapore, we’re working through both with @eth_systems and a group of banks in a closed session.
https://t.co/tpPgdkGjzS
Large scale private llms are incentivized to provide the lowest quality compute at the highest cost to users.
Since we don’t have a general standard of measurement they can degrade the quality of intelligence without any clear indicators other than frustration at the output.
Additionally, as they struggle to find product market fit, they are deeply incentivized to aggressively copy/steal any ideas that their models encounter.
As a result, they are an extreme counter party risk.
@APompliano@cfosilvia Anthropic is such a big counter party risk.
Their commitment to their investors means they will, through whatever means possible, make a profit.
They already train off whatever data they want with complete disregard to data ownership.
‼️ BREAKING: OpenSSH has rushed out a fix for a critical flaw that lets attackers log into some Linux servers without the right password.
The team learned of the bug a day earlier. OpenSSH's Damien Miller says long embargoes now mostly help attackers, because AI agents rediscover bugs, sometimes within hours.
It hits Linux systems on the musl C library with PAM off, such as Alpine Linux. Miller told admins to disable password logins or SSH itself "IMMEDIATELY".
Version 10.6p2 works around it. Systems on glibc or PAM are not affected, and Miller says the root cause sits outside OpenSSH.
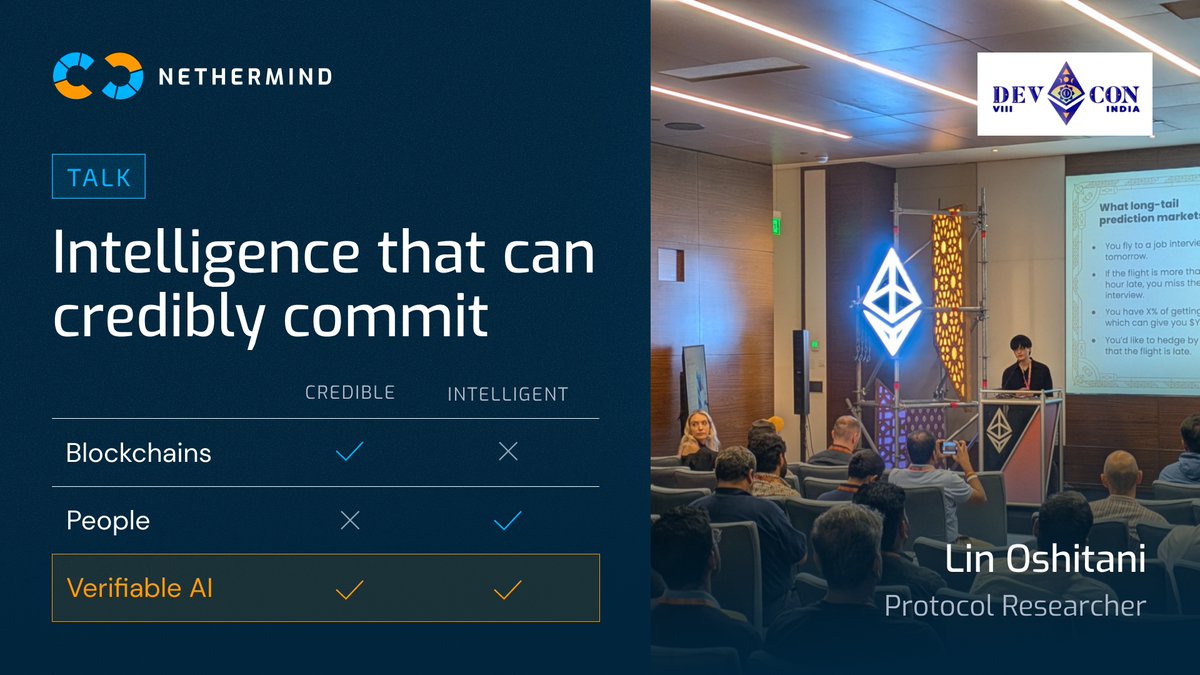
Blockchains are credible but not intelligent. Humans are intelligent but not credible.
At Devcon, our researcher @linoscope showed a way to get both. He built a prototype oracle that runs an LLM inside a TEE: the model answers the question, and the contract checks the TEE’s proof before it accepts the answer.
Most smart contracts today act on numbers a data feed can report, like prices. An oracle like this could let them act on any question you can phrase, like whether a flight left on time or a GitHub PR meets a bounty’s conditions.
https://t.co/AuDS7z9dEW
@dcbuilder Hmm, I would say philosophy(socratic method), meditation, and journaling/self analysis.
As I understand it, cognitive security is a capacity of awareness, perceptions and beliefs, and your ability to navigate them.
Spotting your perceptual biases are hard WITHOUT ai.
0x is moving its Ethereum traffic to Nethermind.
On @0xProject’s Swap API workload, Nethermind now runs with 20–30% lower latency than their current client.
Thanks to the 0x engineers who worked with us to make this happen.