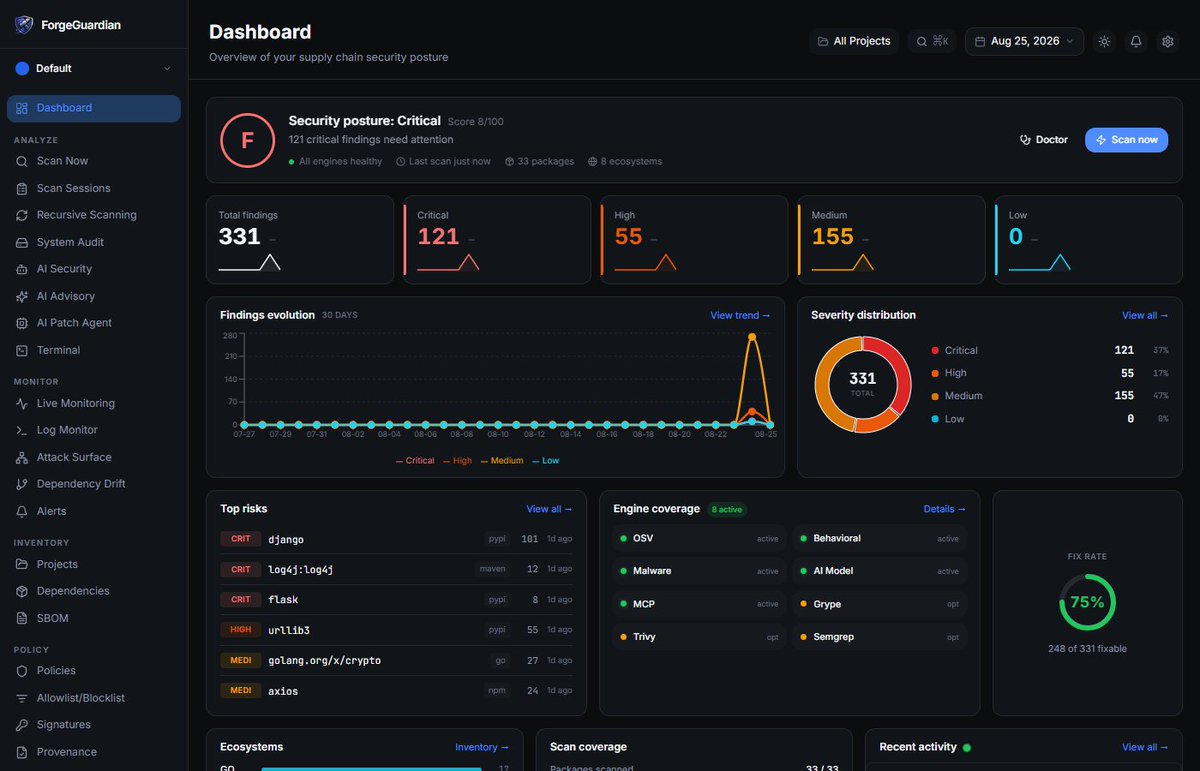
Me and my friend @jaimin2709 started #ForgeGuardian as a weekend experiment around one question:
Can we build a practical, open-source defense layer for software supply-chain attacks?
3 months later, we're putting it out in the open. 🚀
🔎 8 detection engines
🌍 9 ecosystems
🛡️ 223+ detection signatures
💻 CLI + Dashboard
🔒 Offline-first
New threat → New detection → Shared with the community.
Try it. Break it. Tell us what we’re missing.
👉 GitHub: https://t.co/HgF5po2ge9
📚 Docs: https://t.co/hMf3vX0kM4
#CyberSecurity #SupplyChainSecurity #AppSec #OpenSource #infosec #supplychain #devops #secdevops #dev
Hi followers!
We have 5 Delegate Passes to give away. Please requote or tag us, and share your best bug bounty or CVE discovery, along with the write-ups.
We will select the top entries in 2 weeks' time.
This will also be shared on our LinkedIn.
Only for 5 followers combined!
🐛Bug Bounty Tips: Using "Waymore" to discover more security Issues🌐
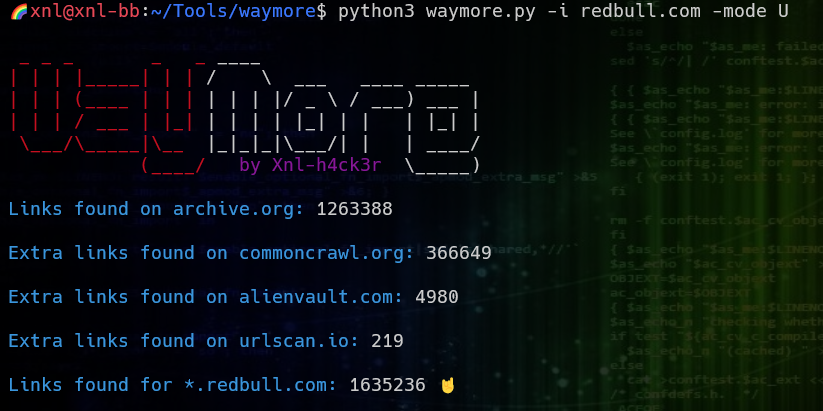
In the bug bounty world, having the right tools is essential. While there are many useful ones like waybackurls and gau, let's focus on "waymore" from @xnl_h4ck3r today. It's a handy tool for finding archived URLs, and it can give you an advantage when hunting for bugs.
🕵️♂️ Why "waymore"? It's my favorite tool for deep investigations. Whether I'm exploring a specific target or a new area, "waymore" helps me collect ALL the archived URLs I need.
Here's where "waymore" gets its data:
📜 Wayback Machine (https://t.co/gAWRY0MUeD): It stores old versions of websites, which can be a goldmine.
🌐 Common Crawl (https://t.co/nZLLYOdzJr): This resource has a massive amount of web data.
🛸 Alien Vault OTX (https://t.co/QrvZM2ns9A): It offers threat intelligence, including valuable URL data.
🔎 URLScan (https://t.co/Uyq55teG9R): This service scans and analyzes websites, giving you crucial insights.
Now, let's dive into using "waymore":
Installation is straightforward:
git clone https://github[.]com/xnl-h4ck3r/waymore.git
cd waymore
sudo python https://t.co/t3WrbvoEzi install
sudo pip3 install -r requirements.txt
Once it's set up, you can run "waymore" on your target like this:
python3 https://t.co/28vL8nki98 -i target[.]com -mode U
If you want to go deeper, use -mode R to download all archived responses. This sets the stage for local analysis, where you might uncover hidden treasures like passwords or forgotten APIs. 💎
But what's next in your bug bounty journey? 🤔
1️⃣ One-Liner Magic: Check out this list of one-liners at https://t.co/QNkVnXD86A. You can apply these to your "waymore" dataset. With a bit of automation, you'll be surprised by the results! 🚀
2️⃣ Testing Tools: Use tools like dalfox, try out nuclei templates, and other XSS detection methods to find vulnerabilities like XSS, SQLI, SSTI, and more.
3️⃣ Custom Searches: Create your checklist for specific keywords like "user," "admin," "orderId=," "id=," "login," "signup," and others. Tailor your searches to what matters most.
4️⃣ Dive into JS: Look at .JS (JavaScript) files, find API endpoints, and test them for issues like IDORs, information leaks, or hardcoded credentials. The details matter.
And if you haven't found any bugs yet? 🤷♂️ Don't worry; there are many creative paths to explore within this dataset. Stay tuned for more insights!
Key Takeaways: Gathering URLs is your secret weapon in bug bounty hunting. Always include testing archived URLs in your research and testing methods – you'll be amazed at what you discover. 🚀 #BugBounty #InfoSec #Cybersecurity #HackerOne #BugCrowd #BugBountyTips
🧨 RCE in ManageEngine
Remote Code Execution Vulnerability in ManageEngine products (CVE-2022-47966) due to the use of an outdated version of Apache Santuario.
Dork for Shodan:
title:"ManageEngine"
Link to template for Nuclei ( https://t.co/frUopqbbbq )
#rce#cve#BugBounty
Latest version of nuclei supports automated tagging to Nuclei CVE Templates that exist in @CISAgov's list of known exploited vulnerabilities.
GitHub Release: https://t.co/SHIDXLe2y9
CISA KEV: https://t.co/iW3eraGhe6
#hackwithautomation#kev#cve#security
Here are 6 of my favourite sources of recon data:
👇
- https://t.co/92fxJ8JNtJ
- https://t.co/jT4IR0HW4U
- https://t.co/RD2sad56Pq
- https://t.co/XMpWGH4bNf
- https://t.co/GhKbZpvUK3
- https://t.co/LxtY7ee0rf
- https://t.co/V5O0NonxBj
They're like search engines for hackers!
I'm really humbled to see 450+ people to show up to today's stream with @zseano!
As promised, Sean is giving away 3 @BugBountyHunt3r subscriptions! All you have to do is RT and follow @zseano and @BugBountyHunt3r to enter!
See you all at #NahamCon2021 :)
CVE-2021-3110 The store system in PrestaShop 1.7.7.0 allows time-based boolean SQL injection via the module=productcomments controller=CommentGrade id_products[] parameter. https://t.co/iN4IcByabB
CVE-2021-3110
The store system in PrestaShop 1.7.7.0 allows time-based boolean SQL injection via the module=productcomments controller=CommentGrade id_prod...
https://t.co/n8EKzbxC3j
Get alerted before hackers: https://t.co/xRmEKSqAVx
🚨 NEW: CVE-2021-3110 🚨 The store system in PrestaShop 1.7.7.0 allows time-based boolean SQL injection via the module=productcomments controller=CommentGrade id_products[] parameter. Severity: CRITICAL https://t.co/FBkNzrYkeb