This is quite insightful. The future is clearly what @fransrosen described as humans+AI hacking in the same loop where AI brings the grind 24x7 and hackers bring the judgement - where to look, what to test, etc.
HackerNotes TLDR for episode 195! https://t.co/PHWcx6HLGT
►⠀Discussing with a OG hacker @fransrosen about the new AI era in the Bug Bounty scene
⠀•⠀AI is just the scanner era again. Everyone runs the same tools the same way, so the first step gets duped and your whole chain dies with it
⠀•⠀You are still the edge. The prompt is the new scan config, and threat modeling is different for every company. Plant a seed nobody else has
⠀•⠀AI is great at fingerprinting and parser bugs, but still weak at race conditions, blind XSS, and SSRF when it has no context
⠀•⠀Programs should pay for impact bumping, not just first report. Turning a known low into a critical is real work that goes unpaid today
We’re disclosing HEIF Heist, a months-long investigation into libheif that allowed us to hack OpenAI, Slack, Meta, GitHub Ent, Rails, Next.js, ImageMagick, and many more.
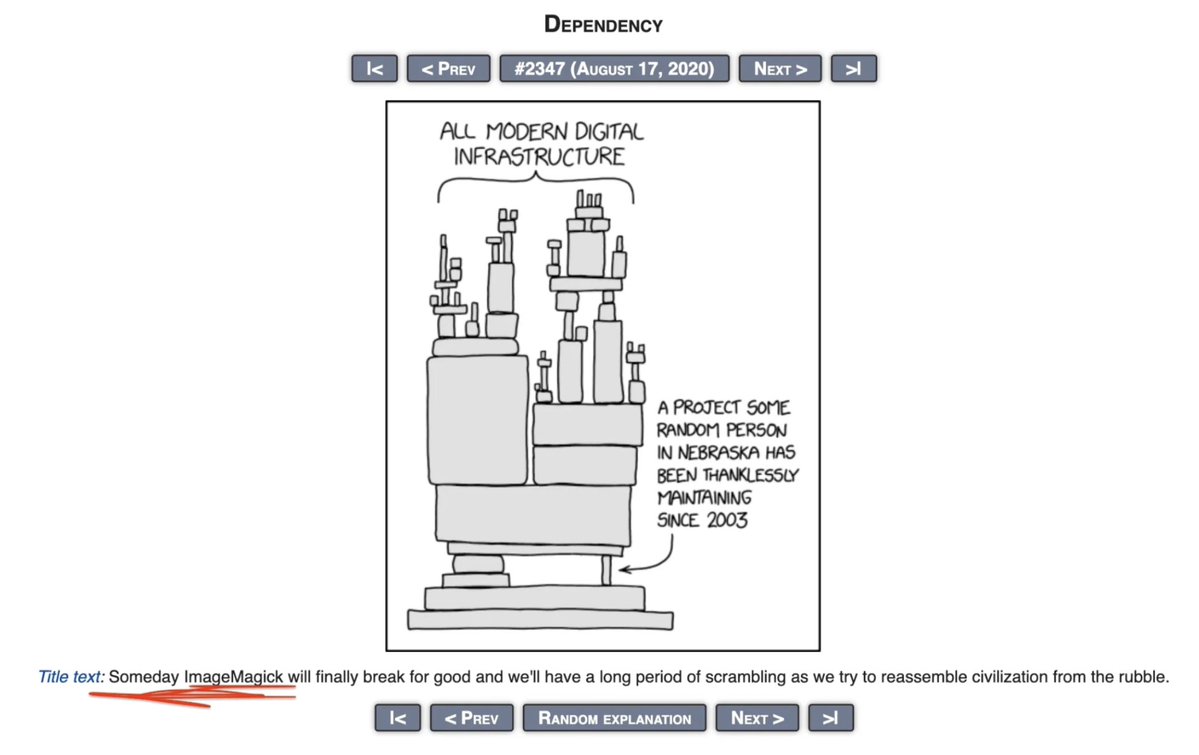
It was literally xkcd #234, one obscure image library beneath a huge number of apps. 🧵
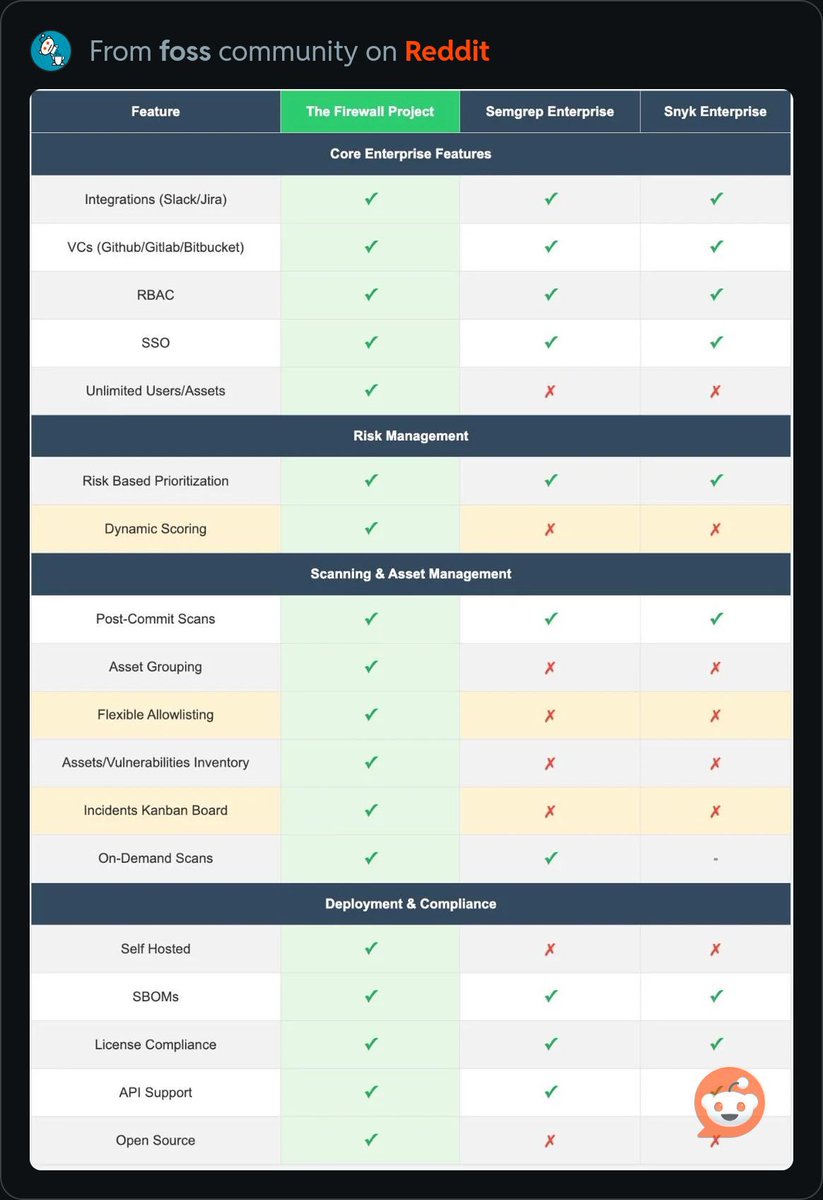
The Firewall Project platform is now FREE on the AWS Marketplace, offering incredibly convenient integration with your AWS environment. Our mission is to make AppSec setup and use straightforward for everyone. Get protected effortlessly!
https://t.co/XBviCeKAHy
#appsec#foss
Join our brand new Discord server and become part of a vibrant community.
Come hang out, ask questions, contribute, and help us build The Firewall Project together. See you there!
🔗 Join The Firewall Project Discord: https://t.co/qI5QdVqdVb
#AppSec#OpenSource#CyberSecurity
Can open source replace a billion dollar company? We tried.
Cyberattacks and data breaches are a common occurrence these days. Many businesses struggle to prioritize cybersecurity due to limited resources and budgets.
We think every business, no matter how big or small, should have access to top-notch security that's also easy to use and doesn't break the bank. Our big idea is simple: to create powerful, enterprise-grade security tools that anyone can easily get started with and understand.
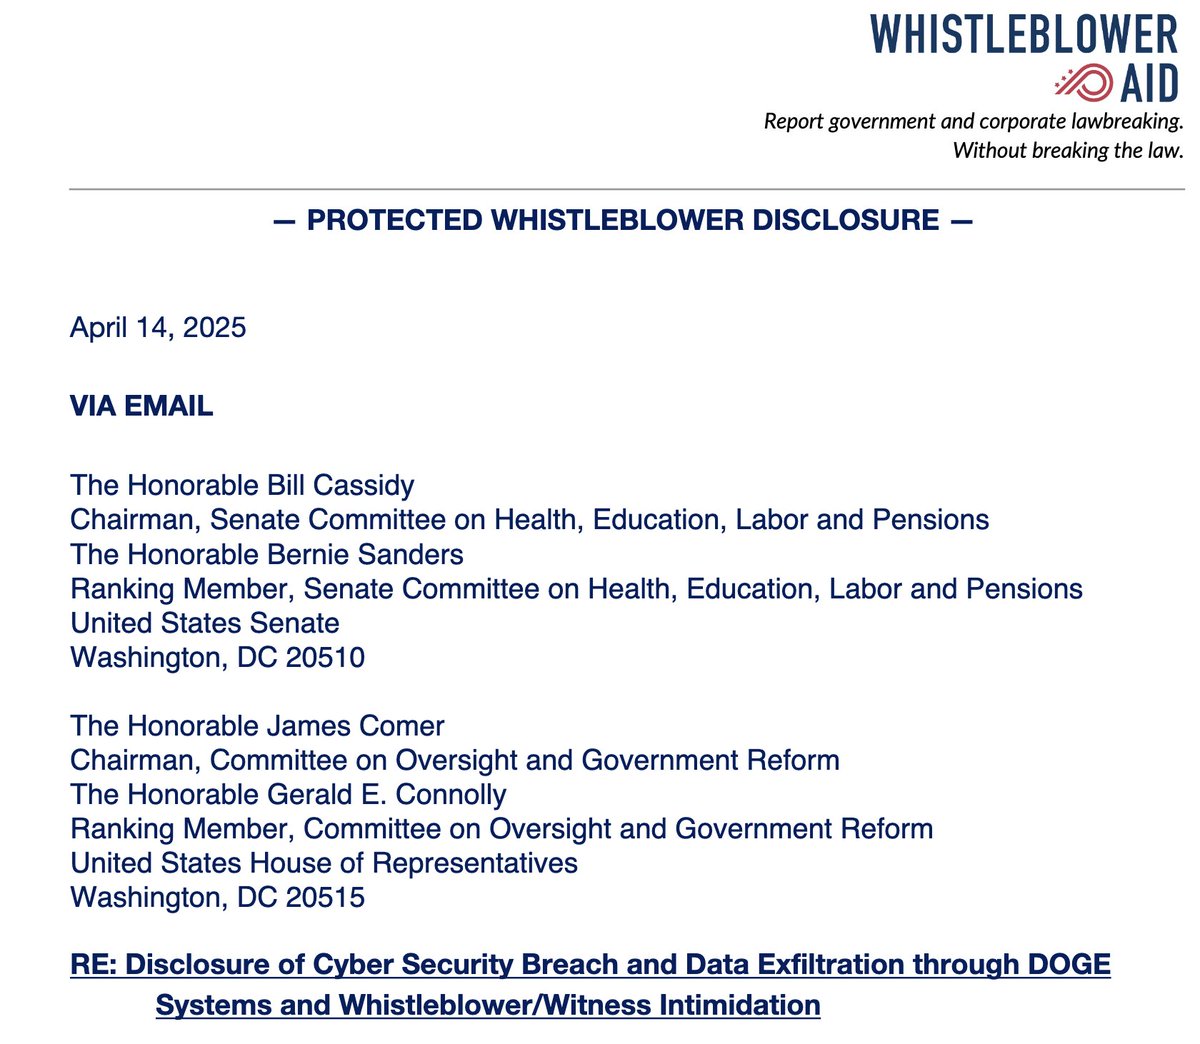
🧵 THREAD: A federal whistleblower just dropped one of the most disturbing cybersecurity disclosures I’ve ever read.
He's saying DOGE came in, data went out, and Russians started attempting logins with new valid DOGE passwords
Media's coverage wasn't detailed enough so I dug into his testimony:
We're live on Product Hunt! 🎉 We'd love your support for The Firewall, our free and community-powered application security platform. Please check it out and give us an upvote! 👇
https://t.co/6jenOyDYXH
#ProductHunt#AppSec#cybersecurity#devsecops
We're stoked to be crashing @bsidesahmedabad today!
Spot us rocking our tees with the coolest quote:
"Open source, open minds, secure future"
No fancy booth, just us soaking up knowledge and vibing with fellow security enthusiasts.
@deedydas Here are some details and history of this threat actor. Also we should not ignore the critical evidence mentioned in the report i.e. the credentials shared by the CISO in the email were available on dark web since 2023.
the reality is that the threat actor had faked the email screenshot. The username and password allegedly shared by the CISO were actually part of a credential leak from a public darkweb incident. The threat actor fabricated the story to frame the CISO to defame him.
@deedydas the reality is that the threat actor had faked the email screenshot. The username and password allegedly shared by the CISO were actually part of a credential leak from a public darkweb incident. The threat actor fabricated the story to frame the CISO to defame him.
@ActusDei@Shiprasorout We have identified active exploitation of this feature by some cyber criminals. Once they are successful in tricking victims into installing their malware and they have a remote access to victim’s device, they go into apps like zomato and purchase gift cards without cvv
If you are wondering why your UPI is not working or you faced issue while sending money through using IMPS, Aeps, NETC etc its because an organisation called CEDGE was ransomed on 27th July
Read the complete blog by @cloudsek
for complete info
Link - https://t.co/xWePgBVu0D
@coffinxp7 @Hacker0x01@ICICIBank@ICICIBank_Care This malware can steal sensitive information like credit card details, credentials, and even intercept SMS messages.
I've encountered similar misconfigurations in other fraudulent apps, and I can share some additional open Firebase instances if that would be helpful.
@coffinxp7 @Hacker0x01@ICICIBank@ICICIBank_Care There's a strong possibility this app isn't a legitimate banking application. It could be linked to a reward app scam. These scams often involve distributing malware disguised as real banking apps.