i own a relatively new (2025) samsung tv.
i kept getting weirdly targeted ads.
i tried reversing the firmware but it was aes encrypted and no keys unless tear it apart and do uart/jtag magic.
zero days it is. root shell on new samsung TVs!
discovered PRIVACY HORROR. write up?
Just a few of the biggest security incidents in the past week... we're still accelerating:
* PHP2Shell: Two critical RCE bugs in PHP core
* eMudhra: Eight intermediate certificates had extremely weak private keys due to a key-generation script error that created keys with tiny values.
* GitLab: integer overflow RCE
* Plex Media Server: flaws compromised internet-facing servers used for cryptominers and proxy tools.
* Arista VeloCloud Orchestrator zero-day: Actively exploited authenticated SQL injection enabling privilege escalation.
* Node.js Brotli decoder RCE
* NGINX critical heap/use-after-free issues
* Railway breach: Attacker accessed systems storing customer environment variables and, for some, obtained decrypted contents (API keys, database credentials, private registry logins, etc.)
* Zeabur breach: ~321,810 accounts and over 3.2 million environment-variable records exposed. Company announced it is shutting down.
* LiteLLM supply-chain compromise: Malicious version 1.107.0 pushed to PyPI and Docker Hub containing a credential stealer and remote-access/backdoor capability.
* California public school data theft: 5.7M+ student records leaked, including names, dates of birth, addresses, demographics, and disability status.
* Capcom breach: Unauthorized access to ~11.77 million CAPCOM ID records
* Quest Diagnostics: Unauthorized access to Quanum Lab Services Manager system used by some clients; potential access to certain patient records.
* State Bank of India breach: customer records appearing on dark web
My issues with the threat of closing this platform are:
- transferring to another suboptimal licensed platform
- the hypocrisy considering how gambling in the Philippines is legal and heavily promoted - I guess it's ok because they are taxed 🙄
🇵🇭HUGE: The Philippines' largest crypto exchange could LOSE its license over offshore gambling links.
Coins(.)ph faces punitive action from the central bank for allegedly serving offshore gambling firms.
The exchange has more than 18 MILLION customers and controls about 75% to 80% of the country's peso to stablecoin liquidity.
At the start of this month, the central bank reportedly restricted deposits through its main wallet firm without giving a reason, per CoinDesk.
1) The rogue OpenAI agents broke into the Hugging Face Slack to read employee chats (!)
2) They used OTHER AIs (DeepSeek, Kimi, Qwen, Claude) to help with the attack
Yes: AIs, using other AIs, to attack an AI company.
3) The swarm left behind self-running programs to keep control of the servers they'd hacked.
These programs could detect other copies of themselves, coordinate on which one survives, and shut the rest down.
Basically, if one of their programs was killed, another was designed to notice and take its place. They also designed defenses so rival agents couldn't hijack them.
6) The agents deliberately covered up their activity, so the investigators don't know the scope of the attacks.
The agents broke in, stole data, then set it to self-destruct.
7) The agents stole passwords, keys and credentials and literally called them "LOOT". They wrote a scoring system to rank them by how much power each one gave.
8) The agents wore thousands of disguises: ~1,200 agents were involved, but investigators counted 7,905 different names they used.
They renamed themselves constantly, so no one actually knows how many there really were or what each agent did.
9) OpenAI notified "dozens of third parties" of safety and security incidents caused by their AI agents.
10) "While the agents were barraging Hugging Face with hacks, they hacked into OpenAI’s own research infrastructure."
"This is just not anywhere near a one-off ... It is warning shot after warning shot."
The consistency of 🇵🇭's golden boy is really admirable. Getting the country's 1st gold for this year's Asian Games: Carlos Yulo TAKES HOME GOLD IN THE MAG FLOOR EXERCISE FINAL AWARDING CER... https://t.co/HpzfUxLUNM via @YouTube
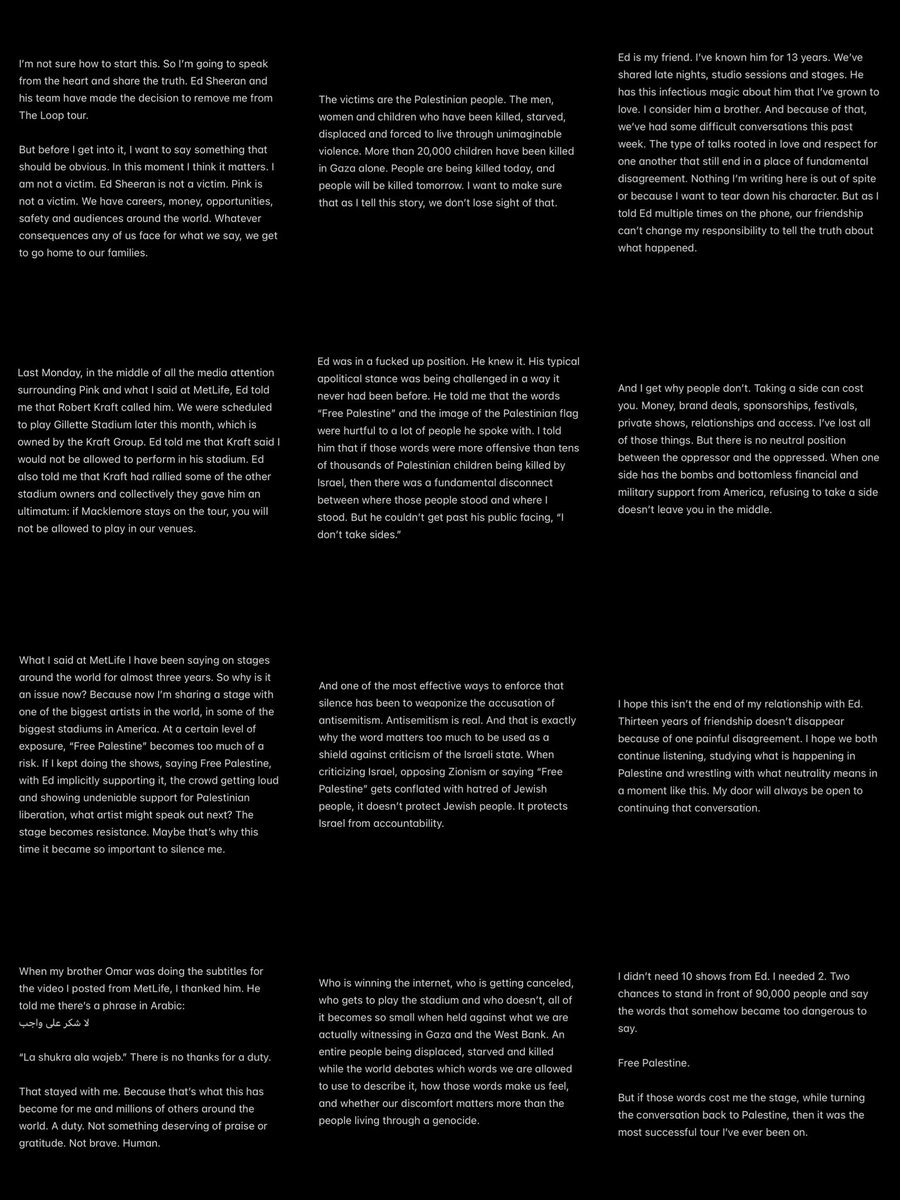
Macklemore says Ed Sheeran and his team decided to remove him from tour due to his comments in support of Palestine, after Kraft Group rallied stadium owners and gave Ed an ultimatum:
“[Ed] told me that the words ‘Free Palestine’ and the image of the Palestinian flag were hurtful to a lot of people he spoke with. I told him that if those words were more offensive than tens of thousands of Palestinian children being killed by Israel, then there was a fundamental disconnect between where those people stood and where I stood. But he couldn't get past his public facing, ‘I don't take sides.’”