In Open-Source, I HATE users who threat to use another product, only to push his/her own interest/issue.
I DO NOT CARE WHEN YOU NO LONGER USE THIS/MY PROJECT.
@awesomekling Following the LibWeb practice of putting spec urls and content inline with code, I started putting docs urls and snippets on the various methods and lines of code while implementing third party integrations in my projects. The difference it makes is enormous.
@DocSparse@github This is complete disrespect for the to the open source community. Definitely NOT OK.
Furthermore, how would you ever trust Copilot to such complex code?
If it is good, it is a plain copy without attributions. If the copy is imperfect, it will have random bugs.
#ITSicherheit wird in kommunalen Verwaltungen zu oft als Kostenfaktor gesehen. Das habe ich im Interview mit @Vitako_eV bemängelt. Hinweise und Warnungen von IT-Sicherheitsbeauftragten – so es sie überhaupt gibt – werden oft ignoriert. (1/2)
Just this whole month of August, we answered to almost 300 tweets, and more than 70% of them were done by contributors. Thank you @jens1o, @vintagemind07, @hellosct1, @fipekoji, @halcance, and many others who we don't mention here for your contribution.
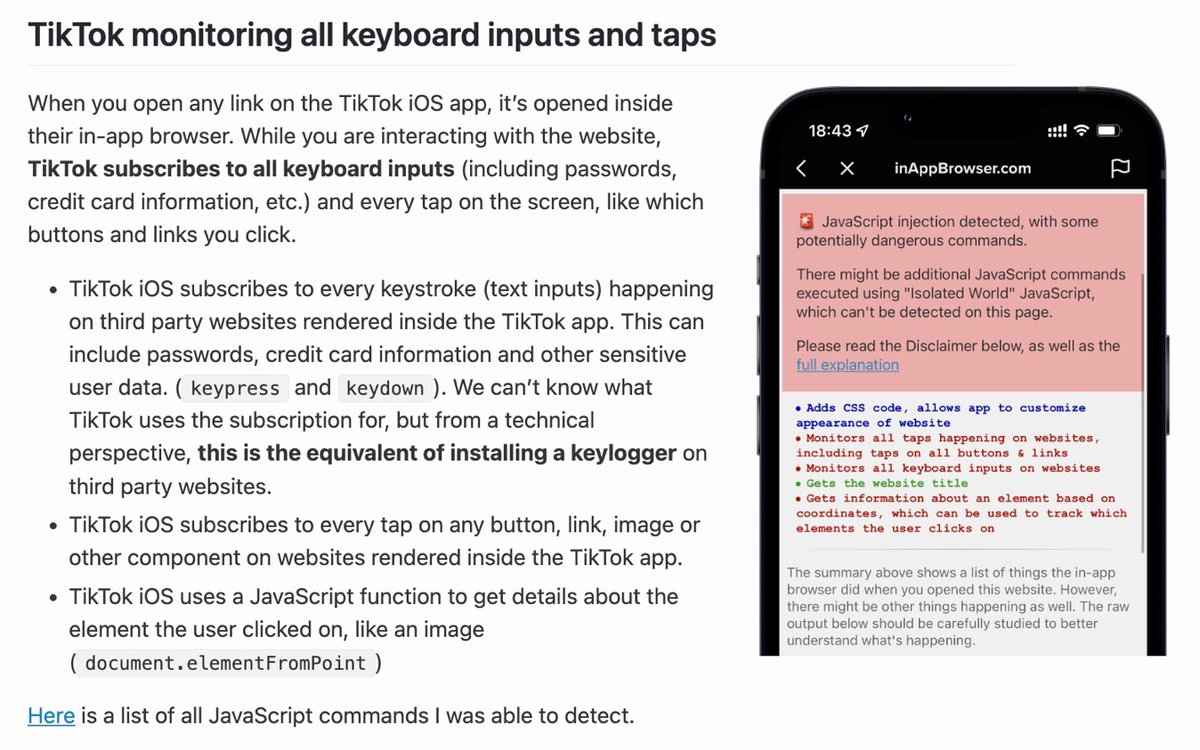
🔥 New Post: Announcing InAppBrowser - see what JavaScript commands get injected through an in-app browser
👀 TikTok, when opening any website in their app, injects tracking code that can monitor all keystrokes, including passwords, and all taps.
https://t.co/TxN1ezZX71
When opening a website from within the TikTok iOS app, they inject code that can observe every keyboard input (which may include credit card details, passwords or other sensitive information)
TikTok also has code to observe all taps, like clicking on any buttons or links.