Vi har opdateret vores vejledning "Sikker brug af Transport Layer Security (TLS)". Vejledningen indeholder en række anbefalinger til, hvordan man sikre data og informationer i transit over åbne netværk gennem brug af krypteringsteknologi.
Læs den her: https://t.co/9FKbRG0Pv5
🚨 Today, we are publishing our Cybersecurity Performance Goals which list high-priority cybersecurity outcomes and associated actions intended to help CI organizations voluntarily reduce risk from malicious cyber activity: https://t.co/hYjIAe7YRE
Let’s say you need to download all the devices in your tenant and you have over 1 million devices.
At first you try running this command and you increase the page size to 999 instead of the default 100 to make it go faster.
It runs for a long time but errors out midway ☹️
1/2
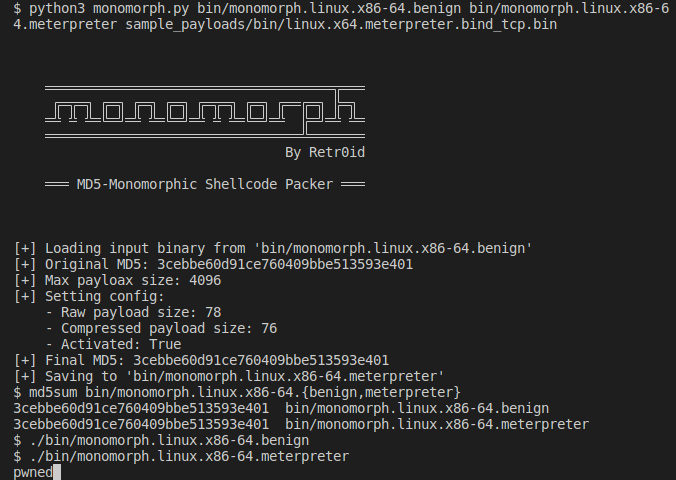
Couple disturbing trends in recent ransomware attacks:
- one operator used DA creds to reset all AD user passwords (like LockerGoga did)
https://t.co/WZFojwEUW3
- Exmatter's rapid data theft and data destruction functionality (h/t @InsideStairwell)
https://t.co/p2pTJJ2cnc
#DFIR
A good reminder that if you allow users to access #Microsoft365/#AzureAD from un-managed devices, there is nothing under your control that can protect their identities. This includes MFA and FIDO2.
this morning FIDO published a white paper that lays out what it thinks are the final elements needed to permanently move away from passwords https://t.co/ySmmth7Jqa
A friend asked me recently why I push FIDO security keys so hard. Should orgs really delay other important work to get FIDO keys rolled out to their staff? Yes!
A thread… 🧵
The Conti ransomware leaks have unveiled Conti's primary Bitcoin address.
From April 21st, 2017 - February 28th, 2022 Conti has received 65,498.197 BTC
That is 2,707,466,220.29 USD.
2) (SHORTLY) We're publishing a free, public, unauthenticated, self-updating feed of all IPs that are exclusively targeting devices geographically located in Ukraine's IP space with scans, exploits, etc. I will post the link to this as soon as it has been pushed to production.
Due to the continued escalation of the crisis in Ukraine and to help the broadest possible community go #ShieldsUp, KSG will make some of our client advisories public. Clients and colleagues who want full access can contact [email protected].
https://t.co/XhGouecLqS
Well this is amazing.
@CISecurity and @NISTcyber just pump out such amazing documentation.
Combine it with some of the stuff Compliance Forge sells and you can have close to an entire GRC program stood up in under a year.