Most BD outreach fails for one reason:
It’s all about them.
The best deals I’ve closed started differently
I led with value and actually listened.
No pitch. No pressure. Just real conversations.
What’s the biggest mistake you see in BD outreach?
What if moving money globally could become as fast and seamless as sending information over the internet?
That's the opportunity behind stablecoins.
Jennifer Lassiter of @StanChart shared her perspective at LINK:NYC on why businesses are increasingly looking at stablecoins and the future of global payments.
Worth watching!
https://t.co/Cex59VFb9g
Looking to grow through smart partnerships.
As a BD rep I’m always open to connecting with founders, sales leaders, and decision-makers who want to explore mutual opportunities.
Drop a comment or DM , let’s talk growth.
#BusinessDevelopment#Partnersship
@Troy_of_Trades@how2onchain@alexcolevv How about Onchain Journal as well, for Forex, Crypto, Stocks and Synthetic.
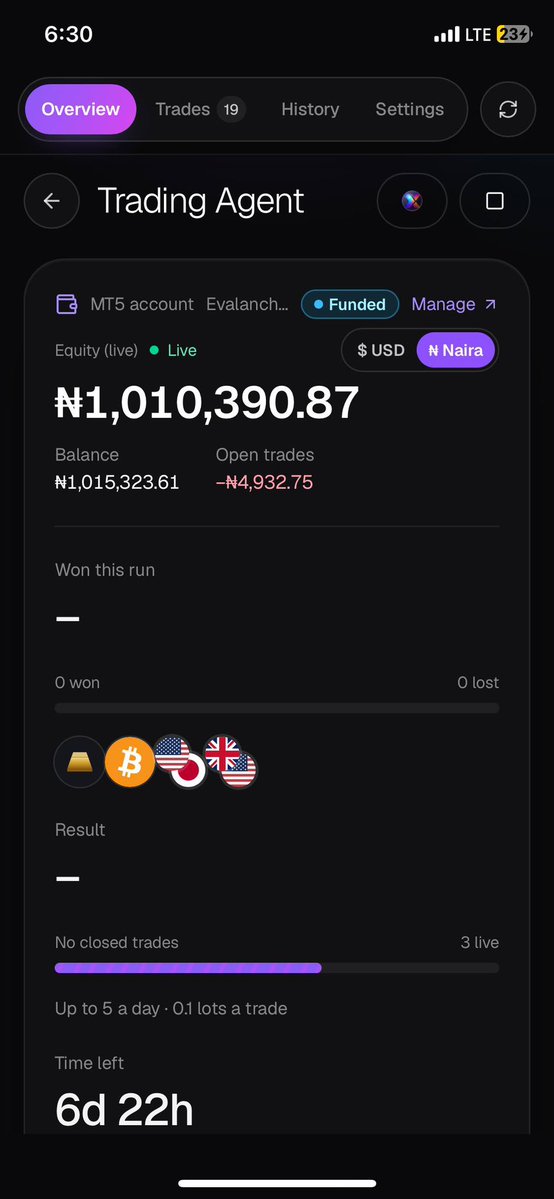
Every trade you or your friends make, is visible and transparent on the blockchain, anyone can look it up at anytime using their Onchain ID on MarketX.
https://t.co/UAb1jvwH7h
Damn! After tuning on my mic, it blocked the device from recording screen record audio…
You can literally ask Matt anything about MarketX, easy way to navigate the site.
https://t.co/BYcrBi21jr
@OlympusDAO, the DeFi protocol behind OHM, has deprecated its legacy bridge and fully migrated to Chainlink CCIP as its canonical cross-chain infrastructure, supporting OHM across seven chains:
@arbitrum@base@berachain@Optimism@solana@RobinhoodCrypto@ethereum
Having an existing bridge doesn't mean you can't migrate to Chainlink. It's all about adopting the right standards.
https://t.co/gW7Vtl08vb
Remember, remember the 5th of November…
Cloud security engineers stop the plot.
BDRs light the deals on fire.
Don’t let the gunpowder hit production.
Happy Bonfire Night.
#BonfireNight#Clou
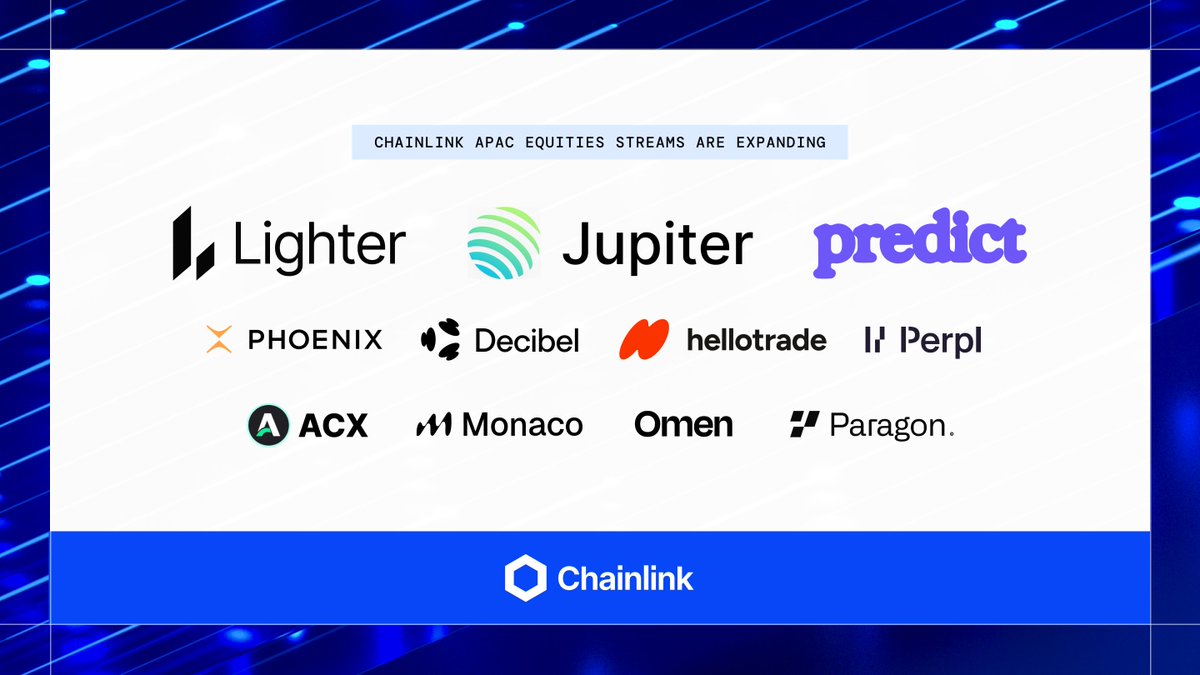
NEW: Chainlink APAC Equities Streams have expanded, covering $40T+ of equity markets across China, Japan, South Korea, Taiwan, and Hong Kong.
TSMC. Tencent. Samsung. SK Hynix. BYD. and more.
Live on: @Lighter_xyz, @jupiterexchange, @Predictdotfun.
LINK everything
Big Tech just dropped $200B+ on AI infra this year.
AI agents are already making 100M+ micropayments on-chain.
The winners won’t be the biggest models they’ll be the ones owning the rails between AI and crypto.
US builders, this is your window.
#AI#Web3#Crypto#AIAgents#Tech
ℍ𝕚𝕤𝕙𝕠
Finally, storing wallet key phrases in system config files is dead. With the rise of AI agent, brace up, the blockchain space will experience more hacks due to private key leak or unpatched hardware wallets.
Agents owns most developers directories. Think of storing your wallets seed phrase in config files? It was secured then, but not now, agents now owns your machines.
The big question right now, are hardware wallets save? Although there are air gaped, if there is a vulnerability, that's it. No patch.
What about exchanges? Well, if they get hacked or decided to go out of business or block you from using their platform, that's it. There are just like banks, just crypto banks.
What about smart contracts and secured onchain vaults? Sorry, there are at risk, a hacker might find a way to drain the onchain vault.
What about browser wallet? Sorry, you will be hacked while using the internet.
Now let's talk about the friction of moving your assets.
Moving your asset from a cold storage wallet is stressful, sometime you don't see the details of what you are signing. Remember the bybit $1.4B hack?
Wish there was an embedded AI model in that cold wallet to interpret the transaction details in ENGLISH.
We love AI models, we love AI agents, we want to use them every day, it makes live easy for us.
At the same, we want to maintain our financial privacy, we don't are seed phrase to leak. Neither do we want a malware to extract our seed phrase or private keys from our machines.
How do we do that?
We need a memory save language in our machines. You know who am taking about. We all need a crab powered system wallet that will save our private keys and seed phrase from hacking.
That's not enough. How do we still use agents to make transaction without leaking our private seeds? The best way is to store your seed phrase in an isolated device storage only accessible by a customized application.
This is why I am building @linkhisho, a terminal agentic wallet that makes live easy without knowing your seed phrase or private key as well.
Your seed is encrypted and isolated inside your operating system native keyring. Even if a malware infiltrates your system, you can still save yourself and your seeds are isolated and secured with no leak and as it zeroized in implementation.
Even during execution, it is quickly overwritten out of your memory, so no way to find a trace in the memory if the malware is so smart, this is the new standard.
The new model is hide your seed phrase and private keys from agents, but let agents orchestrate the work for you and trade directly onchain from your terminal.
The simulation below is simply an architectural flow of hisho.
Would love to get feedback and critics. Always open to learn and improve my product.
#BuildWithGeminiXPRIZE
Cloud Security Engineer tip:
Stop treating IAM as an afterthought.
Most breaches I see still start with over-permissioned roles and long-lived keys.
Least privilege + short-lived credentials isn’t “best practice” it’s the bare minimum.
#CloudSecurity#AWS#Azure