This too shall pass. Used to tweet about programming and infosec. Likes people, science, and music. Swedish & English. jonelf @ Keybase • jonelf.89 @ Signal
@LikeATant När jag gick i högstadiet så hade en kompis en bok med sådana test. Efter att ha gjort ett par stycken så gick resultatet upp. Rätt säker på att jag inte hunnit bli smartare. Litar inte på dem sedan dess.
”Bara för att vi förlorar mot Mjällby i cupfinalen så betyder inte det att vi är världens sämsta lag. Och bara för att vi vinner mot MFF så betyder inte det att vi är världens bästa lag. Jag brukar säga till de unga i truppen, behåll fötterna på jorden & jobba hårt” - Besara ❤️
🚨 Another major supply chain incident 🚨
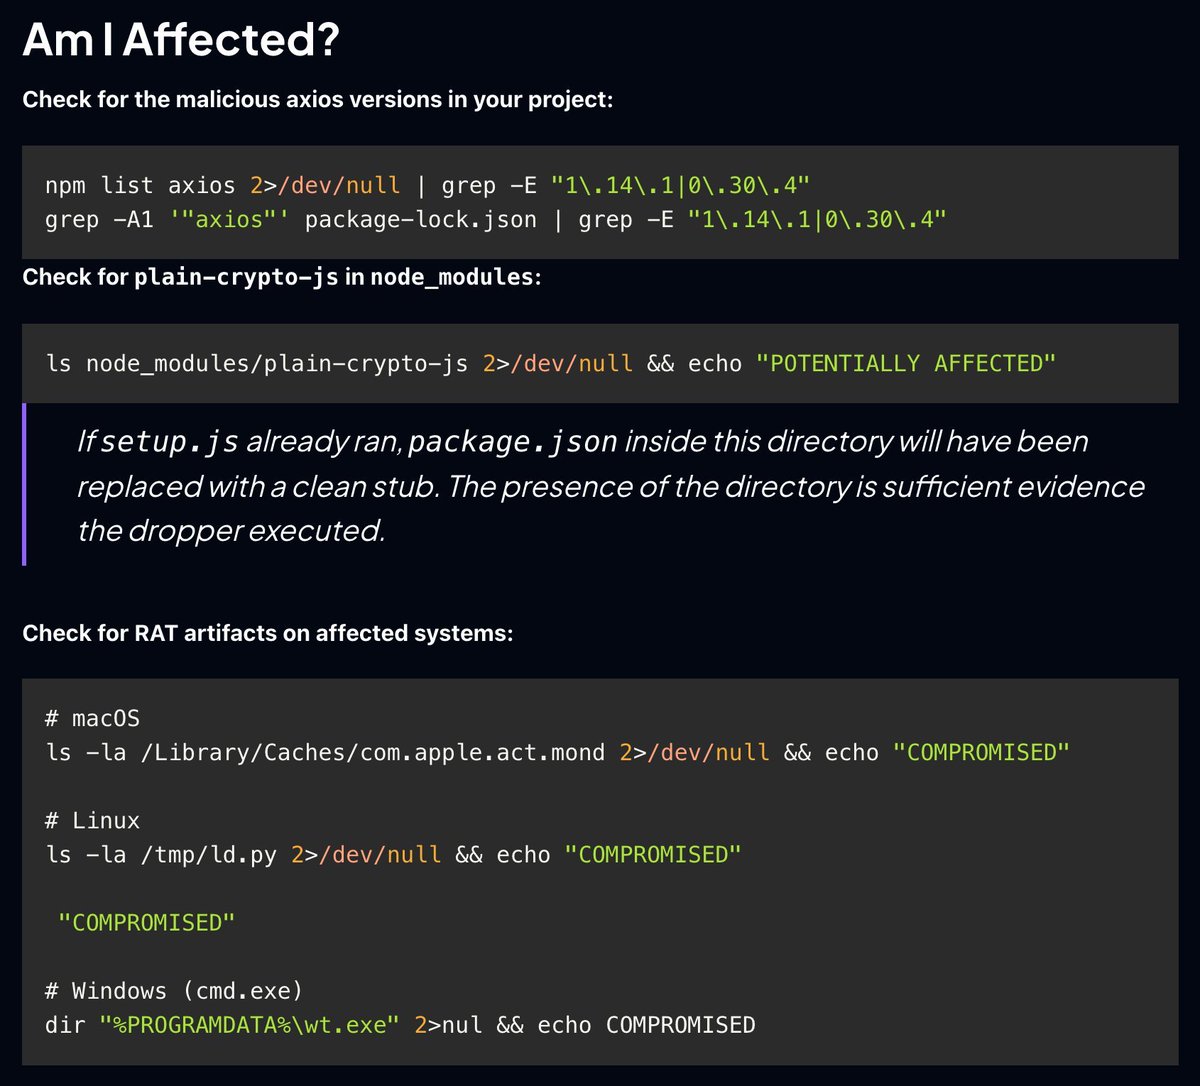
axios — one of the most widely used npm packages — has been compromised. Malicious versions [email protected] and [email protected] were published and are actively dropping malware.
The attack pulls in a newly created dependency [email protected], confirmed as a malicious loader: it executes obfuscated payloads, runs shell commands, and attempts to evade detection while wiping traces.
With 100M+ weekly downloads, this is a live, large-scale supply chain attack.
More details: https://t.co/ex7L7a6hW4
New supply chain attack this time for npm axios, the most popular HTTP client library with 300M weekly downloads.
Scanning my system I found a use imported from googleworkspace/cli from a few days ago when I was experimenting with gmail/gcal cli. The installed version (luckily) resolved to an unaffected 1.13.5, but the project dependency is not pinned, meaning that if I did this earlier today the code would have resolved to latest and I'd be pwned.
It's possible to personally defend against these to some extent with local settings e.g. release-age constraints, or containers or etc, but I think ultimately the defaults of package management projects (pip, npm etc) have to change so that a single infection (usually luckily fairly temporary in nature due to security scanning) does not spread through users at random and at scale via unpinned dependencies.
More comprehensive article:
https://t.co/EJAZbqAPIQ