Next.js on Windows now has a public RCE PoC.
CVE-2026-75604: exploit code dropped shortly after disclosure. Windows-hosted Next.js apps processing untrusted input are in the immediate risk window. Framework RCEs with public material get automated fast.
https://t.co/AQXo2gxLZH
#Cybersecurity #AI #AISecurity #MCP #Claude #GPT #Infosec #Trending #AppSec #RCE
¿Cansado de hacer auditorías de seguridad a mano y perder horas armando reportes?
Conoce ARES: una plataforma open-source de Red Team autónomo construida con FastAPI y React que automatiza todo el proceso.
🚀 ¿Qué hace?
• Genera grafos de ataque autónomos (DAG) en tiempo real.
• Mapeo automático con MITRE ATT&CK.
• Cortafuegos de alcance y reportes instantáneos.
Si te dedicas al hacking ético o la validación de seguridad, esto te ahorra días de trabajo.
El enlace al repositorio lo dejo abajo en los comentarios para que lo pruebes 🔥👇
Netlogon has a CVSS 9.8 public exploit!
CVE-2026-41089: stack buffer overflow in CLDAP. Working PoC is available. Domain-joined Windows that still expose the classic Netlogon path should treat this as urgent.
https://t.co/F6zzTjpjsE
#Cybersecurity#AI#AISecurity#MCP#Claude #GPT #Infosec #Trending #WindowsInternals #ActiveDirectory
ShadowBroker
This tool, ShadowBroker, that brings multiple OSINT feeds into an interactive map, so you to track aircraft, ships, satellites and global events.
When you zoom into the areas you're interested in, you'll find clusters of local news stories sorted by priority
It's pretty easy to set up and doesn't require any paid APIs.
In fact, it can work without any APIs at all.
Great tool
https://t.co/dkXLiwlNUW
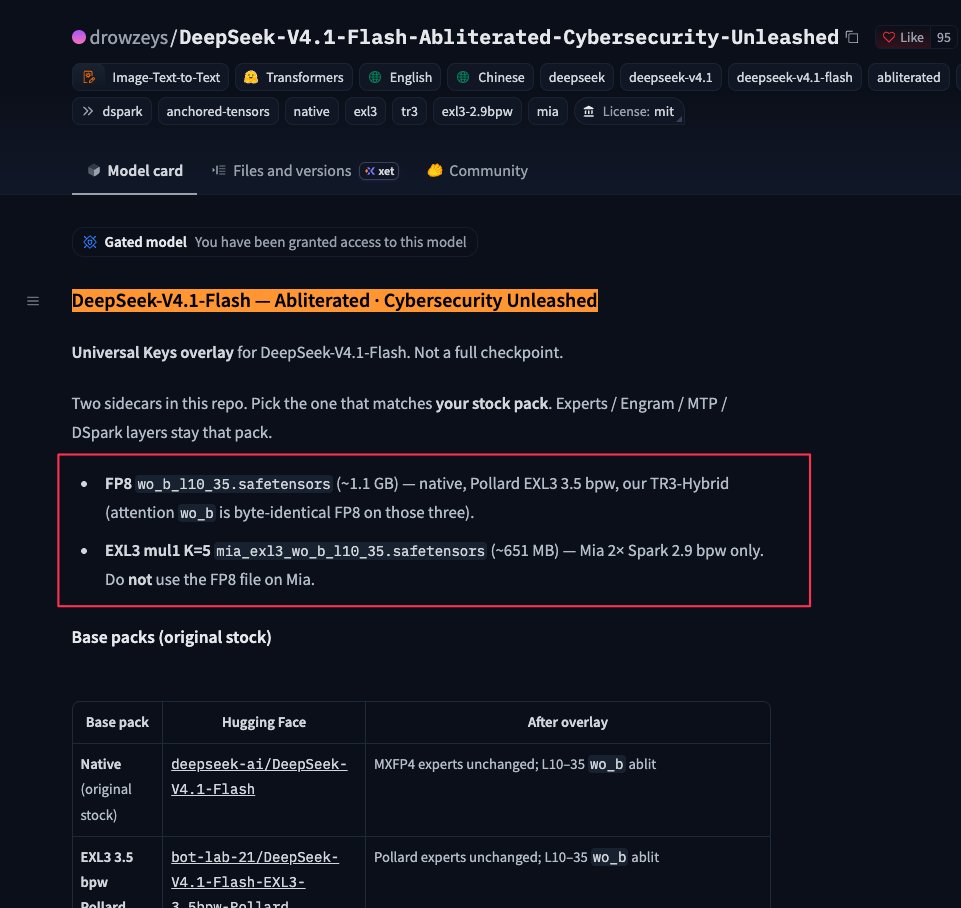
NEW LOCAL MODEL FOR CYBERSECURITY 🚨
DeepSeek-V4.1-Flash-Abliterated-Cybersecurity-Unleashed
> Build on DeepSeek-V4.1-Flash 🧠⚡
> Safety Rails Stripped 👀
Run it locally with DGX Spark / Powerful PC
For SECURITY TESTING On Real Targets 🎯
https://t.co/jcxLe7eMDS
I've just released the first video in the Evilginx Pro Tutorials series, where I'll be providing hands-on tutorials on how to use Evilginx Pro and develop phishlets.
The first video teaches how to set up Evilginx Pro locally and test the Google phishlet from the official phishlet database.
It lays the foundation for the upcoming videos, in which I'll explain, step by step, how to create your own phishlets from scratch.
Enjoy, and happy phishing! 💗
You can find the YouTube link in the post below.
👇
On red team engagements we often may start from a dropbox on the internal network (LAN/Wi-Fi) with no valid domain account. The DCs are easy to find via DNS, and still in plenty of environments anonymous access to the SAMR and LSARPC named pipes are open.
https://t.co/e94x09tKOi
Many of us lean on rpcclient for this (I do too), but over a null session it lists standard users by name only — no machine ($) accounts, full detail one queryuser at a time, and no way to RID-cycle when enumeration is locked down. enum4linux-ng and NetExec cover this ground too and I still use them. I wanted one command that does the whole pass and writes clean, reusable output:
• Users with full detail — descriptions, account restrictions, group memberships
• Groups resolved to their members
• Computer ($) accounts — via RID cycling, which is how you get them at all
• Domain + password/lockout policy, plus LSA/DNS (domain SID, forest, trusts)
• "Interesting" accounts flagged
Output is txt/csv/json plus ready-to-use lists: usernames for AS-REP roasting, computer names for the pre-Windows 2000 machine-account check. SAMR first; if that's locked it still returns LSA recon, with an optional LSA RID-cycling fallback.
Use it only on directories you are authorised to inspect.
Zero-Auth to Domain Admin — Automated Active Directory Attack Chain
A fully automated penetration testing tool that chains 25+ attack techniques to compromise Active Directory environments. Designed for authorized security assessments
#AD#hacking#pwn
https://t.co/nQH3wnPWg1
Attackers burned two rounds of domains on email bomb + fake Teams help desk lures, then stopped registering domains at all. Free M365 trial tenants: no WHOIS, no reputation, unlimited supply.
Time from first Teams message to ClickFix execution: 2m32s.
Lance McNeese on 8 weeks of tracking this campaign, with IOCs and hardening steps:
https://t.co/QMe0oDyRTx
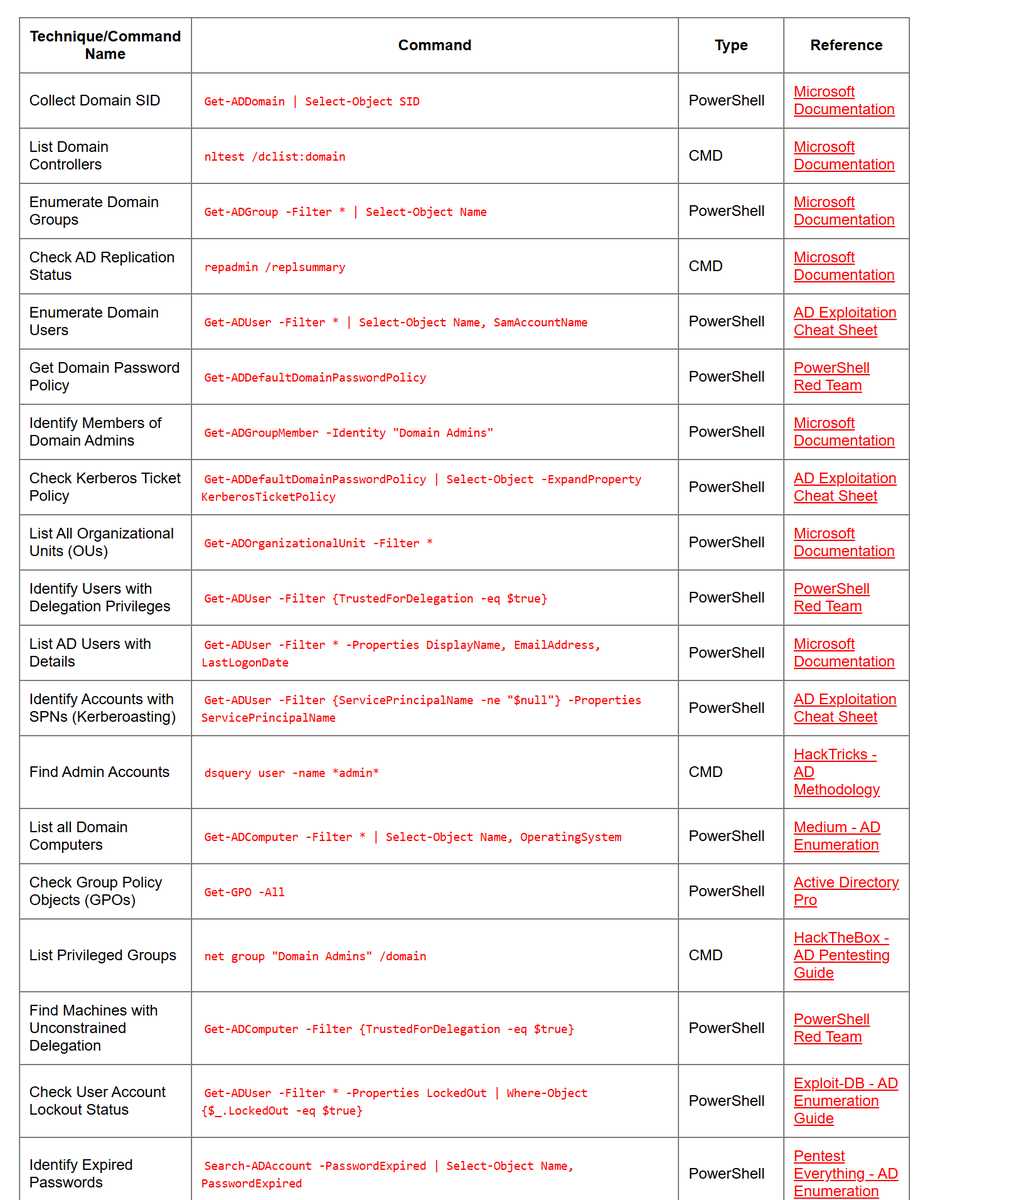
🚨 LOLAD — ACTIVE DIRECTORY ATTACK & ENUMERATION CHEAT SHEET 🔥
🔥 Telegram: https://t.co/upuP8k8ckB
✴️ Twitter: https://t.co/Za7rYILz6E
Working with Active Directory? 🏢⚔️
This is a massive collection of AD commands, techniques and resources for authorized Red Team and security testing.
🔥 Explore:
🔎 AD Enumeration
👥 Users & Groups
💻 Domain Computers
🏢 Domain Controllers
🌐 Forests & Trusts
🔐 Kerberos & SPNs
🎫 Delegation
🛡️ ACL Enumeration
📜 GPO Enumeration
🔑 Credential Techniques
⚔️ Lateral Movement
🧩 Fileless Techniques
⚡ PowerView & PowerUp
💥 Impacket & Mimikatz
🎯 Pass-the-Hash / Pass-the-Ticket
👑 DCSync & Ticket Attacks
💡 The real value?
Instead of memorizing isolated commands, build a structured AD methodology:
ENUMERATE → IDENTIFY WEAKNESSES → VALIDATE → ESCALATE → MOVE → DOCUMENT
🔗 LOLAD:
https://t.co/s1g3bFqaxr
📌 Bookmark this for your next authorized AD lab or assessment.
⚠️ Use offensive techniques only in environments where you have explicit authorization.
♻️ REPOST & SHARE with the Active Directory community!
#ActiveDirectory #ADSecurity #RedTeam #Pentesting #CyberSecurity #Kerberos #PowerShell #Mimikatz #Impacket #EthicalHacking
THIS IS F**KING DANGEROUS
SOMEONE JUST TURNED CLAUDE INTO AN AUTONOMOUS PENTESTER.
HexStrike AI connects an LLM to 150+ professional cybersecurity tools through MCP.
You get:
→ 12 specialized AI agents
→ 150+ security tools
→ Network & web security testing
→ Automated pentesting workflows
→ Local execution on Kali Linux
The wild part?
Claude autonomously generated a SQL injection payload, ran the test, and solved a PortSwigger lab.
AI + real security tooling is getting serious.
REPO BELOW