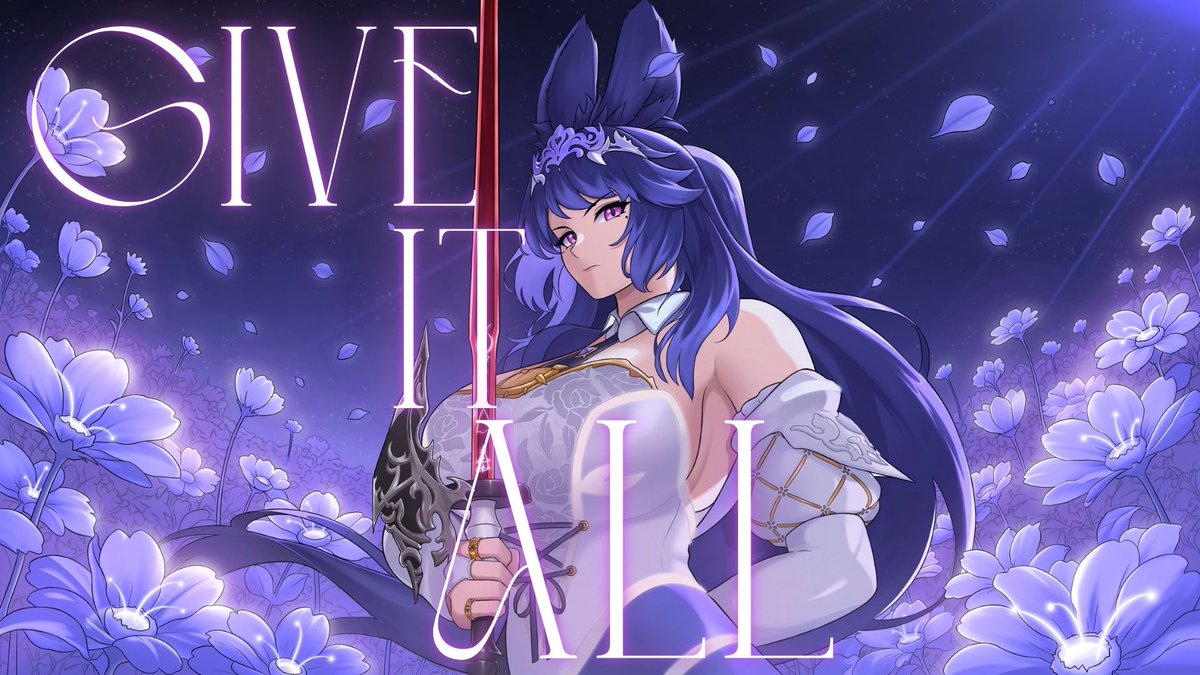
FINAL FANTASY XIV : Give it All【Cover by Bakurin】
TH Ver.
My First #FF14 song cover !
this is my favourite song
I translated the first half of this song.
it's in Thai language , My language 😍
Premiere Tomorrow DO NOT MISS !
29 Oct 18.00
https://t.co/pL8zEkAYJm
New game plus อีกครั้งไม่รู้รอบที่เท่าไหร่แล้ว😮💨
อย่างที่หลายๆคนน่าจะทราบกันแล้ว
เพจเฟสบุ้คผมบินไม่รู้จะสามารถกู้กลับมาได้มั้ย…
ฝากติดตามเพจใหม่กันให้หน่อยได้มั้ยครับ
https://t.co/gVAQWcysNJ
แล้วถ้าจะไม่เป็นการขอมาก
ไปช่วยกดไลค์+แชร์โพสต์นี้กันหน่อยจะขอบคุณมากๆเลยครับ🙏🏻
ผมท้อ…
X ALGORITHM UPDATE 🚨
X just stopped cutting new posts first, and that should help small accounts (I check it daily with Claude and share updates worth sharing with you)
tl;dr:
- X can only check 2,800 posts each time you open your feed
- new posts used to be last in line, so they got cut first
- now everything gets cut equally, new posts included
- posts labeled low quality or misinfo now show a warning, and people can't like, reply or share them
- no score changes this time
lesson learned: your new posts now get a fair chance to be seen. Your first 2 hours still matter most.
full details:
- How it worked until this week
Every time someone opens For You, X collects around 3,700 posts it could show them: posts from people they follow, popular posts, posts liked by similar people, and brand new posts.
But X only has time to check 2,800 of them.
So it just took the first 2,800 in line. Brand new posts were at the back of the line. When there were too many, they were the ones left out... and a post that never gets checked can't be shown.
- What changed
Now everything gets cut by the same amount. 25% too many? Every type of post loses 25%, new posts included. Nobody goes first.
- Why small accounts should care
Those brand new posts are under 2 hours old, with under 8 likes and under 500 views. That's where most posts from smaller accounts are.
My read: they now get a fair chance instead of being cut first. How often X actually hits the 2,800 limit isn't in the code, so I can't tell you how big the difference is.
- Low quality and misinfo posts now show a warning
If X labels your post as low quality or misinformation, people who don't follow you see a warning on it, and they can't like, reply, repost, bookmark or share it. The code doesn't say what gets a post that label.
Here's a recap of what you should be doing:
- a new post gets its extra push only in its first 2 hours and first 200 views, so post when your people are online
- likes carry more weight than ever at 0.66 each
- people sticking around pays, the time-spent score is 50% higher than two weeks ago
- a read of 10+ seconds after someone opens your post adds 0.4
- the boost favors the post with the best like rate from its first viewers
- accounts up to 50K can get one fresh original lifted to roughly 16th
- nothing beats a copy link share, it scores 20
- replies, quotes and DM shares each score 5
- talk with your mutuals, replies between you score 20 instead of 5
- originals are the only posts that travel outside your follower base
- the 1st and the 32nd like each open a new route to strangers
- your 2nd post in the same feed is worth 62% of the first, so pick your best one
- videos still need 10+ seconds to qualify for the video lists
- earning a follow adds 4
- a pinned post with a bad link can flag the account for 7 days, worth a quick check
What you should NOT be doing:
- posts that get labeled low quality or misinfo now carry a warning, and nobody outside your followers can like or share them
- video alone won't carry you, an open counts 0.02 and the watch 0
- hide-worthy posts cost more, "not interested" sits at -52.27
- a post at 3am burns its 2 hour window before anyone sees it
- a tap that turns into a bounce is worth only 0.3
- replies and reposts don't get past your followers
- insults get your post hidden from anyone who doesn't follow you
- adult media in 3 of your last 5 posts puts a label on your account
- disguised content in videos gets checked from 64 likes, harder at 512
- self-reply chains under big accounts risk being zeroed
- one account label and non-followers stop seeing you entirely
- low-rated links don't belong in your pinned post
- recycled wording can get tagged as copypasta spam
- strangers tagged plus a low quality link is a pattern X flags
- engagement bait has no size exemption
- several posts in a row end up competing with each other
- hashtag stacks add nothing
- bookmarks are still worth 0
- 48 hours in, For You is finished with a post
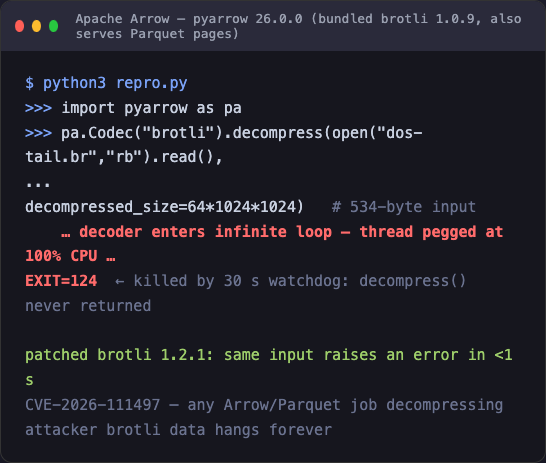
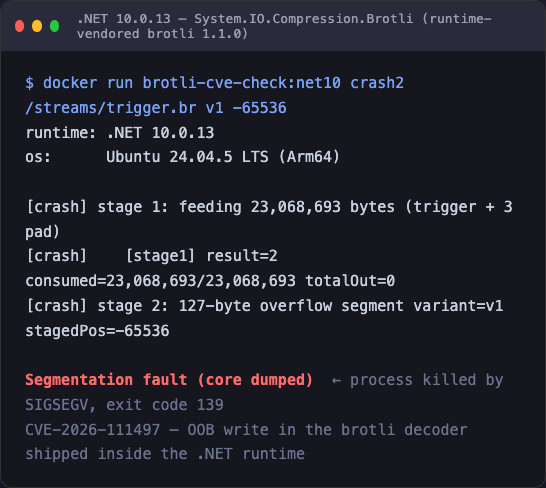
🚨 UPDATE: The Brotli flaw (CVE-2026-111497) goes beyond Node.js and web traffic.
• .NET: patched by Microsoft
• FFmpeg: hit via a crafted JPEG XL image
• ClickHouse: one request crashes it, fix not yet released
• Apache Arrow: no fix yet
Details ↓ https://t.co/H5YLRc19Zw
‼️Microsoft Authenticator Flaw Lets Malicious Android Apps Steal Account Tokens With Zero Permissions
Details: https://t.co/bxLApplffv
Microsoft patched high-severity flaw CVE-2026-80097 (CVSS 8.6) in Authenticator for Android, allowing malicious apps with no declared permissions to steal work account access tokens due to improper authentication in its broker component.
Microsoft classified the flaw as a local elevation-of-privilege vulnerability. The issue affected Android devices with Microsoft Authenticator installed and a signed-in work account.
#cybersecuritynews
‼️ BREAKING: Oracle Issues Emergency Java Update for Critical 9.1 HTTPS Trust Vulnerability
Details: https://t.co/XZV8KY0rPW
Oracle has released an emergency Java security update to address CVE-2026-91403, a critical vulnerability affecting how Java applications trust digital certificates. Published on October 21, 2026, the alert assigns the flaw a CVSS 3.1 score of 9.1 and covers Oracle Java SE and GraalVM.
The update blocks affected intermediate certificate authority certificates linked to eMudhra. According to Oracle’s security advisory, the issue affects the Java Secure Socket Extension, or JSSE, component.
Oracle rates exploitation as low complexity, with no authentication or user interaction required. Successful attacks can expose or change sensitive data, although the risk matrix lists no availability impact.
#cybersecuritynews #vulnerability