From ingesting 30+ intel sources to executing autonomous queries, discover how @SofectaLabs uses AI Agents to slash dwell times and protect your environment 24/7.
The future of MDR is here: https://t.co/6AARjdPKxl
GreyNoise observed a ~500% surge in IPs scanning Palo Alto Networks login portals on October 3, 2025 — the highest level we’ve seen in 90 days. Read our full analysis here 👉 https://t.co/gd89IAsMdW
#PaloAltoNetworks#PaloAlto#GreyNoise#ThreatIntel#PANOS
Do you have your organization emails under control? Check out how we secure our customers emails with @sublime_sec@tines_hq and or home-grown MDR service.
Give us a call and secure your email today!
Email is a primary cyber attack vector with rising phishing and BEC threats. Secure your organization with robust email security, SOC, and MDR services.
https://t.co/isKscX9NUo
#cybersecurity#email#attacksurface#secure
It’s a big day for @tines_hq, as we announce our latest funding round.
This milestone means a great deal to us. It’s a testament to every single customer who trusts Tines to power their most important workflows.
Find out more:
https://t.co/bUgdKLotEU
https://t.co/q46XWCyVBi
We’re thrilled to announce that we’ve raised an additional $50M in funding, allowing us to make even greater investments in our product and customers.
WATCH: CEO @eoinhinchy shares his plans for Tines👇
Learn more:
https://t.co/6pdxWTgC2C
Jäikö 10.04.2024 pitämämme #Akira- webinaari näkemättä?
Tallenne on nyt kaikkien katsottavissa YouTube-kanavallamme
https://t.co/4b3W9yzQGx
Tallenteella kuulemma avaussanat @kimmorousku, sekä asiantuntijapuheenvuorot kiristyshaittaohjelmien yleisestä tilanteesta Suomessa @TraficomFinland@CERTFI erityisasiantuntija Max Mäkinen esittämänä, sekä @AnttiPiriwirta , @Deloitte, puheenvuoro otsikolla "Oppeja Akiran tietomurron tutkinnasta – mitä käytännössä näimme ja koimme?"
Huomioithan myös tulevan #Tietoturvakatsaus2024 -semiraarimme, https://t.co/yTJXijkSja
Katsomalla webinaaritallenteen lunastat myös oikeuden oikeuden erityishinnoiteltuun osallistumisoikeuteen #Tietoturvakatsaus2024 -seminaariin:
Vaikka et olisi jäsenemme, voit lunastaa osallistumisoikeuden samalla hintaa kuin Tietoturva ry yhteisöjäsenet tai TIVIA ry jäsenyhdistysten jäsenet - 95 euroa per henkilö, normaalihinnan ollessa 249 euroa.
Alennushinta koskee vain uusia ostettavia osallistumisoikeuksia, eikä alennushintaa voida soveltaa aikaisemmin ostettuihin osallistumisiin.
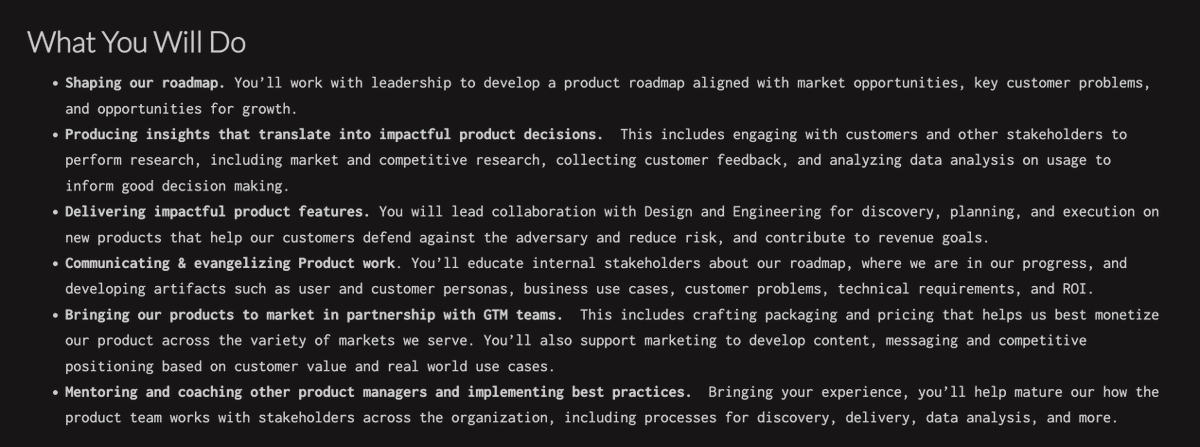
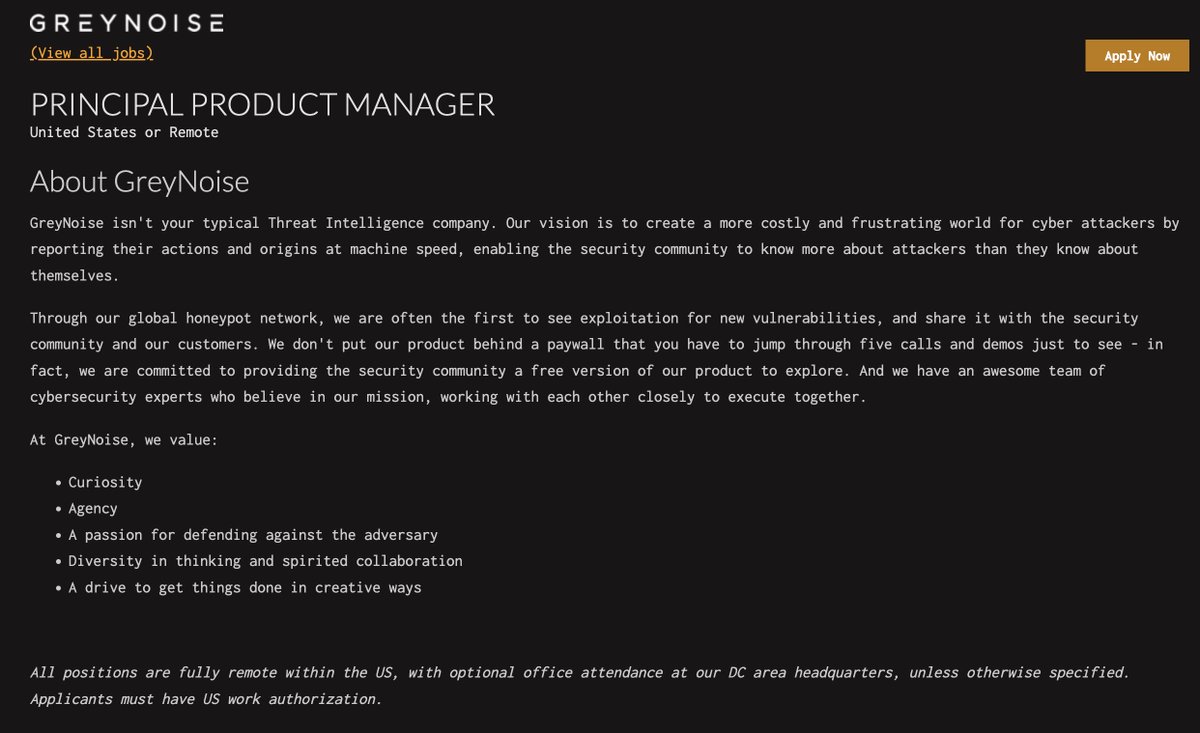
We're hiring a Senior Product Manager at @GreyNoiseIO! This is a really cool opportunity. You'll be working with some of the most insane engineers and designers you've ever met, building and bringing to market the most insane tech you've ever seen.
https://t.co/gkFmXV0qKB
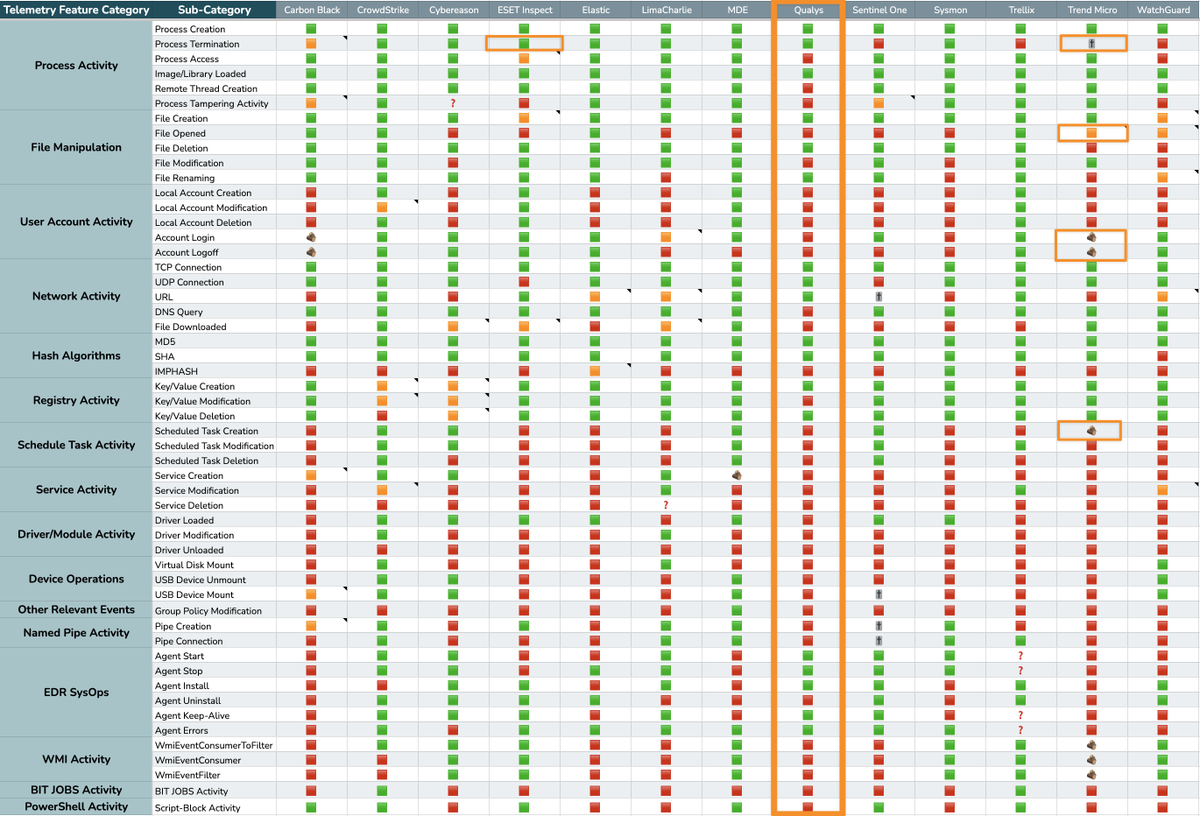
I updated the EDR telemetry project with corrected telemetry and new additions! See below the changes and upcoming EDRs:
✅ Corrected Trend Micro Telemetry
✅ Corrected ESET Telemetry
🌟 Added Qualys EDR
🎯New Additions Coming Up:
🔜 Sophos EDR
🔜 Cortex EDR
Vendors are continuasly evolving their EDR solutions by adding more telemetry capabilities. To keep up with the updates, we need the help of the community.
🔗Checkout and contribute to the project here: https://t.co/8DmXzffYVC
🔗Checkout the telemetry table here: https://t.co/6nvs6ymqof
@Andrew___Morris It has some ethical standards and protects humanity from situations where the universe might collapse. As it probably would if you (@Andrew___Morris ) and @jkamdjou would bathe naked in a bathtub with rubber ducks. Just saying 🤷🏻♂️
1. Comfort - Direct access w/o the need for VPN or tunneling
2. Costs - No additional expenses for VPN services
3. Trust - Assumption that a big vendor's product is inherently secure
4. Lack of Awareness - The belief that it's unlikely anyone would discover & exploit the service
We’ve observed a new uptick in Microsoft QR Code + DocuSign phishing this morning. Decoded QR code leads to a Microsoft credential phishing page. The technique enables highly sus links like .ru and DNGs to land, which traditionally would likely be sent straight to spam by Microsoft/Google.
QR code in the image below has not been defanged, don't scan.
h/t @samkscholten