This week on The Fine Print podcast, @MattInformed of @PractiveSec joins @juliecbarrett 👇
Child safety bills are being sold as “protecting kids and putting parents in the driver’s seat.”
Matt spent 25 years inside cybersecurity (Palo Alto Networks, CrowdStrike, defense work) and sees something different: more data collection, more platform power, and less parental authority.
Full episode drops Sunday at 7PM ET on our YouTube channel - subscribe & turn on notification: https://t.co/P2HENo2lk6
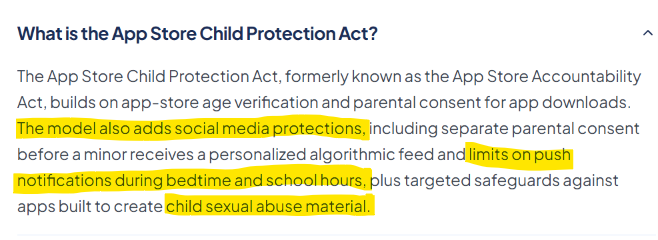
⚠️They've not only rebranded the App Store Accountability Act, but they've given it steroids. The App Store Child Protection Act adds a separate parental consent for social media functions (that means more identity data collection from your family), limits on notifications during bedtime (hey parents...don't send your kids to bed with devices!!!) and school hours (need to reach your kid at school...flip phone).
In order to limit notifications like this, "Big Tech", needs to know a lot about your child, which means ongoing surveillance and monitoring.
So much for "holding Big Tech accountable" - this makes Big Tech your child's babysitter.
The addition of CSAM is an emotional hook for lawmakers - who could be against this? There are existing laws that make this illegal - enforce them!!
Thousands of reachable Bitcoin Core nodes trusted every inbound Tor connection, Bitcoin Core says.
Tor peers arrive with the daemon's local address, which matched the -whitelist range some vendors set. Fixed Oct 2025; disclosed Nov 10, 2026.
https://t.co/lJxsvWr2gZ
got another fake job interview invite today. this time the "assessment" had hidden git hooks that piped a remote script straight into sh to steal SSH/cloud credentials.
they even built a custom C2 dashboard on vercel called "Sentinel".
reverse engineered the whole thing in a sandbox. cc: @vercel@NotionHQ
OpenSSH vulnerability exploited within hours of disclosure (CVE-2026-123158)(OpenSSHの脆弱性が公表からわずか数時間後に実際に悪用される(CVE-2026-123158)) #Help Net Security (Nov 6)
https://t.co/HPvDTkqfx4
Three things that bit us building a checkout with zero JavaScript:
1. Monero addresses are lazy. Our payment server only generates one when a checkout page activates that method. A self-rendered page has to make that call itself or the address field is empty.
2. Every Tor visitor shares one IP. Traffic from an onion service arrives from the Tor daemon, so per-IP rate limits would have let ten visitors lock the whole mirror out of checkout.
3. The last page counts. Our first version handed the finished order to the normal order page. It worked with scripts off, but its source carried the site scripts, which broke the "view the source" promise on the final step.
https://t.co/eSCKDrhQko
A reported bypass puts SAML-enforced MFA on VPN gateways in focus.
Reportedly, credentials for another login path can bypass SAML checks; a patch is available.
Verify versions, patch exposed gateways, and review unusual sessions.
Get the brief → https://t.co/VYSGmOAGGU
You asked an AI for advice.
Meta uses that chat to decide which ads you see.
Its spokesperson said there is no opt out.
The question was free.
The answer came with a sponsor.
The reported loss is also a warning about AI’s blast radius.
CSO Online says attackers allegedly used an internal AI tool after compromising developer machines.
Treat connected AI assistants as privileged enterprise components.
Get the brief → https://t.co/QUJcggkRbs
OPENSSH SHIPS WORKAROUND FOR ALPINE FLAW THAT CAN EXPOSE KEY-ONLY ACCOUNTS
Alpine says exposure requires SSH password logins enabled and PAM disabled. Operators should update and restart sshd, not just install the package.
Read more here:
https://t.co/LZOFZKQbaK
A medium score still warrants urgent Apple fleet checks.
CISA’s KEV listing follows reports of exploitation across multiple Apple operating systems.
Verify patches, find exposed devices, and review relevant telemetry.
Get the brief → https://t.co/OXUd08tcoI
#Vulnerability
Hey bug bounty hunters! Share any AI-powered bug bounty resources or cool stuff you've been experimenting with. Things like building your own bug bounty harness, creating a HackBot, using AI for auth testing, integrating AI with MCP, automating recon, AI-powered vulnerability discovery, or anything else that can make bug hunting smarter and more efficient.
Would be great to have everything in one thread so we can all check it out, learn from each other, and share ideas!
#bugbounty
🆔Online ID checks make your personal information a honeypot for hackers.
“70,000 documents related to people’s identities were leaked” after Discord, a messaging app, suffered a cyber-attack - @mayathomas98 warns
Say no to passports for the internet⤵️
https://t.co/x6drNlyXX2
Security release pre-alert:
We will release new versions of Node.js 22, 24, and 26 release lines on or shortly, after 2026-11-11 in order to address security vulnerabilities.
The highest severity issue fixed in this release is HIGH.
https://t.co/6PdxXwHLE6
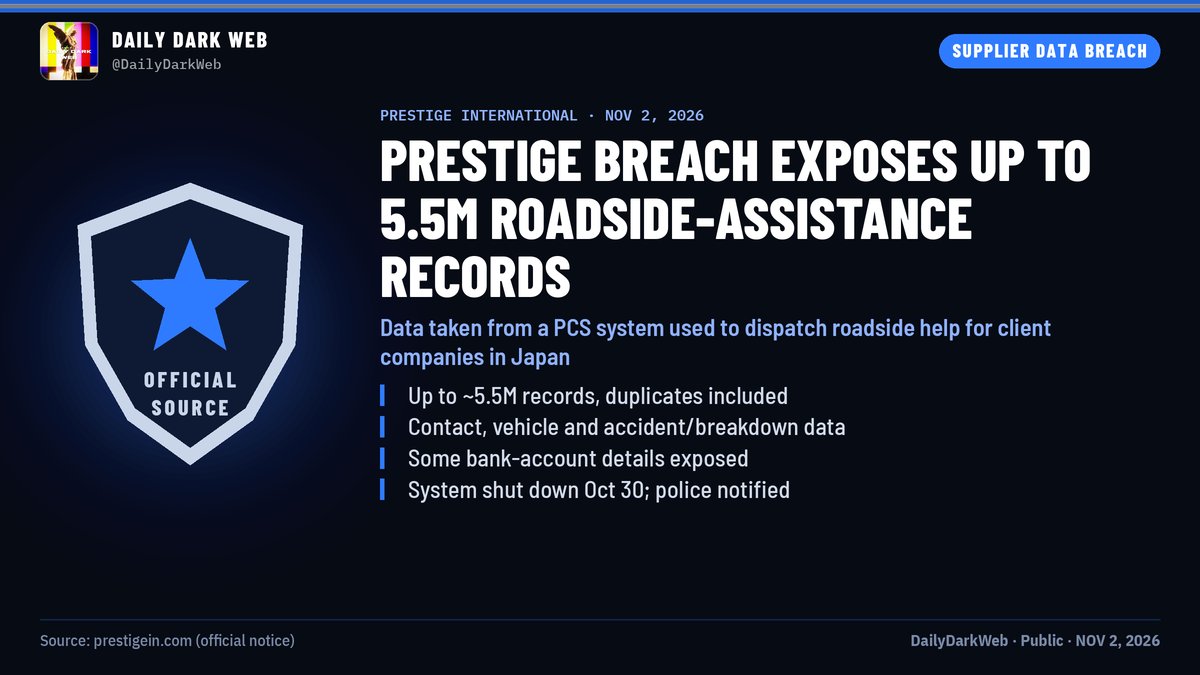
🇯🇵 🚨 PRESTIGE INTERNATIONAL BREACH EXPOSES UP TO 5.5M ROADSIDE-ASSISTANCE RECORDS
Tokyo-listed Prestige International says attackers took customer data from a business system its subsidiary Prestige Core Solution (PCS) uses to take and dispatch roadside-assistance requests for client companies.
• Up to ~5.5M records, a count that includes duplicates; the number of unique people is still being determined
• Data: names, addresses, phone numbers, emails, vehicle details (registration and chassis numbers), accident/breakdown request info and some bank-account details
• Intrusion detected Oct. 29; stolen credentials were disabled, but access continued and the system was shut down Oct. 30
• No credit card data leak confirmed; police and Japan's privacy regulator notified
⚠️ Analyst Note:
ENEOS separately says up to 8,500 of its car-lease contracts are affected; that is part of the same incident, not extra. Sony Assurance says its roadside desk is hard to reach and its customers' exposure is still being checked. No actor, ransomware claim or CVE has been disclosed. Expect phishing posing as insurers or roadside services.
https://t.co/qJp5F7cAdr
#DDW #DataBreach #Japan #CyberSecurity
Context as Infrastructure: Knowledge Compilation for Retrieval in Agentic Systems with Harnesses
Proposes knowledge compilation for agentic search, where LLMs enrich documents at ingestion so agents get compact context.
📝https://t.co/ZUE3mFvJYZ
👨🏽💻https://t.co/6ha1rVPJ36