Fundamentals decide the allocation. The LLM only touches what rules can't read: news, announcements, anything unstructured.
@Yas_MoonUp from @getMoonUp on why that line is where it is. Full episode in the first comment!
Tokenized stock baskets with downside protection, on @solana. That's what @Yas_MoonUp is building at @getMoonUp
He's on the Hot Seat this Monday Sep 21st at 9:30AM CET📅
Stream link coming. Stay tuned!
Building an Ethereum wallet? Explore Vitalik's EIP-8141 proposal in Frame Lab.
Make a deposit fail and compare rollback behavior across account models. Interactive simulation of a draft proposal.
Lab + write-up in the reply.
Vitalik's frame proposal got scheduled for @ethereum's Hegotá upgrade. The receipt has no overall status on it.
So a deposit can fail, roll its approval back, burn the gas anyway, and your wallet is on its own deciding what to tell the user.
we built a lab for it⏬
The fact that your audit report says "no critical findings" doesn't mean you're safe.
@EthAltuve from @Hashlock_ is joining us on dOrg Hot Seat to talk about that gap. Tuesday, Aug 18, 11:30am CET.
Set your reminder👇
What's your purpose?
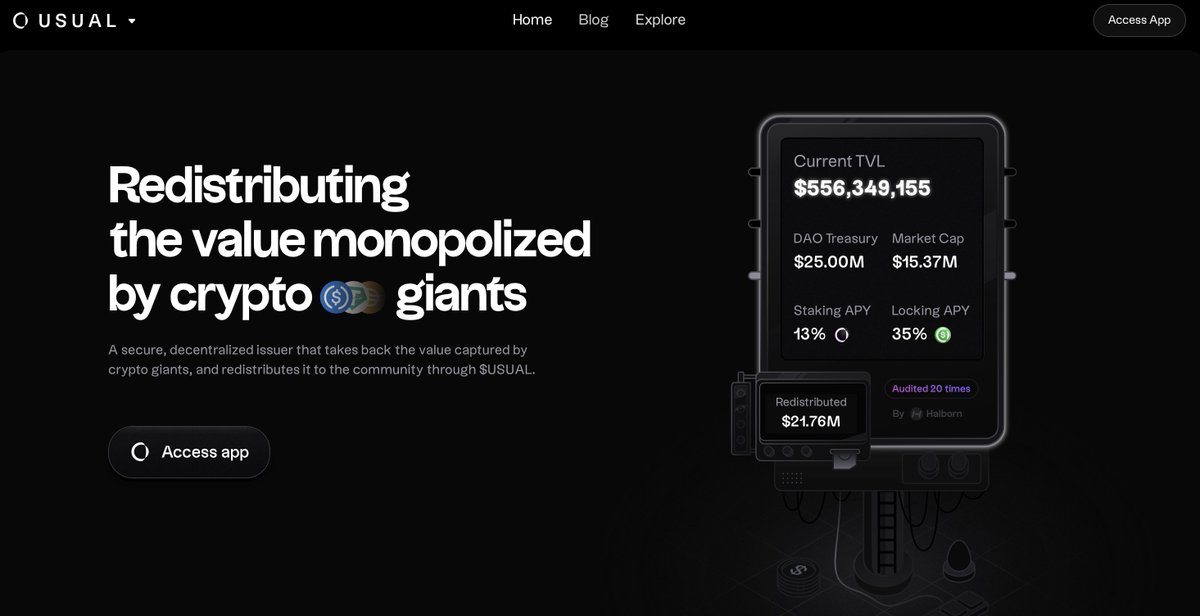
That's the first question we ask every client, because clarity of purpose is what got our clients to +$4B in total value locked.
Technical fear is real when your vision has nowhere to land. That's where dOrg comes in: infrastructure and talent that turn what's in your head into a live product.
See how we did it with @usualmoney 🔽
https://t.co/WqbpXGTsm0
Most teams think a clean audit means they're safe.
Drift lost $285M this year, not to a code bug, but because someone convinced a Security Council member to hand over admin control...🙃
Audits check your code, but they don't check the humans holding the keys.
What's getting more of your security budget right now, audits or opsec?
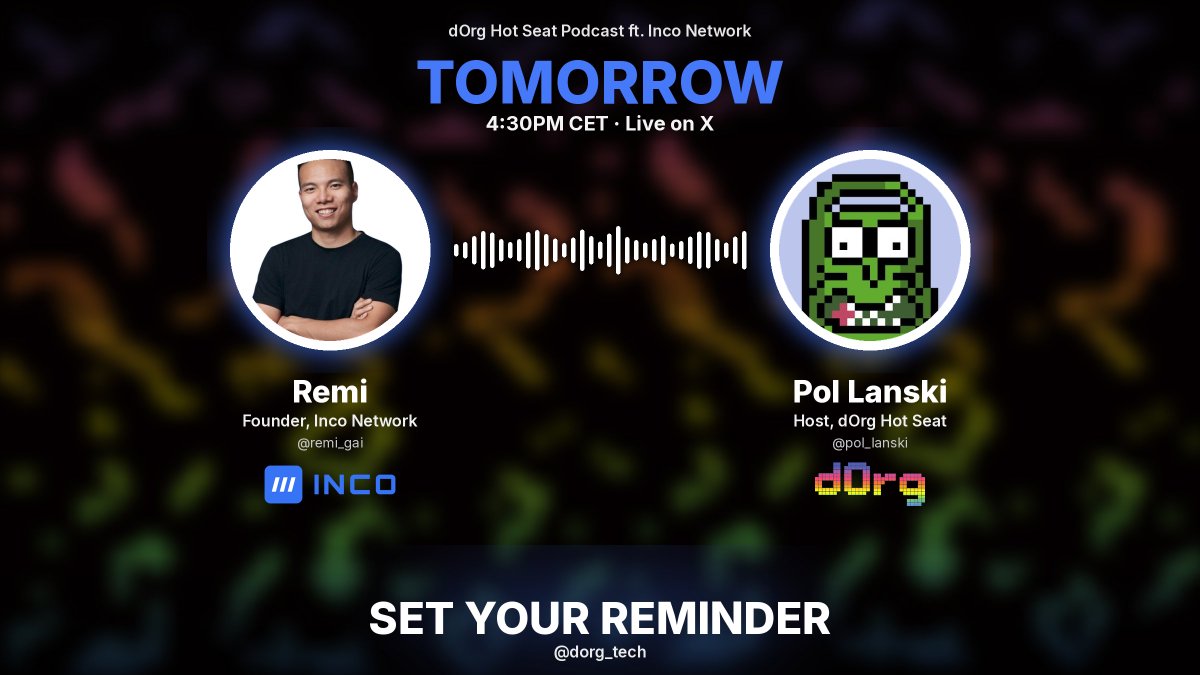
Tomorrow's the day.
@remi_gai from @inconetwork joins dOrg Hot Seat live on X, 4:30PM CET.
Let's talk encrypted smart contracts, on-chain privacy, and everything Inco is building.
Set your reminder now!👇
https://t.co/bmkoiXPEw5
Big weekend energy before two huge conversations drop on dOrg Hot Seat!!
🟦Tuesday: @remi_gai founder of @inconetwork, building encrypted smart contracts so on-chain data can finally stay private.
🟨Thursday: @solquicks, marketing lead at @solflare, one of Solana's most trusted wallets, on what it takes to build for millions of users.
Hosted by @Pol_Lanski🔥
six founders posted the exact same thing on X this month: "need a senior rust engineer for solana, urgently."
None of those threads move fast enough. sourcing today lands someone in Q3, and your window was Q2🫠
The fix isn't a faster hire, it's not hiring for the module at all, we show you how we can solve that pain point: https://t.co/HZ7eGl4y3f
@EliBenSasson If the security of a cryptographic primitive rests on a computational problem that is known to be efficiently solvable by a quantum computer, then it’s not quantum-resistant.
@skeptrune This is one of those engagement farming posts. I get it: everyone’s trying to put meat on the table, but c’mon, this perception-warping fear-mongering slop ought to stop at some point.
ZK Rosetta catalogs zero-knowledge protocol specs or proposals and links to audited implementations where they exist, recording where they do not. It does not, however, implement, fork, or vendor any verifier, primitive, or curve operation.
93.9% of bug bounty programs that run five years or more eventually surface a confirmed critical bug...That's immunefi's own data.
So the bug is almost certainly already in your code. The bounty doesn't change that, it just decides who finds it first: a researcher you pay, or someone who won't report it.
The teams that win that race do the real security work before the bounty goes live. We wrote up what that takes. → https://t.co/UTrlTTvzUg