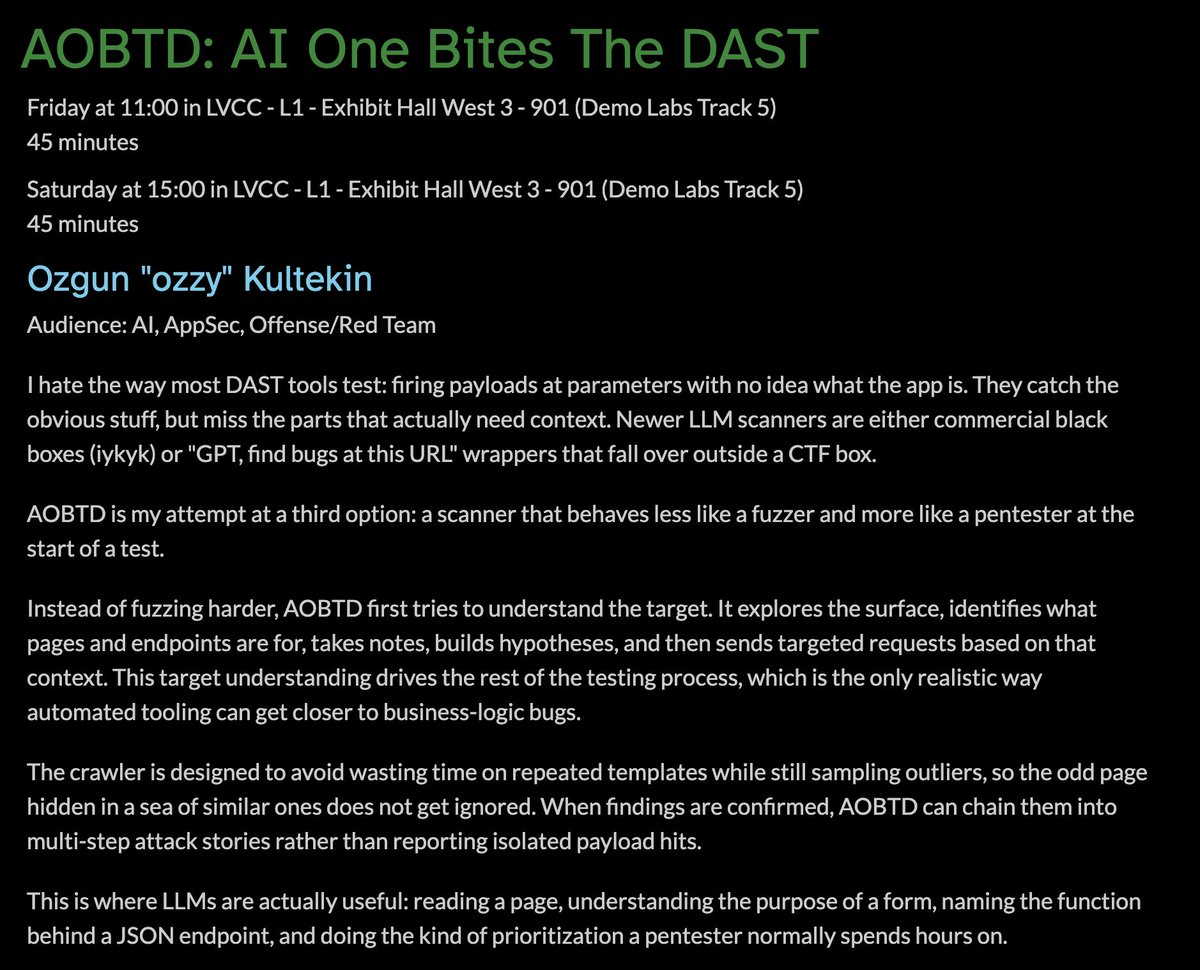
⚠️ public service announcement ⚠️
apparently googling "sshole poc" does not return what you were hoping for (or maybe it does, idk, not judging)
the actual one is here, safe for work:
https://t.co/c2BkpJYulm
i don't think anyone needs a PoC for this but if you'd like to know whether you're an *sshole (i mean affected), there's a script in the repo that tells you. yes or no, and why https://t.co/c2BkpJYulm
i don't think anyone needs a PoC for this but if you'd like to know whether you're an *sshole (i mean affected), there's a script in the repo that tells you. yes or no, and why https://t.co/c2BkpJYulm
I recently discovered two new RCE vulnerabilities in n8n.
One is a bypass for my previous finding (CVE-2025-68613), and the other is a fresh Command Injection in the Git Node.
1. The Sandbox Escape (CVE-2026-25049) I managed to bypass the fix for my original report (CVE-2025-68613) multiple times. By using Javascript quirks like Template Literals and Object Destructuring, I could escape the sandbox again. The issue has been fixed in n8n versions 1.123.17 and 2.5.2. Users should upgrade to these versions or later to remediate the vulnerability.
Full technical analysis: https://t.co/RX1Zg2VMX9
2. Git Node Command Injection (CVE-2026-25053) This one leverages the addConfig operation in the Git Node. It lacks validation, allowing an attacker to inject payloads into core.sshCommand. Leads to RCE. The issue has been fixed in n8n versions 2.5.0, and 1.123.10. Users should upgrade to this version or later to remediate the vulnerability.
Full technical analysis: https://t.co/qxkmdmWhoY
Thanks n8n team!
bir suredir web security enumeration tarafinda LLM'leri nasil kullanabilecegimizi ve seclist gibi wordlistlerin yerine nasil gecebilecegini gosteren bir proje uzerinde calisiyorduk:
https://t.co/c6Tz8iDywD
ozellikle bug hunting/web security tarafinda calismalar yapan kisilerin feedbacklerini almayi cok isterim
ve tabii ki custom model training/qwen fine tuning kisimlarinda da hicbir zaman destegini esirgemeyen @AlicanKiraz0 'a tesekkurler, onsuz olmazdi 🫶🧡
after a big delay i finally published https://t.co/c6Tz8iDywD
i think it's a good starting point to explore how ai can shape the future of the web enumeration, because traditional methods like fuzzing with wordlists feels outdated
would love to hear y'all feedbacks on that! and you're more than welcome to contribute
here is the talk from @defcon :
https://t.co/bqBTyBO2pa
after a big delay i finally published https://t.co/c6Tz8iDywD
i think it's a good starting point to explore how ai can shape the future of the web enumeration, because traditional methods like fuzzing with wordlists feels outdated
would love to hear y'all feedbacks on that! and you're more than welcome to contribute
here is the talk from @defcon :
https://t.co/bqBTyBO2pa
İnternet ağı bana hep büyüleyici gelmiştir; yıllardır sektörde olmayan arkadaşlarıma da, eşime de defalarca heyecanla anlatırım.
Dün bu tutkuyu bir adım öteye taşıyıp https://t.co/yay8zZisb7’u geliştirdim 🥳
Hem sıfırdan başlayanlar hem de meraklı öğrenciler için; teori + simülasyon içeren interaktif bir öğrenme alanı sizlerle. 🚀
TR & EN | Selamlar Dostlar, şu ana kadar açık kaynak olarak yayınlanmış en büyük parametreli siber güvenlik modeli olan TrendyolSecurityLLM-v2-70B modelimizi Huggingface'de open source olarak kullanıma sunduk. 🙏🏻🧡🎉
Bu modelimiz en kapsamlı Siber Güvenlik Ai Benchmark’larından CS-Eval'de İngilizce'de global'de 3. ve Multi-Lang'de 5. sırada yer aldı. Ayrıca modelimiz top 10'da yer alan modeller arasında açık kaynaklı olarak sunulan tek model. 🙏🏻🎉
Özellikler;
- Savunma Odaklı Muhakeme: Standartlarla (OWASP/ATT&CK/NIST/CIS) hizalı öneriler; “neden/kanıt” içeren adım adım açıklamalar.
- Politika ve Mimari Kılavuzlar: Kimlik/erişim, şifreleme, ağ segmentasyonu, bulut kontrol setleri, veri sınıflandırma ve alarm mantığı.
- IR & Threat Hunting Desteği: Olay akışı, triyaj kontrol listeleri, güvenli log sorgu kalıpları, playbook iskeletleri.
- Cloud & DevSecOps: CI/CD güvenlik kapıları, IaC yanlış yapılandırma örüntüleri, K8s hardening kontrol listeleri.
- Tasarımla Reddetme (Refusal-by-Design): İstismarcı/kötücül istemlere uygunlukla hizalı yanıt kalıpları ve güvenli alternatifler.
Hello friends, we’ve open-sourced our TrendyolSecurityLLM-v2-70B model on Hugging Face, the largest-parameter open-source cybersecurity model released to date.
On CS-Eval, one of the most comprehensive cybersecurity AI benchmarks, the model ranks #3 globally in English and #5 in the multi-language track. It’s also the only open-source model among the top 10. 🙏🏻🧡🎉
Features;
- Defense-Focused Reasoning: Standards-aligned (OWASP/ATT&CK/NIST/CIS) recommendations with step-by-step explanations that include the “why/evidence.”
- Policy & Architecture Guides: Identity/access, encryption, network segmentation, cloud control sets, data classification, and alert logic.
- IR & Threat Hunting Support: Incident flow, triage checklists, safe log query patterns, playbook skeletons.
- Cloud & DevSecOps: CI/CD security gates, IaC misconfiguration patterns, K8s hardening checklists.
- Refusal-by-Design: Safe alternatives and compliance-aligned response patterns for exploitative/malicious prompts.
https://t.co/dqtbg2HeUH
Released ai-captcha-bypass 🚀 — new version for gpt4-captcha-bypass.
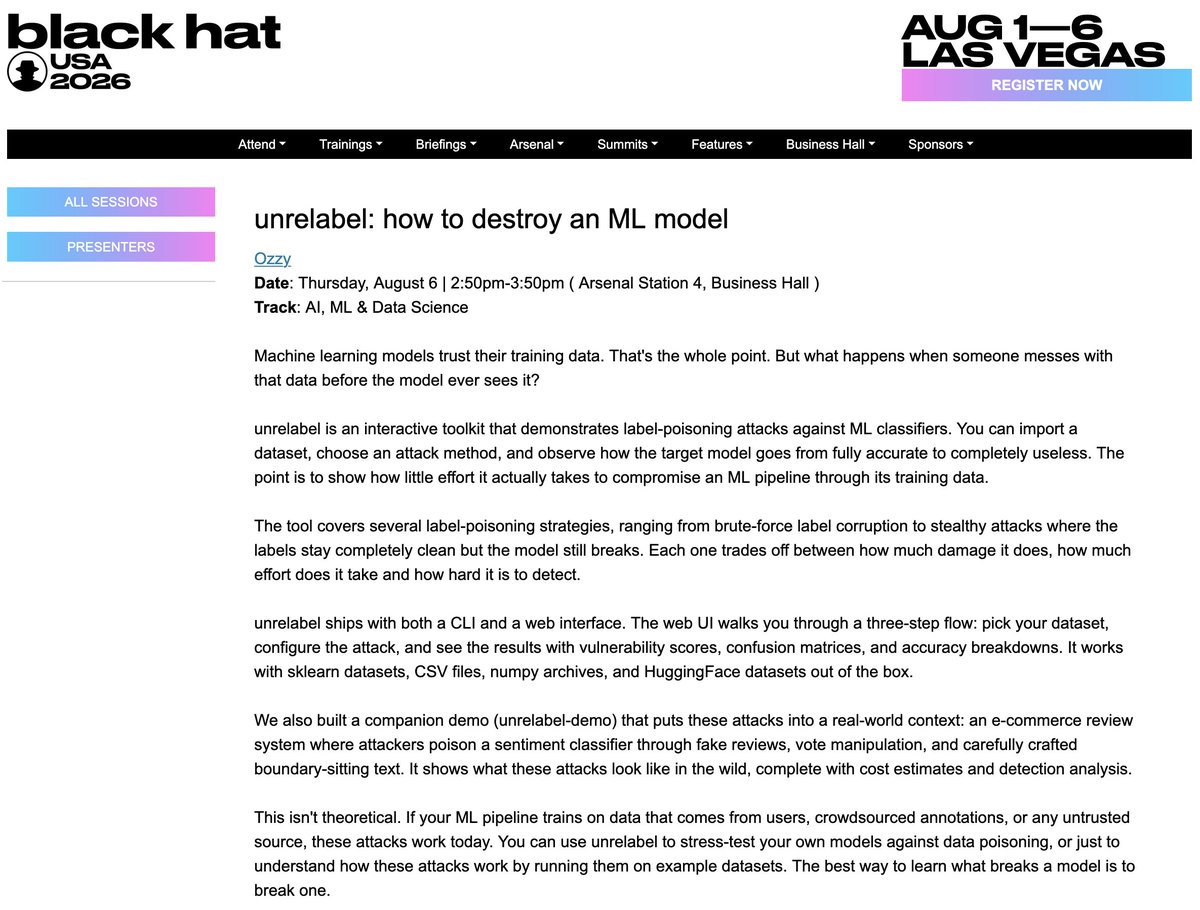
- Supports reCAPTCHA, visual puzzles, simple & complex text CAPTCHAs, and audio challenges. I’ll be presenting this research at @BlackHatEvents!
https://t.co/mVQSZ4Vfme
#bugbounty#security
Daha önce directory-listing sayfalarının ağacını çıkaran bir uygulama yayınlamıştım, şimdi de bunu AI ile yapan bir MCP server geliştirdim, incelemek isterseniz link aşağıda 👇✨
https://t.co/UrR0BNjYG4
The Qwen3-14B finetuned version BaronLLM, which we developed together with @rizasabuncu, @kultekin, Mertcan Kondur, İsmail Yavuz and Melih Yılmaz, ranked 4th among all models in the English cybersecurity benchmark category of CS-Eval 😳🥹🔥🔥☠️☠️ We even surpassed giant models like DeepSeek, Qwen72B, and GPT-4 🔥🥹